
Info
python wrapper for abuseipdb API (https://docs.abuseipdb.com/#introduction)
gives you informations about abuse level of specified IP addresses
focuses on caching results in local db
Install
stable version from pypi
pip install abuseipdb-wrapperor newest version from github
pip install git+https://github.com/streanger/abuseipdb-wrapper.gitCommand-line usage
abuseor as module
python -m abuseipdb_wrapperPython usage
init `AbuseIPDB` object
Init AbuseIPDB object using API KEY created on https://www.abuseipdb.com/. Optionally you can provide db_file for your local database. It is recommended because this project focuses on storing data for further quick access without need of another requests.
from abuseipdb_wrapper import AbuseIPDB
API_KEY = 'YOUR_API_KEY'
abuse = AbuseIPDB(api_key=API_KEY, db_file='abuseipdb.json')
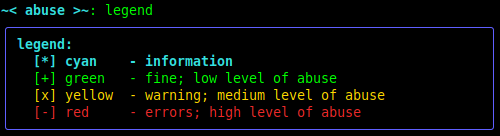
abuse.colors_legend()
check list of IPs
Specify list of IPs to be checked using add_ip_list method. Then call check method and wait for results.
ips = ['1.2.3.4', '5.6.7.8', '9.10.11.12', '13.14.15.16']
abuse.add_ip_list(ips)
abuse.check()
no db caching approach
If you are not interested in caching data in local database and only want to request for IP addresses one by one use the following code. Have in mind that .check_ip method enriches results and removes reports section. If using wrapper is like overkill in your project, go to: https://docs.abuseipdb.com/?python#check-endpoint
from abuseipdb_wrapper import AbuseIPDB
API_KEY = 'YOUR_API_KEY'
abuse = AbuseIPDB(api_key=API_KEY)
ips = ['1.2.3.4', '2.3.4.5', '3.4.5.6']
for IP in ips:
    result = abuse.check_ip()  # enriched with url and request time
    result = abuse.check_ip_orig()  # results in original form
    print(result)
show local db
To display collected informations use show method. Alternatively call print on your AbuseIPDB object. You can specify columns to be displayed using apply_columns_order method. It affects both vertical and table view.
columns = ['ipAddress', 'abuseConfidenceScore', 'totalReports', 'countryCode', 'domain', 'isp']
abuse.apply_columns_order(columns)
# show db by print or using .show method
print(abuse)
abuse.show(matched_only=False, table_view=True)
viewer
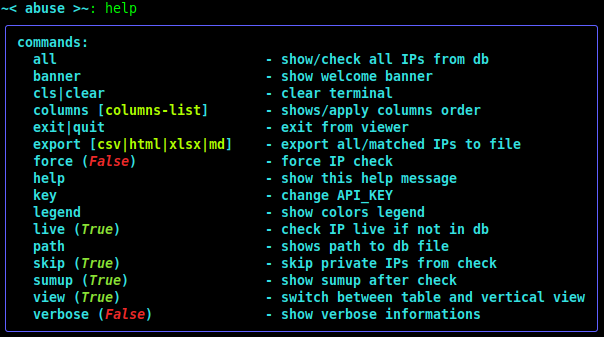
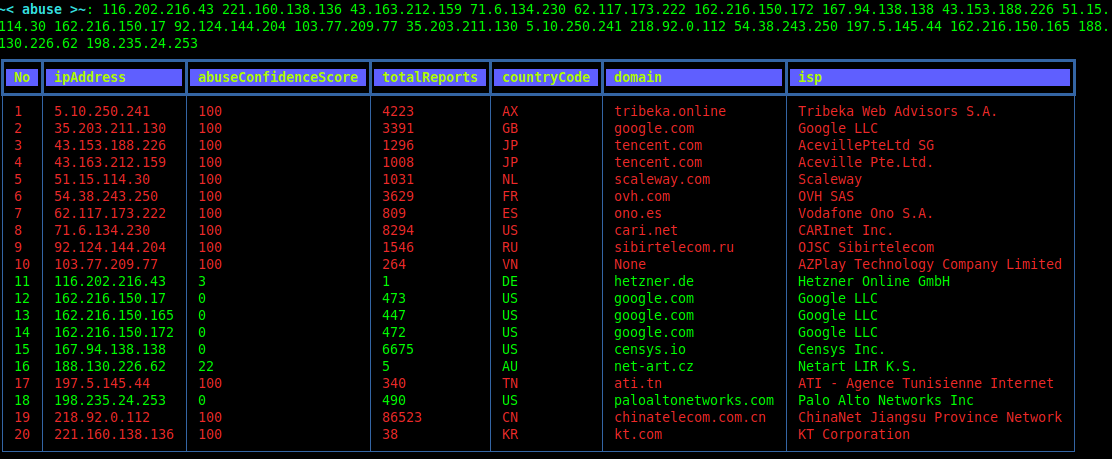
For interactive IP check use .viewer method. It let you to provide multiple IPs at once. Use help for more information.
abuse.viewer()
~< abuse >~: columns [columns list]         # shows or apply columns order
~< abuse >~: export [csv, html, xlsx, md]   # export to file
~< abuse >~: all                            # check/show all database
exports
abuse.export_csv('out.csv', matched_only=False)
abuse.export_html_styled('out.html', matched_only=False)
abuse.export_xlsx_styled('out.xlsx', matched_only=False)
abuse.export_md('out.md', matched_only=False)
convert to dataframe object
import pandas as pd
matched = abuse.get_db(matched_only=False)
df = pd.DataFrame(matched.values())
json columns
abuseConfidenceScorecountryCodedate# additionaldomainhostnamesipAddressipVersionisPublicisWhitelistedisplastReportedAtnumDistinctUserstotalReportsurl# additionalusageTypeisTor
Screenshots
banner
colors legend
help
vertical view
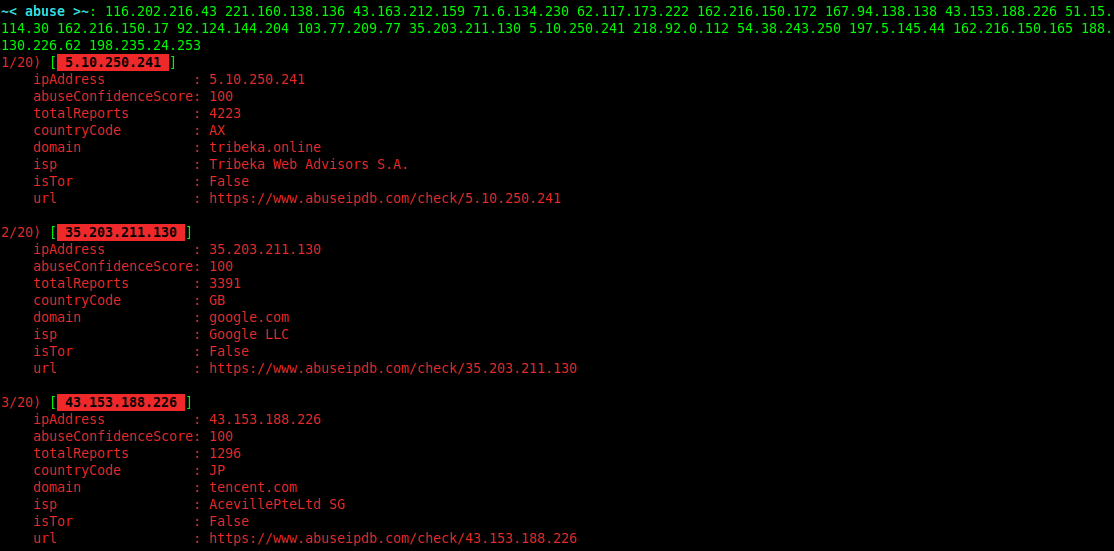
table view
Changelog
v.0.2.0:
removed pandas and Jinja2 dependencies
custom export functions
dateas isoformat with timezone
v.0.1.9:
additional
isTorNodefield replaced withisTorsupported by api
v.0.1.8:
more flexible exports
passing
api_keytoAbuseIPDBis now optionalkeep order for passing IPs
- viewer:
skip private IPs flag
sumup flag
force new check flag
more verbose logs
asterisks for api key using pwinput
colors support for: windows-cmd, windows-terminal, windows-powershell, vscode, linux-terminal
tests coverage for most features
export to markdown
and few smaller changes
v.0.1.7:
abuse entrypoint
columns command in interactive view
export command in interactive view (to .csv, .html, .xlsx)
tor exit nodes enrichment
storing db file in user home directory
original API request using .check_ip_orig
getpass and keyring for API_KEY read & store
v.0.1.6 and before:
black background for better view in powershell
export to csv, html, xlsx (from pandas df)
wrap text in table cells - made using rich table
return dataframe object
enrich results with date of last check
1 maintainer

Metadata
1 maintainer
Release files for abuseipdb-wrapper 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| abuseipdb_wrapper-0.2.0-py2.py3-none-any.whl | Python 3, Python 2 | none | any | Details for abuseipdb_wrapper-0.2.0-py2.py3-none-any.whl |
Release files / abuseipdb_wrapper-0.2.0-py2.py3-none-any.whl
| Download URL | abuseipdb_wrapper-0.2.0-py2.py3-none-any.whl |
|---|---|
| Size | 21.0 kB |
| Tags | Python 2 Python 3 |
|
SHA-256 checksum How to use checksums |
74f6aa905275c453916c7a63a01d0d814c7de5ea959dd6a2072f44e00f741338
|
|
BLAKE2b-256 checksum How to use checksums |
f9ba692313318a1fc2e81d8a612b158657beb80b1c5ac4b9201d4b5ac50703af
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.10.12
|
Security for abuseipdb-wrapper 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














