


🔗 Example of a backend for a TODO app
Apijet is a Python framework for building APIs via the command line. Apijet is a useful framework for fast prototyping Rest APIs. Apijet will deploy python code according to the well-defined pattern (see here), you only have to pay attention to the business logic and to the database queries.
You will be able to deploy endpoints following these 5 steps:
- Install apijet Once you have installed the package, apijet will be available as bash command.
$> pip install apijet
- Create a project The create command generates the skeleton of the project and the main project files.
$> apijet create --name myProject --port 9090 --address 127.0.0.1
$> cd my_projet
- Add and endpoint. The endpoint can also need database support, in this case, you pass the --database parameter and Apijet will generate the code for CRUD basic operation for the endpoint. If you need database support, you make sure that mongodb is running. Consider a Docker container to deploy an instance in a short time (see here).
$> apijet endpoint --name myEndpoint
- Run the server
$> python -m myProject.app
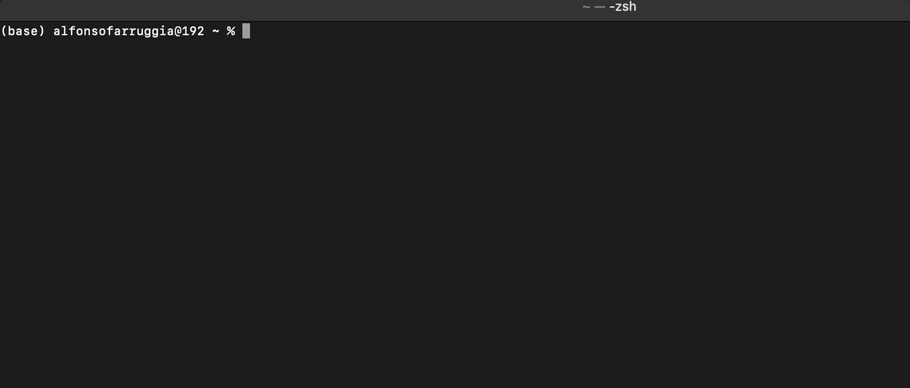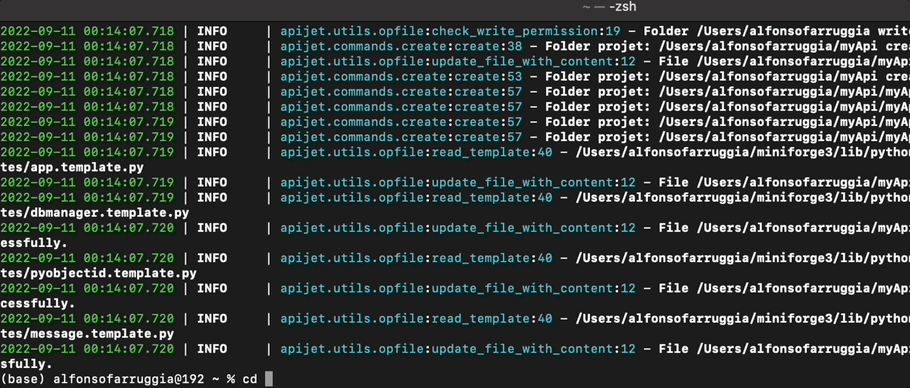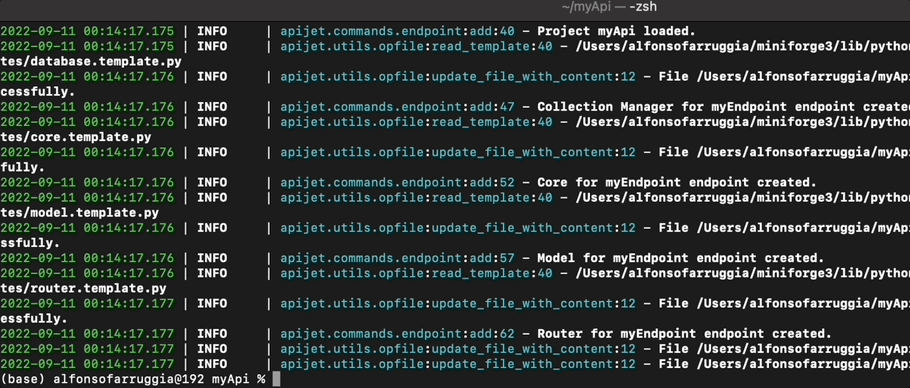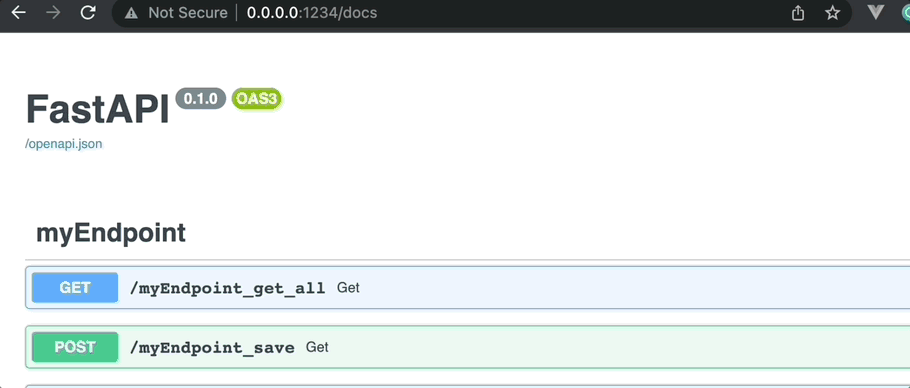
- Open your browser The APIs will be exposed according the automatic interactive API documentation by Swagger. Open your browser @ http://127.0.0.1:9090/docs to test out your work!
These steps generate a follow folder and file structure:
.
|-- myProject
|   |-- core
|   |   |
|   |   `-- myendpoint.py
|   |-- database
|   |   |-- dbmanager.py
|   |   |-- message.py
|   |   |-- myendpoint.py
|   |   `-- pyobjectid.py
|   |-- models
|   |   |
|   |   `-- myendpoint.py
|   |-- routers
|   |   |
|   |   `-- myendpoint.py
|   `-- app.py
`-- apijet.json
The project configuration is saved in the apijet.json file:
{
    "name": "myProject",
    "port": 1234,
    "address": "127.0.0.1",
    "workers": 1,
    "mongo": {
        "auth": false,
        "address": "127.0.0.1",
        "port": 27017,
        "username": "",
        "password": ""
    },
    "endpoints": [
        "myEndpoint"
    ]
}
where:
- address and port are used by the web server.
- if workers > 1, Gunicorn will be started otherwise Unicorn as ASGI web server
- if mongo.auth is true, mongo.username and mongo.password are requested
Run MongoDB in a docker contaienr
If you are a fan of docker and you want to run an instance of MongoDb without stress:
$> docker run -d -p 27017:27017 --name myProject-db mongo:latest
Source code and pattern.
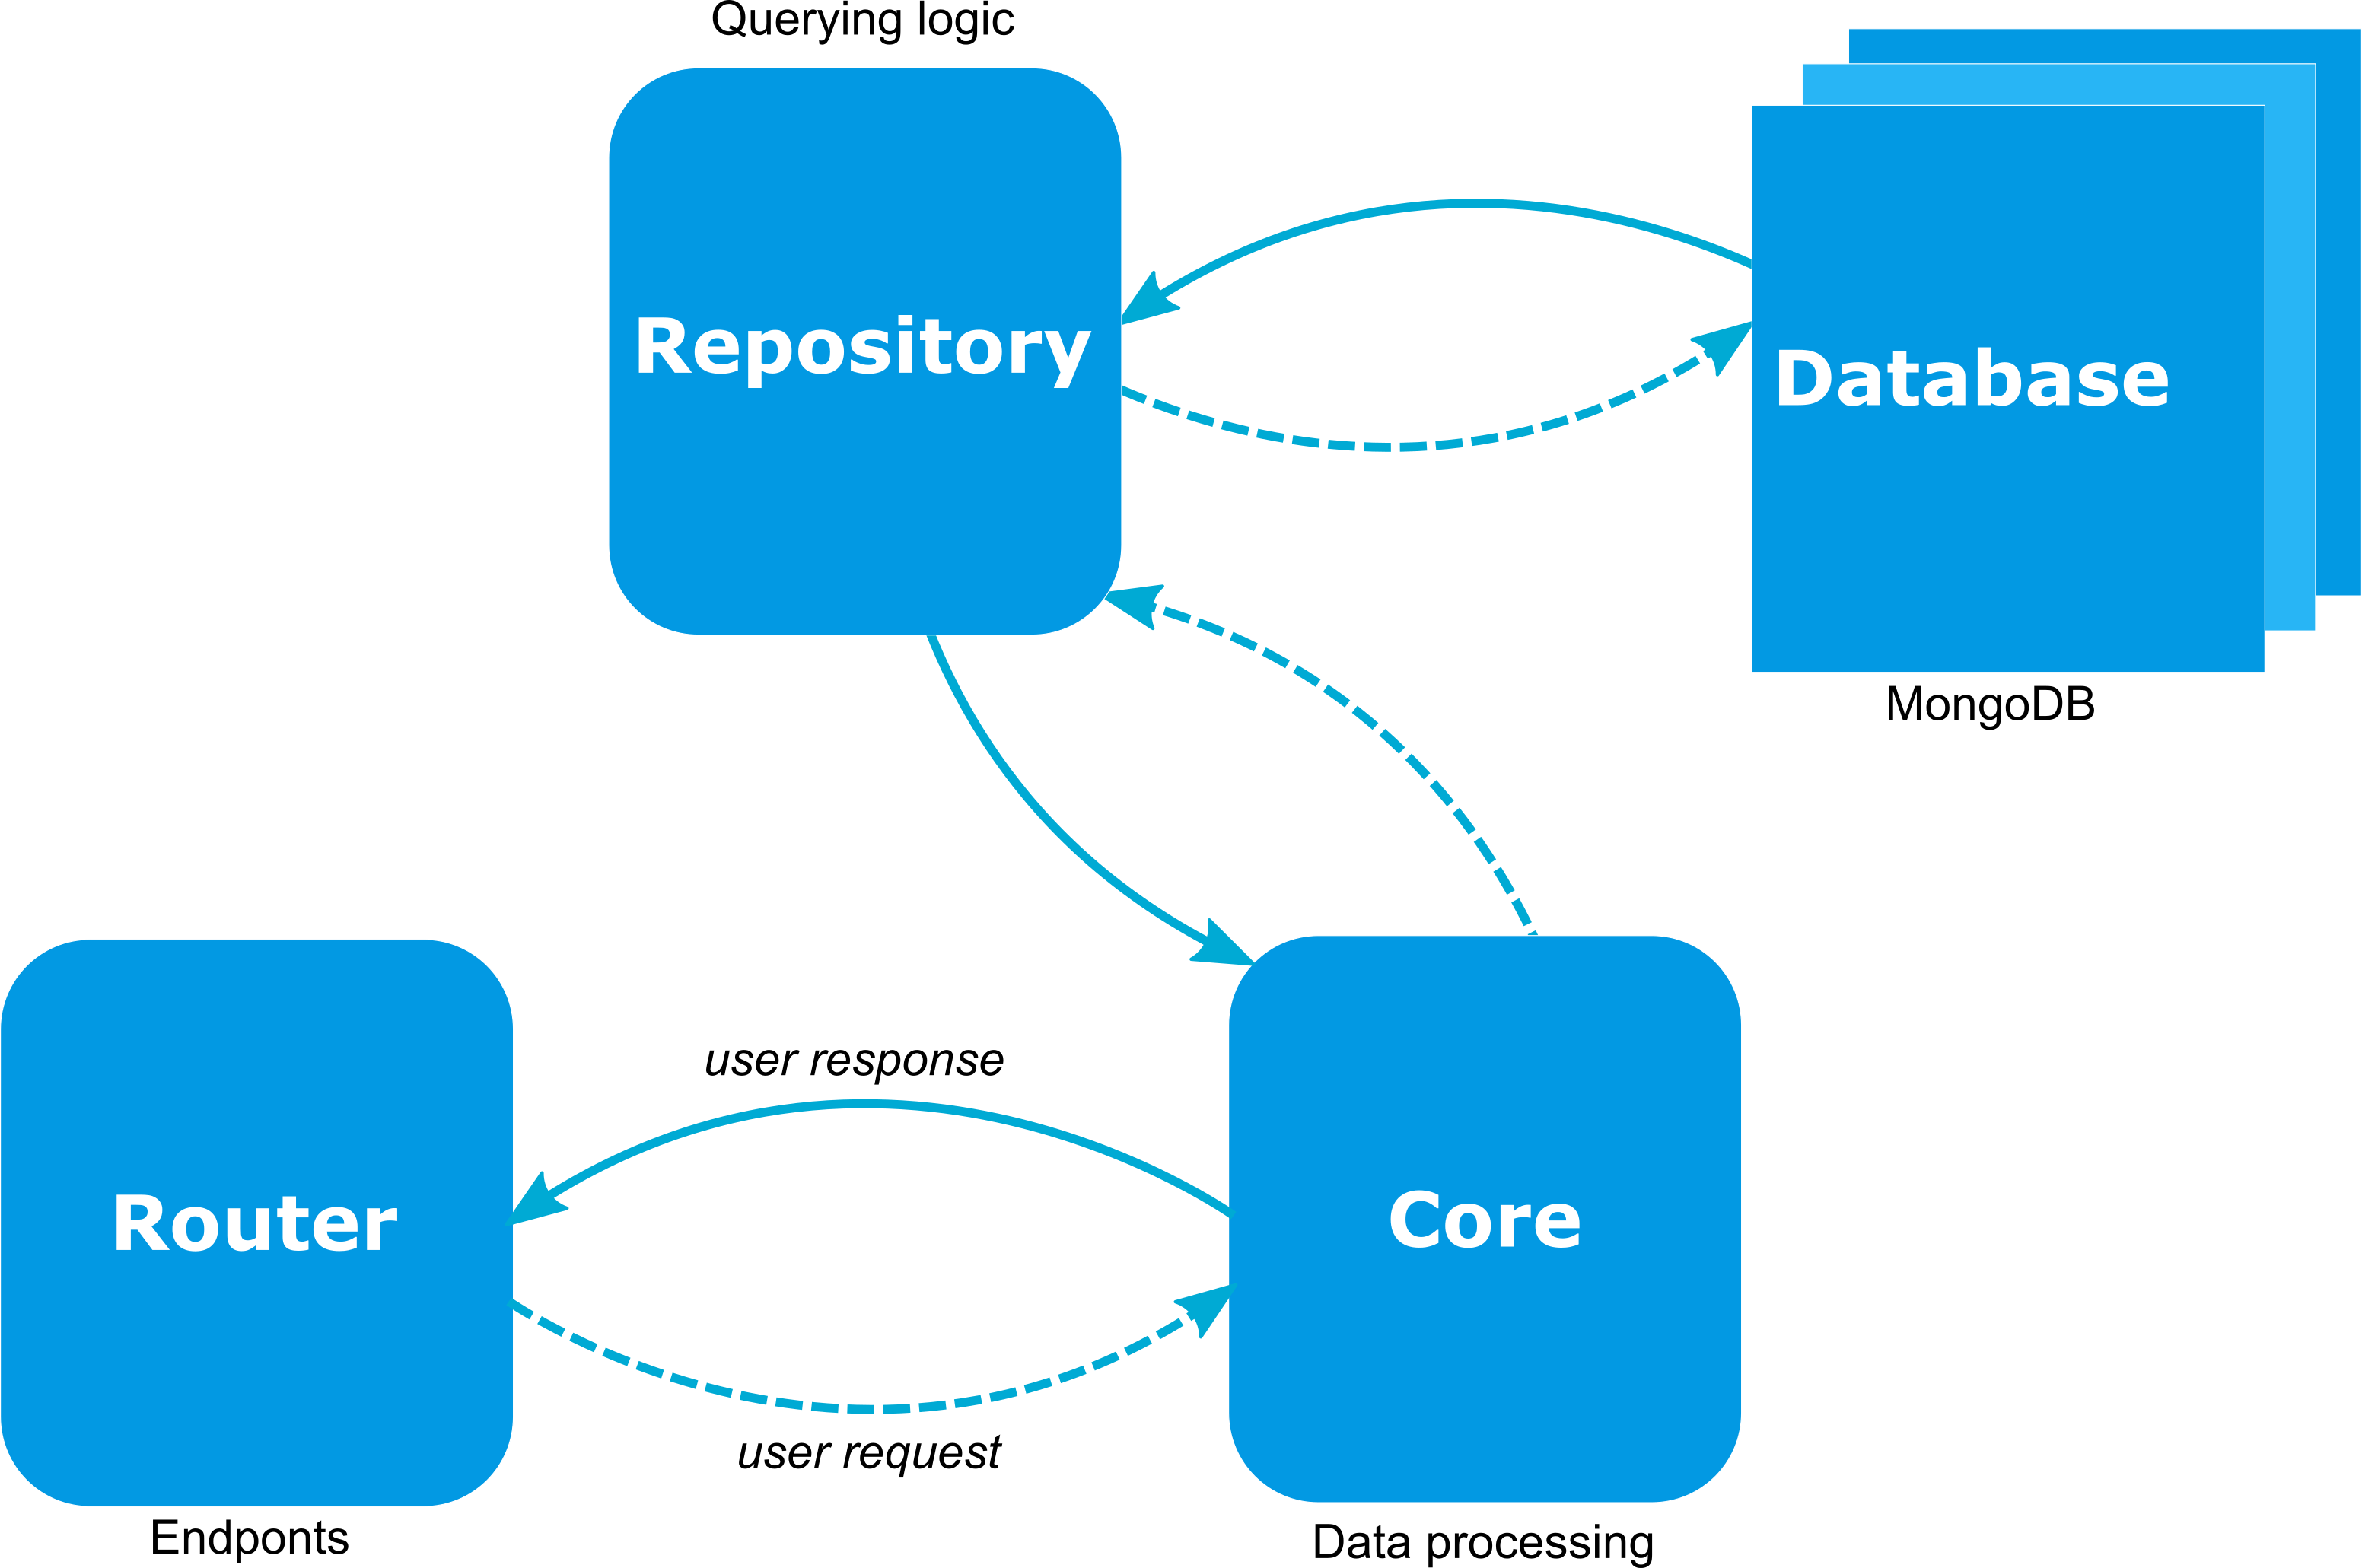
Apijet project folder contains the auto-generated python code. The code is arranged in four folders: core, repository, router and models. When a new endpoint is added, a new file in each of these four folders is created. These four files have the same name (/myEndpoint.py) of the endpoint but they have different behaviour, see the following pattern.
Router
Files created as routers expose the endpoints, they receive the user request and send back the response. (i.e. router/myEndpoint.py)
Core
Files as core implement the business logic. Your algorithms and data processing stuff go here. (i.e. core/myEndpoint.py)
Repository
Files as repositories make the interaction with the database. Your queries go here. (i.e. repository/myEndpoint.py)
Models
For each endpoint, core, repository, and router communicate through the data structure. The data structure is located in the folder models. You modify this file with the parameters you need to handle in your project.
🔗 Follow this link for the example on how to implement a backend for a TODO app
Expose an endpoint in 20 secs.
Dev-Stack
The code is generated exploiting the following development stack :
-
MongoDB : Document database - 🔗
-
Pymongo : Python library for working with MongoDB - 🔗
-
apijet : RestApi framework -🔗
-
Pydantic : Python data validator & more - 🔗
-
Uvicorn : ASGI web server implementation for Python - 🔗
CLI Commands
Helper
$> apijet -h
usage: apijet [-h] {create,endpoint,remove} ...

apijet - Api Generator v: 0.2.2

optional arguments:
  -h, --help            show this help message and exit

Actions:
  {create,endpoint,remove}
    create              Create a new project
    endpoint            Add or Remove an endpointto the project
    remove              Remove a project
Create projet
$> apijet create -h
usage: apijet create [-h] [--port PORT] [--name NAME] [--address ADDRESS]

optional arguments:
  -h, --help         show this help message and exit
  --port PORT        port where apis are exposed
  --name NAME        project name
  --address ADDRESS  ip address where apis are exposed
Add endpoint
$> apijet endpoint -h
usage: apijet endpoint [-h] [--add ADD] [--database] [--remove REMOVE]

optional arguments:
  -h, --help       show this help message and exit
  --add ADD        endpoint name
  --database       say that the endpoint needs database support
  --remove REMOVE  endpoint name
1 maintainer

Metadata
1 maintainer
Release files for apijet 0.5.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| apijet-0.5.1-py3-none-any.whl | Python 3 | none | any | Details for apijet-0.5.1-py3-none-any.whl |
Release files / apijet-0.5.1-py3-none-any.whl
| Download URL | apijet-0.5.1-py3-none-any.whl |
|---|---|
| Size | 15.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
db928c19adbf6755a55e1c2a7fe07179e8b0a56cc973df6f934e6238f013514f
|
|
BLAKE2b-256 checksum How to use checksums |
b83be5e00ff4b8ce31a1b28ce32d012caa1bc6001b33fbd161bfd3b39ca0245e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.9.13
|
Security for apijet 0.5.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














