


A security linter from PyCQA
Free software: Apache license
Documentation: https://bandit.readthedocs.io/en/latest/
Source: https://github.com/PyCQA/bandit
Contributing: https://github.com/PyCQA/bandit/blob/main/CONTRIBUTING.md
Overview
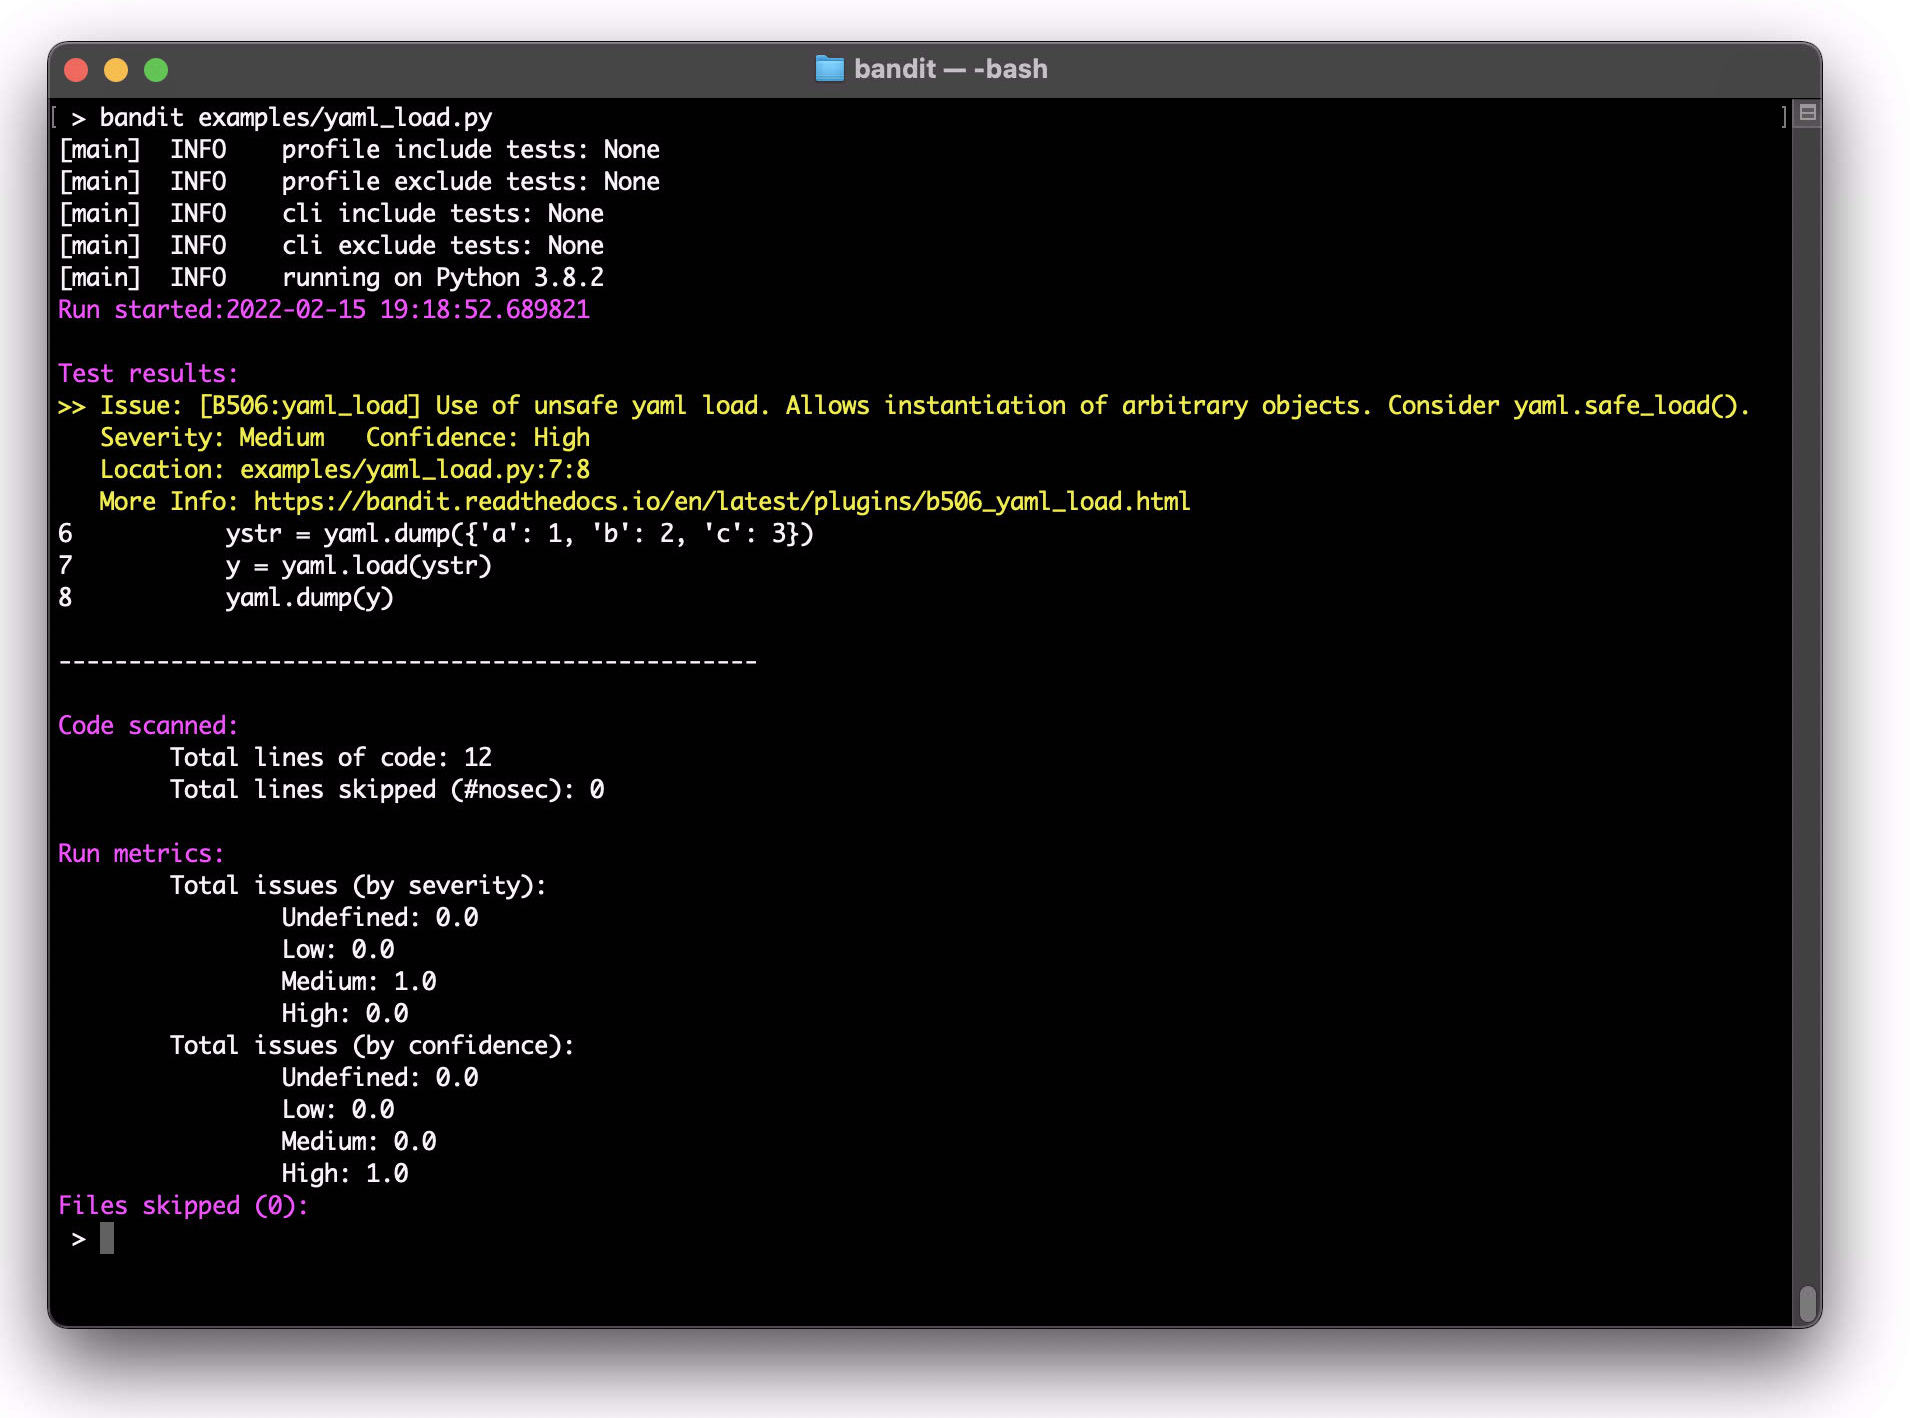
Bandit is a tool designed to find common security issues in Python code. To do this Bandit processes each file, builds an AST from it, and runs appropriate plugins against the AST nodes. Once Bandit has finished scanning all the files it generates a report.
Bandit was originally developed within the OpenStack Security Project and later rehomed to PyCQA.
Show Your Style

Use our badge in your project’s README!
using Markdown:
[](https://github.com/PyCQA/bandit)
using RST:
.. image:: https://img.shields.io/badge/security-bandit-yellow.svg
    :target: https://github.com/PyCQA/bandit
    :alt: Security Status
References
Python AST module documentation: https://docs.python.org/3/library/ast.html
Green Tree Snakes - the missing Python AST docs: https://greentreesnakes.readthedocs.org/en/latest/
Documentation of the various types of AST nodes that Bandit currently covers or could be extended to cover: https://greentreesnakes.readthedocs.org/en/latest/nodes.html
Container Images
Bandit is available as a container image, built within the bandit repository using GitHub Actions. The image is available on ghcr.io:
docker pull ghcr.io/pycqa/bandit/banditThe image is built for the following architectures:
amd64
arm64
armv7
armv8
To pull a specific architecture, use the following format:
docker pull --platform=<architecture> ghcr.io/pycqa/bandit/bandit:latestEvery image is signed with sigstore cosign and it is possible to verify the source of origin using the following cosign command:
cosign verify ghcr.io/pycqa/bandit/bandit:latest \
  --certificate-identity https://github.com/pycqa/bandit/.github/workflows/build-publish-image.yml@refs/tags/<version> \
  --certificate-oidc-issuer https://token.actions.githubusercontent.com
Where <version> is the release version of Bandit.
Sponsors
The development of Bandit is made possible by the following sponsors:
|

|
|
If you also ❤️ Bandit, please consider sponsoring.


Release files for bandit 1.9.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| bandit-1.9.2.tar.gz | 4.2 MB | With provenance | Details for bandit-1.9.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| bandit-1.9.2-py3-none-any.whl | Python 3 | none | any | Details for bandit-1.9.2-py3-none-any.whl |
Total release size: 4.4 MB
Release files / bandit-1.9.2.tar.gz
| Download URL | bandit-1.9.2.tar.gz |
|---|---|
| Size | 4.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
32410415cd93bf9c8b91972159d5cf1e7f063a9146d70345641cd3877de348ce
|
|
BLAKE2b-256 checksum How to use checksums |
cf72f704a97aac430aeb704fa16435dfa24fbeaf087d46724d0965eb1f756a2c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 23, 2025.
Transparency logRelease files / bandit-1.9.2-py3-none-any.whl
| Download URL | bandit-1.9.2-py3-none-any.whl |
|---|---|
| Size | 134.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
bda8d68610fc33a6e10b7a8f1d61d92c8f6c004051d5e946406be1fb1b16a868
|
|
BLAKE2b-256 checksum How to use checksums |
551a5b0320642cca53a473e79c7d273071b5a9a8578f9e370b74da5daa2768d7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 23, 2025.
Transparency logSecurity for bandit 1.9.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for bandit-1.9.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 23, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














