
Introduction

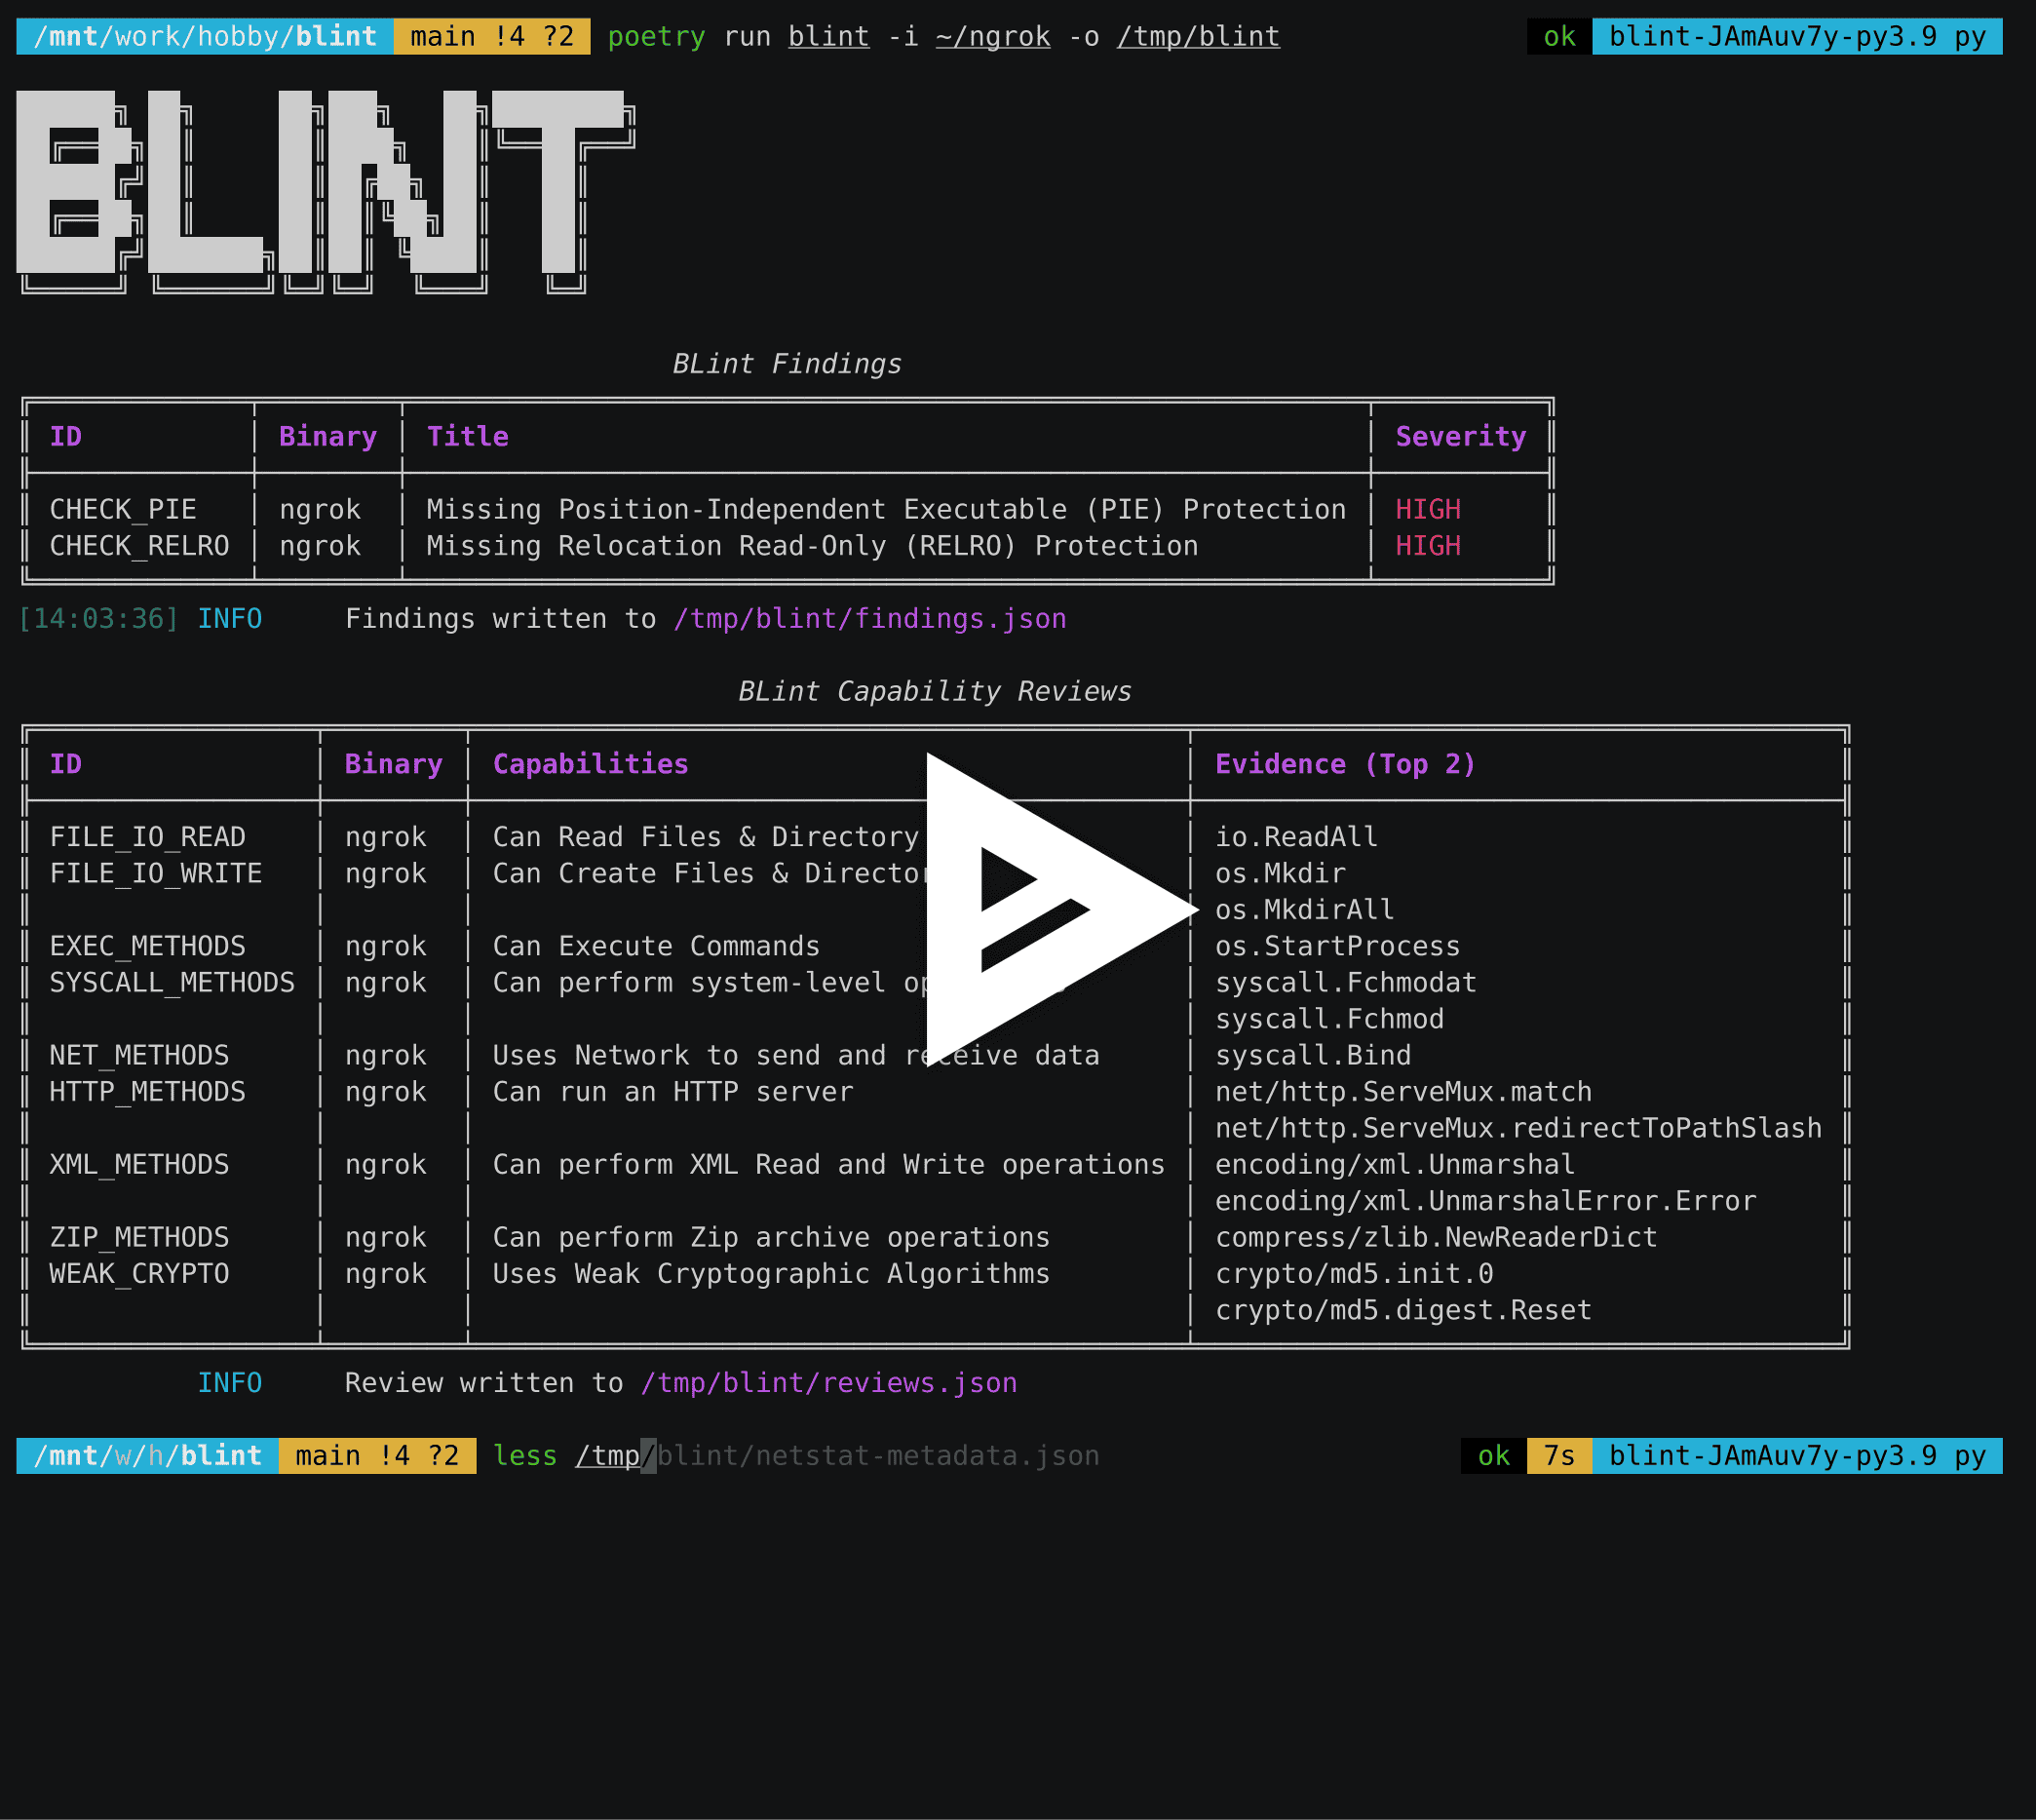
BLint is a Binary Linter to check the security properties, and capabilities in your executables. It is powered by lief
Supported binary formats:
- ELF (GNU, musl)
- PE (exe, dll)
- Mach-O (x64, arm64)
You can run blint on Linux, Windows and Mac against any of these binary formats.
Motivation
Nowadays, vendors distribute statically linked binaries produced by golang or rust or dotnet tooling. Users are used to running antivirus and anti-malware scans while using these binaries in their local devices. Blint augments these scans by listing the technical capabilities of a binary. For example, whether the binary could use network connections, or can perform file system operations and so on.
The binary is first parsed using lief framework to identify the various properties such as functions, static, and dynamic symbols present. Thanks to YAML based annotations data, this information could be matched against capabilities and presented visually using a rich table.
NOTE: The presence of capabilities doesn't imply that the operations are always performed by the binary. Use the output of this tool to get an idea about a binary. Also, this tool is not suitable to review malware and other heavily obfuscated binaries for obvious reasons.
Use cases
- Add blint to CI/CD to inspect the final binaries to ensure code signing or authenticode is applied correctly
- Identify interesting functions and symbols for fuzzing
- Blint was used at ShiftLeft to review the statically linked packages and optimize the distributed cli binary
- Quickly identify malicious binaries by looking at their capabilities (Ability to manipulate networks or drivers or kernels etc)
Installation
- Install python 3.8 or 3.9
pip3 install blint
Single binary releases
You can download single binary builds from the blint-bin releases. These executables should work with requiring python to be installed. The macOS .pkg file is signed with a valid developer account.
Usage
usage: blint [-h] [-i SRC_DIR_IMAGE] [-o REPORTS_DIR] [--no-error] [--no-banner] [--no-reviews]

Linting tool for binary files powered by lief.

optional arguments:
  -h, --help            show this help message and exit
  -i SRC_DIR_IMAGE, --src SRC_DIR_IMAGE
                        Source directory or container image or binary file
  -o REPORTS_DIR, --reports REPORTS_DIR
                        Reports directory
  --no-error            Continue on error to prevent build from breaking
  --no-banner           Do not display banner
  --no-reviews          Do not perform method reviews
  --suggest-fuzzable    Suggest functions and symbols for fuzzing based on a dictionary
To test any binary including default commands
blint -i /bin/netstat -o /tmp/blint
Use -i to check any other binary. For eg: to check ngrok
blint -i ~/ngrok -o /tmp/blint
Pass --suggest-fuzzable to get suggestions for fuzzing. A dictionary containing "common verbs" is used to identify these functions.
blint -i ~/ngrok -o /tmp/blint --suggest-fuzzable
PowerShell example

Reports
Blint produces the following json artifacts in the reports directory:
- blint-output.html - HTML output from the console logs
- exename-metadata.json - Raw metadata about the parsed binary. Includes symbols, functions, and signature information
- findings.json - Contains information from the security properties audit. Useful for CI/CD based integration
- reviews.json - Contains information from the capability reviews. Useful for further analysis
- fuzzables.json - Contains a suggested list of methods for fuzzing
References
Metadata
Release files for blint 1.0.23
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| blint-1.0.23.tar.gz | 78.3 kB | Without provenance | Details for blint-1.0.23.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| blint-1.0.23-py3-none-any.whl | Python 3 | none | any | Details for blint-1.0.23-py3-none-any.whl |
Total release size: 160.0 kB
Release files / blint-1.0.23.tar.gz
| Download URL | blint-1.0.23.tar.gz |
|---|---|
| Size | 78.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1589b7b107220a35d598abdb1e409aec8705343fbdfe2256139afb0013caf44f
|
|
BLAKE2b-256 checksum How to use checksums |
78465d740dc19a047da2a66ed565a8d353adc520b4f418b3050b0ec65a38d418
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.2.2 CPython/3.10.6 Linux/6.0.2-76060002-generic
|
Release files / blint-1.0.23-py3-none-any.whl
| Download URL | blint-1.0.23-py3-none-any.whl |
|---|---|
| Size | 81.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1bc24a202f461391bd7f3678053d6492ce989942340ea6cb77c08e0450853121
|
|
BLAKE2b-256 checksum How to use checksums |
032ea10ca2fbb5e680294cc1f3ad49b04fb16c58a31c64efdd7e3e5cc4f62c0d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.2.2 CPython/3.10.6 Linux/6.0.2-76060002-generic
|
Security for blint 1.0.23
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














