
Django easy report
Django App for generate easily reports using Celery
Implments the following functions:
- Allows permissions by report.
- Allows multi storage systems.
- Allows prevalidation before generate.
- Detect same report params to allows cache it.
- Allows add requeters to a existing report.
- Allows customize send flow inside the report code.
- Allows secrets keys for storage setup based on:
django settings,environmentorcryptography. - Allows filter for storages and report classes.
- Action that allows generate report from Admin page.
SetUp
- Install package from pypi:
pip install django-easy-report
- Add application on
settings.py:
# ...
INSTALLED_APPS = [
# ...
    'django_easy_report',
# ...
]
- Add on
urls.pythe namespacedjango_easy_report:
# ...
urlpatterns = [
    # ...
    path('reports/', include(('django_easy_report.urls', 'django_easy_report'), namespace='django_easy_report')),
    # ...
]
- Configure celery
Protect import dynamic classes
In order to block insecure classes on ReportSender and ReportGenerator models,
is allowed to define the on settings.py the setting SENDER_CLASSES and/or REPORT_CLASSES:
# ...
SENDER_CLASSES = [
    'django.core.files.storage.FileSystemStorage',
]

REPORT_CLASSES = [
    'django_easy_report.reports.ReportModelGenerator',
    'django_easy_report.reports.AdminReportGenerator',
]
# ...
That values will be checked when model is saved and loaded, that means that you will not able to use the reports who have classes not listed on the proper setting.
Howto
- Create your code (see example).
- Create
Formclass for validate input. - Create Report class (extended from
ReportBaseGenerator).- Overwrite function
get_paramsfor know the users params and the report params. - Overwrite function
validatecallingsuperto validate the form. - Implement function
generatefunction usingself.bufferfor write the report. - Overwrite function
get_filenameto set report name. - Overwrite function
get_messageto return the email body or raiseDoNotSendto omit email send.
- Overwrite function
- Create
- Create report
Senderon Admin page. - Create
Report Generatoron Admin page. - Use you report endpoint defined on Admin page.
Using Secrets
In order to protect your secrets you could use the SecretKey Model.
That allows you use
django settings,
environment or
cryptography to protect your secrets.
When you use that secrets you must create the model, on the Admin page.
The information that you enter must be on plain text.
The key field is only required when crypto is using.
Then you must create or edit a ReportSender model, adding on the key that you want to use.
The replace word will be used on the Storage init params field to replace with the value of the secret in plain text.
That allow you to replace the value of Storage init params from:
{
  "my_secret": "Insecure secret"
}
to
{
  "my_secret": $my_replace_word
}
Using Admin Action
In order to allow generate reports based on admin page,
there is an action localed on django_easy_report.actions.generate_report.
You could see an example on: test_web/custom/admin.py
To allows the generation flow on the standard flow you must
create Report Generator on Admin page using the class django_easy_report.reports.AdminReportGenerator.
In order to work you could only have one report using that class.
API workflow
See doc as OpenAPI format or in swagger
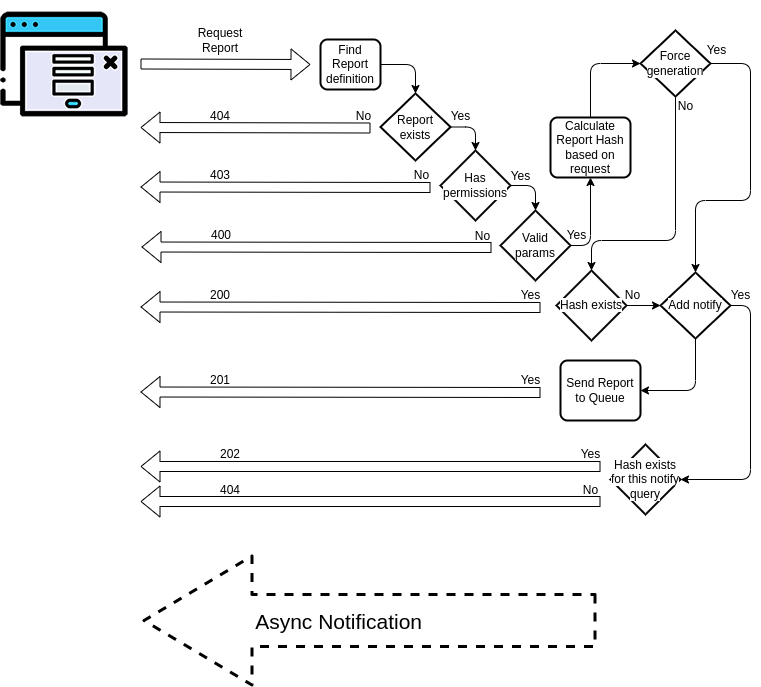
Examples
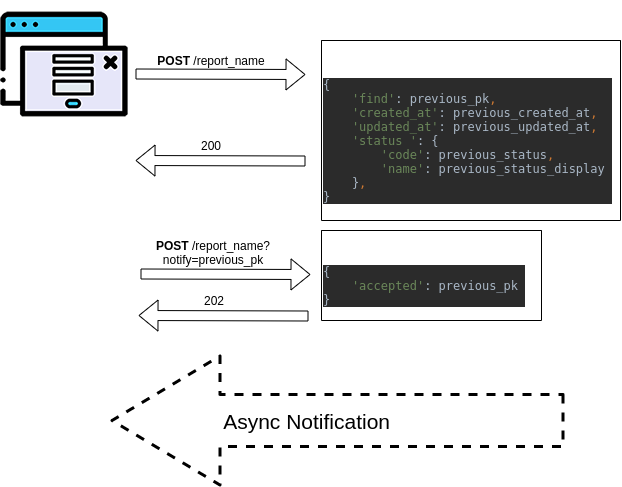
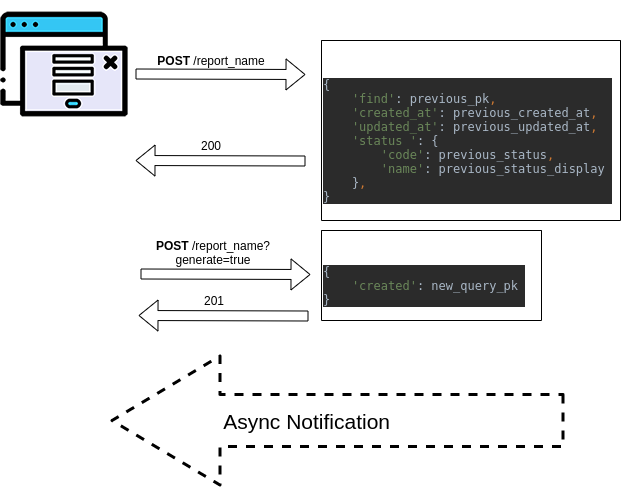
In both cases, the report is already generated by other user.
- Notify me when report is done
- Regenerate new report
Test it with Docker
- Docker-compose
docker-compose up web -d
docker-compose exec web bash
- Docker
docker build . --tag="django_easy_report:latest"
docker run --publish=8000:8000 --name=django_easy_report_web django_easy_report:latest -d
docker exec -ti django_easy_report_web bash
- Run tests locally
docker build . --tag="django_easy_report:py38dj22" --build-arg PY_VERSION=3.8 --build-arg DJANGO_VERSION=2.2
docker run --rm --entrypoint /usr/local/bin/python --name=test_django_easy_report_web django_easy_report:py38dj22 manage.py test
Note that in that case you need rebuild with any change in the code
MIT License
Copyright 2021 Victor Torre
Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions:
The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
1 maintainer

Metadata
1 maintainer
Release files for django-easy-report 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| django-easy-report-0.2.0.tar.gz | 33.4 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| django_easy_report-0.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 75.4 kB
Release files / django-easy-report-0.2.0.tar.gz
| Download URL | django-easy-report-0.2.0.tar.gz |
|---|---|
| Size | 33.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8cc320c52f2fde3796f3167860feb8fcff6b2ba454c312fb3c620e4b0d9dbf4b
|
|
BLAKE2b-256 checksum How to use checksums |
a994d211000df0056ed41a03b3ef57740d23c08d1e30e208e8d42043314e7963
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.8.0 pkginfo/1.8.2 readme-renderer/32.0 requests/2.22.0 requests-toolbelt/0.9.1 urllib3/1.26.8 tqdm/4.62.3 importlib-metadata/4.10.1 keyring/18.0.1 rfc3986/2.0.0 colorama/0.4.3 CPython/3.8.10
|
Release files / django_easy_report-0.2.0-py3-none-any.whl
| Download URL | django_easy_report-0.2.0-py3-none-any.whl |
|---|---|
| Size | 42.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
bd09ea3f717e1f22c912faa6fb07c3a1f4b2a2d157e1126a43a81ed1473e418e
|
|
BLAKE2b-256 checksum How to use checksums |
337a2b1c1739e048b6693a94af97996d3023496725f92694fd26984b31a64148
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.8.0 pkginfo/1.8.2 readme-renderer/32.0 requests/2.22.0 requests-toolbelt/0.9.1 urllib3/1.26.8 tqdm/4.62.3 importlib-metadata/4.10.1 keyring/18.0.1 rfc3986/2.0.0 colorama/0.4.3 CPython/3.8.10
|
Security for django-easy-report 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














