
Django ZXCVBN Password
Back-end and Front-end password validation with ZXCVBN.
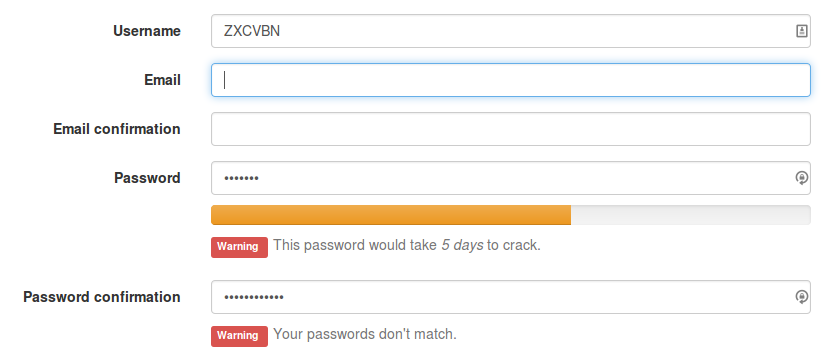
A combination of pirandig’s django-zxcvbn and aj-may’s django-password-strength Django apps. It combines back-end and front-end validation with strength meter display.
License
Software licensed under ISC license.
Installation
pip install django-zxcvbn-password
Requirements
The JavaScript code of this application uses JQuery, but JQuery is not bundled with it. Please install it separately. You might also want to use Bootstrap.
Usage
# settings.py

INSTALLED_APPS = [
    ...
    'zxcvbn_password',
    ...
]

AUTH_PASSWORD_VALIDATORS = [
    {
        'NAME': 'django.contrib.auth.password_validation.UserAttributeSimilarityValidator',
    },
    {
        'NAME': 'django.contrib.auth.password_validation.MinimumLengthValidator',
    },
    {
        'NAME': 'django.contrib.auth.password_validation.CommonPasswordValidator',
    },
    {
        'NAME': 'django.contrib.auth.password_validation.NumericPasswordValidator',
    },
    {
        'NAME': 'zxcvbn_password.ZXCVBNValidator',
        'OPTIONS': {
            'min_score': 3,
            'user_attributes': ('username', 'email', 'first_name', 'last_name')
        }
    }
]
# forms.py
from django import forms
from zxcvbn_password.fields import PasswordField, PasswordConfirmationField
class RegisterForm(forms.Form):
password1 = PasswordField()
password2 = PasswordConfirmationField(confirm_with=’password1’)# views.py
if form.is_valid():
user = User.objects.create_user(
username=...,
password=form.cleaned_data['password1']
)By default, other inputs won’t be used to compute the score, but you can enforce it like this:
# forms.py

from django import forms
from zxcvbn_password import zxcvbn
from zxcvbn_password.fields import PasswordField, PasswordConfirmationField

class RegisterForm(forms.Form):
    password1 = PasswordField()
    password2 = PasswordConfirmationField(confirm_with=’password1’)

    def clean(self):
        password = self.cleaned_data.get('password1')
        other_field1 = ...
        other_field2 = ...

        if password:
            score = zxcvbn(password, [other_field1, other_field2])['score']
            # score is between 0 and 4
            # raise forms.ValidationError if needed

        return self.cleaned_data
Custom frequency lists
zxcvbn-python provides a feature to add custom frequency lists, you can specify your own custom frequency lists in the validator by adding frequency_lists to AUTH_PASSWORD_VALIDATORS, where dutch_words is a list of strings:
# settings.py

AUTH_PASSWORD_VALIDATORS = [
    ...
    {
        'NAME': 'zxcvbn_password.ZXCVBNValidator',
        'OPTIONS': {
            'frequency_lists': {
                'dutch': dutch_words,
            }
        }
    }
]
Screen-shot
Documentation
Development
To run all the tests: tox
Similar projects
You should check out django-zxcvbn-password-validator for backend validation only, but with a good UX and translated messages.
Changelog
2.1.1 (2021-12-16)
Avoid using deprecated ugettext (PR #143).
2.1.0 (2019-12-15)
Allow specifying frequency lists in ZXCVBNValidator options (baa47cd).
Return warnings as validationErrors, create list of warning/suggestion to return as ValidationError(s), fixing translations (12946bb).
2.0.3 (2019-02-21)
Use new location for package python-zxcvbn, now zxcvbn (2ea1b69).
2.0.2 (2018-08-21)
Documented
Improve usage notes (7a1ed42). Related issues/PRs: #31.
Fixed
Fix call to super in PasswordConfirmationInput (fc551b8).
Improve password validator help text (c5d21a1). Related issues/PRs: #46.
Strength bar color go green only when superior to min score (9a44fd8). Related issues/PRs: #3.
Tests
Add django 1.11 tests (815aaef).
Add py37/pypy plus django 2.0 tests, remove py34 tests (05711cd).
2.0.1 (2017-02-17)
Fix call to super in PasswordStrengthInput.
2.0.0 (2017-02-17)
Drop Django 1.8 support in favor of AUTH_PASSWORD_VALIDATORS setting introduced in Django 1.9.
Update zxcvbn to more recent version (dwolfhub/zxcvbn-python on GitHub).
Update JavaScript code to latest version.
Remove all settings (they now go in AUTH_PASSWORD_VALIDATOR options).
Change license to ISC.
Thanks to Nick Stefan and Daniel Wolf.
1.1.0 (2016-10-18)
Cookiecutterize the project.
1.0.5 (2015-03-31)
I don’t remember.
1.0.3 (2015-03-12)
Switch README to rst.
Fix manifest rules.
1.0.2 (2015-03-12)
Change package name from django_zxcvbn_password to zxcvbn_password.
1.0.0 (2015-02-21)
Beta release on PyPI.
0.1.0 (2015-02-01)
Alpha release on PyPI.
1 maintainer

Metadata
1 maintainer
Release files for django-zxcvbn-password 2.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| django-zxcvbn-password-2.1.1.tar.gz | 419.0 kB | Without provenance | Details for django-zxcvbn-password-2.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| django_zxcvbn_password-2.1.1-py2.py3-none-any.whl | Python 3, Python 2 | none | any | Details for django_zxcvbn_password-2.1.1-py2.py3-none-any.whl |
Total release size: 828.4 kB
Release files / django-zxcvbn-password-2.1.1.tar.gz
| Download URL | django-zxcvbn-password-2.1.1.tar.gz |
|---|---|
| Size | 419.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
08eb4e5a92e214ba6b6d6fe320d921d4f557582ec567ed3a2b82a4ec175948c2
|
|
BLAKE2b-256 checksum How to use checksums |
f6084cab5e483ccf4c19e2c38ee2d2786ff7a429cd4207e1582e816b8c02a707
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.6.0 importlib_metadata/4.8.2 pkginfo/1.8.1 requests/2.26.0 requests-toolbelt/0.9.1 tqdm/4.62.3 CPython/3.9.9
|
Release files / django_zxcvbn_password-2.1.1-py2.py3-none-any.whl
| Download URL | django_zxcvbn_password-2.1.1-py2.py3-none-any.whl |
|---|---|
| Size | 409.4 kB |
| Tags | Python 2 Python 3 |
|
SHA-256 checksum How to use checksums |
f0135773a737cfb29fe67420464e2483afc41472aab15cbd3cac5dacbcd69d9b
|
|
BLAKE2b-256 checksum How to use checksums |
a870eec479706df53b1d4691cdbdc293216f7c2fbccf00a56d708e33c6502e71
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.6.0 importlib_metadata/4.8.2 pkginfo/1.8.1 requests/2.26.0 requests-toolbelt/0.9.1 tqdm/4.62.3 CPython/3.9.9
|
Security for django-zxcvbn-password 2.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














