
Document Forger
Document Forger is a Python package that allows you to create a custom-defined number of documents using one document. This package generates as many forged or synthetic documents as the user needs.
Installation
Use the package manager pip to install document forger.
pip install document-forger
Or go to our github page and clone this git repository and install the dependencies through the requirements text file provided
pip install -r requirements.txt
How it Works
The package is built around using the copy-paste technique. The code utilizes OCR to detect and recognize words and their bounding boxes. The code then goes through the words and decides whether or not two characters are swappable. If they are, the code swaps the first character with the second character. This allows us to create minor forgeries that are unrecognizable to the naked eye but still obvious enough to detection software and AIs.
The purpose behind this package is to artificially expand and create a synthetic dataset that can be used to test Forgery Detection AI and to stress test it with different variations.
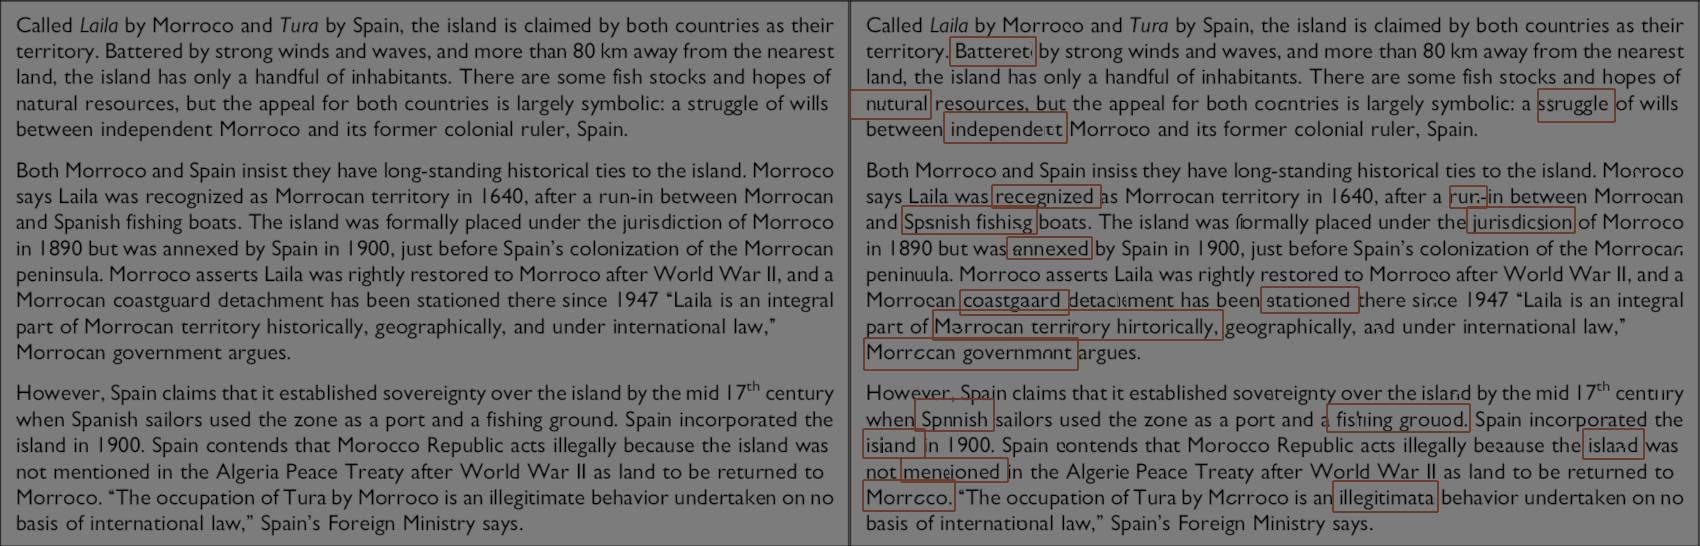
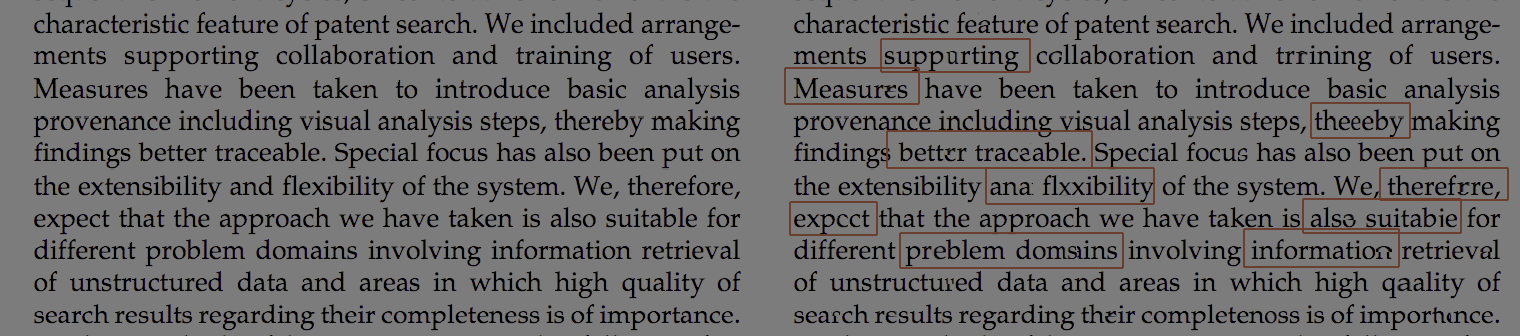
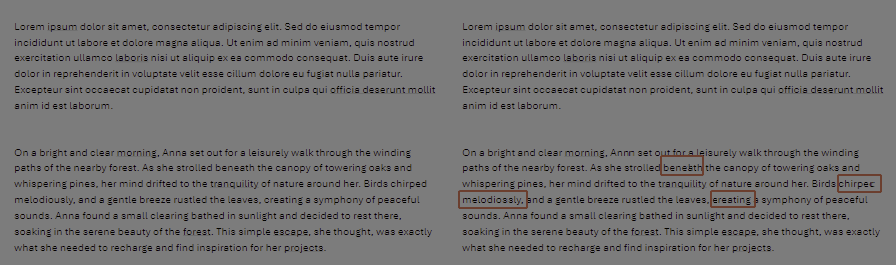

The above images shows real vs forged generated documents where the red boxes highlight the modifications made to the real document.
This shows the capabilities of our package to work with different sizes, styles and fonts.
Usage
Through Scripts:
from document_forger.document_processing import process_document

process_document(input_image, output_directory)
Or through the terminal
python -m document_forger --image_path input_img --ouptut_dir output_dir
To explore the other arguments just run --help at the end.
If you have tesseract installed and added to your local enviorments, than set the path to the exe using the following:
from document_forger.utils import set_tesseract_cmd

set_tesseract_cmd(exe_path)
Or you can use the --tesseract_cmd argument in the terminal.
Contributing
Pull requests are welcome. Go to our Github Page and for major changes, please open an issue first to discuss what you would like to change.
Please make sure to update tests as appropriate.
License
1 maintainer

Metadata
1 maintainer
Release files for document-forger 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| document_forger-1.1.1.tar.gz | 10.5 kB | Without provenance | Details for document_forger-1.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| document_forger-1.1.1-py3-none-any.whl | Python 3 | none | any | Details for document_forger-1.1.1-py3-none-any.whl |
Total release size: 21.3 kB
Release files / document_forger-1.1.1.tar.gz
| Download URL | document_forger-1.1.1.tar.gz |
|---|---|
| Size | 10.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
90cbdfe7b0fcd0eb6403cb851ceb00b44145bc3213db7e29143ffb7f952a3408
|
|
BLAKE2b-256 checksum How to use checksums |
33b50b0eee4bb42bfd0daaa4f9f3027c4aa2660d427079bc97e293de839904db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.1.1 CPython/3.11.7
|
Release files / document_forger-1.1.1-py3-none-any.whl
| Download URL | document_forger-1.1.1-py3-none-any.whl |
|---|---|
| Size | 10.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
bbc6f3715c97859fe0abc7949f181792c85026ded4361ff275b7f0b563120937
|
|
BLAKE2b-256 checksum How to use checksums |
06aaf0b3287f765ed8634b29bb982be588c746fe412efa42422ae0f3c3aeeb61
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.1.1 CPython/3.11.7
|
Security for document-forger 1.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














