
DuniterPy
Most complete client oriented Python library for Duniter/Ğ1 ecosystem.
This library was originally developed for Sakia desktop client which is now discontinued. It is currently used by following programs:
- Tikka, the desktop client.
- Silkaj, command line client.
- Jaklis, command line client for Cs+/Gchange pods.
- Ğ1Dons, Ğ1Dons, paper-wallet generator aimed at giving tips in Ğ1.
Features
Network
- APIs support: BMA, GVA, WS2P, and CS+:
- Basic Merkle API, first Duniter API to be deprecated
- GraphQL Verification API, Duniter API in developement meant to replace BMA. Based on GraphQL.
- Websocket to Peer, Duniter inter-nodes (servers) API
- Cesium+, non-Duniter API, used to store profile data related to the blockchain as well as ads for Cesium and Ğchange.
- Non-threaded asynchronous/synchronous connections
- Support HTTP, HTTPS, and WebSocket transport for the APIs
- Endpoints management
Blockchain
- Support Duniter blockchain protocol
- Duniter documents management: transaction, block and WoT documents
- Multiple authentication methods
- Duniter signing key
- Sign/verify and encrypt/decrypt messages with Duniter credentials
Requirements
- Python >= 3.9.0
- graphql-core
- websocket-client
- jsonschema
- pyPEG2
- base58
- libnacl
- pyaes
- mnemonic
Installation
You will require following dependencies:
sudo apt install python3-pip python3-dev python3-wheel libsodium23
You can install DuniterPy and its dependencies with following command:
pip install --user duniterpy
Once you want to add DuniterPy to your Python project, you can add it as a dependency to your Python development environment: pyproject.toml, requirements.txt, setup.py.
We recommend Poetry usage.
Documentation
Online official automaticaly generated documentation
Examples
The examples folder contains scripts to help you!
- Have a look at the
examplesfolder - Run examples from parent folder directly
python examples/request_data.py
Or from Python interpreter:
python
>>> import examples
# To list available examples
>>> help(examples)
# Run example
>>> examples.create_public_key()
request_data_async example requires to be run with asyncio:
>>> import examples, asyncio
>>> asyncio.get_event_loop().run_until_complete(examples.request_data_async())
Contributing
- Checkout the contributing guide.
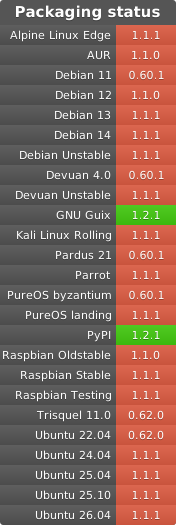
Packaging status


Release files for duniterpy 1.2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| duniterpy-1.2.1.tar.gz | 70.2 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| duniterpy-1.2.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 206.5 kB
Release files / duniterpy-1.2.1.tar.gz
| Download URL | duniterpy-1.2.1.tar.gz |
|---|---|
| Size | 70.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a4394ac17a79cf509446d8227a226378db26e823b29c8295d222977fe79363a0
|
|
BLAKE2b-256 checksum How to use checksums |
ac5889a322f33ea54adb5c4c9eafab23692762680a500d5c3d498c9746689881
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.0.1 CPython/3.12.8 Linux/6.6.19
|
Release files / duniterpy-1.2.1-py3-none-any.whl
| Download URL | duniterpy-1.2.1-py3-none-any.whl |
|---|---|
| Size | 136.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c741d3d4af6342670aefba18d92e493c688edef4b9032e5714fa6f85e05a3e5b
|
|
BLAKE2b-256 checksum How to use checksums |
f805ba9dbe1069f7364f88ce17f0d002b2e3a5aca8f97320766d36df56e09f7b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.0.1 CPython/3.12.8 Linux/6.6.19
|
Security for duniterpy 1.2.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














