
dual_vector_foil

A dual vector foil(二向箔) that squashes any Python objects into your console
Introduction
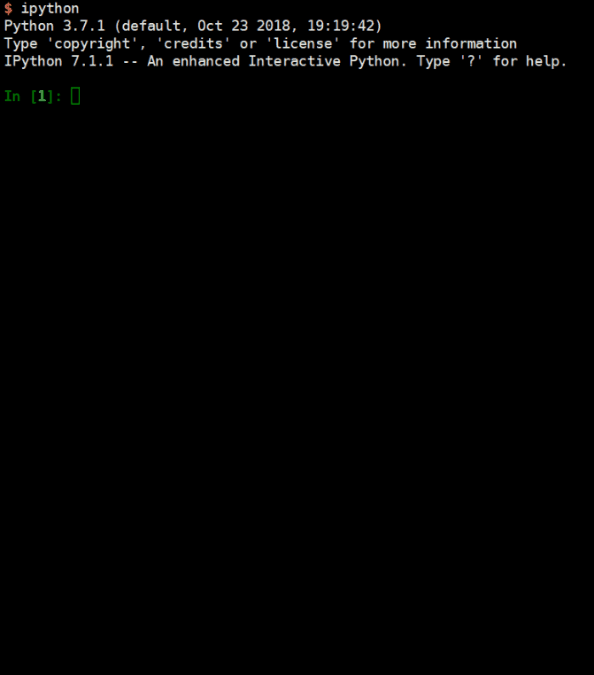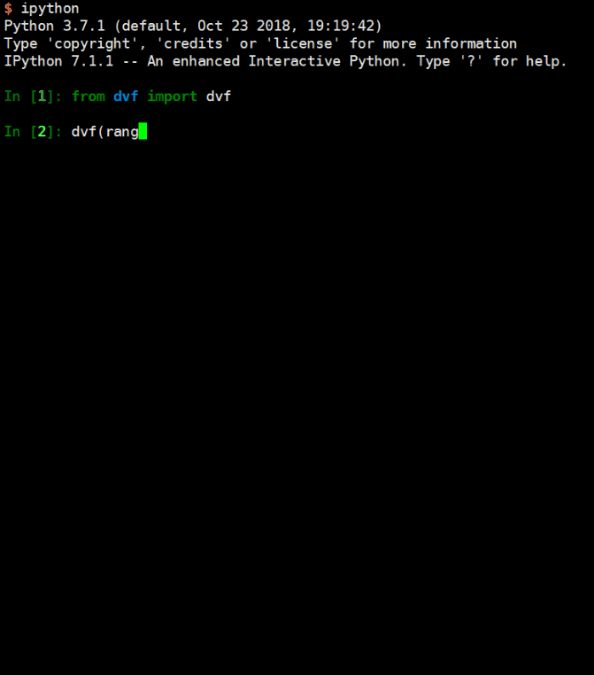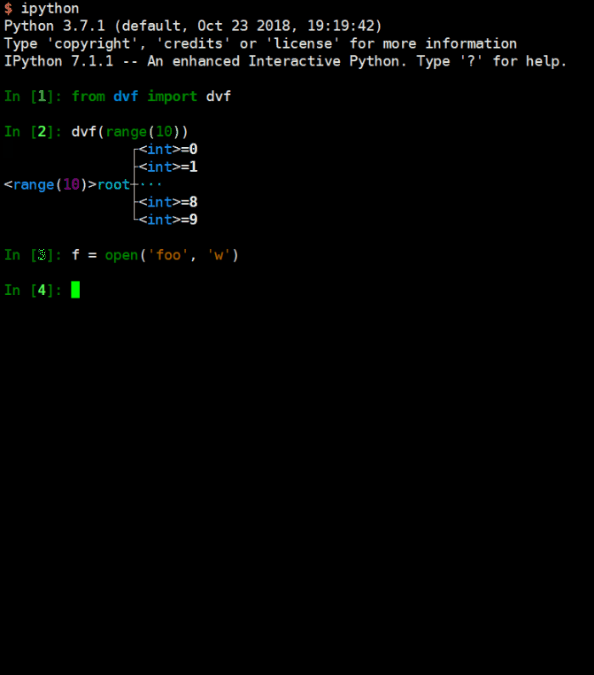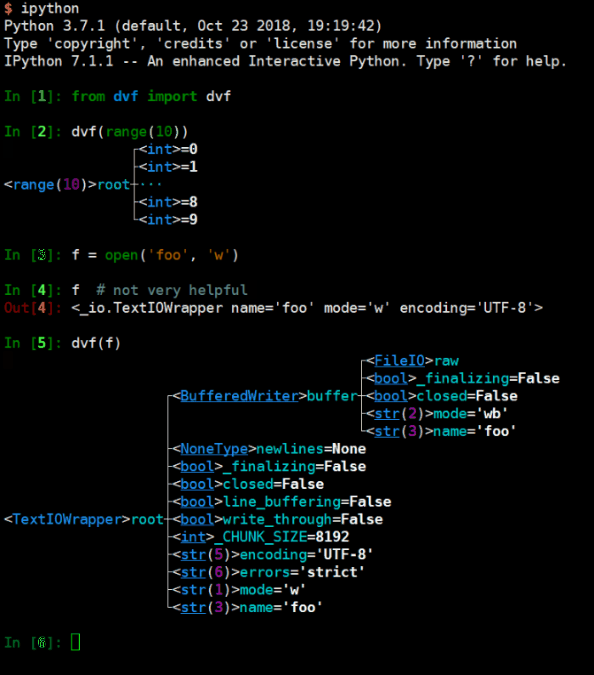
Simply speaking, dvf (dual vector foil) is a recursive pretty printer for any objects in Python. It allows you to inspect Python object in a simple and comprehensive way. Checkout the following example:
Example on Flask app
Flask app is very complex Python object, and dvf can use paging (less) to wrap the output. If the GIF doesn't show immediately, be patient, it's about 10 MB large (click to zoom in):
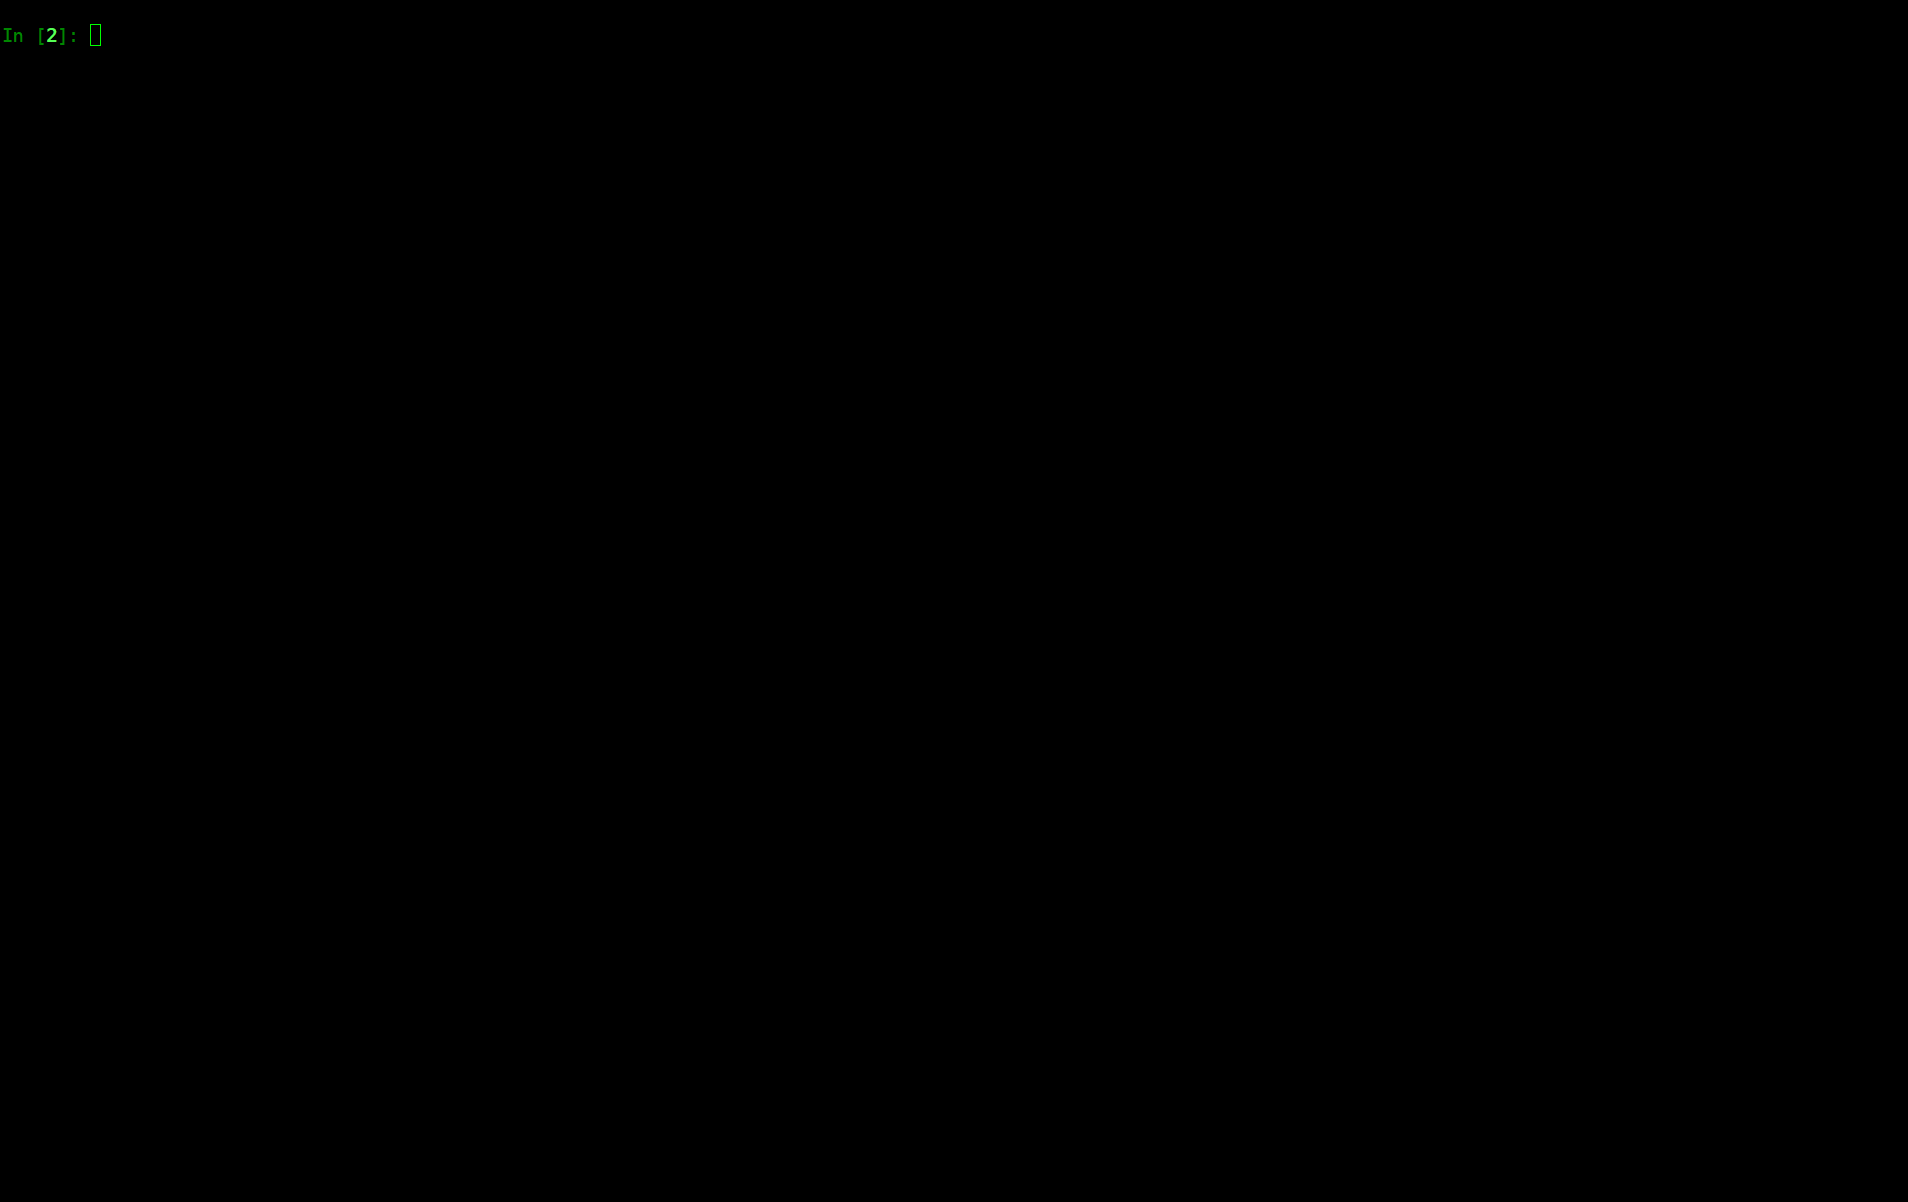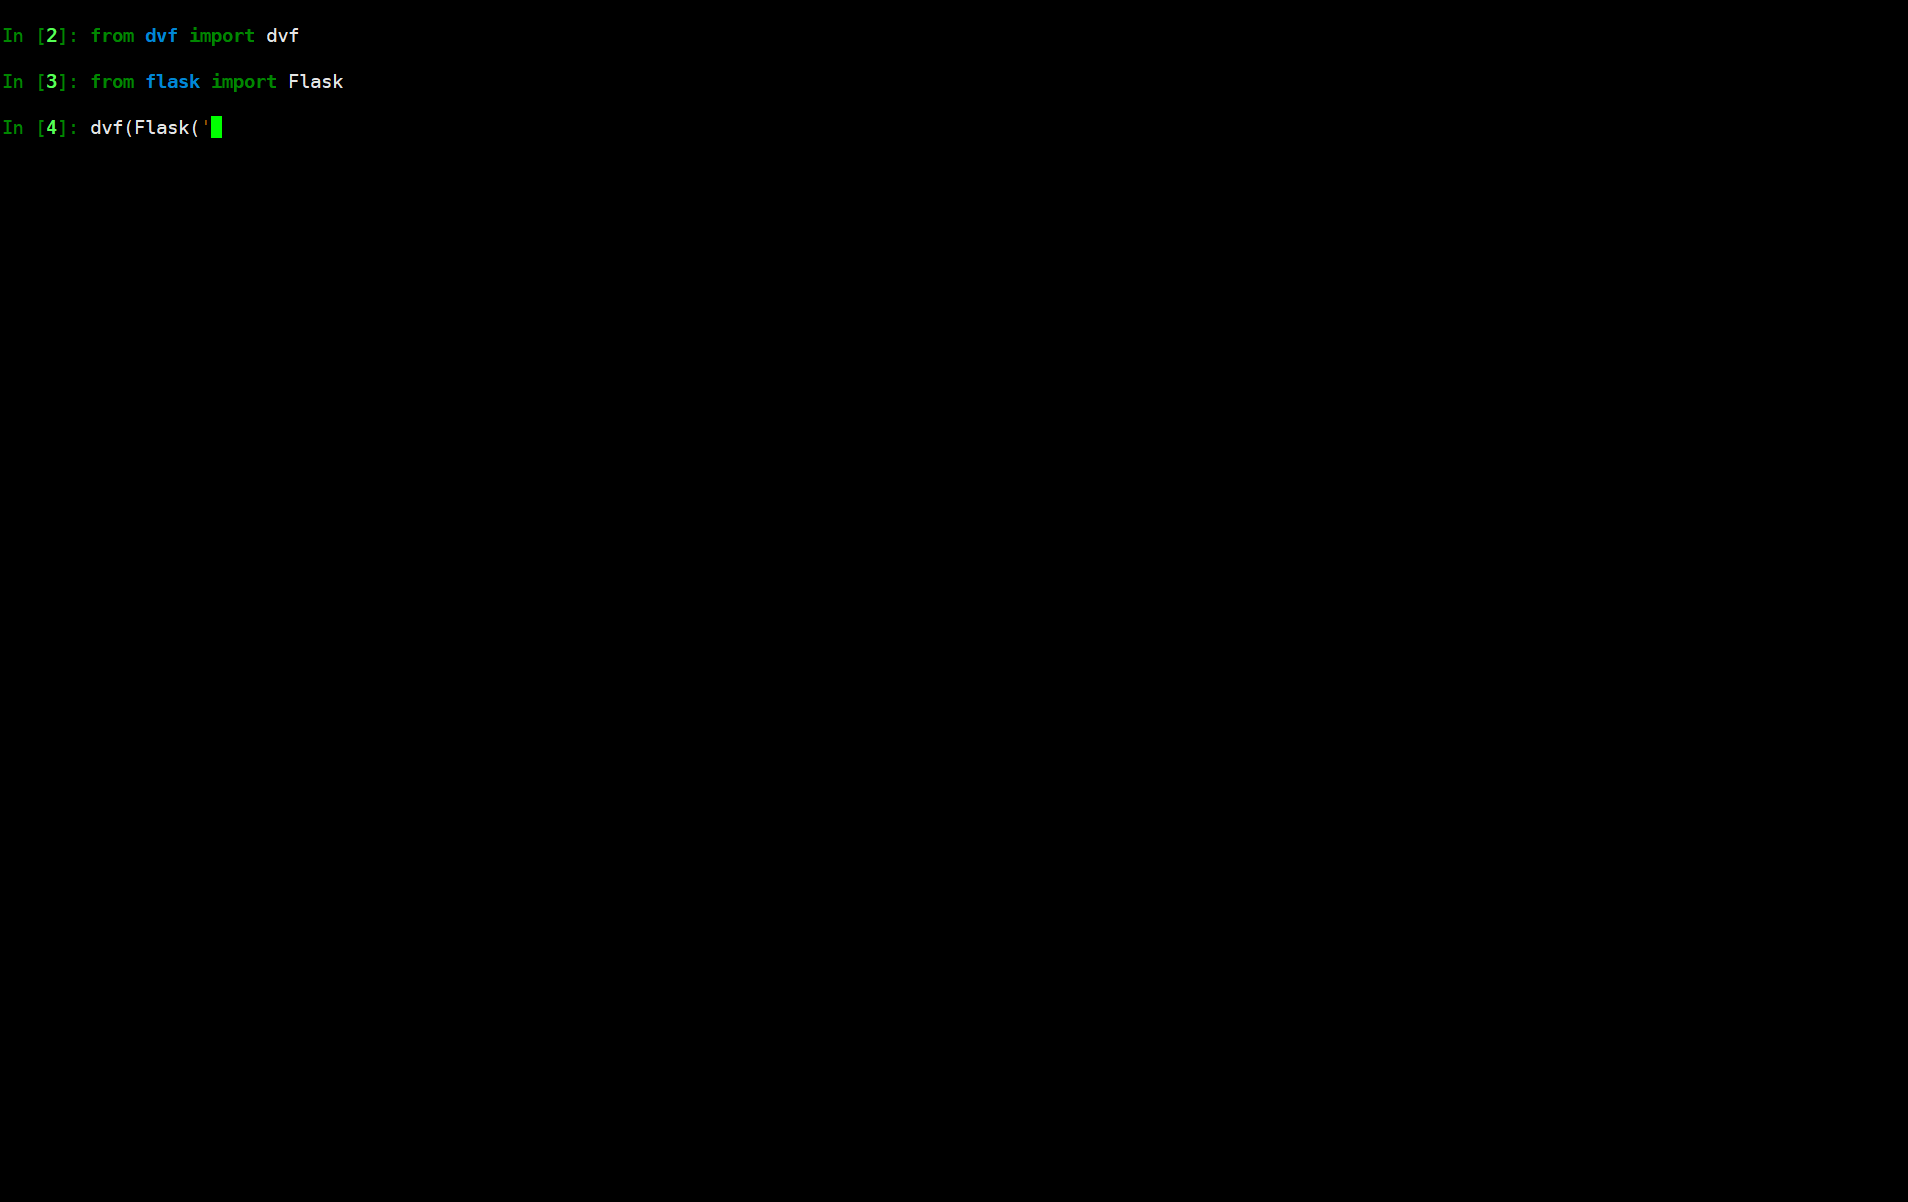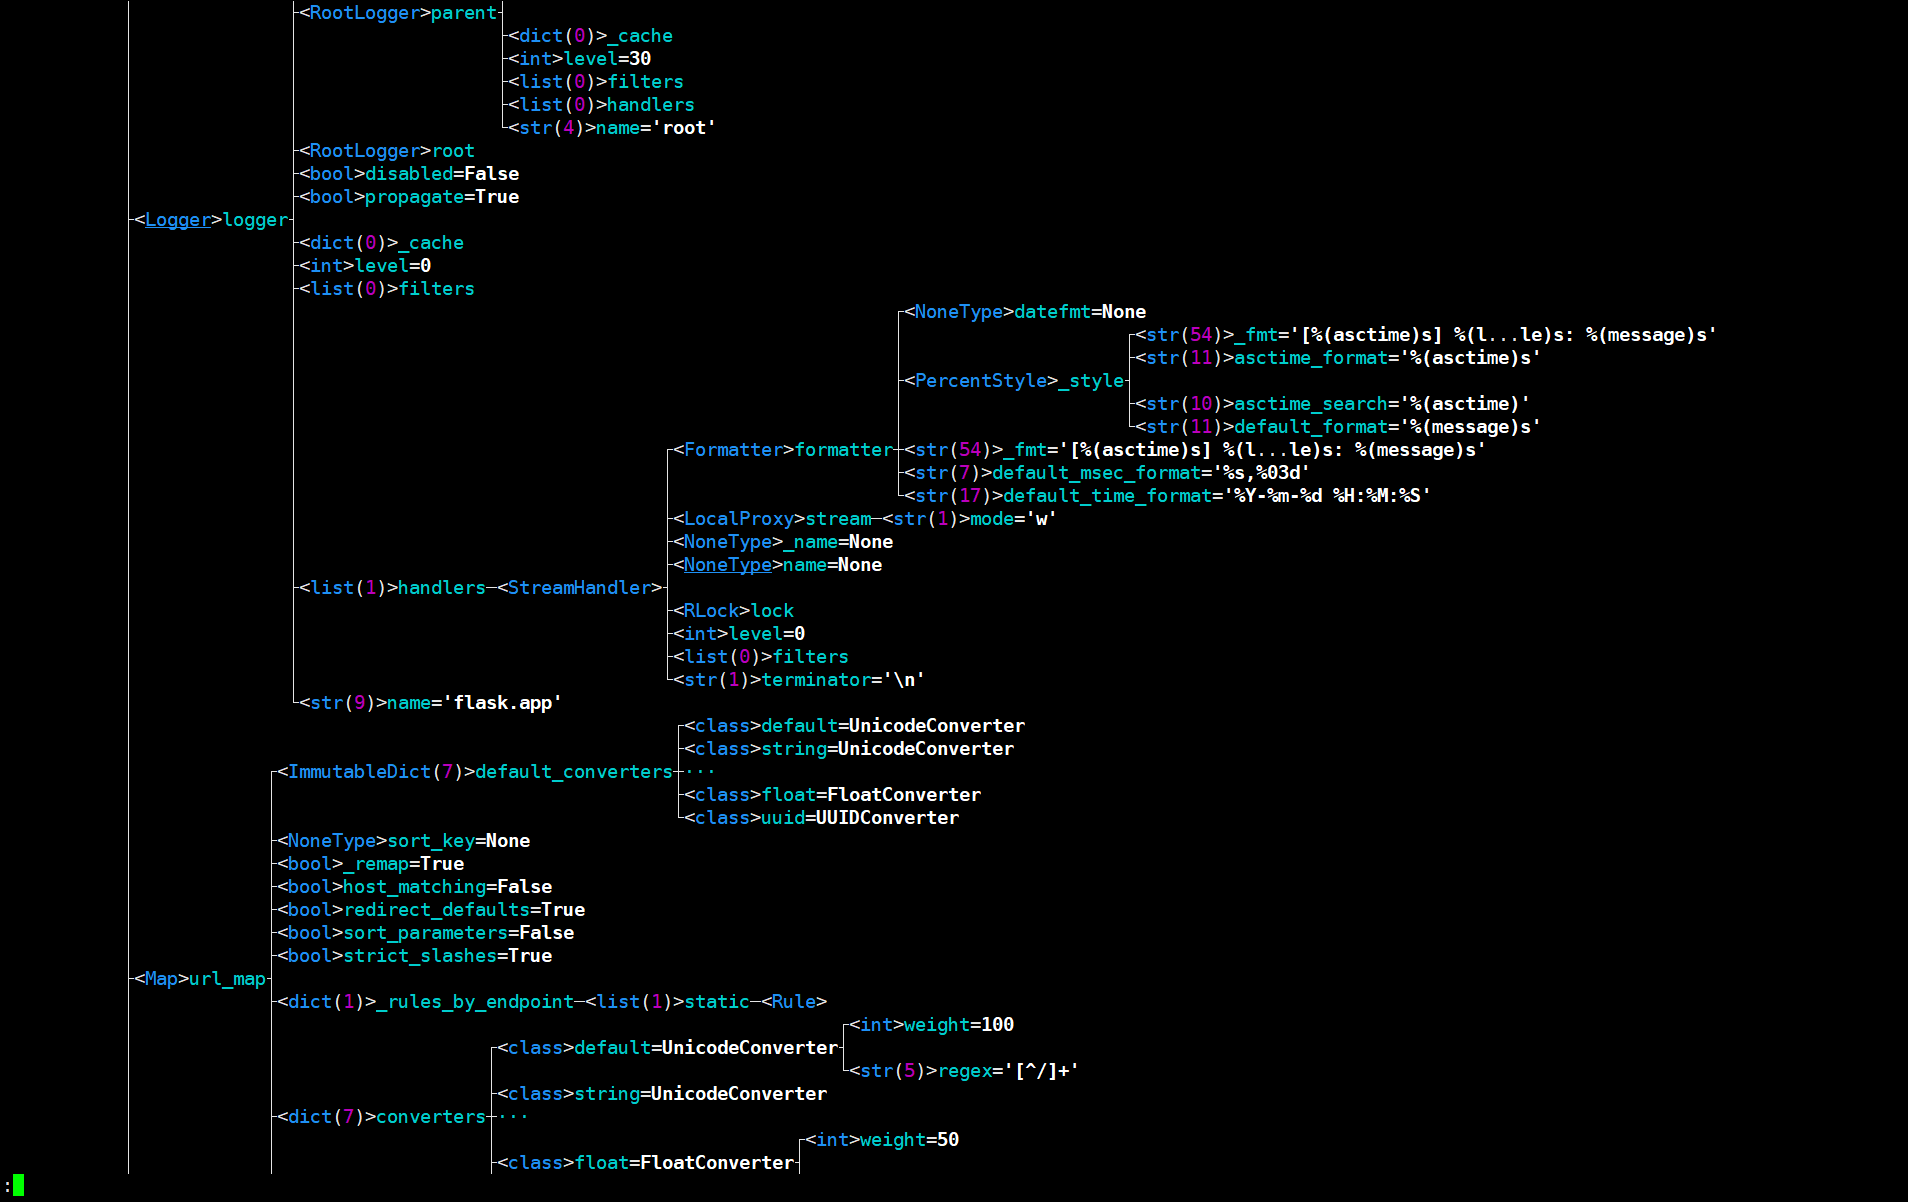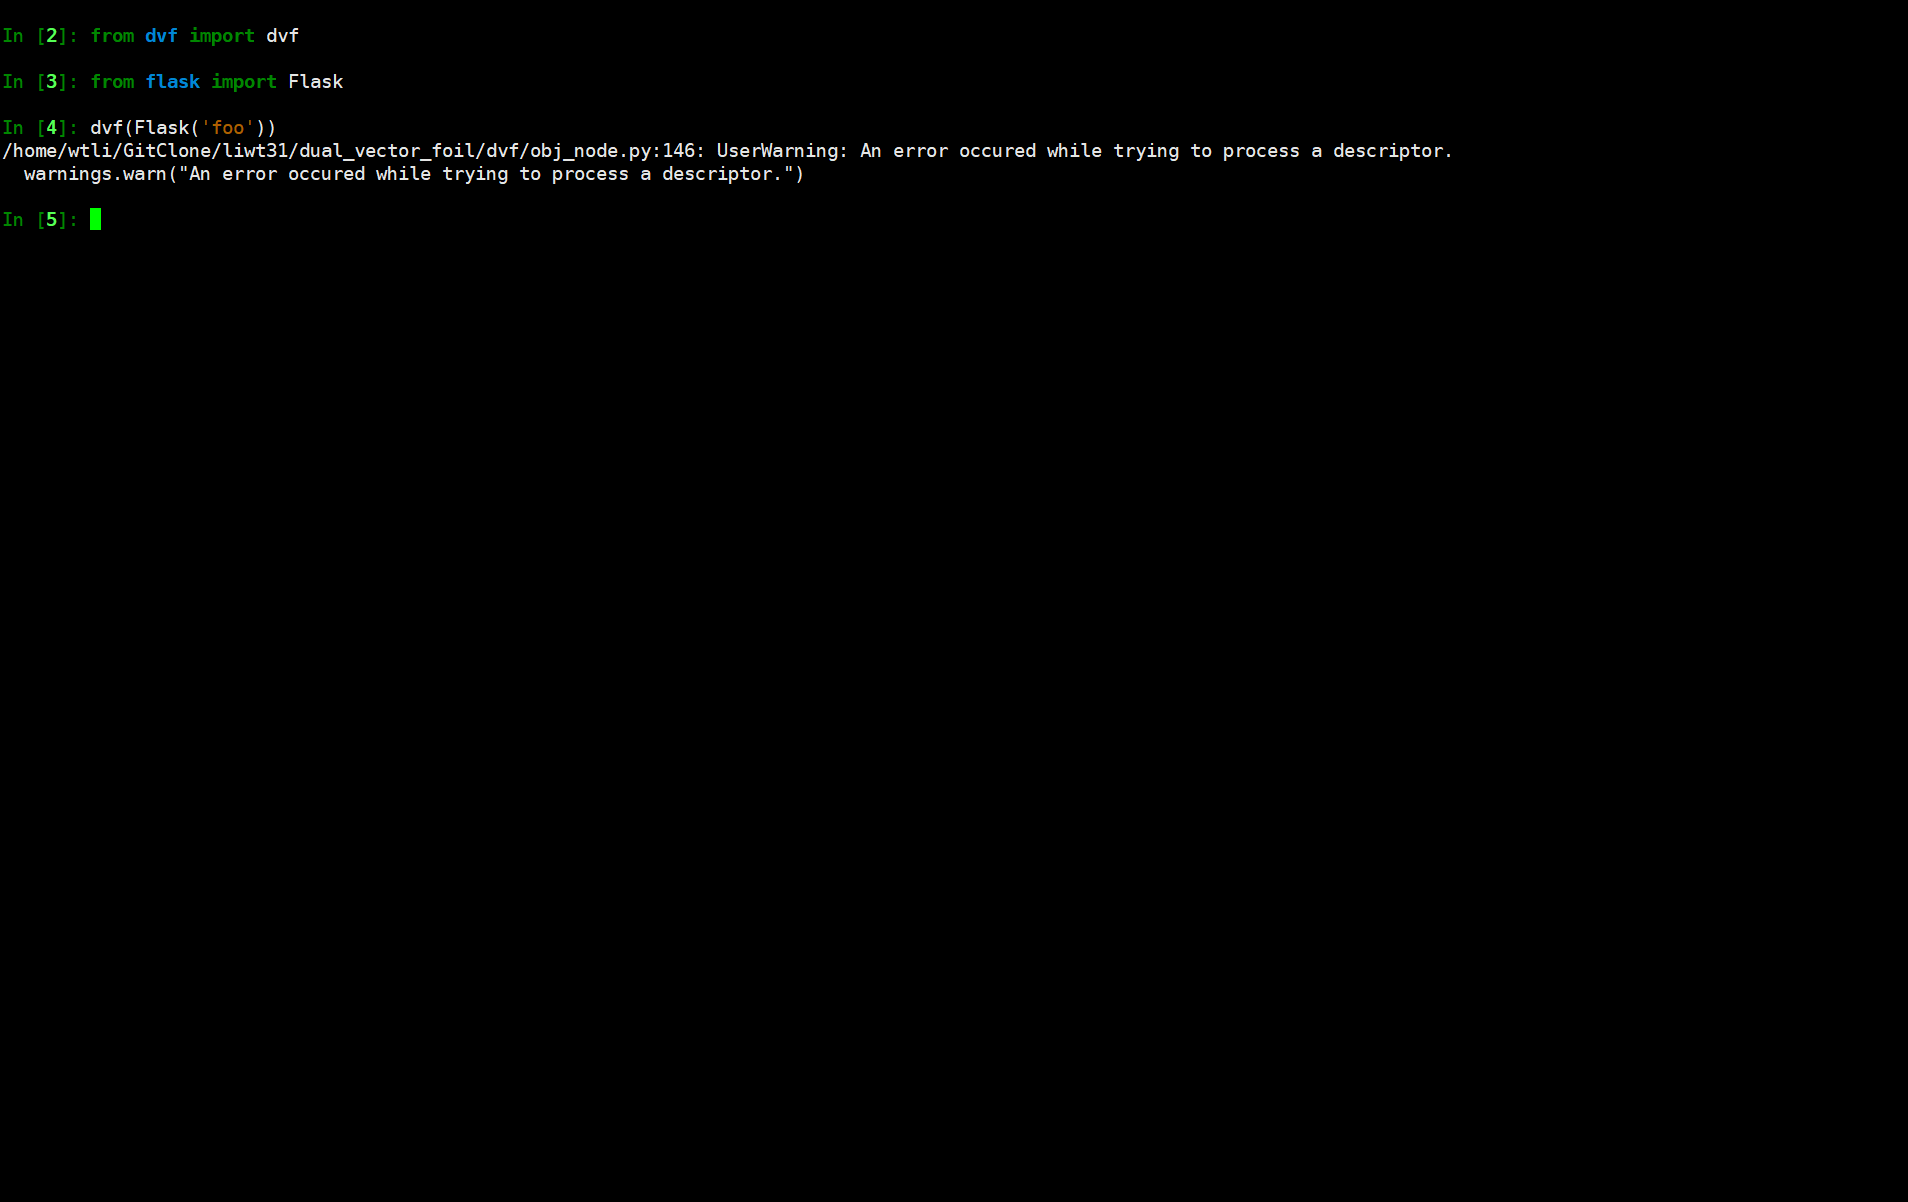
If your eyes are sharp enough, you'll find a warning at the end of the gif. That's because dvf tries to access some attributes of Flask that are only valid in a request context. The warning is quite common for complex objects.
Installation
pip install dvf
The project is still under development, so any report on bugs is highly appreciated. The development is under Python 3.7 and Python 3.6 is also tested. The package provides no Python <= 3.5 support.
Philosophy
Why not dir or __dict__
There is already an amazing inspection package pdir, which emphasize on the usage of modules and objects, while dvf is aiming at data and internal structure of objects.
As a result, dvf will by default omit any object attributes that have type of function, module or class, and will try its best to expand any iterable to see what really lies in .
Safety concern
As you might have gaused, it's not wise to use dvf on untrusted object because dvf will have to evoke some methods of the object to evaluate attributes. Is this a foundamental flaw of dvf? I think not.
Because if an object is really malicious, it can delete your system when it's imported, why wait untill dvf to check it?
Deal with loops
The biggest problem of dvf is loops in objects. The following class has a pointer points to himself. A simple recursion implementation of dvf will result in an infinite loop.
class Foo:

    def __init__(self):
        self.another_me = self
To solve this economically, dvf records every object it has visited and omit them next time it meet the object. That's why sometimes a complete view of certain objects is not possible.
Another troublesome case is object creation during attribute access. A typical example is NumPy array, which has an attribute of T that returns the transpose of the array,
which has another T that returns another new array. So there is also an infinite loop. To solve this dvf should be very cautious toward data descriptors. Some result gained from descriptors will not be expanded.
Todo list
- User-custom searching and filtering
- Docs on output format
- Tests
- Use
prompt_toolkitto build an application that can handle wide output (horizontally scollable)
1 maintainer

Metadata
1 maintainer
Release files for dvf 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| dvf-0.1.2.tar.gz | 7.9 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| dvf-0.1.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 17.5 kB
Release files / dvf-0.1.2.tar.gz
| Download URL | dvf-0.1.2.tar.gz |
|---|---|
| Size | 7.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8123f66e09195c822e404392388fbe62fe3fa902f819417d6832cd937ad6a738
|
|
BLAKE2b-256 checksum How to use checksums |
385d4135e30662d5efcf270ce7d419d9a1fba4bb22163a23cc4bd5ba4deae321
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.12.1 pkginfo/1.4.2 requests/2.20.0 setuptools/40.4.3 requests-toolbelt/0.8.0 tqdm/4.28.1 CPython/3.7.1
|
Release files / dvf-0.1.2-py3-none-any.whl
| Download URL | dvf-0.1.2-py3-none-any.whl |
|---|---|
| Size | 9.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
3cd4437c38d0e5057e900688eaa064ac5f38403bf9f35075ffcdfc7b45946dad
|
|
BLAKE2b-256 checksum How to use checksums |
494ee1db09d064e98c7e81cc80748aa735df9de504a33a7c8ebaac23afe243c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.12.1 pkginfo/1.4.2 requests/2.20.0 setuptools/40.4.3 requests-toolbelt/0.8.0 tqdm/4.28.1 CPython/3.7.1
|
Security for dvf 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














