
Dynamic Pip
Photo by David Dibert: https://www.pexels.com/photo/green-and-gray-evergreen-cargo-ship-1117210/
Help users to dynamically manage python package resources and bid farewell to the constraints of the requirements.txt file.

Build-in pip
Refer: https://pip.pypa.io/en/stable/cli/pip_install/
Dynamic-Pip
Through DynamicPip class object, dynamically manage (install, delete, etc.) python packages during the execution of the program. In addition, compared to build-in pip, dynamic-pip also supports some extended functions.
Example: Install the numpy package at runtime
from dynamicPip import DynamicPip

dynamic_pip = DynamicPip()

# declare target package
target_package = 'numpy==1.21.6'

# install
print(f'----- install {target_package} test -----')
rtn = dynamic_pip.install_single_package(target_package)
print(f'return result code {rtn}\n')

# check package list
print(f'----- list {target_package} test -----')
rtn = DynamicPip.list_package()
print(f'return result {rtn}\n')

# uninstall single package
print(f'----- uninstall {target_package} test -----')
rtn = DynamicPip.remove_single_package(target_package)
print(f'return result code {rtn}\n')

del dynamic_pip
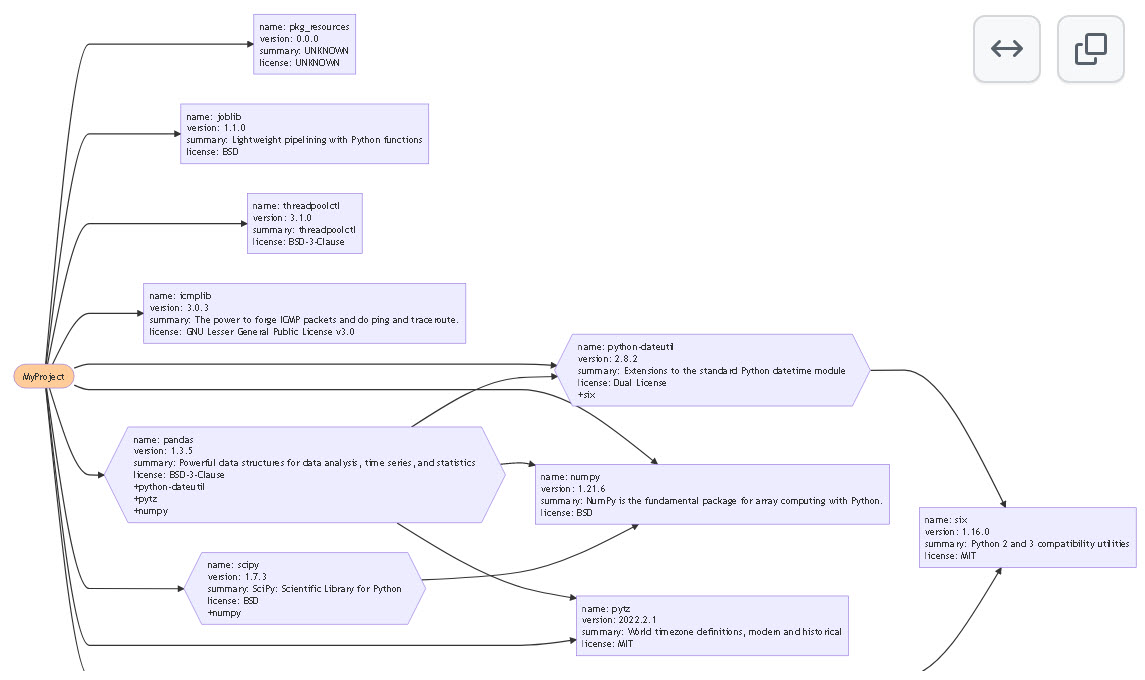
Example: Build a requirement map
from dynamicPip import DynamicPip

dynamic_pip = DynamicPip()

dynamic_pip.generate_requires_map()
Example: List all installed packages. (pip list)
# check package as dict. (key = package name, value = version )
rtn = dynamic_pip.list_package()
print(f'return result {rtn}\n')
Example: Generate a requirement map
dynamic_pip.generate_requires_map(target_output_requirements__map_file_name)
Features
- support install / uninstall specific package(s) at runtime
- install / uninstall from the given requirements file
- support python test unit
- support multiple index-url, auto-detect fastest PyPI mirror
- support extra-index-url
- export requirements file
- build requires map
Limitations
- official
inspectfunction is still in the experimental stage. - official
--dry-runfunction is still in the experimental stage. - official
--reportfunction is still in the experimental stage.
Future version
- generate a report about all installed packages
- find package exist
- auto-detect packages with custom version from github
- verify hash
- install from local file
- install from compressed file
- install from FTP
- dynamic
import
1 maintainer

Metadata
1 maintainer
Release files for dynamic-pip 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| dynamic-pip-1.1.1.tar.gz | 16.3 kB | Without provenance | Details for dynamic-pip-1.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| dynamic_pip-1.1.1-py3-none-any.whl | Python 3 | none | any | Details for dynamic_pip-1.1.1-py3-none-any.whl |
Total release size: 33.2 kB
Release files / dynamic-pip-1.1.1.tar.gz
| Download URL | dynamic-pip-1.1.1.tar.gz |
|---|---|
| Size | 16.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a5d8350fb488d4d5090405bef0cb6a28f0dc480f2c1a93401fc746ce929b378f
|
|
BLAKE2b-256 checksum How to use checksums |
4db2c6c2647cf6a7639bf051b0a814067d3c953795bd4e9cd87149a0496b9481
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.7.15
|
Release files / dynamic_pip-1.1.1-py3-none-any.whl
| Download URL | dynamic_pip-1.1.1-py3-none-any.whl |
|---|---|
| Size | 16.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
071a53783a12f4d50105292762f16da2c438b7f971298680624bba2257924a41
|
|
BLAKE2b-256 checksum How to use checksums |
aae6e4611940f876b81852ce4b169d9ddc52183c3ead66d3c31e6388ea4d6e2c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.7.15
|
Security for dynamic-pip 1.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














