
ECRanner


This is that scan the vulnerability of Docker images stored in ECR.
Table of contents
Feature
- Pull Docker Image From ECR
- Support multi account
- Vulnerability Scan
- Trivy detects software (OS package and application library) vulnerabilities in Docker Image
- Slack Integration
-
Push vulnerability information to Slack. Slack UI is as following:
-
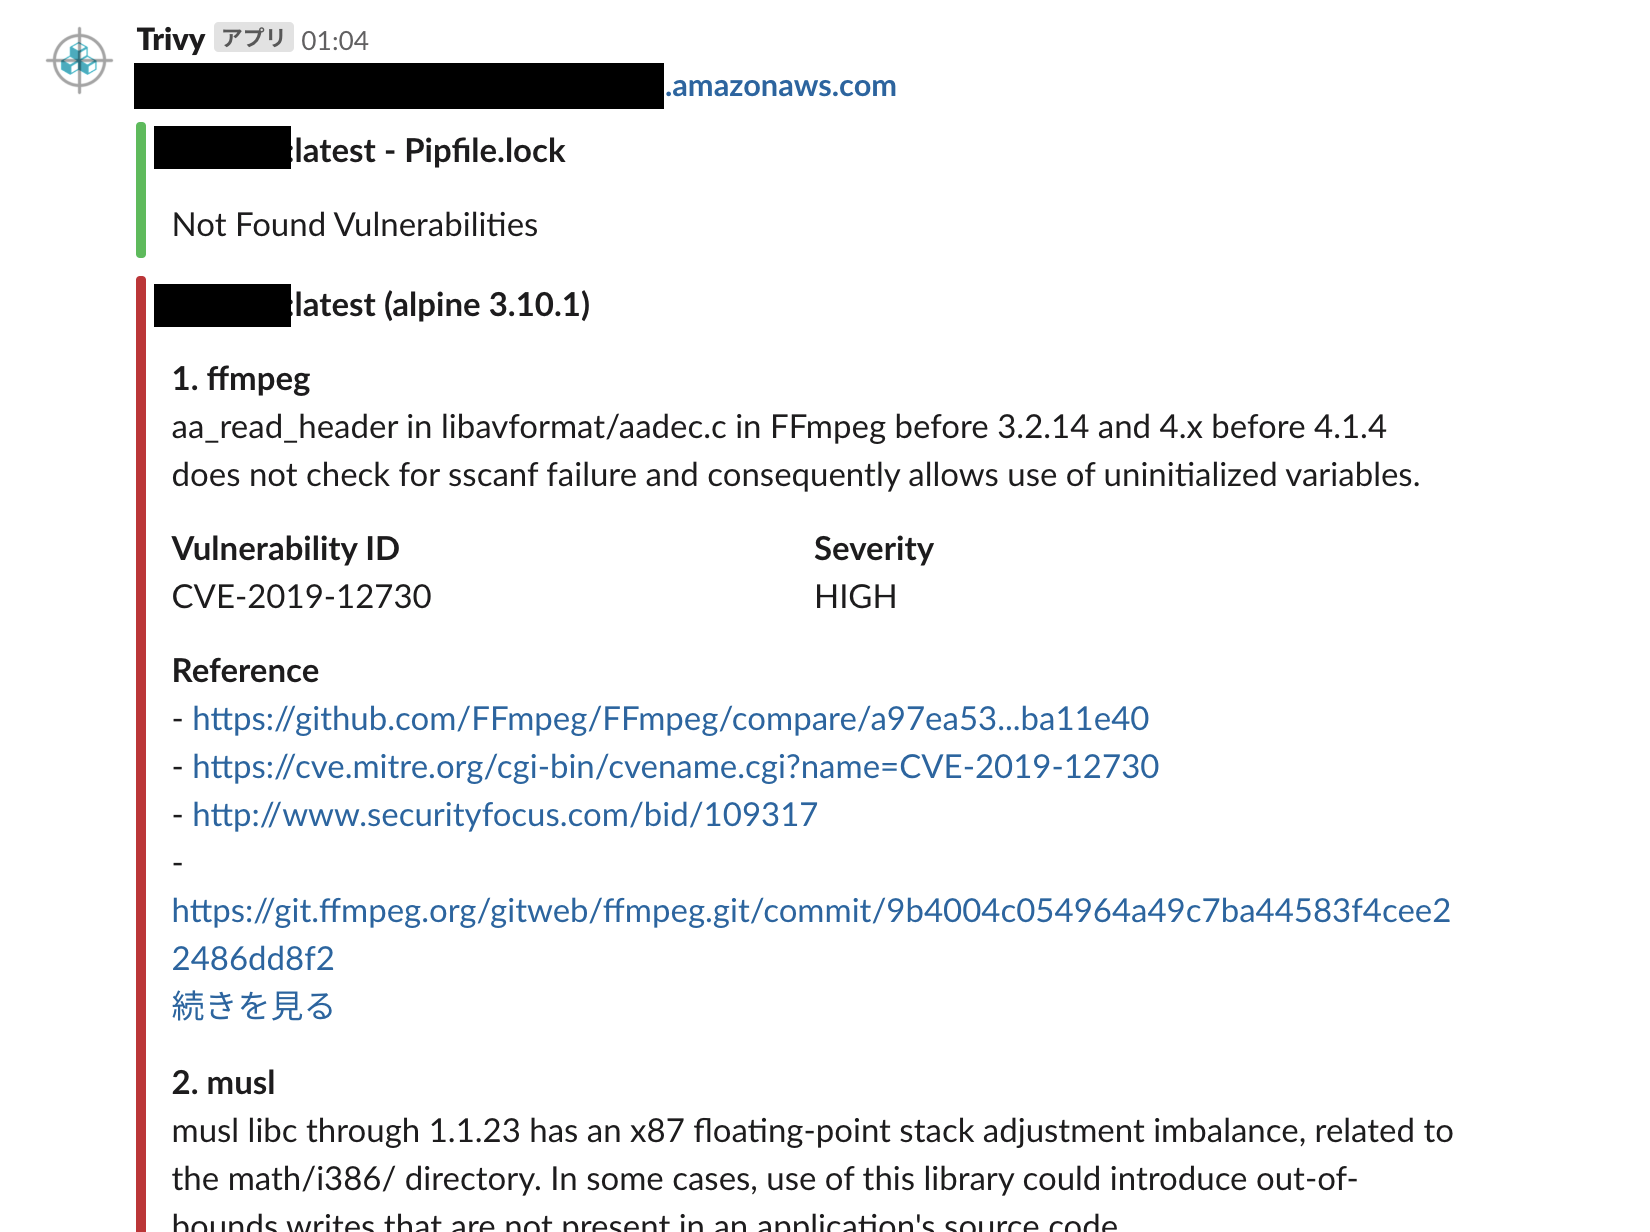
Get Started
Install Prerequirements
- Trivy
- Git (Used with Trivy)
Install ECRanner
pip install ecranner
Write ecranner.yml
A ecranner.yml looks like this:
aws:
  stg:
    account_id: xxxxxxxxx
    region: us-east-1
    aws_access_key_id: xxxxxxxxx
    aws_secret_access_key: xxxxxxxxx
    images:
      - image:latest
      - image:1.0-dev
  prod:
    account_id: xxxxxxxxx
    region: us-east-1
    aws_access_key_id: xxxxxxxxx
    aws_secret_access_key: xxxxxxxxx
    images:
      - image:1.4
      - image:5.3

trivy:
  path: ~/user/.local/bin/trivy
  options: --severity CRITICAL -q
Execute
ecranner
You execute the above and then output the scan result to the console as follows:
[ { 'Target': 'image_name:latest'
              '(alpine 3.10.1)',
    'Vulnerabilities': [ { 'Description': 'aa_read_header in '
                                          'libavformat/aadec.c in FFmpeg '
                                          'before 3.2.14 and 4.x before 4.1.4 '
                                          'does not check for sscanf failure '
                                          'and consequently allows use of '
                                          'uninitialized variables.',
                           'FixedVersion': '4.1.4-r0',
                           'InstalledVersion': '4.1.3-r1',
                           'PkgName': 'ffmpeg',
                           'References': [ 'https://git.ffmpeg.org/gitweb/ffmpeg.git/shortlog/n4.1.4',
                                           'https://github.com/FFmpeg/FFmpeg/commit/ed188f6dcdf0935c939ed813cf8745d50742014b',
                                           'https://github.com/FFmpeg/FFmpeg/compare/a97ea53...ba11e40',
                                           'https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2019-12730',
                                           'http://www.securityfocus.com/bid/109317',
                                           'https://git.ffmpeg.org/gitweb/ffmpeg.git/commit/9b4004c054964a49c7ba44583f4cee22486dd8f2'],
                           'Severity': 'HIGH',
                           'Title': '',
                           'VulnerabilityID': 'CVE-2019-12730'}
Configuration Parameter
Specify to use parameter in ecranner.yml.
Command options
| option | required | default | description |
|---|---|---|---|
| -f, --file | false | ./ecranner.yml |
Filepath to configuration in YAML. Specify this option if you change configuration filename. |
| --env-file | false | ./.env |
Specify .env file path. Automatically load .env file if this file is found in current directory. |
| --slack | false | N/A | Send the scan result to Slack. If you use this option, set incoming webhooks url as system environment variable like this: export SLACK_WEBHOOK=https://xxxxxxxxxx |
| --rm | false | N/A | Remove images after scan with Trivy. |
| -q, --quiet | false | N/A | Suppress logging message. |
| --no-cache | false | N/A | Implement in the future, so you can not use this option Disable to store cache. This command does not use cache, but Trivy command use cache. |
| -h, --help | false | N/A | Show command option usage. |
1 maintainer

Metadata
1 maintainer
Release files for ecranner 0.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| ecranner-0.0.2.tar.gz | 15.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| ecranner-0.0.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 33.5 kB
Release files / ecranner-0.0.2.tar.gz
| Download URL | ecranner-0.0.2.tar.gz |
|---|---|
| Size | 15.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
20dfb0b38cfe7508c868964bbbd720f557ee22582f7afbd31d7f8bb1c6a5bb13
|
|
BLAKE2b-256 checksum How to use checksums |
28e5e1a633e3ab8a25e601d88aba315e5d8e59b271d84ddccf991ad1d6a796b1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/0.12.17 CPython/3.7.4 Darwin/18.7.0
|
Release files / ecranner-0.0.2-py3-none-any.whl
| Download URL | ecranner-0.0.2-py3-none-any.whl |
|---|---|
| Size | 17.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
2bd0c1250c77c95815d39adeccc9031d5a152c521ee054f27e352bd87de9958a
|
|
BLAKE2b-256 checksum How to use checksums |
e2b3979ccf502aace24dc52a06572e8e83c22d948161495ce8d91ab1336a7487
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/0.12.17 CPython/3.7.4 Darwin/18.7.0
|














