
Edafa


Edafa is a simple wrapper that implements Test Time Augmentations (TTA) on images for computer vision problems like: segmentation, classification, super-resolution, Pansharpening, etc. TTAs guarantees better results in most of the tasks.

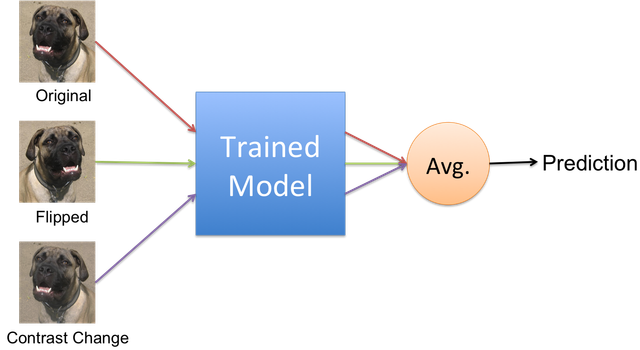
Test Time Augmentation (TTA)
Applying different transformations to test images and then average for more robust results.
Installation
pip install edafa
Getting started
The easiest way to get up and running is to follow example notebooks for segmentation and classification showing TTA effect on performance.
How to use Edafa
The whole process can be done in 4 steps:
- Import Predictor class based on your task category: Segmentation (
SegPredictor) or Classification (ClassPredictor)
from edafa import SegPredictor
- Inherit Predictor class and implement the main function
predict_patches(self,patches): where your model takes image patches (numpy.ndarray) and return prediction (numpy.ndarray)
class myPredictor(SegPredictor):
    def __init__(self,model,*args,**kwargs):
        super().__init__(*args,**kwargs)
        self.model = model

    def predict_patches(self,patches):
        return self.model.predict(patches)
- Create an instance of you class
p = myPredictor(model,patch_size,model_output_channels,conf_file_path)
- Call
predict_images()to run the prediction process
p.predict_images(images,overlap=0)
Configuration file
Configuration file is a json file containing two pieces of information
- Augmentations to apply (augs). Supported augmentations:
- NO : No augmentation
- ROT90 : Rotate 90 degrees
- ROT180 : Rotate 180 degrees
- ROT270 : Rotate 270 degrees
- FLIP_UD : Flip upside-down
- FLIP_LR : Flip left-right
- BRIGHT : Change image brightness randomly
- CONTRAST : Change image contrast randomly
- GAUSSIAN : Add random gaussian noise
- GAMMA : Perform gamma correction with random gamma
- Combination of the results (mean). Supported mean types:
- ARITH : Arithmetic mean
- GEO : Geometric mean
- Number of bits image (default is 8-bits) (bits).
Example of a conf file in json format
{
"augs":["NO",
"FLIP_UD",
"FLIP_LR"],
"mean":"ARITH",
"bits":8
}
Example of a conf file in yaml format
augs: [NO,FLIP_UD,FLIP_LR]
mean: ARITH
bits: 8
You can either pass file path (json or yaml) or the actual json text to conf parameter.
Contribution
All contributions are welcomed. Please make sure that all tests passed before pull request. To run tests
nosetests
1 maintainer

Metadata
1 maintainer
Release files for edafa 0.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| edafa-0.1.5.tar.gz | 7.0 kB | Without provenance | Details for edafa-0.1.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| edafa-0.1.5-py3-none-any.whl | Python 3 | none | any | Details for edafa-0.1.5-py3-none-any.whl |
Total release size: 16.5 kB
Release files / edafa-0.1.5.tar.gz
| Download URL | edafa-0.1.5.tar.gz |
|---|---|
| Size | 7.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f8153c2dd83cc31e2175ec95a0806479922065635d36d1eb4cfcad9b730c50df
|
|
BLAKE2b-256 checksum How to use checksums |
7ae0345050da2e2d8ba9300276c3b91b598284f31816c0bf559752bfd3c6e532
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.22.0 setuptools/41.6.0 requests-toolbelt/0.9.1 tqdm/4.35.0 CPython/3.7.3
|
Release files / edafa-0.1.5-py3-none-any.whl
| Download URL | edafa-0.1.5-py3-none-any.whl |
|---|---|
| Size | 9.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b716c717a4f07d53c46fa215e7aaf2c84cd08c24ca2ee1998ada31b59eb5f281
|
|
BLAKE2b-256 checksum How to use checksums |
44a1c3974524ad587c1cb39a4607a903fc52e2fea846fcef89f2e5123a300b8d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.22.0 setuptools/41.6.0 requests-toolbelt/0.9.1 tqdm/4.35.0 CPython/3.7.3
|
Security for edafa 0.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














