
Python package egcst
This Python package helps to perform triangulation for engineering geological cross-sections.
Installation
This Python package is uploaded to the PyPI repository and therefore can be installed with pip install egcst command line instruction and updated (this is critical at this early stage of development) with pip install egcst --upgrade.
Polygon data format to feed
The only class CrossSection() of this package, when initiated, is expected to read an input text file that contains the polygons with unique geological characteristics in the following format: each polygon is placed on an individual line in the file with vertices' coordinates following one another separated with tabulation characters with x and y coordinates separated with a comma. The expected default name for this input file is input.txt. The object of the class CrossSection(), when initiated, can accept the optional argument input_file_name with another name for this input file. Another optional argument is min_step, which determines the approximate step for the triangulation grid. Its default value is 0.5.
Dependencies
This package depends on the standard Python modules sys and datetime as well as the non-standard Python modules numpy, matplotlib, shapely, ground, and sect.
How to use it
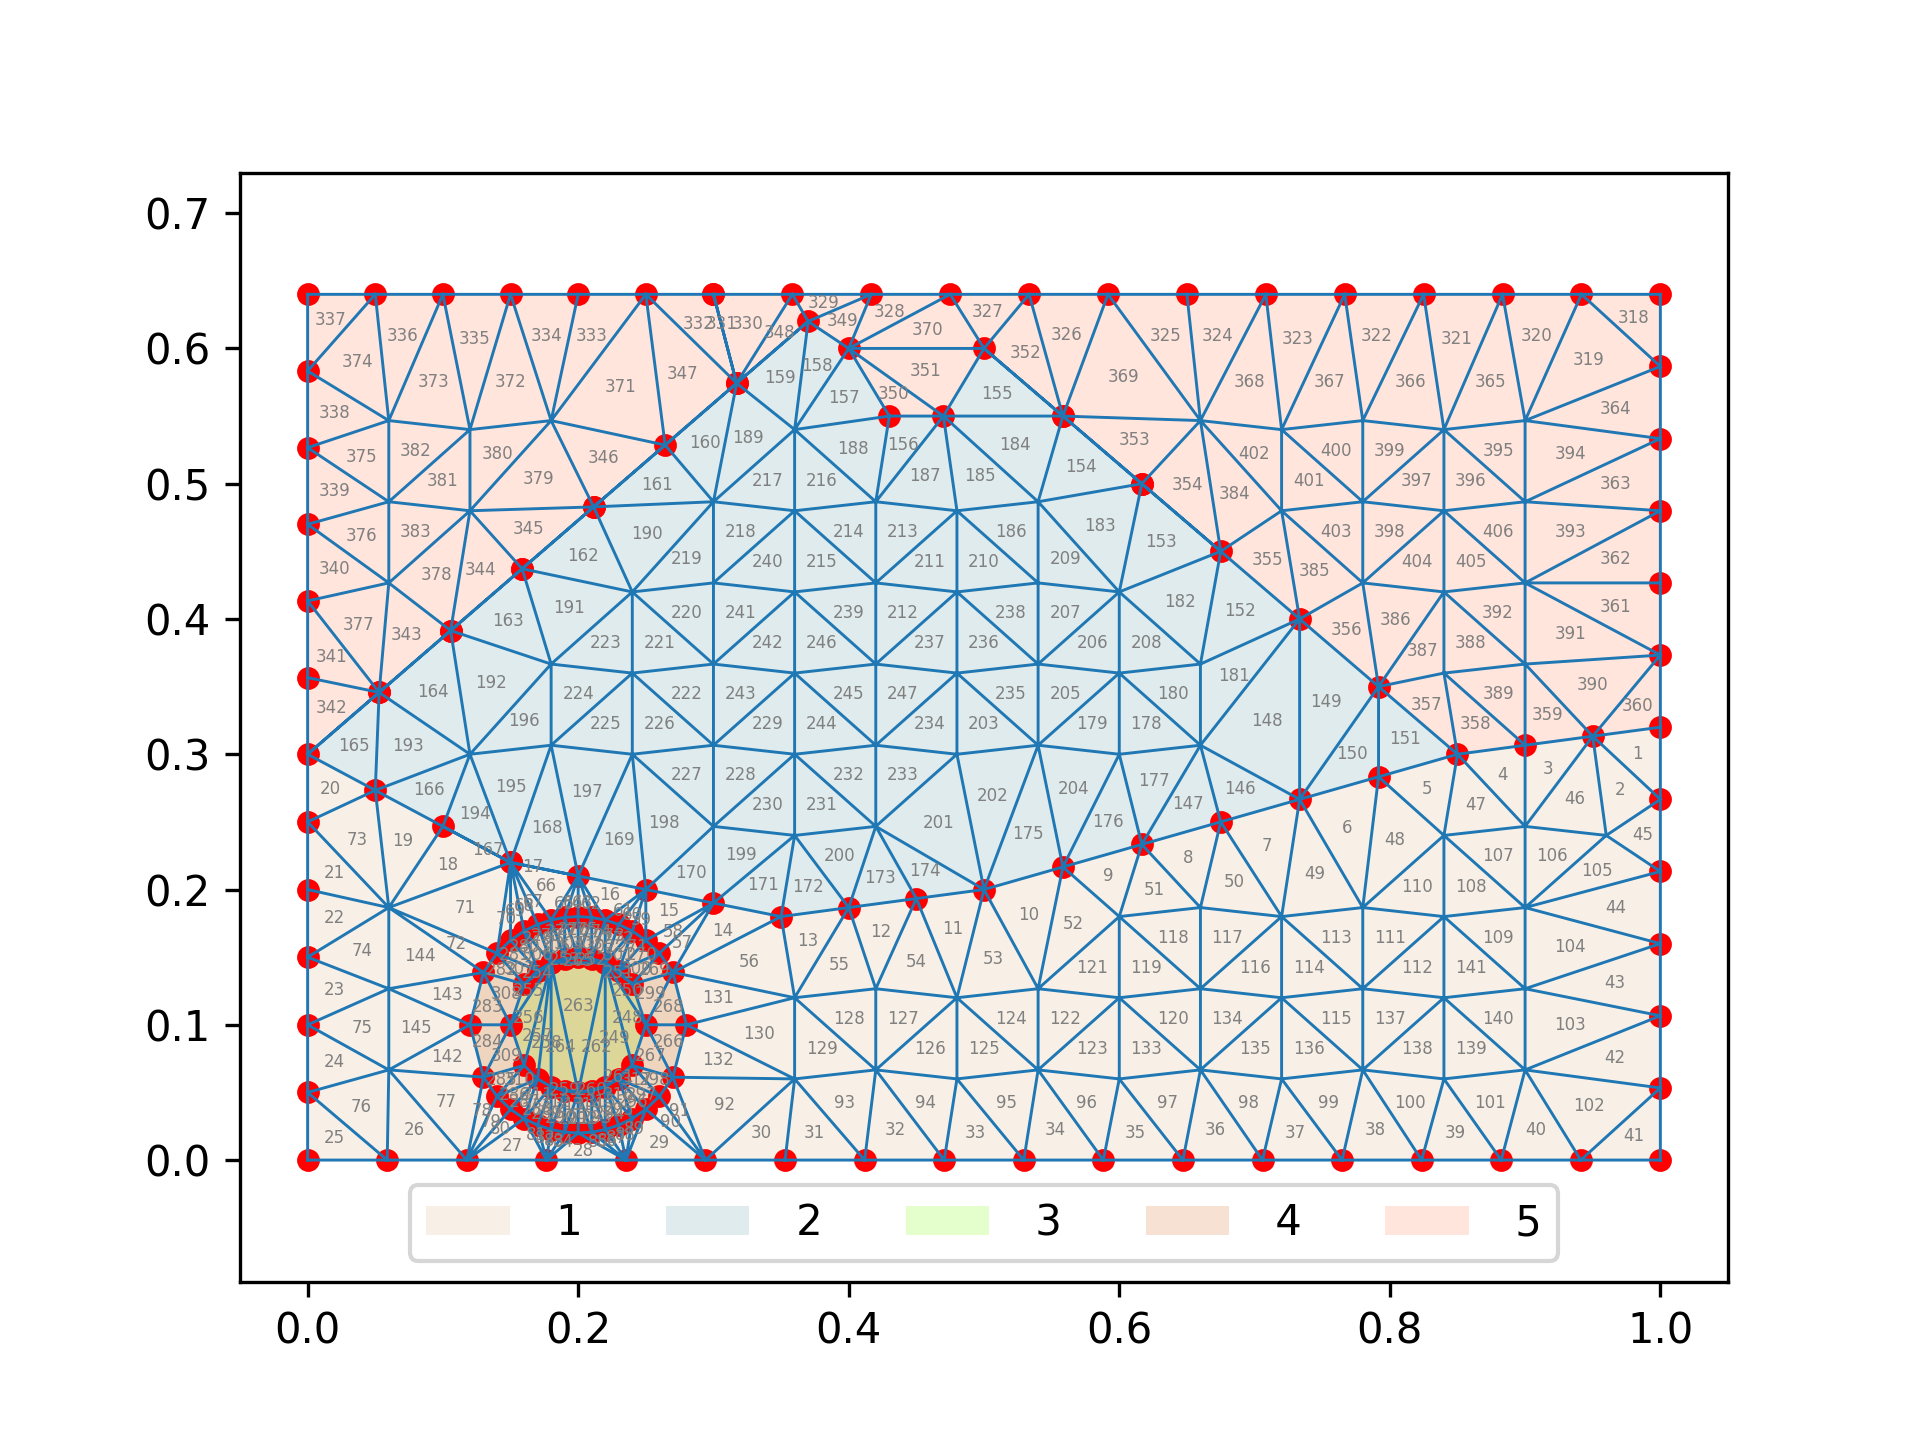
Very easy. The package has only one class CrossSection(), which is initiated with the input text file containing the coordinates for the polygons of the engineering geological cross-section. This class has only 5 'public' methods: .draw_blank(), .triangulate(), .save_triangles(), .draw_triangles(), .do_everything(), which (except for the last one) are expected to be called in this order (and never repeated for the same object). The .save_triangles() method saves triangles in a simplified text formats as well as attempts to do so in a STEP (ISO 10303-21) format. Although since I failed to find a single free working STEP analyzer, it is still a question whether the exported .step files actually comply with the stantard. Your comments on them are very welcome.
The illustration of how to use this package can be found in the attached file egcst_illustration.ipybn .
Briefly this can be expressed like this:
from egcst import CrossSection
cs = CrossSection(input_file_name="input.txt", min_step=1.0)
cs.do_everything()
1 maintainer

Metadata
1 maintainer
Release files for egcst 0.0.12
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| egcst-0.0.12.tar.gz | 5.8 kB | Without provenance | Details for egcst-0.0.12.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| egcst-0.0.12-py3-none-any.whl | Python 3 | none | any | Details for egcst-0.0.12-py3-none-any.whl |
Total release size: 11.7 kB
Release files / egcst-0.0.12.tar.gz
| Download URL | egcst-0.0.12.tar.gz |
|---|---|
| Size | 5.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5b05a1c24ee8cfe76be128d69d35a8623423eecbef3b8171daf5c9613dcdb80a
|
|
BLAKE2b-256 checksum How to use checksums |
b401210fe829d175862c40c1a625d672b92fcf1ac5bdf2e62920899b388958a5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.9.7
|
Release files / egcst-0.0.12-py3-none-any.whl
| Download URL | egcst-0.0.12-py3-none-any.whl |
|---|---|
| Size | 5.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
bf4ac18a48bc3de3cfebf2f36147cf7ffd892db7421a70ad5d32c9e622b4816b
|
|
BLAKE2b-256 checksum How to use checksums |
992edf00fb4466dd27ec689eeaefa77eb6056e4ef686128ef05994e21d14bb37
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.9.7
|
Security for egcst 0.0.12
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














