
icli - interactive command line interfaces
What is icli
icli is a Python library, built on top of argparse, which allows you to quickly build rich interactive command line interfaces with sections, command history, command batch processing, command repeating and interactive auto-complete.
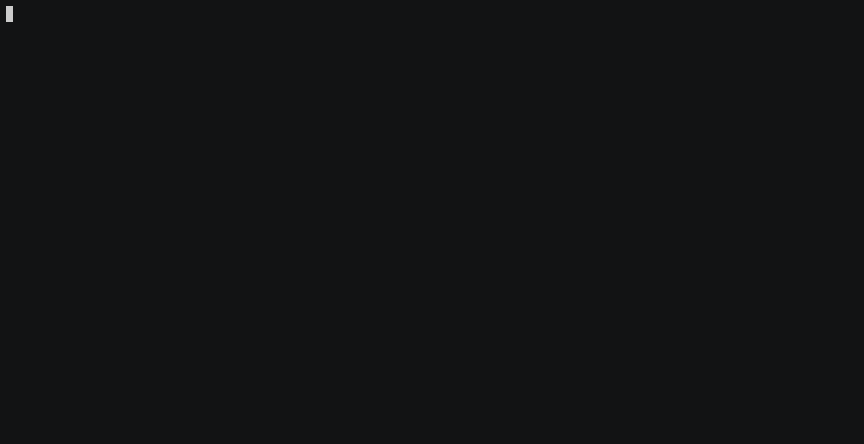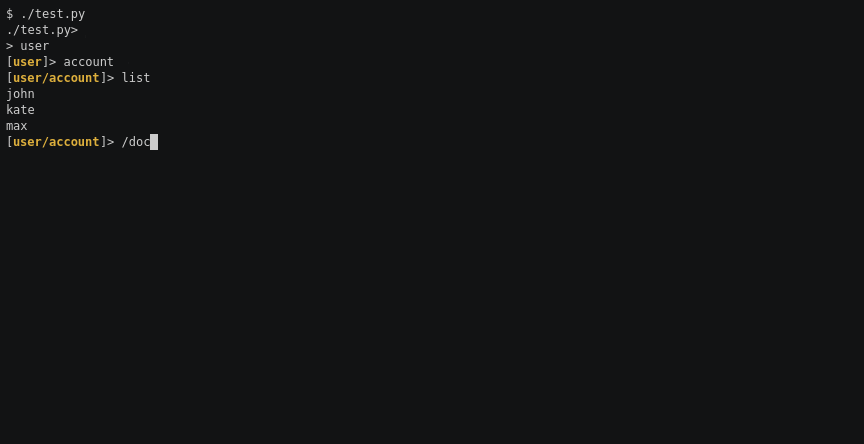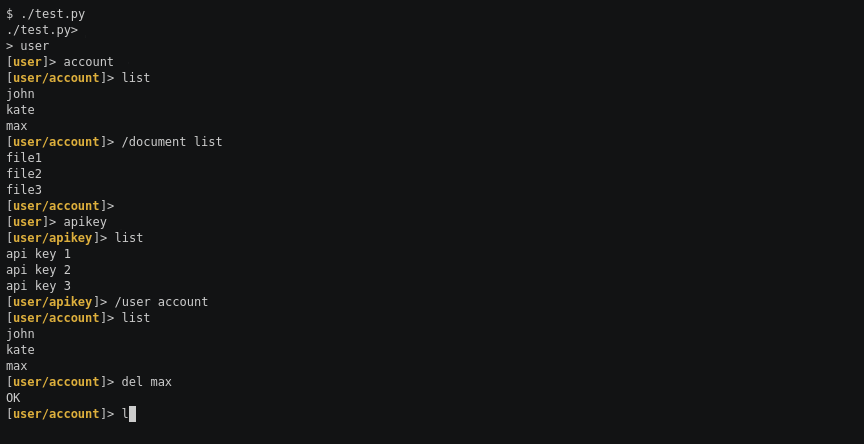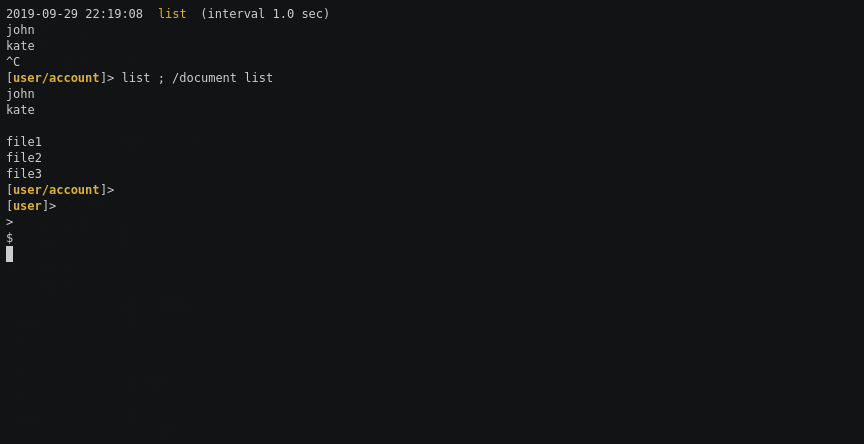
icli uses readline library for command inputs.
Features
-
Jump between command sections (use / for root section, .. or Ctrl-d to jump to upper section)
-
Send multiple commands, separated with ;
-
Repeat command execution, by adding |X to the end of input (X - delay in seconds between commands, use |cX to clear screen before next command execution)
-
Auto-completion (via argcomplete)
How to install
pip3 install icli
How to use
-
use icli.ArgumentParser just like argparse.ArgumentParser (create parsers, sub-parsers etc.)
-
create dispatcher method for commands. This method receives parsed arguments in **kwargs:
def dispatcher(**kwargs):
    # ....
- define CLI sections tree and start interactive mode:
import icli
ap = icli.ArgumentParser()

# ...

ap.sections = {'user': ['account', 'apikey'], 'document': []}
ap.run = dispatcher
ap.interactive()
Customizing
Override:
- get_interactive_prompt customize input prompt
- print_repeat_title customize title for repeating commands
- handle_interactive_exception handle exceptions, raised during interactive loop
Global commands
You may define global commands, which work in all sections, e.g. let's make w system command executed, when user type w:
def w(*args):
    # the method receives command name and optional command arguments in *args
    import os
    os.system('w')

ap.interactive_global_commands['w'] = w
Note: global commands are not auto-completed
History file
If history file is defined, input commands are loaded before interactive session is started and saved at the end.
ap.interactive_history_file = '~/.test-icli'
By default, last 100 commands are saved. To change this behavior, modify:
ap.interactive_history_length = 500
Combining shell and interactive CLI
Let's launch interactive mode when your program is started without arguments, otherwise process them:
import sys

# prog param sets program name in help to empty for interactive mode
ap = icli.ArgumentParser(prog='' if len(sys.argv) < 2 else None)

# ...

if len(sys.argv) > 1:
    ap.launch()
else:
    ap.interactive()
Batch processing
Your program may read commands from stdin or external file, then process them without user input
To do this, put commands to I/O steam and launch batch method:
import io

f = io.StringIO()
f.write('user account list ; user apikey list\ndocument list')
f.seek(0)
ap.batch(f)
or just launch batch method with a source stream:
with open('commands.list') as cf:
    ap.batch(cf)
1 maintainer

Metadata
1 maintainer
Release files for icli 0.0.10
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| icli-0.0.10.tar.gz | 5.3 kB | Without provenance | Details for icli-0.0.10.tar.gz |
Release files / icli-0.0.10.tar.gz
| Download URL | icli-0.0.10.tar.gz |
|---|---|
| Size | 5.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
910681cd23a1e5284220eadcc4d2b1cc35d8d57dff577d435cbca324606922bb
|
|
BLAKE2b-256 checksum How to use checksums |
71856aa881360781eae4599d53ddbf15500fe4bff99108c1baa232e41c3cd084
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.21.0 setuptools/45.2.0 requests-toolbelt/0.9.1 tqdm/4.45.0 CPython/3.8.5
|
Security for icli 0.0.10
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














