
6 files were added to this release more than 14 days after its initial publication. Inspect the release files before installing.
Learning Robot Trajectories subject to Kinematic Joint Constraints


This python package enables learning of robot trajectories without exceeding limits on the position, velocity, acceleration and jerk of each robot joint.
Movements are generated by mapping the predictions of a neural network to safely executable joint accelerations. The time between network predictions must be constant, but can be chosen arbitrarily.
Our method ensures that the kinematic constraints are never in conflict, which means that there is at least one safely executable joint acceleration at any time.
This package provides the code to compute the range of safely executable joint accelerations.
Installation
The package can be installed by running
pip install klimits
Trajectory generation 
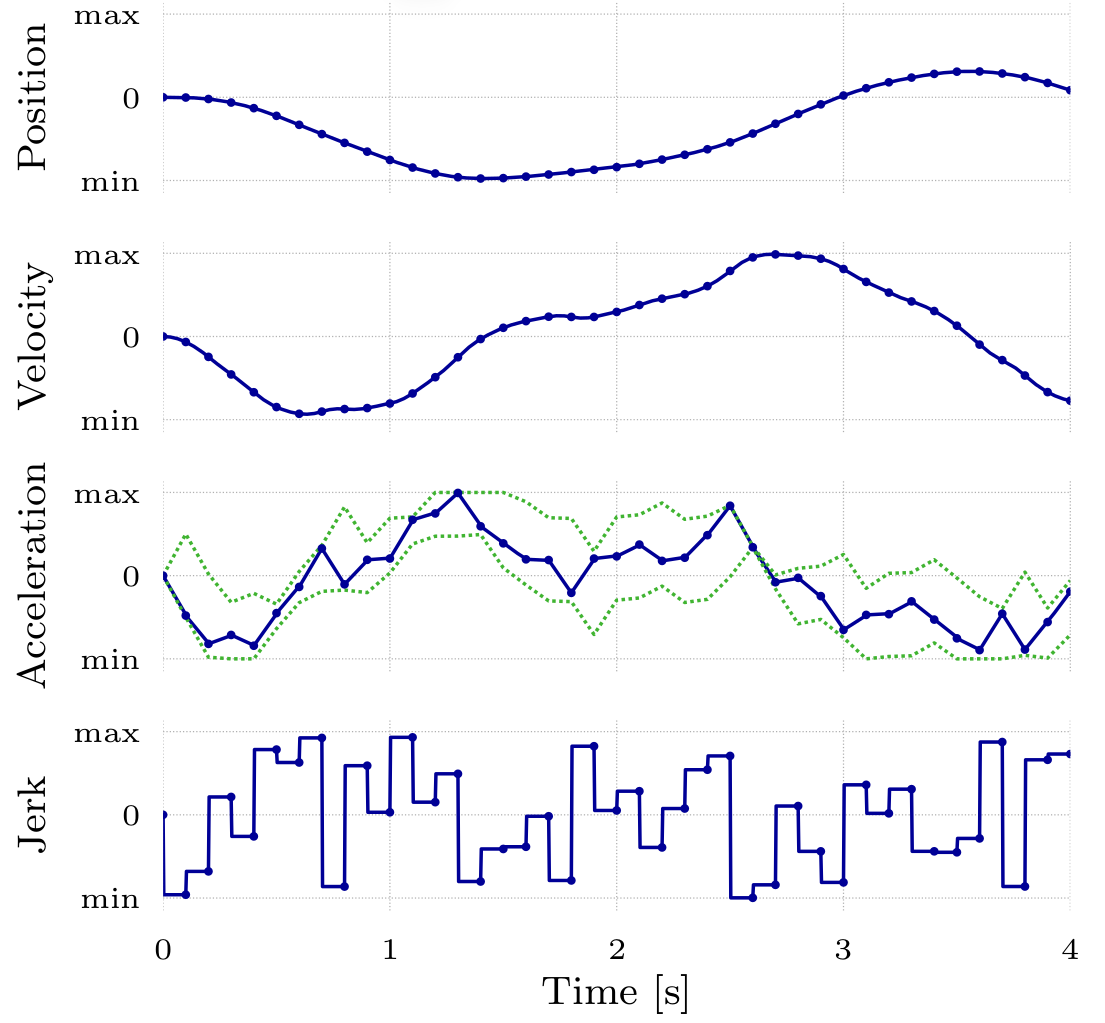
To generate a random trajectory with limited jerk, acceleration, velocity and position run
python -m klimits.test_trajectory_generation
Several parameters can be adjusted to modify the generated trajectory. E.g:
python -m klimits.test_trajectory_generation --time_step=0.1 --pos_limits='[[-2.96705972839, 2.96705972839], [-2.09439510239, 2.09439510239]]' --vel_limits='[[-1.71042266695, 1.71042266695], [-1.71042266695, 1.71042266695]]' --acc_limits='[[-15, 15], [-7.5, 7.5]]' --plot_joint='[1, 0]' --pos_limit_factor=0.9 --vel_limit_factor=0.8 --acc_limit_factor=0.7 --jerk_limit_factor=0.6 --trajectory_duration=20 --plot_safe_acc_limits
Run
python -m klimits.test_trajectory_generation --help
for further details on the optional arguments.
Further reading
A preprint of the corresponding ICRA 2021 publication is available at arXiv.org.
Further information on the implementation can be found here.
This library is used by safeMotions to learn collision-free reaching tasks via reinforcement learning.
Video
Disclaimer
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
1 maintainer

Metadata
1 maintainer
Release files for klimits 1.1.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Files added late
6 files were uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release files before installing.
Built distributions (wheels)
Total release size: 45.6 MB
Release files / klimits-1.1.3-cp313-cp313-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp313-cp313-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.13 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
810dc01bc8af96317696161b7289e26f6a5c7029b0fa81aba63ec1cc91537346
|
|
BLAKE2b-256 checksum How to use checksums |
23e169e375605ca02424d4923ea879386e0fff40f224e79b431a69d8bccae9dd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp313-cp313-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp313-cp313-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.13 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
ac09421fb98bbba65c0e796dcb012c2cca905c8199bf146979995bc6260a1203
|
|
BLAKE2b-256 checksum How to use checksums |
0104545866d4b174cce86c9a6c1b3b601583e6a548b4b19e09e832cd70dd11e6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | klimits-1.1.3-cp313-cp313-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
4bb1f9b28ae477257d9491aa45cefb0ef218832639947a454d7c1363f30bd3d1
|
|
BLAKE2b-256 checksum How to use checksums |
b038023ee84eb75df0ed1f03a7a3d042ba9f53a01601cca3882a7c9e22fe3317
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp313-cp313-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | klimits-1.1.3-cp313-cp313-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.13 Linux glibc 2.17+ x86-32 |
|
SHA-256 checksum How to use checksums |
7ad3efc591bc538309e06f3c1de0964f46b1e17d18014fe4204e7a01bb1e625a
|
|
BLAKE2b-256 checksum How to use checksums |
a43a6c03dad2c183369fd2ed489546b2ce79d467f6713ab056fdad9029624bba
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp312-cp312-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp312-cp312-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.12 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
d960e743cfa9410a54f75fcd85dafbabd292b3add397b9fcdb6b9e4f4cdb9114
|
|
BLAKE2b-256 checksum How to use checksums |
11b4e2bfd78a15e13fb46656d4ab432ba9f1faf1cd410ecc81dc5a3d323f3385
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp312-cp312-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp312-cp312-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.12 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
171dd1b4a0d5fafc8692beff52accf2dd79316719bc697449658b4fa71b8e6b2
|
|
BLAKE2b-256 checksum How to use checksums |
61411bdb030b899ea40b51f3e565f1839897a1f58beeb8c9fb017312c0112348
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | klimits-1.1.3-cp312-cp312-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
b776a9cc671775cb636be1304f40e443de13e2d47793e534587ba3446344111d
|
|
BLAKE2b-256 checksum How to use checksums |
dbe0cedb8322a4689e9d282cc05210bac4de02fd209d295e62822f4e77aa5acd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp312-cp312-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | klimits-1.1.3-cp312-cp312-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-32 |
|
SHA-256 checksum How to use checksums |
65145695d825e7130769558e6c346763c2d80ed59aa74d10d270cb5be6ddf485
|
|
BLAKE2b-256 checksum How to use checksums |
db22f3b2a9b8f44b37a35cbee698be5fd869c71700c5000777fdbf1ef2d31145
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp311-cp311-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp311-cp311-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
73e1a09ecb5da973f1dabd54c48ad586a0898f89e82931420bdb226675cac848
|
|
BLAKE2b-256 checksum How to use checksums |
fc53e248c0e44e9751d619642079fc91303a5901f91bb80361a66ce9df8af069
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp311-cp311-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp311-cp311-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
2fa6db1539ce65cb086f17bac130c3301bf2f491e3173c5afbc6686c081faea8
|
|
BLAKE2b-256 checksum How to use checksums |
a8860d06d169fe96cd9cb9d8d194bc267889b231cc3eb36b03ec76d73f4767aa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | klimits-1.1.3-cp311-cp311-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
8cf2f8ee6ce7cbc48c10c580de8e33e44301b0d8a7121df053634ad466d868fb
|
|
BLAKE2b-256 checksum How to use checksums |
0684c23e9e25c77a57ff0a51f56de310f82df1f548cc2f40b5206ad1253c78db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp311-cp311-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | klimits-1.1.3-cp311-cp311-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-32 |
|
SHA-256 checksum How to use checksums |
708c1ff3bda71cbe7c083971bb0b2c250abac1ba36e87f4dd05cb877b8da7e11
|
|
BLAKE2b-256 checksum How to use checksums |
e47fe1c0bab433b9a0cd6f28059597716201cf64de683cf68f0ec198c3c6af84
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp310-cp310-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp310-cp310-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
6eb2aadc949b445da2e28f12fae65961024741c8931a6044eb0d94634a041178
|
|
BLAKE2b-256 checksum How to use checksums |
3e0aad5241adc93cb827f3603a1b90592047f26f487b7cd6f131b1e1659dc34a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp310-cp310-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp310-cp310-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.10 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
8fb49e77e276a039302f2eeb07c21c115a54d45870bf040e17e06953309ae52d
|
|
BLAKE2b-256 checksum How to use checksums |
b03453a56e467f70e3ab5d146bb434575a2b9e7faaac720f235d5736b113647a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | klimits-1.1.3-cp310-cp310-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
e184d7b7e025a1cf27aa97a6f74652da9efcbf046866b1250b88c3898046e41e
|
|
BLAKE2b-256 checksum How to use checksums |
b159200bf4c674e6bb2bd09d9ae5db1bde97236368c1012c26ed9df8d9f9a9fb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp310-cp310-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | klimits-1.1.3-cp310-cp310-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.10 Linux glibc 2.17+ x86-32 |
|
SHA-256 checksum How to use checksums |
5f34bf51babe841fe1a756db676cd980bcb14f465b7c66bc3590f5ae001e2de6
|
|
BLAKE2b-256 checksum How to use checksums |
a23c1c140a89969962ff6cbb11843947b24e75a7bc5e9ef4e0e9495fe331d646
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp39-cp39-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp39-cp39-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.9 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
3d71cbcc14dd8dffa7a274024c5a9470ebe793f9297502829dc44d26a2070568
|
|
BLAKE2b-256 checksum How to use checksums |
0c2d2ce9ccfd71178d102da6b842f05d771eda51abfa91d0ac63fae99f6a32c1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp39-cp39-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp39-cp39-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.9 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
2086efb9f401382ca23b6afd913af0b219a9ff5295cb0934e21fe2937e70591c
|
|
BLAKE2b-256 checksum How to use checksums |
9b7e43827b26a18618cf7fc1b831dbaf09b93f9a2419b89b61f80b6fdb9d50e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp39-cp39-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | klimits-1.1.3-cp39-cp39-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ x86-64 |
|
SHA-256 checksum How to use checksums |
49fab8bf9f2551b35a10c0d06f8918e7adcdae02a94810d717013e38abda648d
|
|
BLAKE2b-256 checksum How to use checksums |
6b34fcf339a3e3fdd8d3e83ae41511e4380afeef6489ed14c6e8f982f595e9f9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp39-cp39-manylinux_2_17_i686.manylinux2014_i686.whl
| Download URL | klimits-1.1.3-cp39-cp39-manylinux_2_17_i686.manylinux2014_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.9 Linux glibc 2.17+ x86-32 |
|
SHA-256 checksum How to use checksums |
c13c070c6daa41d95b404449432b61061381fa0afc2a4dcfe9233974bfb1bff9
|
|
BLAKE2b-256 checksum How to use checksums |
c1bf46334c5fafdf1ff9ec8f9ea0bc9df2756b26b0ae9183ab765388503eda78
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp38-cp38-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp38-cp38-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.6 MB |
| Tags | CPython 3.8 Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
a2f302bf048b5e641c9a0d55134ae4e44fd4ab85df1acc535f0cce6365001ac0
|
|
BLAKE2b-256 checksum How to use checksums |
697eccdbcfbce6ce61148ee3e86907a8d47206a26583b91e8dbc472d32821d02
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp38-cp38-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp38-cp38-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.5 MB |
| Tags | CPython 3.8 Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
d695520726243e8098ffeed3dc7ecaedbd49c08c8dd436033ef4baeceaa0b466
|
|
BLAKE2b-256 checksum How to use checksums |
2f976b4ae94c543a7f1384573df495a815c51f4adc27adcbf3776d1303e2493a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp38-cp38-manylinux2010_x86_64.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp38-cp38-manylinux2010_x86_64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.8 Linux glibc 2.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
0c6abd828fc7e4db2305e933e786b9af58ecc8069828c1028895913c2e7b0125
|
|
BLAKE2b-256 checksum How to use checksums |
b55551b484da9826eb646be0921325684f855ae98b27be3c65fcd39c9380e3c8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency logRelease files / klimits-1.1.3-cp38-cp38-manylinux2010_i686.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp38-cp38-manylinux2010_i686.whl |
|---|---|
| Size | 1.2 MB |
| Tags | CPython 3.8 Linux glibc 2.12+ x86-32 |
|
SHA-256 checksum How to use checksums |
4d3080e8b3e8750d001715ece04bbb95d6b3a14359c213326c05319e4239c017
|
|
BLAKE2b-256 checksum How to use checksums |
9febe1562ab4d3d8804604bd2daa3d3c69105bee88cd7e7ce31242d2057de388
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency logRelease files / klimits-1.1.3-cp37-cp37m-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp37-cp37m-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.7 CPython 3.7 pymalloc Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
4f3e64bf8e3c2bcd37eb7279e10dc2b61e23e62526f051131cafb596715f911a
|
|
BLAKE2b-256 checksum How to use checksums |
c70ed29fe6f6b00468a14196f1aa362a7f9a0e37017d05c3d4cc16e6158961f1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp37-cp37m-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp37-cp37m-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.7 CPython 3.7 pymalloc Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
bb61fa8e5e1031d0664961a8b34473d2997988b3d29586aa12b2f0f5678b54b5
|
|
BLAKE2b-256 checksum How to use checksums |
9d30d0b75f746edcbed54c82ac4644067d056bc6ec9975dc68f55e57809975f1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp37-cp37m-manylinux2010_x86_64.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp37-cp37m-manylinux2010_x86_64.whl |
|---|---|
| Size | 1.2 MB |
| Tags | CPython 3.7 CPython 3.7 pymalloc Linux glibc 2.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
26526eca62c281f698ff69e5b80e284b105e737c5c21b0dba60cd84d0cd1c686
|
|
BLAKE2b-256 checksum How to use checksums |
396fa3ebef6db65a694c64d8a33ca02ab3a2e7b1c931285e03ed777652213482
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency logRelease files / klimits-1.1.3-cp37-cp37m-manylinux2010_i686.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp37-cp37m-manylinux2010_i686.whl |
|---|---|
| Size | 1.1 MB |
| Tags | CPython 3.7 CPython 3.7 pymalloc Linux glibc 2.12+ x86-32 |
|
SHA-256 checksum How to use checksums |
32ec777f09bc31083cb68e95fcc78f8100f91323d02c6544e844ccb0c54af1d9
|
|
BLAKE2b-256 checksum How to use checksums |
c370846f3e561aede38bd34f30d14635026dfc806d011e3c6e294ef5396e49e3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency logRelease files / klimits-1.1.3-cp36-cp36m-musllinux_1_2_x86_64.whl
| Download URL | klimits-1.1.3-cp36-cp36m-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.6 CPython 3.6 pymalloc Linux musl 1.2+ x86-64 |
|
SHA-256 checksum How to use checksums |
ff2cbc820a66162b6f5d7bf3097dc525bacb6b17c1a713bc3d7a8e699860ffbb
|
|
BLAKE2b-256 checksum How to use checksums |
df8d4500d0679ec906302dd64765f8ad72da8ad763d795d462b2abc57eda4460
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp36-cp36m-musllinux_1_2_i686.whl
| Download URL | klimits-1.1.3-cp36-cp36m-musllinux_1_2_i686.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.6 CPython 3.6 pymalloc Linux musl 1.2+ x86-32 |
|
SHA-256 checksum How to use checksums |
c67747b5485ed7a5c3ef25560a9b1490665cfd3d58454737a7822f6d27bc6149
|
|
BLAKE2b-256 checksum How to use checksums |
fe22e92fed41ef523570f2cea52678d872006e215e2fa5eec36074da755b97ff
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.0.1 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 10, 2025.
Transparency logRelease files / klimits-1.1.3-cp36-cp36m-manylinux2010_x86_64.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp36-cp36m-manylinux2010_x86_64.whl |
|---|---|
| Size | 1.2 MB |
| Tags | CPython 3.6 CPython 3.6 pymalloc Linux glibc 2.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
fb8e0033b24f3f2433046ea874bb36971de65c4d539617cb83dbaa9508496b05
|
|
BLAKE2b-256 checksum How to use checksums |
ee9ad9e689df8014829ebe70c12fd75dadcfe42a6fdf45c3f484398776433181
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency logRelease files / klimits-1.1.3-cp36-cp36m-manylinux2010_i686.whl
File added late
This file was uploaded more than 14 days after the first file in this release.
While project maintainers occasionally add legitimate files to an existing release, late additions can also indicate a security compromise.
We recommend inspecting the release file before installing.
| Download URL | klimits-1.1.3-cp36-cp36m-manylinux2010_i686.whl |
|---|---|
| Size | 1.1 MB |
| Tags | CPython 3.6 CPython 3.6 pymalloc Linux glibc 2.12+ x86-32 |
|
SHA-256 checksum How to use checksums |
b5b6face9f92c0c8a793e41cf205bd7bbfd0775d9bb93210aa8a651b932560a7
|
|
BLAKE2b-256 checksum How to use checksums |
a3748173be6c2df6189e6b64d4034b08eaef63e73476fc5d680e852aa87639f5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 8, 2025.
Transparency log













