
Autogenerated Table of Contents for Github Markdown or Bear Notes
Generated by the script ;)
Table of Contents
Overview
I love using Bear Notes for note taking of all sorts. Recently, Bear released a feature that allowed headers to be linked with x-callback-urls. And thus, I created a script to autogenerate a Table of Contents for your notes based on the headers.
Installation
NOTE: This program is only compatible with Python 3.x
PyPi (Preferred)
$ pip3 install markdown-toc --upgrade
Manually
$ git clone https://github.com/alexander-lee/markdown-github-bear-toc.git

$ cd markdown-github-bear-toc
$ python3 setup.py install
Usage
Flags
-hor--header-priorityis the Limiting Header Priority/Strength (whether you limit your Table of Contents to h3s or h4s)-tor--typeis the type of anchor you want to use (Github or Bear x-callback-url)--no-writeis a flag on whether you want to disable the feature that automatically injects the ToC into your Markdown file or Bear Note-tocor--table-of-contents-styleis the Markdown style for your Table of Contents header
With Bear
- Add a Table of Contents to a Bear Note with the title "Bear Note Title"
$ markdown-toc -h <default: 3> -t bear [--no-write] "Bear Note Title"
- Add a Table of Contents to a Bear Note with the UUID
20703126-FA33-400A-B98E-F55F57E3EF48-47683-000143B2335758CA
$ markdown-toc -h <default: 3> -t bear [--no-write] "20703126-FA33-400A-B98E-F55F57E3EF48-47683-000143B2335758CA"
- Add a Table of Contents to two Bear Notes with titles "Bear Note Title 1" and "Bear Note Title 2"
$ markdown-toc -h <default: 3> -t bear [--no-write] "Bear Note Title 1" "Bear Note Title 2"
- Add a Table of Contents to all Bear Notes that contain the tag
#bearOR tag#beet
$ markdown-toc -h <default: 3> -t bear [--no-write] "#bear" "#beet"
- This allows you to take input a list of Bear Note titles, tags, or UUIDs and will inject the ToC into your note whether or not you submit the
--no-writeflag. - If you have
#tagsat the top of your note (cause I use them to categorize my notes), it will inject the ToC right after any tags.
| Original Note | Note with ToC |
|---|---|
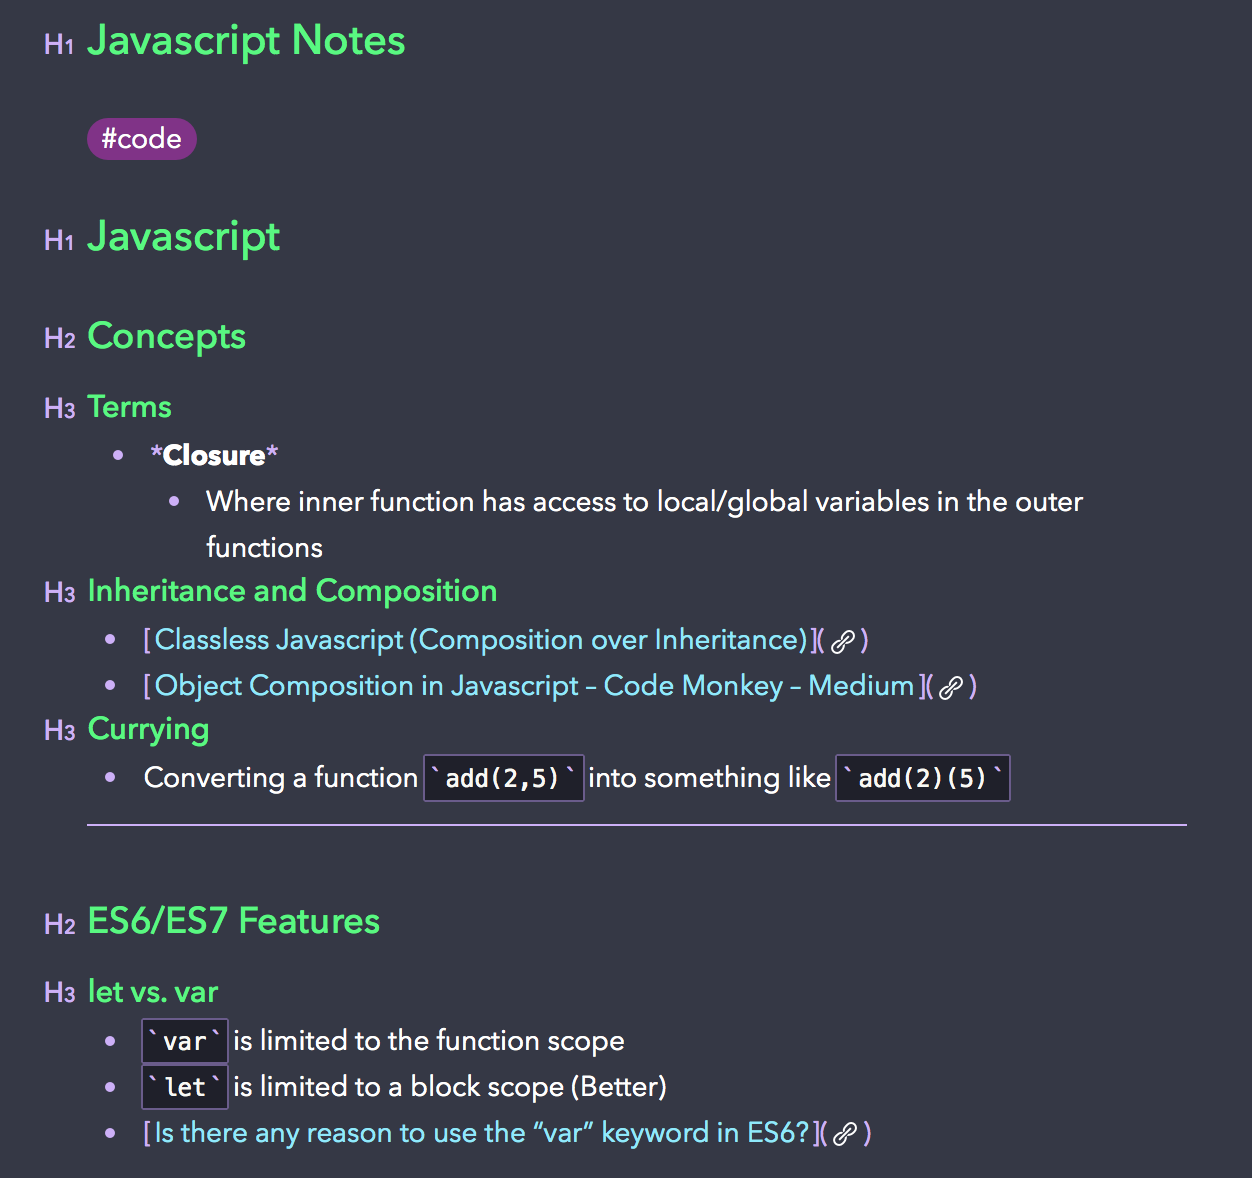 |
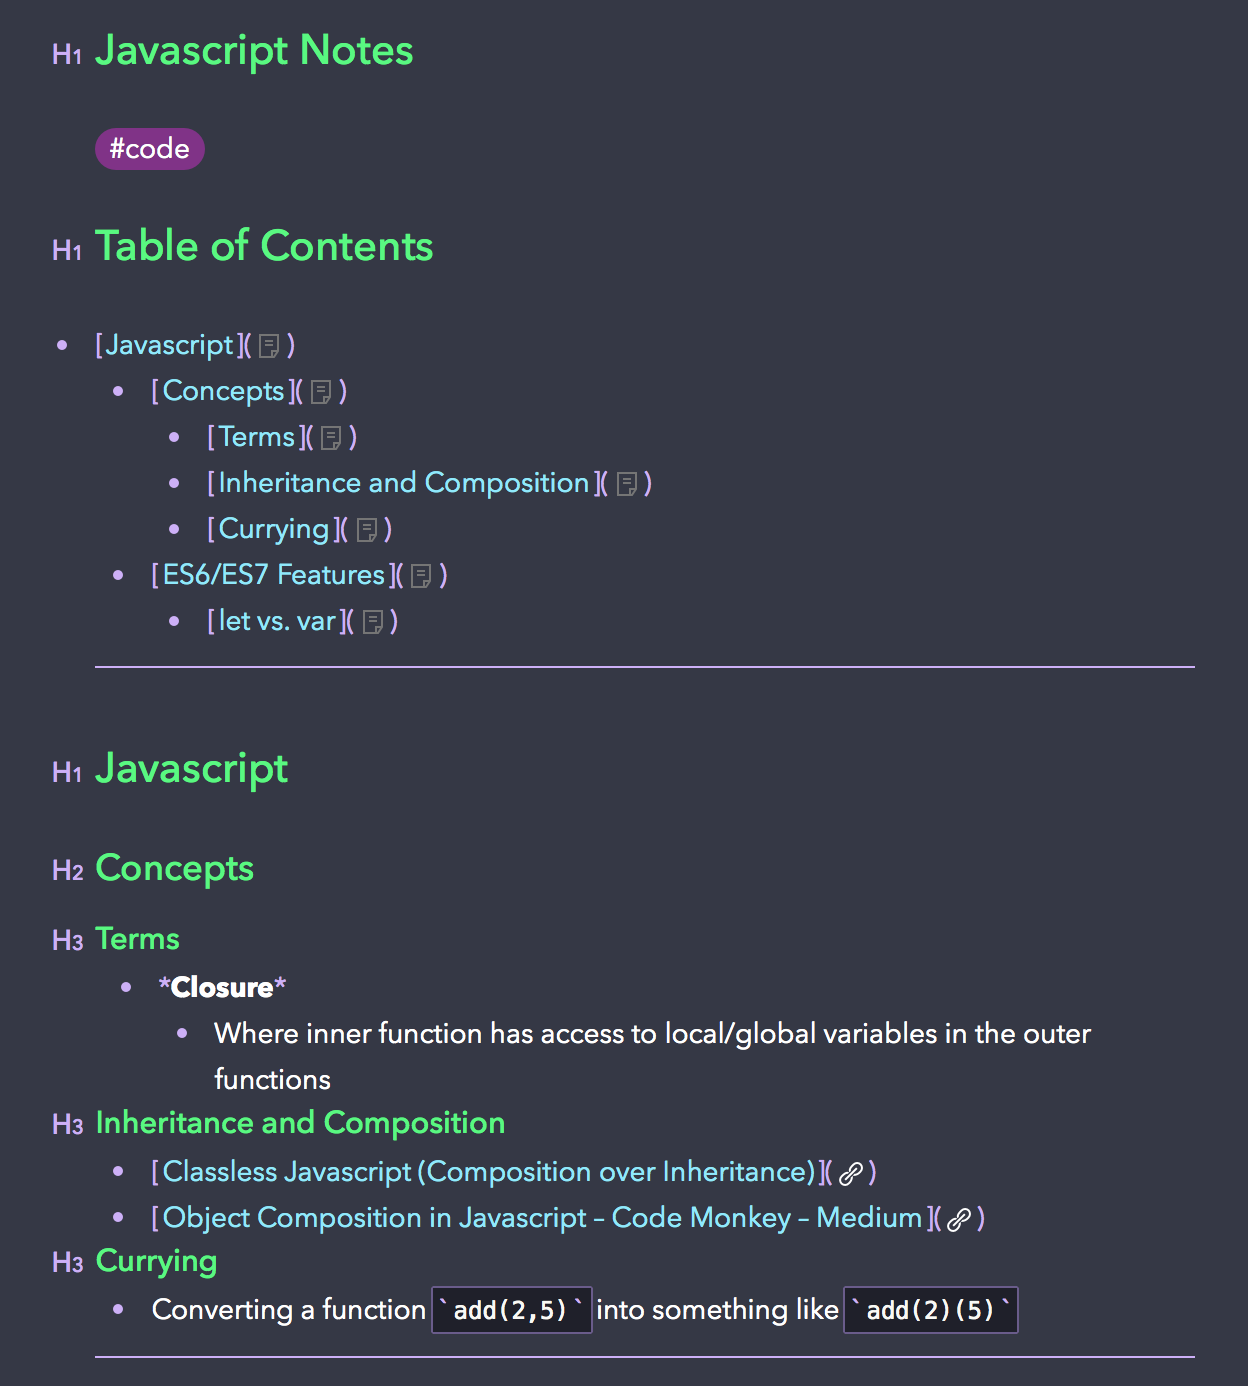 |
With Markdown Files
- Add of a Table of Contents to README.md (Using Github Anchors)
$ markdown-toc -h <default: 3> -t github [--no-write] README.md
- Add of a Table of Contents to README.md and Folder/README2.md (Using Github Anchors)
$ markdown-toc -h <default: 3> -t github [--no-write] README.md Folder/README2.md
1 maintainer

Metadata
1 maintainer
Release files for markdown-toc 1.2.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| markdown-toc-1.2.6.tar.gz | 6.7 kB | Without provenance | Details for markdown-toc-1.2.6.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| markdown_toc-1.2.6-py3-none-any.whl | Python 3 | none | any | Details for markdown_toc-1.2.6-py3-none-any.whl |
Total release size: 14.8 kB
Release files / markdown-toc-1.2.6.tar.gz
| Download URL | markdown-toc-1.2.6.tar.gz |
|---|---|
| Size | 6.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8e89536688000c05b329df220e8036211c572af376cc83cee8763335711c19bd
|
|
BLAKE2b-256 checksum How to use checksums |
222ea41b4efe2ffab22e7f1aeba325fb843117dce9386530ba7efa89c5c14b96
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.12.1 pkginfo/1.4.2 requests/2.20.1 setuptools/40.6.2 requests-toolbelt/0.8.0 tqdm/4.28.1 CPython/3.6.5
|
Release files / markdown_toc-1.2.6-py3-none-any.whl
| Download URL | markdown_toc-1.2.6-py3-none-any.whl |
|---|---|
| Size | 8.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
63706ab4ccde4c82840f79197cefbcf47dc2a25582cf86187a83a9206cb38345
|
|
BLAKE2b-256 checksum How to use checksums |
869ba2ef42a5a1bcba508afec04da982839681ee62fa9dded969692f3cbb7ae7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.12.1 pkginfo/1.4.2 requests/2.20.1 setuptools/40.6.2 requests-toolbelt/0.8.0 tqdm/4.28.1 CPython/3.6.5
|
Security for markdown-toc 1.2.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














