
mkdocs-safe-text-plugin

Plugin for safe text editing with MKDocs.
Table of Contents
How does this plugin work?
Markdown is a very flexible format, and raw HTML is allowed. But it is unnecessary in multiple-person text editing.
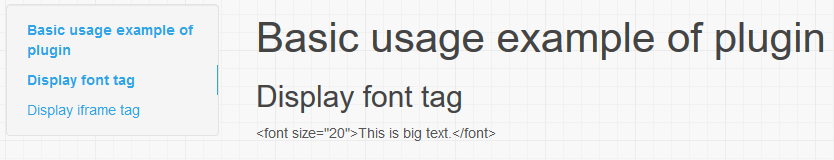
When raw HTML like <font> tag is used in MKDocs, it is rendered as it is.
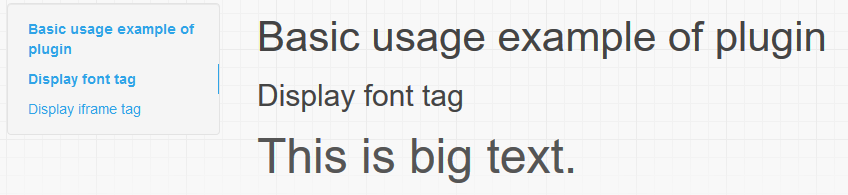
If you use this plug-in with MKDocs, tags that are not allowed in the allowlist are escaped.
Installation
Install it via PyPI using pip command.
$ pip install mkdocs-safe-text-plugin
And add it to your mkdocs.yml file.
plugins:
  - mkdocs_safe_text
An example of use can be checked by example/basic-usage.
Plugin configuration
This plugin works with the HTML tag element for Markdown defined by bleach-allowlist enabled. This implementation approach is recommended in the Python-Markdown release notes.
And user can change this setting.
plugins:
  - mkdocs_safe_text:
      append_allowed_tags:
        - tag1
        - tag2
      remove_allowed_tags:
        - tag3
        - tag4
      allowed_attrs:
        tag5:
          - attribute1
          - attribute2
An example of use can be checked by example/customization-usage.
License
CHANGELOG
1.6.1
- Use SPDX short identifier style for license text
1.6.0
- Clarified support for Python 3.12
- Dropped support Python 3.7 and Python 3.8
- Migration pyproject.toml about this package
1.5.1
- Clarified support for Python 3.11(fix metadata)
1.5.0
- Clarified support for Python 3.11
1.4.0
- Clarified support for Python 3.10
- Dropped support Python 3.6
1.3.1
- Requires
bleach-allowlistversion 1.0.3 or higher
1.3.0
- Migrate using Python package from
bleach-whitelisttobleach-allowlist - Clarified support for Python 3.9
- Dropped support Python 3.5
1.2.0
- Clarified support for Python 3.8
- Dropped support Python 2.7
1.1.2
- Dropped support Python 3.4
1.1.1
- Fix to work even after MKDocs 1.0
- Dropped support Python 3.3
1.1.0
- Embed distribution license in source code
- Remove dependency on 'pytest-pythonpath'
1.0.0
- First stable release version
- Support Python 3.3 or later
0.5.0
- Support reST format in PyPI Web UI
- Add dependency on pypandoc
0.4.0
- Update status to Beta version
- Add documentation about this plugin
- Add a Makefile for tidy tasks
0.3.0
- Update status to Alpha version
0.2.0
- Implement plugin configuration
- Add class files to
mkdocssafetext - Add unittest files to
tests
- Add class files to
0.1.0
- First planning version
- Make temporary directory structure
- Add requirement specifiers
1 maintainer

Metadata
1 maintainer
Release files for mkdocs-safe-text-plugin 1.6.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| mkdocs_safe_text_plugin-1.6.1.tar.gz | 6.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| mkdocs_safe_text_plugin-1.6.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 14.2 kB
Release files / mkdocs_safe_text_plugin-1.6.1.tar.gz
| Download URL | mkdocs_safe_text_plugin-1.6.1.tar.gz |
|---|---|
| Size | 6.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
664be5a6dd17582f5b0c45f2f8f66735e64151a360ea65066cdb3bfe2bc1202a
|
|
BLAKE2b-256 checksum How to use checksums |
92694e7028a62a869635c0cc341771546153f2a79e9b3352352e687d409773b5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.1.1 CPython/3.11.0
|
Release files / mkdocs_safe_text_plugin-1.6.1-py3-none-any.whl
| Download URL | mkdocs_safe_text_plugin-1.6.1-py3-none-any.whl |
|---|---|
| Size | 7.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ac3bbd4ca7db38fbbec224f90e92bce7189977268cca0ee9e09340f7e7af0f9a
|
|
BLAKE2b-256 checksum How to use checksums |
7669e83dde27b75820442f0ac59c777cf051e33a7245b46b6a61aa9dd1c27ee0
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.1.1 CPython/3.11.0
|
Security for mkdocs-safe-text-plugin 1.6.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














