
WARNING: THIS IS ALPHA STAGE QUALITY AND WILL MOST CERTAINLY DELETE YOUR APACHE CONFIGURATION- It doesn’t, but: no warranty and such. - Also, hasn’t many features yet.
modseccfg
Simple GUI editor for SecRuleRemoveById settings
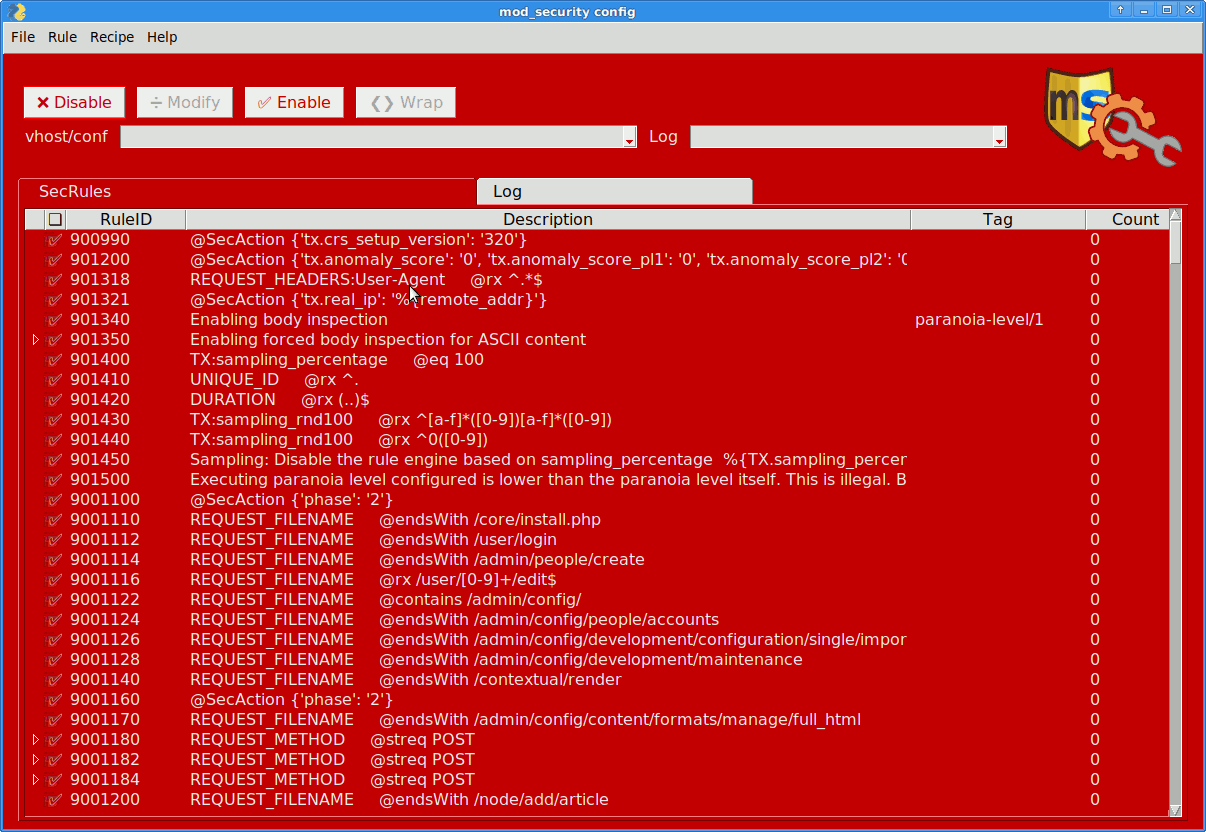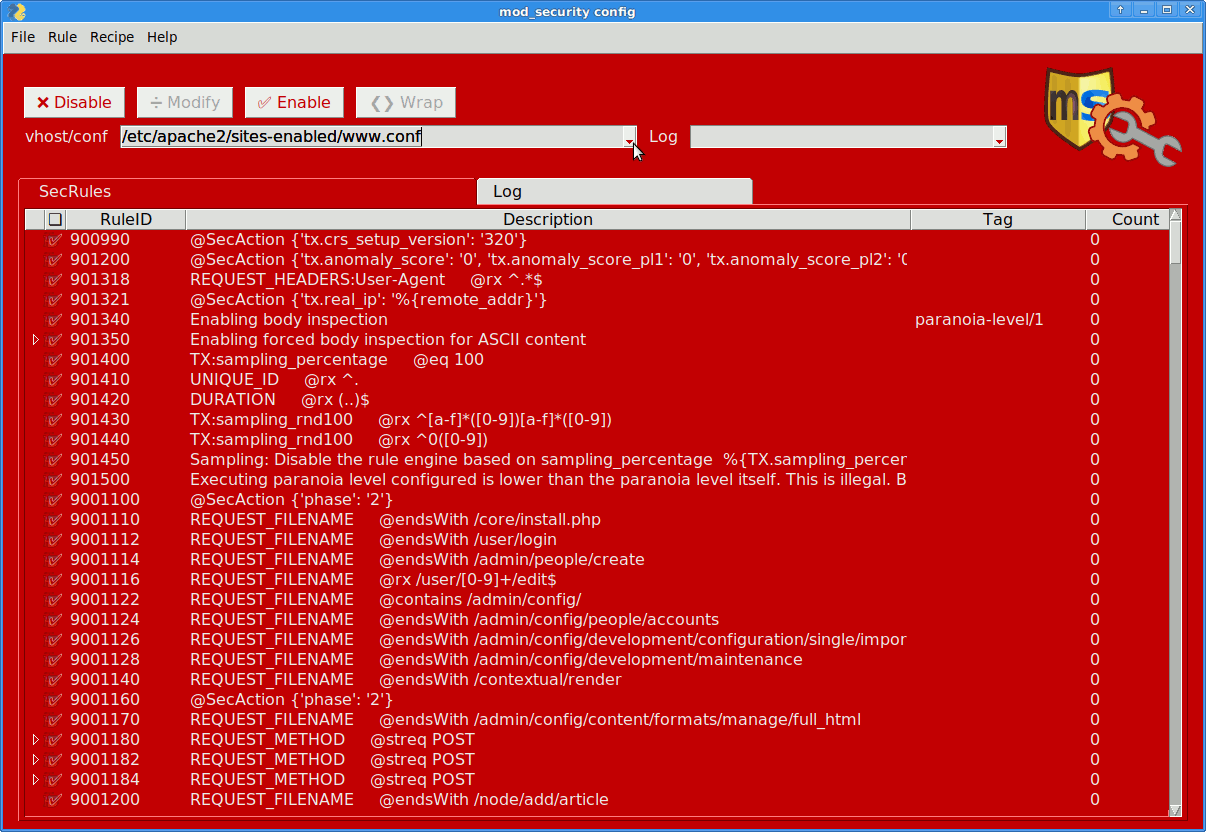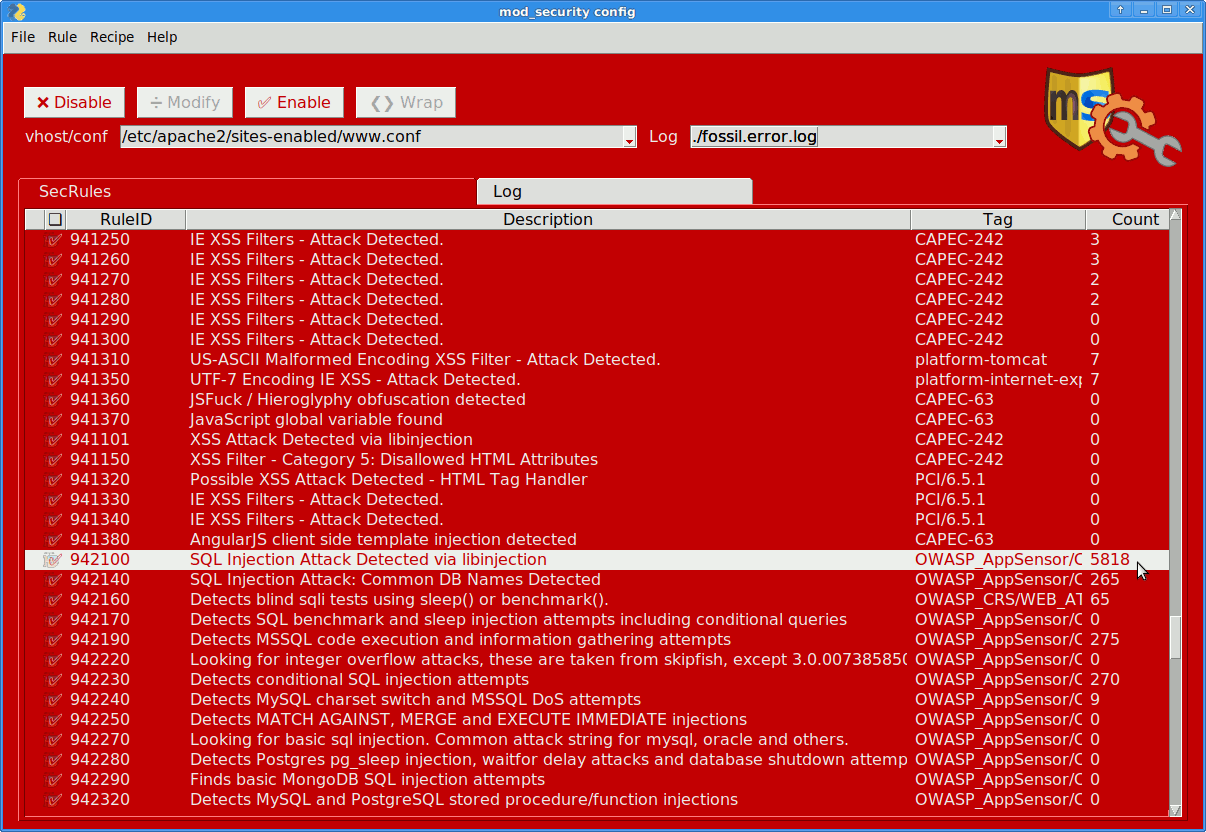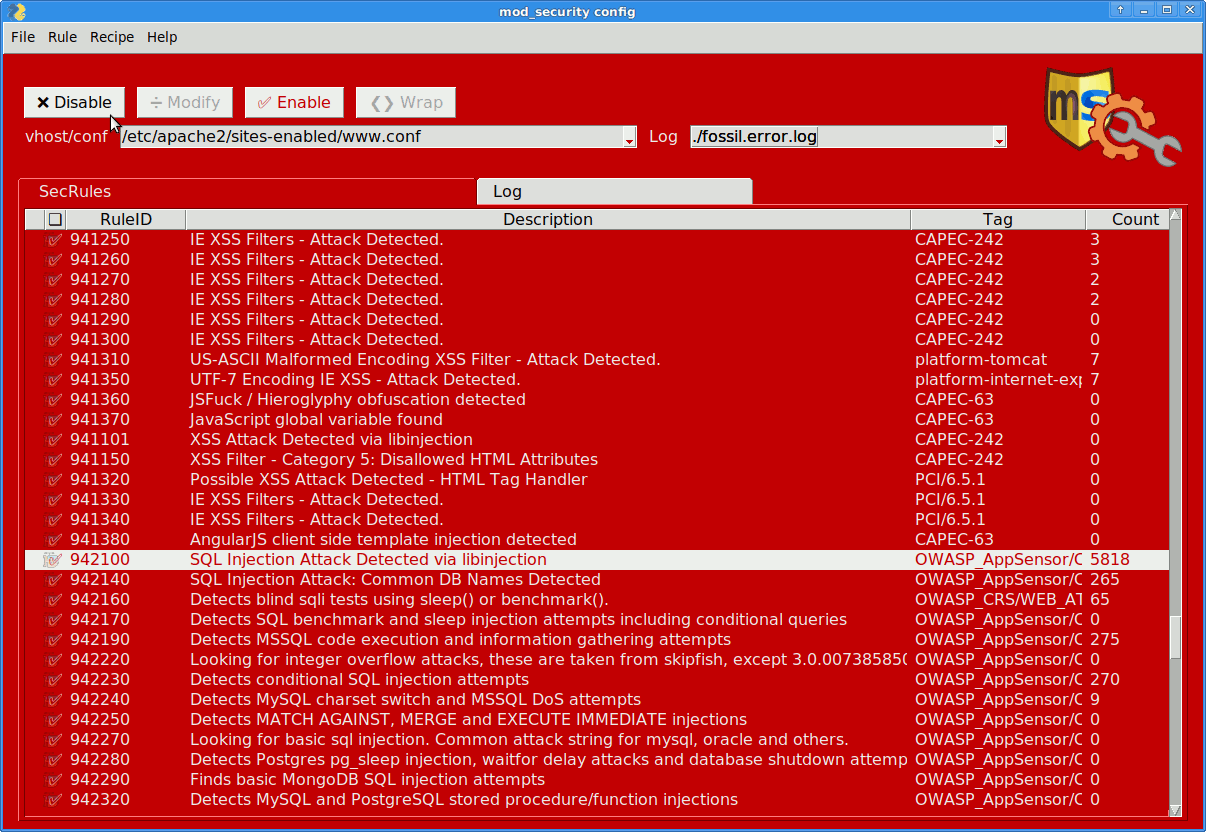
Tries to suggest false positives from error and audit logs
And configure mod_security and CoreRuleSet variables.
Runs locally, via ssh -X forwarding, or per modseccfg vps5:/ automount.
Installation
You can install this package locally or on a server:
pip3 install modseccfg
And your distro must provide a full Python 3.x installaton:
sudo apt install python3-tk ttf-unifont libapache2-mod-security2
Start options
To run the GUI locally / on test setups:
modseccfg
To start it on a server per X11 forwarding (terribly slow over SSH):
ssh -X vps5 modseccfg
Alternatively use xpra:
xpra --start ssh:vps5 --start=modseccfg
Best: use an automatic filesystem mount (with ssh shortcut/pubkey auth already configured). That’s a bit slow on startup, but pays off when browsing for details.
modseccfg vps5:/
WARNING: This will bind the remote / server root. Take care to configure the mount point (File → Settings → Utils → Remote binding), and no backup or cleanup job is running whilst modseccfg is active.This doesn’t strictly require the root user for ssh, but permissions for logs and individual *.conf files when changed (chown the ones that shall be editable). The sshfs/fuse mount will be terminated with the GUI, though.
Usage
You obviously should have Apache(2.x) + mod_security(2.9) + CRS(3.x) set up and running already (in DetectionOnly mode initially), to allow for log inspection and adapting rules.
Start modseccfg (python3 -m modseccfg)
Select a configuration/vhost file to inspect + work on.
Pick the according error.log
Inspect the rules with a high error count (→[info] button to see docs).
[Disable] offending rules
Don’t just go by the error count however!
Make sure you don’t disable essential or heuristic rules.
Compare error with access log details.
Else craft an exception rule ([Modify] or →Recipes).
Thenceforth restart Apache after testing changes (apache2ctl -t).
Notes
Preferrably do not edit default /etc/apache* files
Work on separated /srv/web/conf.d/* configuration, if available
And keep vhost settings in e.g. vhost.*.dir files, rather than multiple <VirtualHost> in one *.conf (else only the first section will be augmented).
Missing features
File permission check on remote host is non-functional still.
Doesn’t process any audit.log yet.
Can’t classify wrapped (<Location>/<FilesMatch>) rules yet.
[STRIKEOUT:No rule information dialog.]
[STRIKEOUT:No SecOption editor yet.]
[STRIKEOUT:No CRS settings (setvar:crs…) editor yet.]
Recipes are not worth using yet.
No sudo usage.
1 maintainer

Metadata
1 maintainer
Release files for modseccfg 0.3.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| modseccfg-0.3.1-py3-none-any.whl | Python 3 | none | any | Details for modseccfg-0.3.1-py3-none-any.whl |
Release files / modseccfg-0.3.1-py3-none-any.whl
| Download URL | modseccfg-0.3.1-py3-none-any.whl |
|---|---|
| Size | 79.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
75cb190b6491815264af9bde21d79ddb3d1ee3d1a2e0fa275c4faf8448182d10
|
|
BLAKE2b-256 checksum How to use checksums |
6b98ef9c517b6fe4c5e40bc212f4fd682d4ca5867c2a7322a6df1baaa5d4bc9b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
Python-urllib/3.7
|
Security for modseccfg 0.3.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














