
RTSPBrute
Inspired by Cameradar
Features
- Find accessible RTSP streams on any target
- Brute-force stream routes
- Brute-force credentials
- Make screenshots on accessible streams
- Generate user-friendly report of the results:
.txtfile with each found stream on new line.htmlfile with screenshot of each found stream
Report files
result.txt: Each target is on a new line. Import to VLC: change extension to.m3uand open in VLCindex.html: Click on the screenshot to copy its link
Installation
Requirements
python(>3.6)avPillowrich
Install with pip or your favorite PyPi package manager.
pip install rtspbrute
CLI
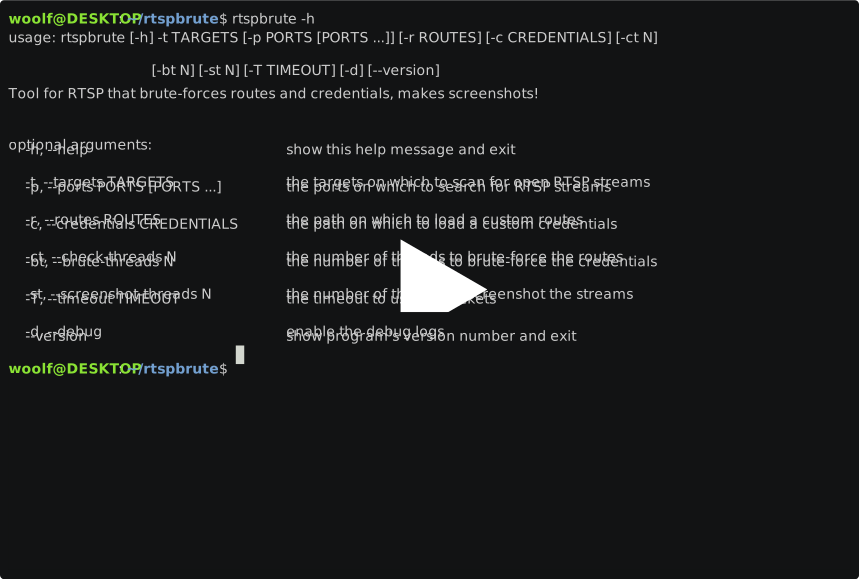
USAGE
    $ rtspbrute -t TARGETS [-p PORTS [PORTS ...]] [-r ROUTES] [-c CREDENTIALS]
                [-ct N] [-bt N] [-st N] [-T TIMEOUT] [-d] [-h]

ARGUMENTS
    -h, --help                     show this help message and exit
    -t, --targets TARGETS          the targets on which to scan for open RTSP streams
    -p, --ports PORTS [PORTS ...]  the ports on which to search for RTSP streams
    -r, --routes ROUTES            the path on which to load a custom routes
    -c, --credentials CREDENTIALS  the path on which to load a custom credentials
    -ct, --check-threads N         the number of threads to brute-force the routes
    -bt, --brute-threads N         the number of threads to brute-force the credentials
    -st, --screenshot-threads N    the number of threads to screenshot the streams
    -T, --timeout TIMEOUT          the timeout to use for sockets
    -d, --debug                    enable the debug logs

EXAMPLES
    $ rtspbrute -h
    $ rtspbrute -t hosts.txt -p 554 5554 8554 -d
    $ rtspbrute -t ips.txt -r routes.txt -c combinations.txt
    $ rtspbrute -t targets.txt -st 10 -T 10
"argument" (default_value):
- "-t, --targets" (No default value): Set the path to the input file. The file can contain IPs, IP ranges and CIDRs. Each one of them should be on a separate line, e.g.:
0.0.0.0
192.168.100.1-192.168.254.1
192.17.0.0/16
- "-p, --ports" (
554): Set custom ports, e.g.:-p 554 5554 8554 - "-r, --routes" (
routes.txt): Set custom path to the file with routes. Each route should start with/and be on a separate line, e.g.:
/1
/11
/h264
- "-c, --credentials" (
credentials.txt): Set custom path to the file with credentials. Each combination should contain:and be on a separate line, e.g.:
admin:admin
user:user
- "-ct, --check-threads" (
500): Set custom number of threads to brute-force the routes - "-bt, --brute-threads" (
200): Set custom number of threads to brute-force the credentials - "-st, --screenshot-threads" (
20): Set custom number of threads to screenshot the streams. Smaller number leads to more successful screenshots: when there's too much threads PyAV will throw errors and wouldn't connect to target. - "-T, --timeout" (
2): Set custom timeout value for socket connections - "-d, --debug" (
False): Enable debug logging todebug.logfile
1 maintainer

Metadata
1 maintainer
Release files for rtspbrute 1.0.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| rtspbrute-1.0.4.tar.gz | 34.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| rtspbrute-1.0.4-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 71.3 kB
Release files / rtspbrute-1.0.4.tar.gz
| Download URL | rtspbrute-1.0.4.tar.gz |
|---|---|
| Size | 34.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b0d46d7f16c3d2a98270a101d854dac3fbb225e7467c2d8457be83b1257e27a2
|
|
BLAKE2b-256 checksum How to use checksums |
f78babf1ed8d8646601d93c05fe639eb4fcee3ed52c1d9bf2958099fdc431f60
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.4.1 importlib_metadata/4.0.1 pkginfo/1.7.0 requests/2.25.1 requests-toolbelt/0.9.1 tqdm/4.60.0 CPython/3.9.5
|
Release files / rtspbrute-1.0.4-py3-none-any.whl
| Download URL | rtspbrute-1.0.4-py3-none-any.whl |
|---|---|
| Size | 36.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
a0ecc7510a421f3e341896b14af8e373edc07ff1566ee4dabf7a2a458b48f99e
|
|
BLAKE2b-256 checksum How to use checksums |
1d5755e4285274b8fa8b4bdc2812378afa4e1cb70502411a68675f6fe54819bd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.4.1 importlib_metadata/4.0.1 pkginfo/1.7.0 requests/2.25.1 requests-toolbelt/0.9.1 tqdm/4.60.0 CPython/3.9.5
|
Security for rtspbrute 1.0.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














