
sensitive_variables - strip local variables in tracebacks


sensitive_variables is a decorator you can apply to your functions to
prevent certain local variables from being read by debugging tools, such as the
Django crash reporter or Sentry.
Unlike Django's sensitive_variables it is independent of the web framework
you use and also does not rely on debugging tools to know about the decorator
for things to work.
Usage:
Basic
from sentry_sdk import init

from sensitive_variables import sensitive_variables

init()

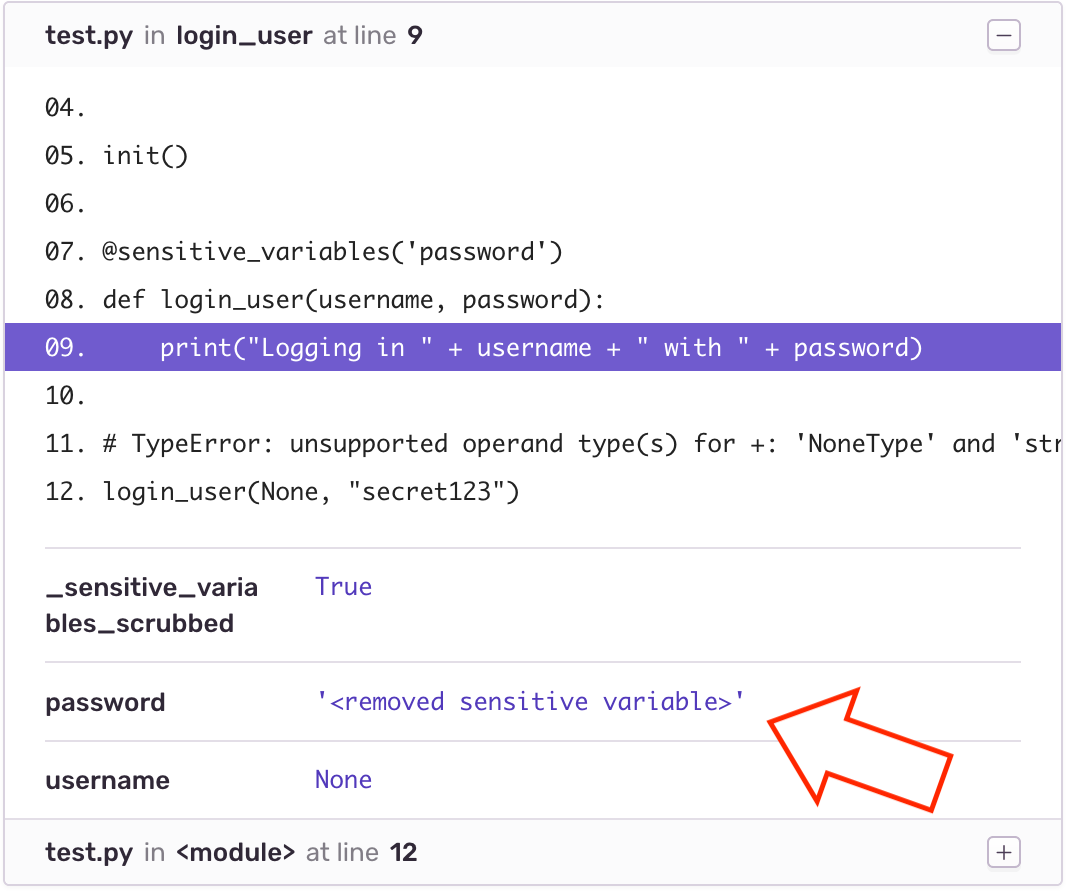
@sensitive_variables('password')
def login_user(username, password):
    print("Logging in " + username + " with " + password)

# TypeError: unsupported operand type(s) for +: 'NoneType' and 'str'
login_user(None, "secret123")
results in:
Custom scrub function
sensitive_varibles can receive a custom_scrub_fn parameter which will ba called for each local variable.
It receives the local value and variable name and must return value_has_changed, new_value.
Where value_has_changed is a boolean which represents the value being changed or not and new_value is the new value.
You can use this to extend scrub for dictionaries and any other custom type.
Example:
from sentry_sdk import init

from sensitive_variables import sensitive_variables

init()

def my_scrub_fn(value, variable_name):
    if variable_name == 'password':
        return True, 'scrubbed-value'
    return False, value


@sensitive_variables(custom_scrub_fn=my_scrub_fn)
def login_user(username, password):
    print("Logging in " + username + " with " + password)

# TypeError: unsupported operand type(s) for +: 'NoneType' and 'str'
login_user(None, "secret123")
How does it work?
When the decorated function throws an exception, sensitive_variables walks through the traceback, removes sensitive data from frame.f_locals calling custom_scrub_fn so custom processing can be made and reraises the exception.
This is usually not problematic because a function that just threw an exception is unlikely to still use its local variables.
Why would I use this over Django's decorator?
Django has a decorator also called sensitive_variables, which this package is inspired by. It sets an attribute on the function object that contains the variable names.
Debugging tools have to know about this attribute and respect it. For anything outside of the Django world, this is unlikely to be the case.
The decorator in this package will always work because it actually modifies your locals.
Why would I use this over Sentry's datascrubbing options?
-
This decorator does not couple your configuration for what is sensitive data to a specific crash reporting tool.
-
Behavior of the decorator is easily unit-testable (see
tests/folder).
Why would I not use this?
This decorator inherently requires custom code for each Python implementation. Currently this is only tested against CPython 2.7, CPython 3.6, CPython 3.7, CPython 3.8 and PyPy 2.7.
License
Licensed under the MIT, see LICENSE.
1 maintainer

Release files for sensitive-variables 0.1.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| sensitive-variables-0.1.4.tar.gz | 5.7 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| sensitive_variables-0.1.4-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 10.6 kB
Release files / sensitive-variables-0.1.4.tar.gz
| Download URL | sensitive-variables-0.1.4.tar.gz |
|---|---|
| Size | 5.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c6cba828e3d40769dfdb38a41c20a27e2df3da8541f6934a52349a8250dad93f
|
|
BLAKE2b-256 checksum How to use checksums |
1d85234bc922dd1b243240a2ce0cd88685980a6942429ad233667e11b1243437
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.23.0 setuptools/45.2.0 requests-toolbelt/0.9.1 tqdm/4.46.0 CPython/3.7.5
|
Release files / sensitive_variables-0.1.4-py3-none-any.whl
| Download URL | sensitive_variables-0.1.4-py3-none-any.whl |
|---|---|
| Size | 4.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
8534c557da3c3f03096a3eabbdecdf3a5b704430351bc237dcbc55081eef44df
|
|
BLAKE2b-256 checksum How to use checksums |
e1542b75f7c7ceb487d86be66e29a277ffc0ebc414eebb2d55b47abedae28ef4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.23.0 setuptools/45.2.0 requests-toolbelt/0.9.1 tqdm/4.46.0 CPython/3.7.5
|














