
World Serpant Search
World Serpant Search is a command-line tool for vulnerability detection. It allows you to scan directories for various types of vulnerabilities, including XSS vulnerabilities, authentication bypass vulnerabilities, and package vulnerabilities using the National Vulnerability Database (NVD).
Installation
To install World Serpant Search, you can use pip:
pip install serpant
Usage and Examples
To use the CLI, follow the instructions below:
-
Install the CLI using pip:
pip install serpant
-
Run the CLI using the following command:
serpant
-
Use the available commands to perform vulnerability scans. For example:
serpant scan /path/to/directory
-
For scan local repo:
serpant scan /path/to/directory
-
For SQL injection detection:
serpant sqlinjection /path/to/directory
-
For search authentication bypass in local repo:
serpant abypass /path/to/directory
-
For detect xss vulnerabilities repo:
serpant xss /path/to/directory
-
For search vulnerabilities in national vulnerability databae:
serpant nvd package name
-
For check sensitive data exposure in local repo:
serpant sensetive /path/to/directory
-
For check unsecure deserialization:
serpant deserialization /path/to/directory
-
For detect access control vulnerabilities:
serpant accesscontrol /path/to/directory
Model Logic Explanation
CommandLineInterface
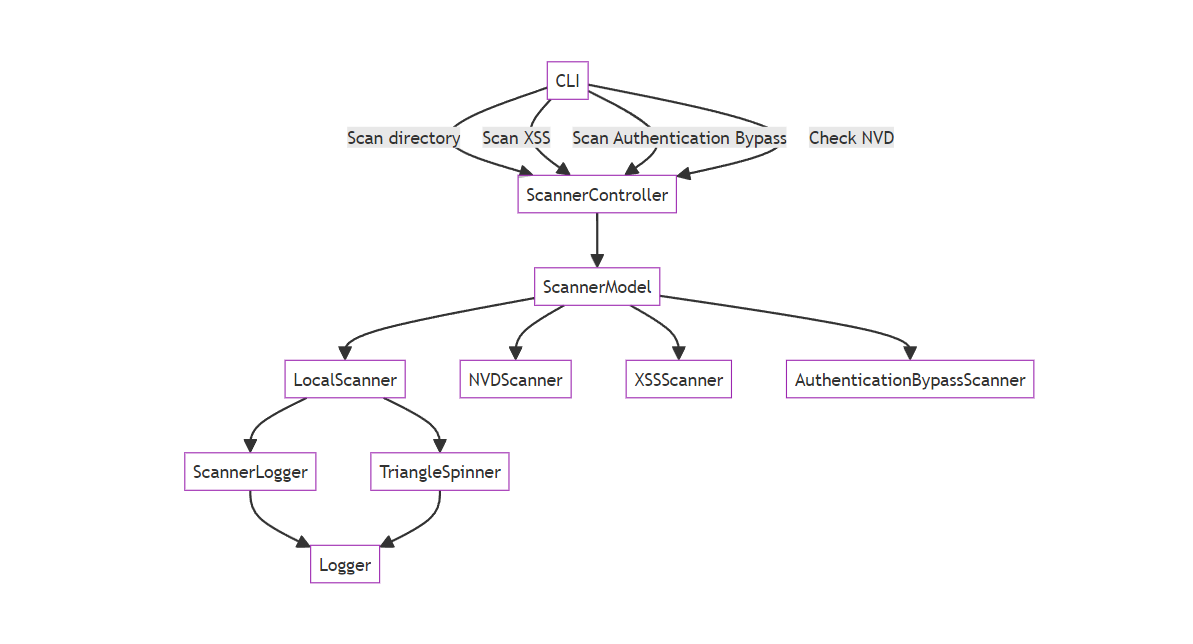
The CommandLineInterface class represents the command-line interface for the CLI tool. It provides methods for initializing the CLI, printing the banner, and running the interface.
__new__(cls): This method ensures that only one instance of theCommandLineInterfaceclass is created using the Singleton design pattern.__init__(self): Initializes the command-line interface and prints the banner._print_banner(self): Prints the banner when the CLI initializes.run(self): Runs the command-line interface by parsing arguments and executing corresponding commands.
ScannerController
The ScannerController class is responsible for controlling scanning operations and interacting with the underlying data and business logic.
scan_local_directory(self, directory): Scans a local directory for vulnerabilities.scan_xss_directory(self, directory): Scans a local directory for XSS vulnerabilities.scan_authentication_bypass_directory(self, directory): Scans a directory for authentication bypass vulnerabilities.scan_package_vulnerabilities_nvd(self, package): Checks package vulnerabilities using the National Vulnerability Database (NVD).check_sensitive_files_exposure(self, directory): Checks for sensitive file exposure in a directory.detect_insecure_deserialization(self, directory): Detects insecure deserialization vulnerabilities.detect_access_control_vulnerabilities(self, directory): Detects access control vulnerabilities.
Business Logic
Local Repository Scan
Implement a feature to scan a local directory or project for common vulnerabilities such as exposed secrets, hardcoded credentials, or sensitive data.
Remote Repository Scan
Extend the application to support scanning remote repositories by providing a URL. This could involve fetching the repository contents and analyzing them for vulnerabilities.
SQL Injection Detection
Implement a feature to detect SQL injection vulnerabilities in code files or database configurations.
Cross-Site Scripting (XSS) Detection
Develop functionality to detect cross-site scripting vulnerabilities in web applications or scripts.
Sensitive Data Exposure Detection
Implement a feature to identify instances where sensitive data such as API keys, passwords, or personal information is exposed in the codebase.
Dependency Vulnerability Check
Integrate with package vulnerability databases (e.g., NVD) to check for known vulnerabilities in project dependencies.
Authentication Bypass Detection
Implement checks to identify potential authentication bypass vulnerabilities in the application.
Insecure Deserialization Detection
Develop functionality to detect insecure deserialization vulnerabilities in the codebase.
Sensitive File Exposure Check
Implement checks to identify sensitive files (e.g., configuration files, log files) that may be exposed to unauthorized access.
Access Control Vulnerability Check
Develop checks to identify access control vulnerabilities, such as insecure direct object references or missing authorization checks.
License
This project is licensed under the MIT License. See the LICENSE file for details.
1 maintainer

Metadata
1 maintainer
Release files for serpant 1.2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| serpant-1.2.1.tar.gz | 11.9 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| serpant-1.2.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 26.6 kB
Release files / serpant-1.2.1.tar.gz
| Download URL | serpant-1.2.1.tar.gz |
|---|---|
| Size | 11.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
17a854ede045a1fbd2e4a3a93d3de5d8e09dae7d5f83c09bc4db160c55f38a87
|
|
BLAKE2b-256 checksum How to use checksums |
975625f34529cbe101b5286f17976f8efb4d003029b1447f8819409b4e8054d9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.11.4
|
Release files / serpant-1.2.1-py3-none-any.whl
| Download URL | serpant-1.2.1-py3-none-any.whl |
|---|---|
| Size | 14.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5eafc00576fddc483437876df1c6119d819f64cc04ab905c2fa4f05f3b0b6195
|
|
BLAKE2b-256 checksum How to use checksums |
b7d1cdecf75845dd495cbf63b30a41aadadd8635441ed9ffda96793efaf731ce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.11.4
|














