
sumo_docker_pipeline
The package sumo_docker_pipeline enables you to run a traffic simulator SUMO efficiently
and to interact with Python easily.
The package is valid when you need to run SUMO iteratively.
SUMO is often tricky to install locally because of its dependencies. Thus, it's a straightforward idea to run SUMO in a docker container.
However, another issue arises when we run SUMO in a docker container. It is challenging to construct a pipeline between SUMO and API.
The package provides an easy-to-use API; at the same time, SUMO runs in a docker container.
Requirement
- python > 3.5
- docker
- docker-compose
Install
Pull the image (or build of a docker image with SUMO)
The existing image is on the Dockerhub.
docker pull kensukemi/sumo-ubuntu18
If you prefer to build with yourself, you run the following command.
docker-compose build
Install a python package
make install
Example case: iterative run with parameter updates
Let's say that you want to run SUMO iteratively. At the same time, you want to change input parameters depending on the results of a simulation.
In that case, you need to check the output of SUMO and update the parameters.
sumo_docker_pipeline package enables you to make the process automatic.
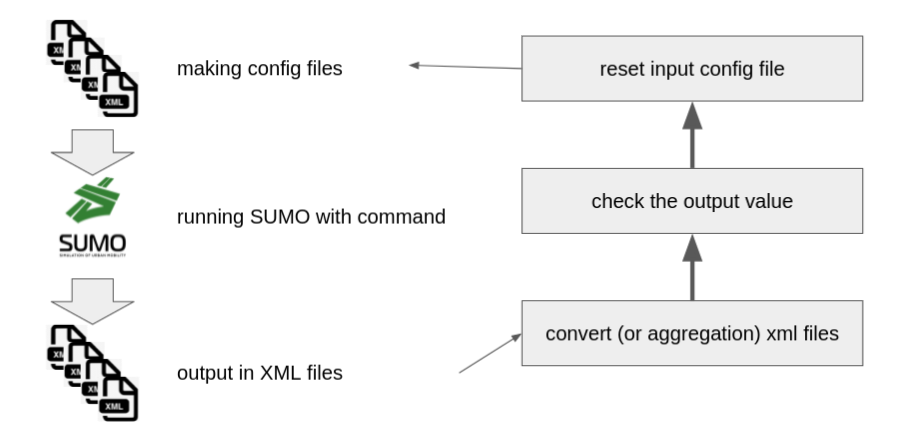
Setups
- creation of a directory where you save SUMO's configuration.
- creation of template-files of SUMO's configuration.
- running the pipeline.
1. creation of a directory
It is a directory that SUMO accesses.
Let's say that we create test/resources/config_template
2. creation of SUMO's configuration
You prepare configuration files which SUMO requires. The format of the conf. files are totally same as SUMO's requirements.
The only difference is that you write wildcard ? at the place where you wanna replace during pipeline.
For example, tests/resources/config_template/grid.flows.xml has the following element,
<vType vClass="passenger" id="passenger" tau="0.5" speedDev="0.1" maxSpeed="?" minGap="?" accel="?" decel="?" latAlignment="center" />
With the sumo_docker_pipeline package, you can replace the attributes with the wildcards ?.
3. running the pipeline
See examples directory.
For developer
pytest tests
license and credit
The source code is licensed MIT. The website content is licensed CC BY 4.0.
@misc{sumo-docker-pipeline,
  author = {Kensuke Mitsuzawa},
  title = {sumo-docker-pipeline},
  year = {2021},
  publisher = {GitHub},
  journal = {GitHub repository},
  howpublished = {\url{https://github.com/Kensuke-Mitsuzawa/sumo_docker_pipeline}},
}
1 maintainer

Metadata
1 maintainer
Release files for sumo-docker-pipeline 2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| sumo_docker_pipeline-2.0.tar.gz | 13.4 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| sumo_docker_pipeline-2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 30.4 kB
Release files / sumo_docker_pipeline-2.0.tar.gz
| Download URL | sumo_docker_pipeline-2.0.tar.gz |
|---|---|
| Size | 13.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c1e84f46d4502d8178760f0dc2b56b862de2807a22de44043554f6627f6398fe
|
|
BLAKE2b-256 checksum How to use checksums |
6bf90d9a16f92fcc2c7891a2b29c24362f048fb3805d8ef7916b2f4a6ad9923a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.1.7 CPython/3.8.8 Linux/5.4.0-91-lowlatency
|
Release files / sumo_docker_pipeline-2.0-py3-none-any.whl
| Download URL | sumo_docker_pipeline-2.0-py3-none-any.whl |
|---|---|
| Size | 16.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
695dc854cf53d96bb743881d37d2ec268a35c1d074c1979bd38914a57fab9289
|
|
BLAKE2b-256 checksum How to use checksums |
539b4088ba0774c634d63c7757e841ffdce1820d3f90967e66a9eced21b17bce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/1.1.7 CPython/3.8.8 Linux/5.4.0-91-lowlatency
|
Security for sumo-docker-pipeline 2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














