
vue-lexer

A Vue lexer for Pygments (based on jsx-lexer)
Installation
$ pip install vue-lexer
Usage with Sphinx
To use within Sphinx, simply specify vue for your code-block:
.. code-block:: vue

    <template>
      <p>{{ greeting }} World!</p>
    </template>

    <script>
    module.exports = {
      data: function () {
        return {
          greeting: 'Hello'
        }
      }
    }
    </script>

    <style scoped>
    p {
      font-size: 2em;
      text-align: center;
    }
    </style>
Usage with mkdocs
First, you need to create the CSS for the highlighting:
$ pygmentize -S default -f html -a .codehilite > code/pygments.css
Then, add the following to your mkdocs.yml:
markdown_extensions:
  - codehilite
extra_css: [pygments.css]
Now, you can use vue in your code blocks:
```vue
<template>
  <p>{{ greeting }} World!</p>
</template>

<script>
module.exports = {
  data: function () {
    return {
      greeting: 'Hello'
    }
  }
}
</script>

<style scoped>
p {
  font-size: 2em;
  text-align: center;
}
</style>
```
Examples
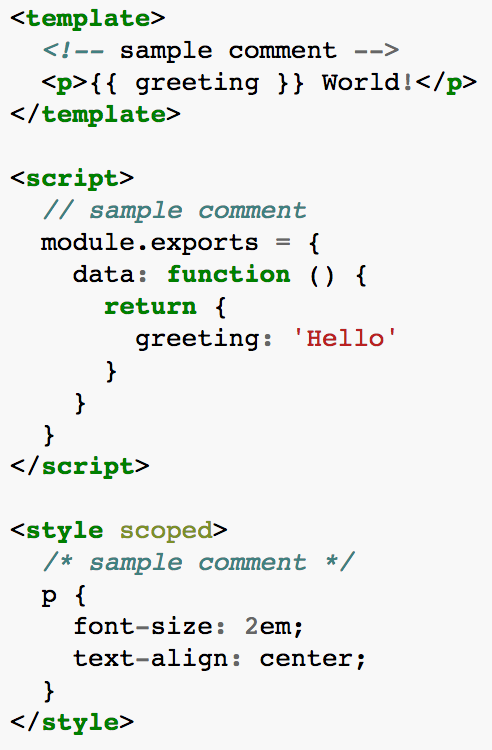
Example 1:
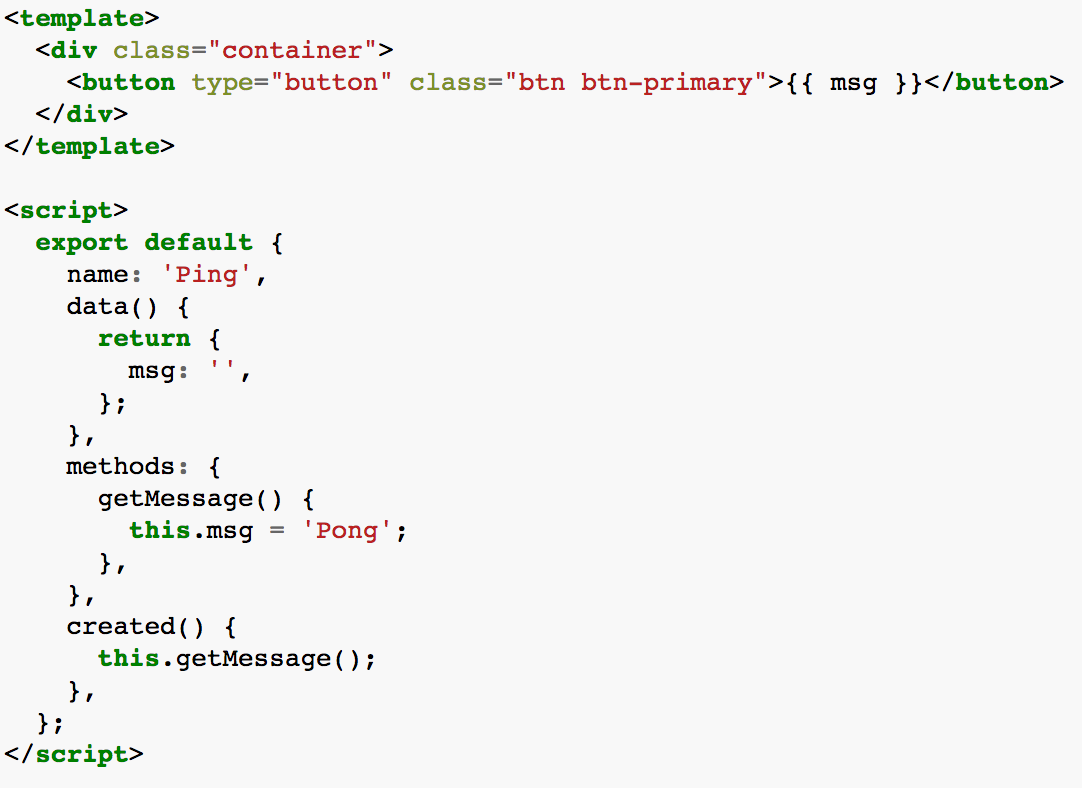
Example 2:
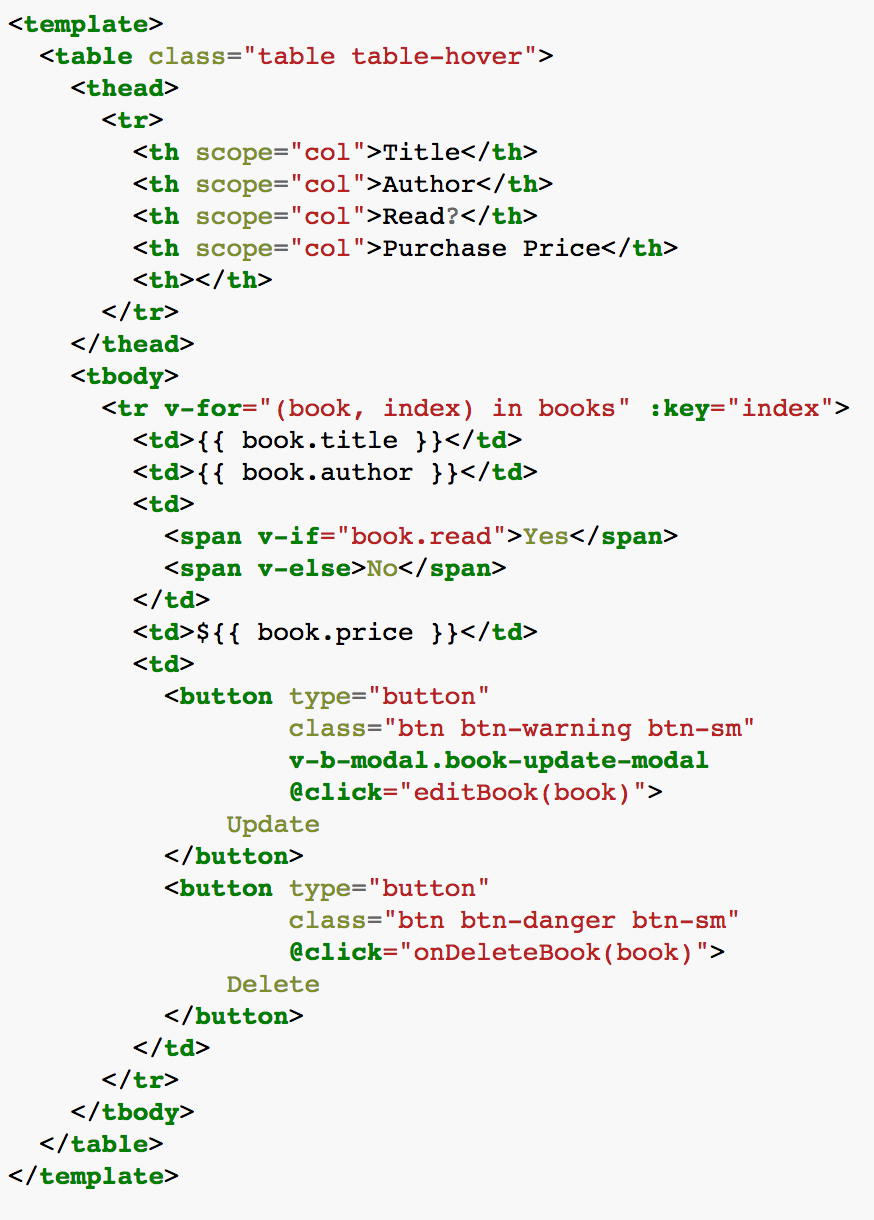
Example 3:
1 maintainer

Metadata
1 maintainer
Release files for vue-lexer 0.0.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| vue-lexer-0.0.4.tar.gz | 2.9 kB | Without provenance | Details |
Release files / vue-lexer-0.0.4.tar.gz
| Download URL | vue-lexer-0.0.4.tar.gz |
|---|---|
| Size | 2.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
6046623116bca2e25919225ba3e7fb2009a9d6cfadb905af9792859da8f9da62
|
|
BLAKE2b-256 checksum How to use checksums |
7ef34c18d5594879158e7e00418ad58d528453785906ce24911f9ffaa210398f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.13.0 pkginfo/1.5.0.1 requests/2.21.0 setuptools/40.6.2 requests-toolbelt/0.9.1 tqdm/4.31.1 CPython/3.7.4
|
Security for vue-lexer 0.0.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














