
wagtail-netlify
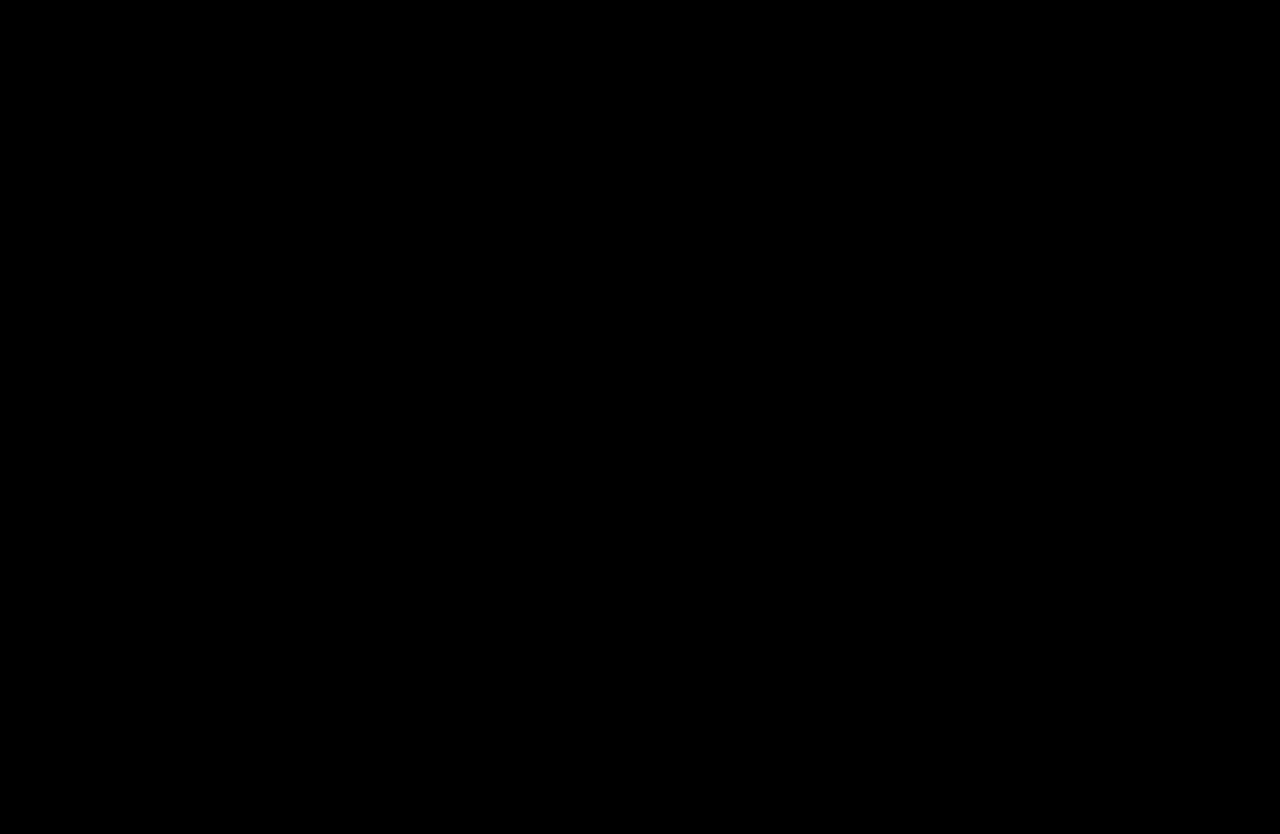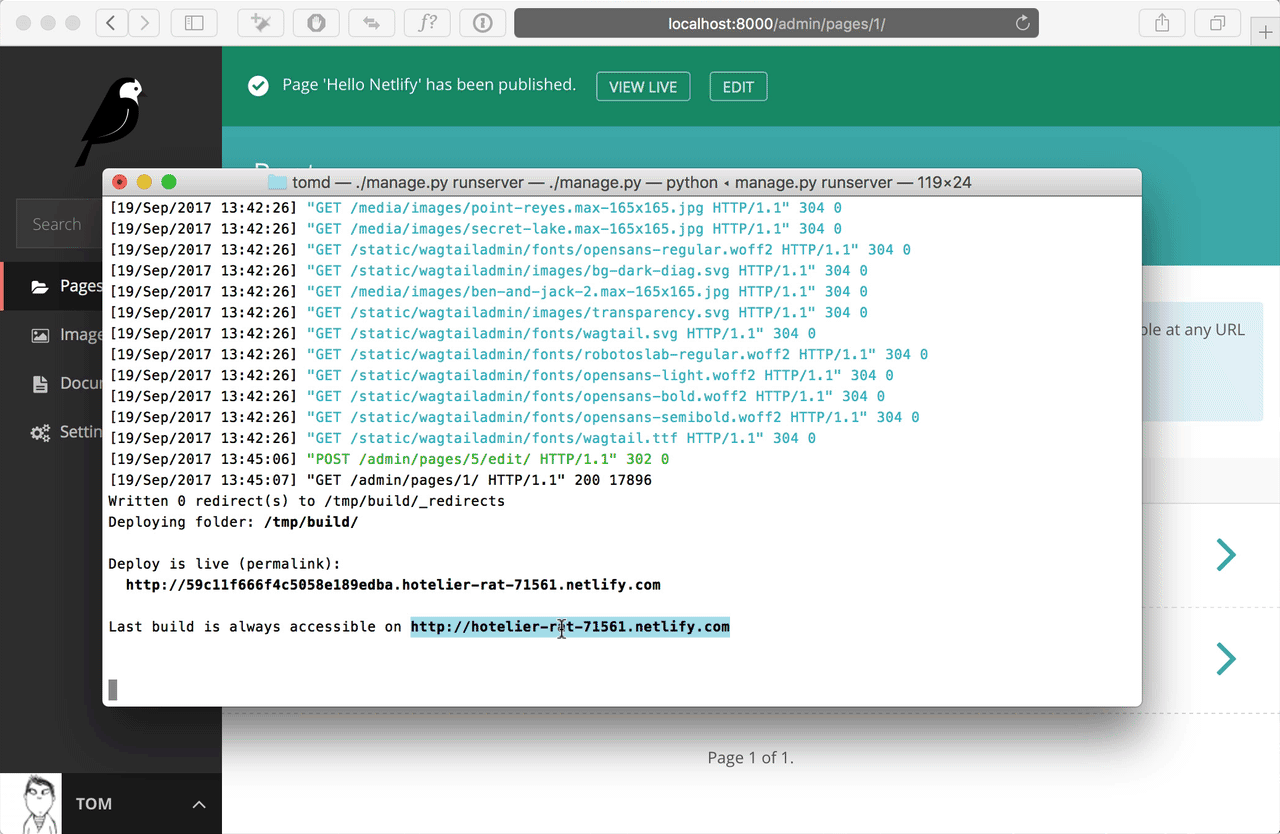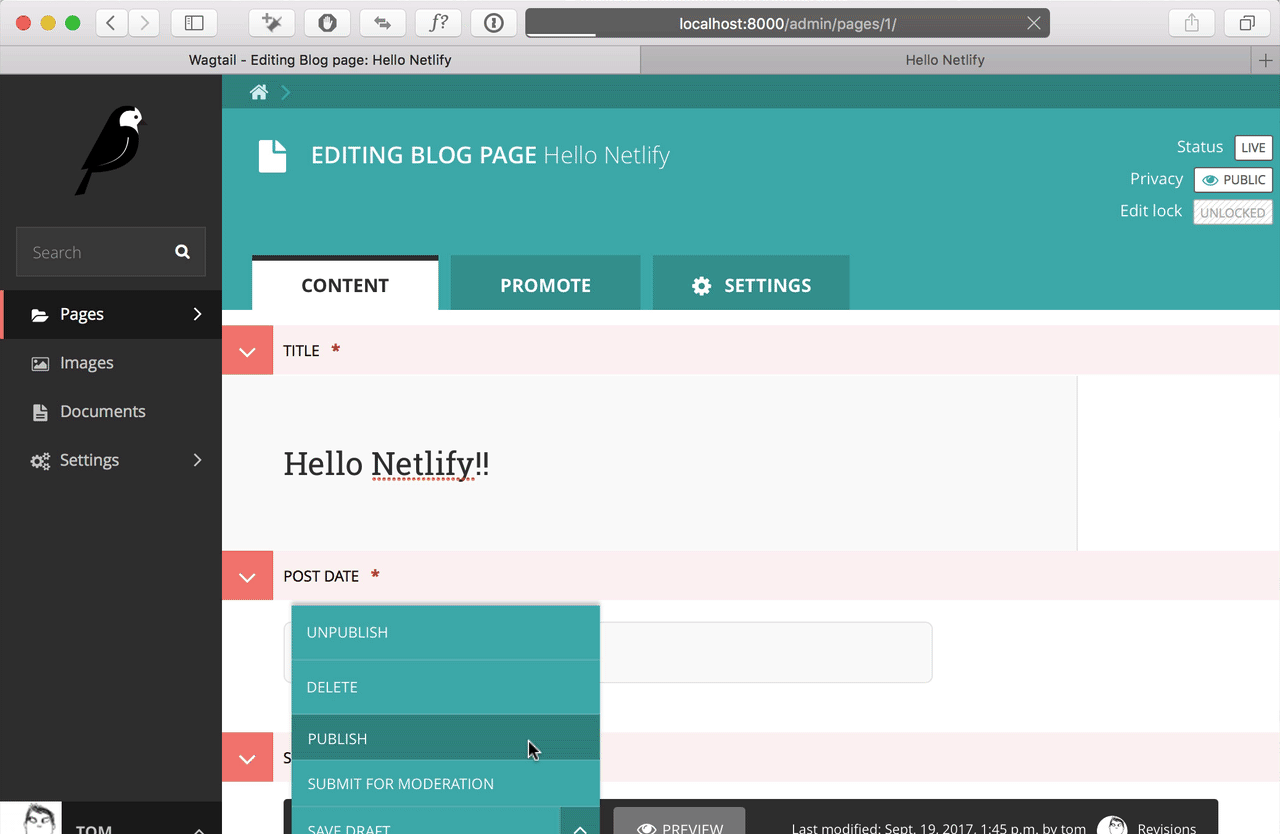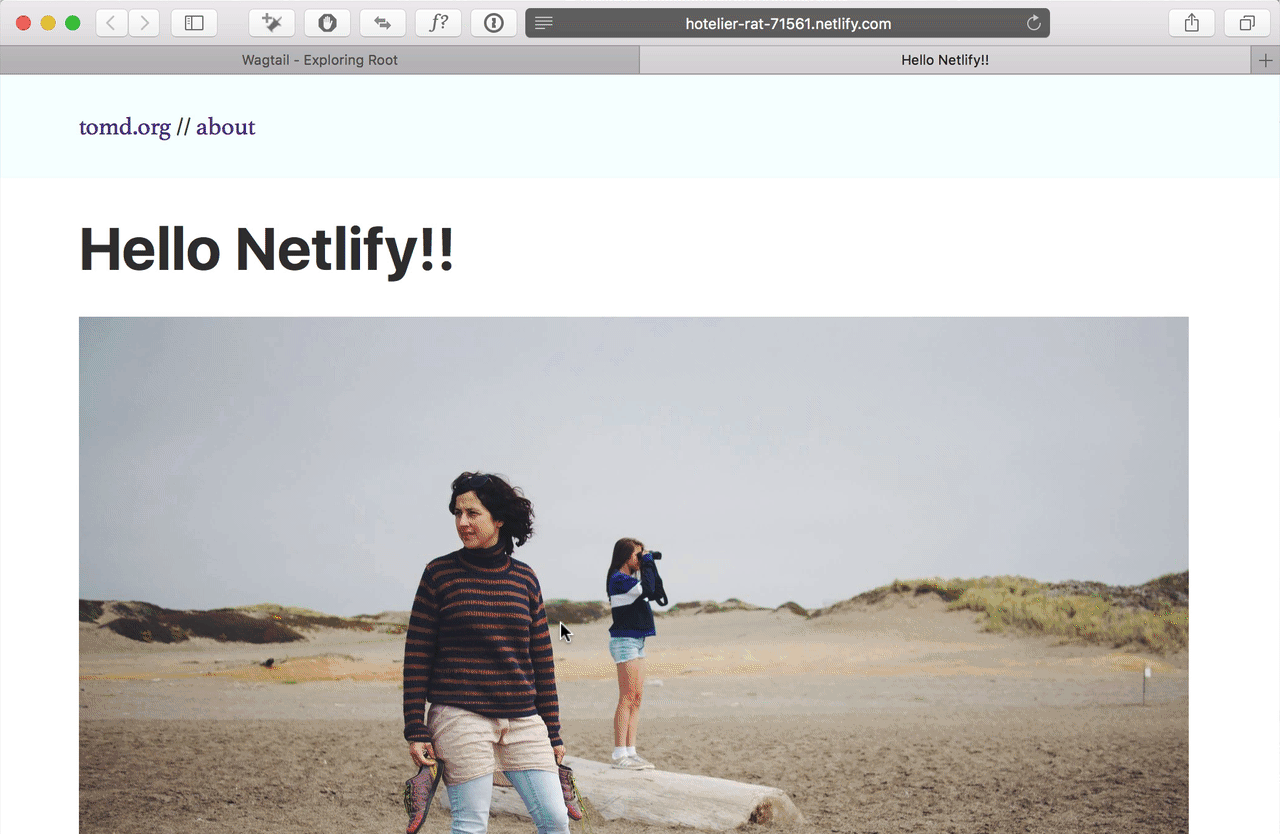
Deploy your Wagtail site on Netlify. Features include:
- automatic deployment when pages are published
- a new
netlifymanagement command - conversion of Wagtail redirects to Netlify's format
Installation
- Install and configure Wagtail Bakery, if you haven't already.
- Install Netlify CLI v2.x, if you haven't already.
- Install Wagtail-Netlify via pip (with
pip install wagtailnetlify).
Configuration
- Add
wagtailnetlifyto yourINSTALLED_APPS. - Run the migrations:
./manage.py migrate wagtailnetlify. - Add
NETLIFY_PATHorNETLIFY_BUILD_HOOKto your settings.
Check the Settings section below for more customisation options.
Usage
If NETLIFY_AUTO_DEPLOY is set to True, Wagtail will automatically deploy your site every time a page is published.
or
To deploy changes manually, use ./manage.py netlify.
To generate redirects without deploying, use the -n or --no-deploy flag: ./manage.py netlify --no-deploy.
To trigger a build on Netlify's servers, configure settings.NETLIFY_BUILD_HOOK and use the -t or --trigger-build flag: ./manage.py netlify --trigger-build.
Settings
NETLIFY_PATH
The path to the Netlify CLI. Hint: type which netlify to check the location.
NETLIFY_SITE_ID
Default: None
If set, deploy to that specific Netlify site.
If not set, the Netlify CLI might prompt you to select one.
NETLIFY_API_TOKEN
Default: None
If set, the Netlify CLI will not prompt you to click the authentication link in the console. It can be useful when deployed to a remote server where you don't see the console output.
Connect to your Netlify account to generate a token and then set the settings. Warning: You should never check credentials in your version control system. Use environment variables or local settings file instead.
NETLIFY_AUTO_DEPLOY
Default: False
Whether to automatically deploy your site to Netlify every time you publish a page. This make take between a few seconds and a few minutes, depending on the size of your site, and the number of pages which are affected by your change. If you have configured settings.NETLIFY_BUILD_HOOK, publishing a page will trigger a build on Netlify's servers.
NETLIFY_DEPLOY_FUNCTION
Default: wagtailnetlify.models.deploy
The function to be called when a deploy is triggered (excluding when triggered manually with the ./manage.py netlify command). It can be useful if you want to use your own task runner (like Celery) instead of the built-in threading model.
The function needs to be a valid Django signal receiver.
NETLIFY_BUILD_HOOK
Default: None
The URL of a Netlify build hook. If provided, ./manage.py netlify --trigger-build will call this hook, triggering a build
on Netlify's servers. This may be useful if you have a headless front-end on Netlify which handles its own static site generation,
e.g. Nuxt, Next or Gatsby. See https://docs.netlify.com/configure-builds/build-hooks/ for more details.
Optional admin view and endpoints
Netlify can send a webhook after a successful deployment. This app provides an endpoint for that webhook and an admin view of completed deployments. To enable this view:
- Add
wagtail.contrib.modeladminto yourINSTALLED_APPS - Update your project's
urls.py:
# in your imports
from wagtailnetlify import urls as netlify_urls

# in urlpatterns, before including wagtail_urls
url(r"^netlify/", include(netlify_urls)),
- In Netlify's admin interface for your app, add http://yourdomain/netlify/success as a URL to notify for the outgoing webhook on Deploy succeeded events (in Settings / Build & deploy / Deploy notifications).
The view will be available under Settings / Deployments in your site's admin.
Including the wagtailnetlify URLs will also enable a view at /netlify/redirects, which outputs any Wagtail redirects in Netlify's plain text format. This may be useful if you are using Netlify to host a headless front-end for your Wagtail site.
Development
Releases
- Ensure you have the latest versions of
pip,setuptoolsandtwineinstalled in your virtual environment. - Ensure your
masterbranch is up to date. - Create a new branch (e.g.
release/v1.1.3) for the release of the new version. - Update the version number in
wagtailnetlify/__init__.pyfollowing Semantic Versioning. - Update
CHANGELOG.md. - (Optional) If you need to verify anything, use
make publish-testto upload to https://test.pypi.org and enter your PyPi test credentials as needed. - On GitHub, create a pull request and squash merge it.
- Checkout and pull the
masterbranch locally. - Use
make publishand enter your PyPi credentials as needed. - On GitHub, create a release and a tag for the new version.
1 maintainer

Metadata
1 maintainer
Release files for wagtailnetlify 0.7
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| wagtailnetlify-0.7.tar.gz | 8.4 kB | Without provenance | Details for wagtailnetlify-0.7.tar.gz |
Release files / wagtailnetlify-0.7.tar.gz
| Download URL | wagtailnetlify-0.7.tar.gz |
|---|---|
| Size | 8.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
96f57a10179be835fa9ee703c42591d6b9284c8043953a951f1684eb1812c282
|
|
BLAKE2b-256 checksum How to use checksums |
1d73b243278091bdbf3ecd9a40476da30b48c9153b0bbabb1e53fba3737e0e37
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.1.1 pkginfo/1.5.0.1 requests/2.23.0 setuptools/46.0.0 requests-toolbelt/0.9.1 tqdm/4.46.0 CPython/3.7.7
|
Security for wagtailnetlify 0.7
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














