
Find sensitive information using dorks from different search-engines.




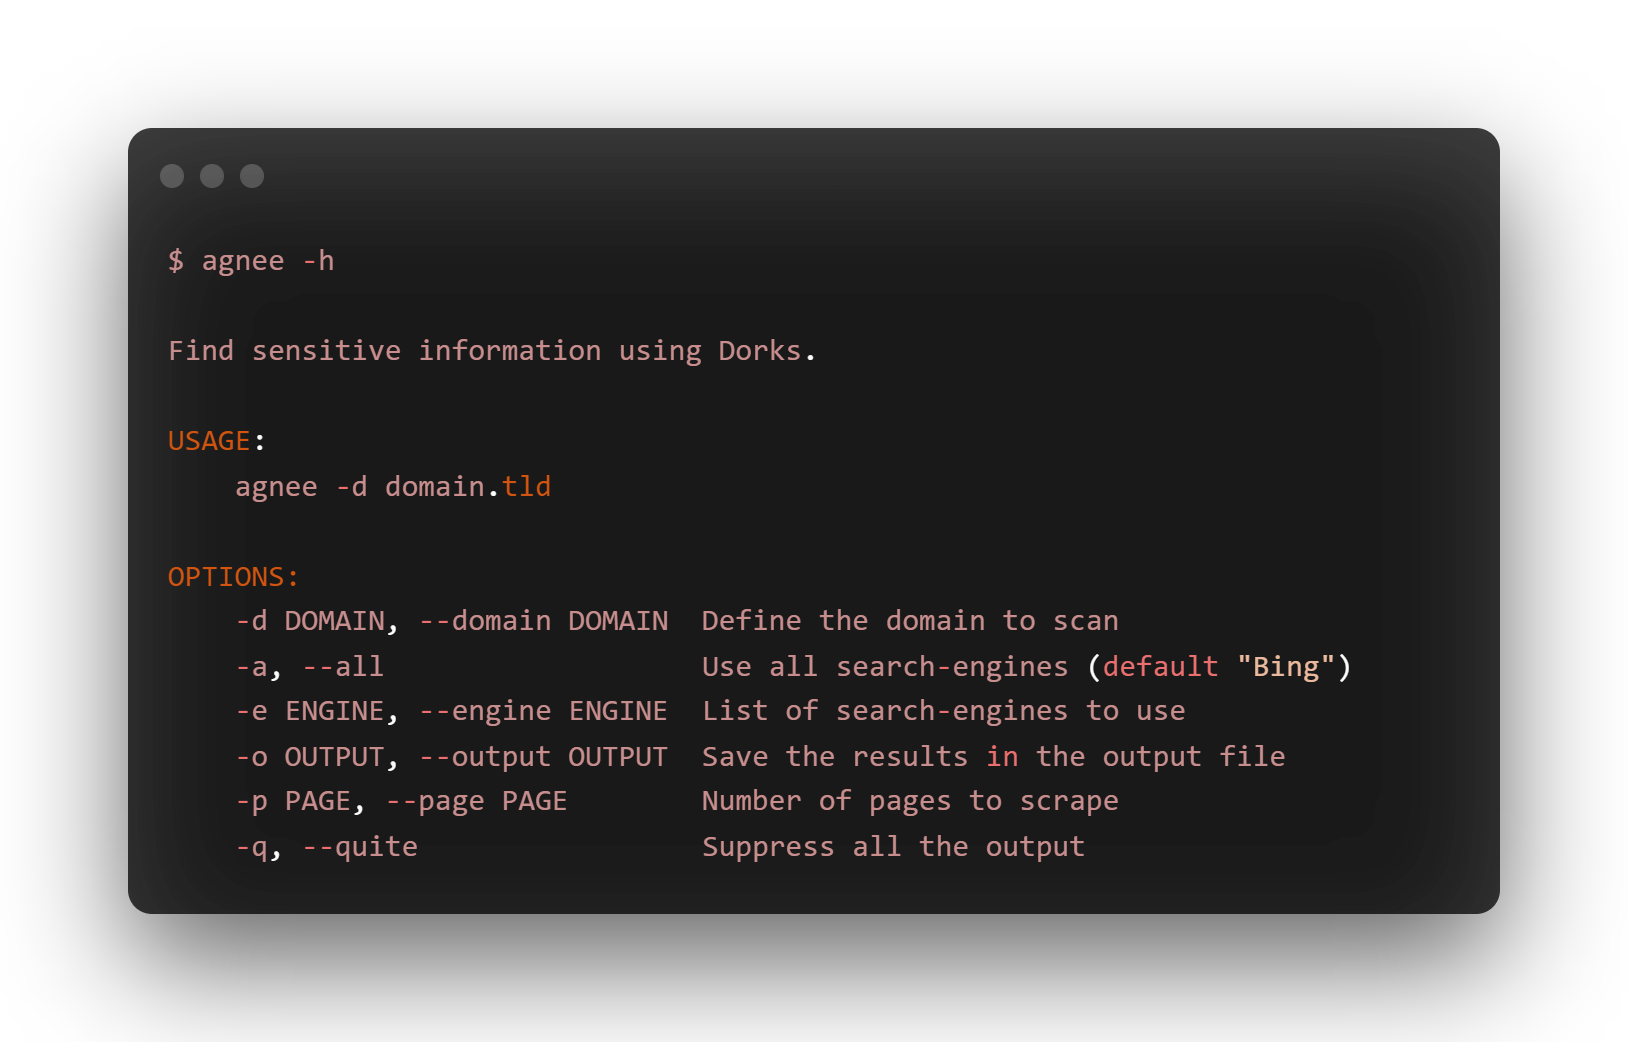
Agnee uses search_engines to find sensitive information about given domain using multiple dorks through mutltiple search-engines. I have modified some code of search_engines and used it in this script to get the custom results and currently it only find results from bing, google and yahoo (will implement more in future for sure).
Installation
sudo pip3 install git+https://github.com/R0X4R/Search-Engines-Scraper.git && sudo pip3 install agnee
Note: Before installing agnee you must need git and python3 installed on your system.
Usage
-
Simple usage arguments
$ agnee -d testphp.vulnweb.com

https://www.exploit-db.com/ghdb/6630
https://www.exploit-db.com/ghdb/5665
http://testphp.vulnweb.com/secured/phpinfo.php
-
To use a specific engine
$ agnee -d testphp.vulnweb.com -e yahoo

Yahoo Dork: inurl:"/.git" testphp.vulnweb.com -github

https://www.exploit-db.com/ghdb/6630
https://www.exploit-db.com/ghdb/5665
http://testphp.vulnweb.com/secured/phpinfo.php
-
To search specific number of pages
$ agnee -d testphp.vulnweb.com -p 1
-
Use all the search-engines
$ agnee -d testphp.vulnweb.com -all
Note: Sometimes google may block your requests so you need to wait for few hours.
Donate
If this tool helped you or you like my work
buymeacoffee.com/R0X4R |
pmny.in/bIKNZngt4ys1 |
ko-fi.com/R0X4R |
|---|
Warning: This code was originally created for personal use, do not abuse the traffic, please use with caution.
1 maintainer

Metadata
1 maintainer
Release files for agnee 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| agnee-1.1.1.tar.gz | 5.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| agnee-1.1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 11.1 kB
Release files / agnee-1.1.1.tar.gz
| Download URL | agnee-1.1.1.tar.gz |
|---|---|
| Size | 5.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
70300f4262a62efdc535fb7dab589bcce78a2de74cf9664ac74469e98c4a63c6
|
|
BLAKE2b-256 checksum How to use checksums |
ce2561f9eabd2a957bf131250159167e9ed487435533e3da1892c976a7bab418
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.8.10
|
Release files / agnee-1.1.1-py3-none-any.whl
| Download URL | agnee-1.1.1-py3-none-any.whl |
|---|---|
| Size | 5.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1f259b3b81bef1a22e5e101d76e0e6feb77014d5ea61ebb574140df924f29f06
|
|
BLAKE2b-256 checksum How to use checksums |
2545f62f27e08d73b0fd8119d404b3f36b3990a4733411a8a010202bc6421a56
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.8.10
|
Security for agnee 1.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














