

CAF.cvt


CAF.cvt is a python model that takes climate and transport data and generates a climate risk assessment for the North's key transport infrastructure.
Table of Contents
Overview
What does it do?
The Common Analytical Framework (CAF) Climate Vulnerability Tool (CVT) is a geospatial python package that translates complex climate and infrastructure data into a set of climate risk assessments for the North of England's key transport networks.
Main Features
-
Data Cleaning - Reads and cleans a wide variety of climate and transport datasets, preprocessing into a standard format in preparation for analysis.
-
Apply Functional Rules - Applies a set of funtional rules and spatial overlays to the climate data to translate complex values into distinct hazard categories and grids.
-
Infrastructure Layering - Layers infrastructure on top of hazard grids to assign risk to the transport assets.
Work-in-Progress
There are currently no work-in-progress features.
Who is it for?
- Target audience: Transport Analysts, Transport Planners, Climate Researchers
- CAF Analytical Stage: Modelling
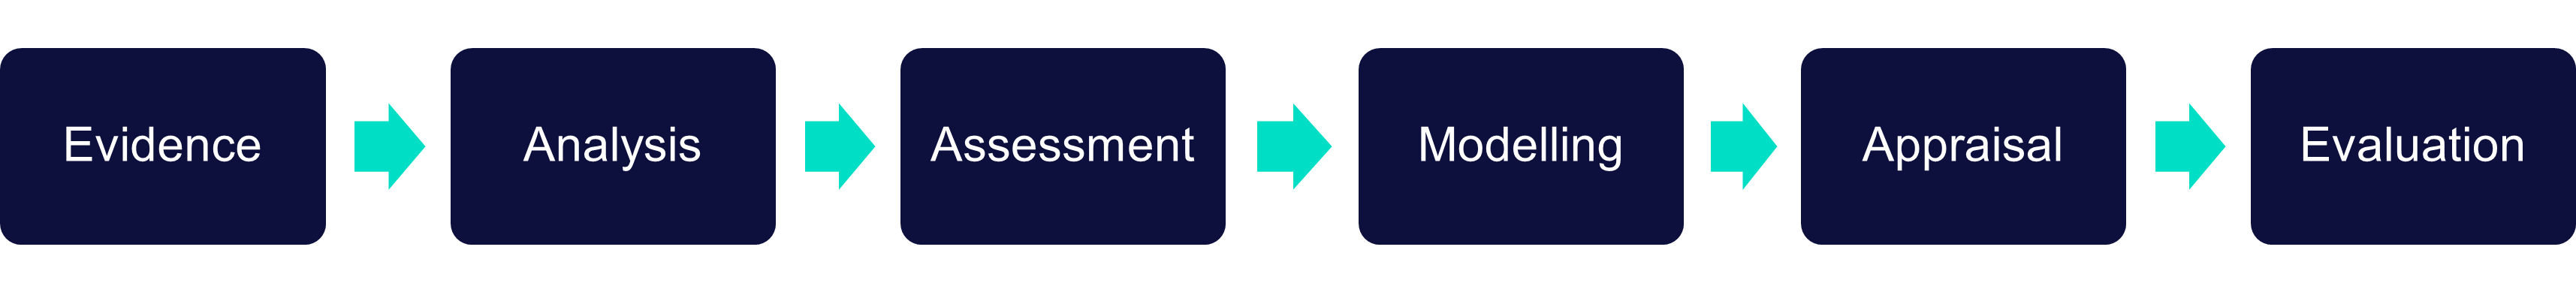
For more details on CAF Analytical Stages see the description within TfN's GitHub homepage
Where to get it
The latest released version are available at the Python Package Index (PyPI) and on Conda.
conda install -c conda-forge caf.cvt
pip install caf.cvt
Installation from GitHub
The latest, unreleased, version can be installed directly from GitHub using:
pip install "git+https://github.com/transport-for-the-north/caf.cvt"
Usage
CAF.cvt provides and Command-line (CLI) and graphical interface (GUI) to use many of it's features without the need to write any Python code, see the Tool Usage section of the user guide for more details.
Command Line
The tool can be run from command line, with the command:
caf.cvt
See Command-Line Interface (User Guide) for full explanations of the parameters.
Documentation
The code documentation is hosted at https://cafcvt.readthedocs.io/en/stable/.
What is CAF?
This tool is part of TfN's Common Analytical Framework (CAF). CAF is Transport for the North's structured suite of analytical tools designed to support transport modelling, appraisal, and strategic decision-making.
More information on CAF and details on other CAF tools can be found on TfN's GitHub Homepage.
Contribution
We encourage use of, and contributions to, the repositories within this organisation, licenses are provided within the repositories and the organisation contribution guide provides details for contributions.
Contact Us
For further information about using this tool or CAF tools in your projects and work contact Transport for the North - TfNOffer@transportforthenorth.com
Metadata
Release files for caf.cvt 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| caf_cvt-0.2.0.tar.gz | 49.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| caf_cvt-0.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 96.6 kB
Release files / caf_cvt-0.2.0.tar.gz
| Download URL | caf_cvt-0.2.0.tar.gz |
|---|---|
| Size | 49.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
de270fc1638ba8512ef53bb476cdd00b12207c6e03d5e43a09d874c5ad57b7db
|
|
BLAKE2b-256 checksum How to use checksums |
4f0961f6360ec70a529cc6a717ec08343f7880eb2b4fe94263fb5e13d5fed39b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 13, 2026.
Transparency logRelease files / caf_cvt-0.2.0-py3-none-any.whl
| Download URL | caf_cvt-0.2.0-py3-none-any.whl |
|---|---|
| Size | 47.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
fab28233a16781eda3dd2755988e468821e726e9f878d31c7bd644afb767aa35
|
|
BLAKE2b-256 checksum How to use checksums |
49665e0284ba815c76a901d8459b0c2906fdbafa0a1c2e25788494634db8b6b6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 13, 2026.
Transparency log













