
This release is a pre-release and may not be stable for production use.
Disclaimer
Life, the Universe, and Everything
Show a disclaimer the first time a user visits a site.
Mostly Harmless


Got an idea? Found a bug? Let us know by opening a support ticket.
Don’t Panic
Installation
To enable this package in a buildout-based installation:
Edit your buildout.cfg and add the following to it:
[buildout]
...
eggs =
    collective.disclaimer
After updating the configuration you need to run ‘’bin/buildout’’, which will take care of updating your system.
Go to the ‘Site Setup’ page in a Plone site and click on the ‘Add-ons’ link.
Check the box next to ‘Disclaimer’ and click the ‘Activate’ button.
Usage
After installing the package, go to the ‘Disclaimer’ configlet on ‘Site Setup’ and enable the feature.
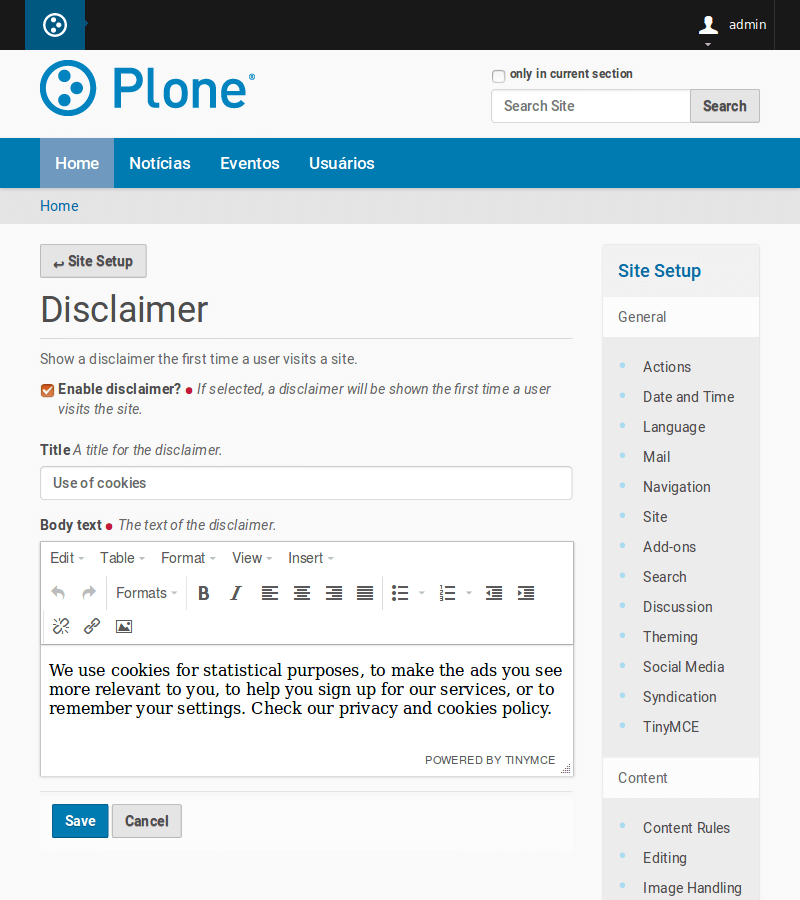
The Disclaimer control panel configlet.
Now, the first time a user visits the site the disclaimer will be shown at the bottom of the page.
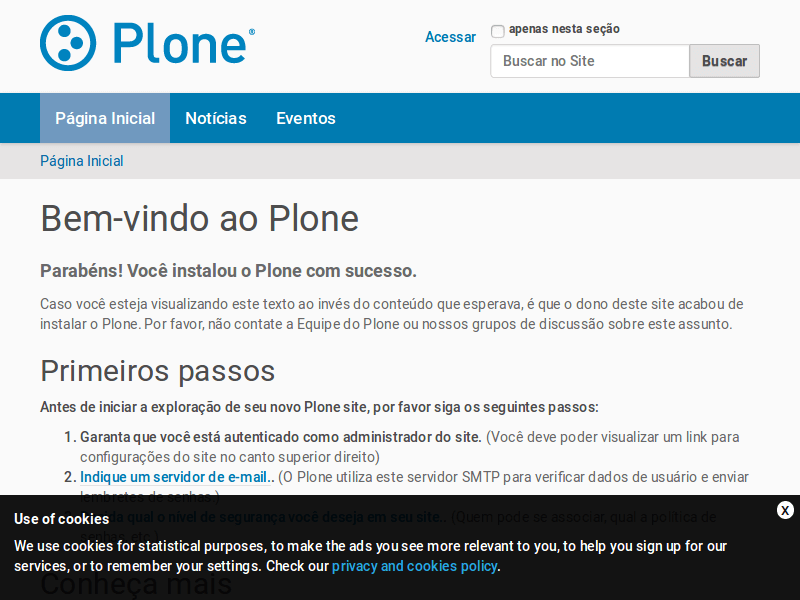
The Disclaimer viewlet at work.
Users will see the disclaimer again whenever information in the configlet is updated.
How Does It Work?
This package registers a new viewlet on plone.portalfooter viewlet manager. The viewlet is normally hidden and it will only be shown after checking the user hasn’t seen it yet. The information on last time the viewlet was updated is stored in the user’s browser local storage.
Changelog
1.0b1 (2018-12-08)
Register the controlpanel for any context. The correct registry is automatically acquired. This way, it’s possible to set different disclaimer texts in a Lineage site with lineage.registry installed. [thet]
Add a disclaimer-inner wrapper to allow easier styling, e.g. positioning the viewlet centered on the website and darkening the whole background. [thet]
Move styles and scripts into the viewlet, so that they are included when using Diazo and just using the viewlet selector to copy the viewlet into the theme. [thet]
Add an “OK” button instead of the close link. When the button is hit, the viewlet is closed and the storage key is set. Previously the storage key was immediately set even without using the “close” link. [thet]
Fix translation of default values on configlet (HT @fredvd). [hvelarde]
Fix style of hover and visited links inside disclaimer viewlet. [agnogueira]
1.0a1 (2018-05-14)
Initial release.
3 maintainers


Metadata
3 maintainers
Release files for collective.disclaimer 1.0b1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| collective.disclaimer-1.0b1.tar.gz | 90.0 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| collective.disclaimer-1.0b1-py2-none-any.whl | Python 2 | none | any | Details |
Total release size: 117.7 kB
Release files / collective.disclaimer-1.0b1.tar.gz
| Download URL | collective.disclaimer-1.0b1.tar.gz |
|---|---|
| Size | 90.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7651d05c4e08dcb68aeea9f874091212119ee09a4efec909ba0320f0184a734c
|
|
BLAKE2b-256 checksum How to use checksums |
009227500285fa921275b76480a51041162a92af9981a825a75f88c3b5b0e534
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.11.0 pkginfo/1.4.2 requests/2.18.4 setuptools/39.0.1 requests-toolbelt/0.8.0 tqdm/4.23.0 CPython/2.7.12
|
Release files / collective.disclaimer-1.0b1-py2-none-any.whl
| Download URL | collective.disclaimer-1.0b1-py2-none-any.whl |
|---|---|
| Size | 27.7 kB |
| Tags | Python 2 |
|
SHA-256 checksum How to use checksums |
6d49e22d78729524767f222a3cb29f19c02f981fab8e0f0a75fcb939f73e733d
|
|
BLAKE2b-256 checksum How to use checksums |
ba6cc6eef1735ec69bb4a6c96178a7530245af8ae5073234a5464bc4ff9fd4c5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.11.0 pkginfo/1.4.2 requests/2.18.4 setuptools/39.0.1 requests-toolbelt/0.8.0 tqdm/4.23.0 CPython/2.7.12
|
Security for collective.disclaimer 1.0b1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














