
discord-ext-prometheus


This is a extension library for discord.py that makes it easy to add prometheus metrics to your Python Discord bot.
Installation
pip install discord-ext-prometheus
Exposed Metrics
| Name | Documentation | Labels |
|---|---|---|
discord_connected |
Determines if the bot is connected to Discord | shard |
discord_latency_seconds |
Latency to Discord | shard |
discord_event_on_interaction |
Amount of interactions called by users | shard, interaction, command |
discord_event_on_command |
Amount of commands called by users | shard, command |
discord_stat_total_guilds |
Amount of guild this bot is a member of | None |
discord_stat_total_channels |
Amount of channels this bot is has access to | None |
discord_stat_total_users |
Amount of users this bot can see | None |
discord_stat_total_commands |
Amount of commands | None |
logging |
Log entries | logger, level |
Notes:
on_interactionare application interactions such as slash commands or modalson_commandare traditional message commands (usualy using the command prefix)
Grafana Dashboard
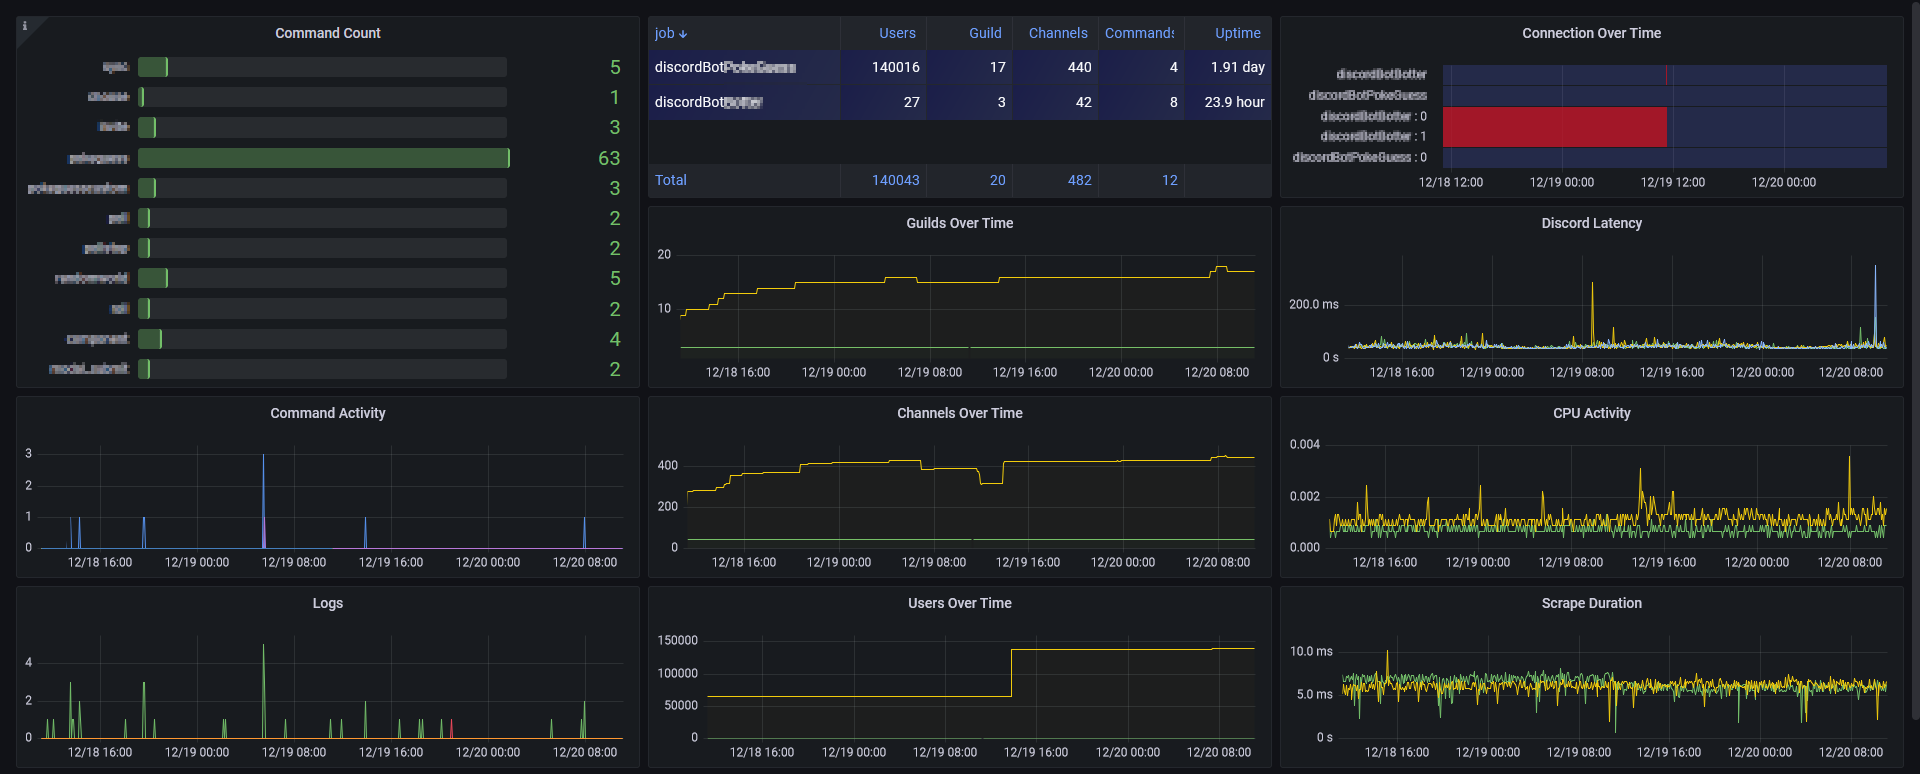
Available to import from Grafana dashboards.
How to use
Once the cog is added to your bot, the Prometheus metric endpoint can be accessed
at localhost:8000/metrics.
Sample code with the Prometheus Cog
import asyncio
from discord import Intents
from discord.ext import commands
from discord.ext.prometheus import PrometheusCog

async def main():
    bot = commands.Bot(
        command_prefix="!",
        intents=Intents.all(),
    )

    await bot.add_cog(PrometheusCog(bot))

    await bot.start("YOUR TOKEN")

asyncio.run(main())
Sample code with logging metrics
import asyncio
import logging
from discord import Intents
from discord.ext import commands
from discord.ext.prometheus import PrometheusCog, PrometheusLoggingHandler

logging.getLogger().addHandler(PrometheusLoggingHandler())

async def main():
    bot = commands.Bot(
        command_prefix="!",
        intents=Intents.all(),
    )

    await bot.add_cog(PrometheusCog(bot))

    @bot.listen()
    async def on_ready():
        logging.info(f"Logged in as {bot.user.name}#{bot.user.discriminator}")

    logging.info("Starting the bot")
    await bot.start("YOUR TOKEN")

asyncio.run(main())
Changing the Prometheus port
The default port is 8000 but can be changed while creating the cog.
await bot.add_cog(PrometheusCog(bot, port=7000))
1 maintainer

Metadata
1 maintainer
Release files for discord-ext-prometheus 0.2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| discord_ext_prometheus-0.2.1.tar.gz | 10.2 kB | Without provenance | Details for discord_ext_prometheus-0.2.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| discord_ext_prometheus-0.2.1-py3-none-any.whl | Python 3 | none | any | Details for discord_ext_prometheus-0.2.1-py3-none-any.whl |
Total release size: 16.2 kB
Release files / discord_ext_prometheus-0.2.1.tar.gz
| Download URL | discord_ext_prometheus-0.2.1.tar.gz |
|---|---|
| Size | 10.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a65c176d2205868bfa6cf0ad01633cc3846939696d59c21dcc4a27c949dec368
|
|
BLAKE2b-256 checksum How to use checksums |
a8e4553725e355e632a73dc27f251f40c8b57400c9ffb496504013f7b02f5741
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.11.11
|
Release files / discord_ext_prometheus-0.2.1-py3-none-any.whl
| Download URL | discord_ext_prometheus-0.2.1-py3-none-any.whl |
|---|---|
| Size | 6.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c2e13115c3f0fbb1a3fd3d67bff2711604742fb8742cc5e9eb80488854bf12f8
|
|
BLAKE2b-256 checksum How to use checksums |
2d0141648aaa4eb04f0be18ce5565ab7034c4dbf3b9fcc970222d24bb226a8bb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.11.11
|
Security for discord-ext-prometheus 0.2.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














