
Jolt
Build anything, once. Jolt runs your build, test and deployment tasks, caches what they produce, and shares the results with your whole team and CI.


Tasks are plain Python classes. Jolt works out what each task depends on, computes a fingerprint of everything that influences its output, and skips it if that output already exists in a cache, on your machine or on a server shared with everyone else. What has been built once is never built again, whether by you, a colleague or a CI job. In one real-world deployment, Jolt cut the CI build time from 10 hours to 10 minutes.
Highlights
- Recipes in Python
Tasks, dependencies and parameters are Python code, so there is no new language to learn and no limit to what a task can do.
- Cached by content
A task’s identity is a hash of its source, parameters, files and dependencies, so a cached result is only reused when nothing that matters has changed.
- Shared caches
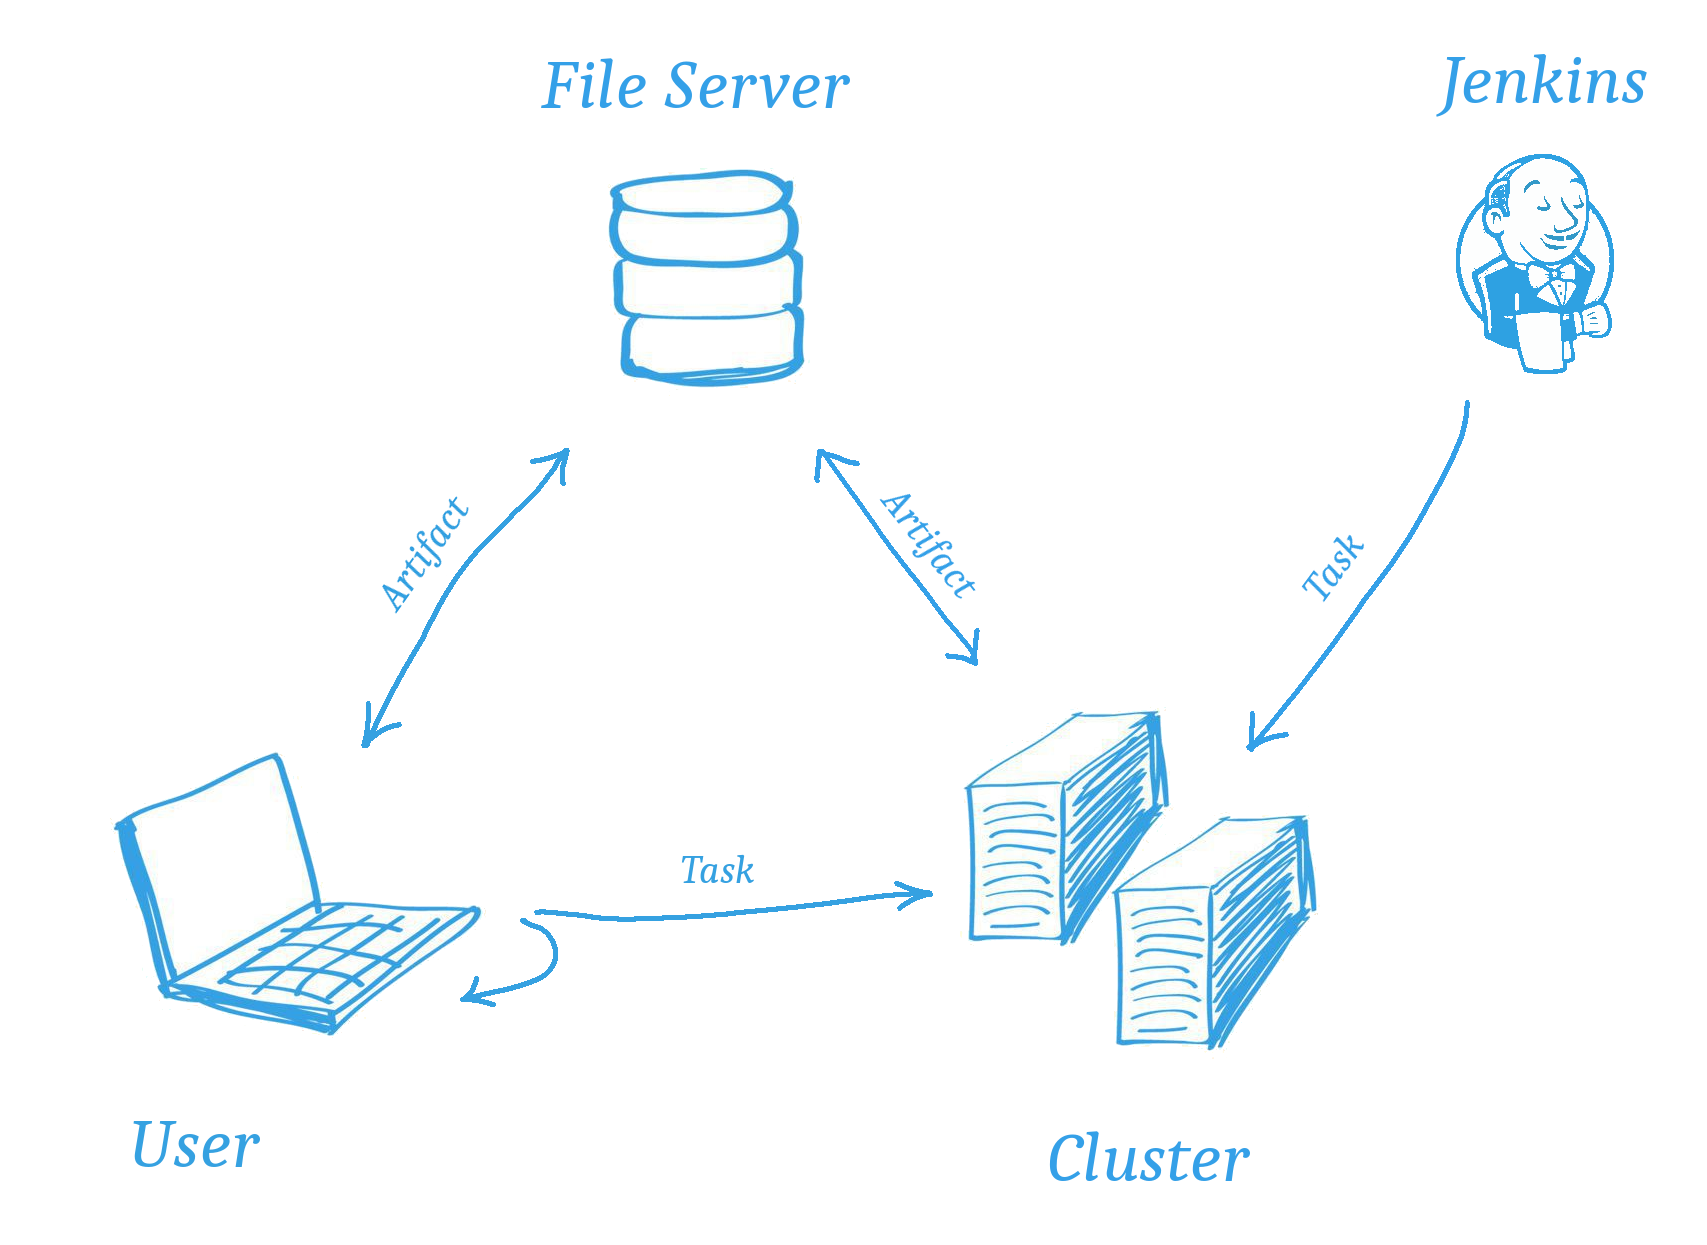
Artifacts are uploaded to a cache server, and anyone who needs the same result downloads it instead of building it.
- Distributed builds
jolt build -n sends tasks to a cluster of workers that run them in parallel. The scheduler, workers and cache run as containers on Docker or Kubernetes.
- Over 150 packages
Compilers, libraries and tools, from zlib and OpenSSL to LLVM, Qt and gRPC, built from source and kept apart for each platform and compiler.
- One command for everything
C++, Rust, Go, Node.js, Python or containers: every task is built the same way, so nobody needs to learn the others’ build tools.
- Secure by default
TLS between all services, tokens or single sign-on with an OpenID Connect provider, and builds that only their owners can stop.
- Kind to your machines
A built-in jobserver shares the CPUs between all builds on a machine and slows down before memory runs out.
Quick start
Install Jolt from PyPI:
$ pip install joltWrite a task in a file called hello.jolt:
from jolt import Task


class Hello(Task):
    """ Says hello, and publishes it. """

    def run(self, deps, tools):
        tools.write_file("hello.txt", "Hello, world!")

    def publish(self, artifact, tools):
        artifact.collect("hello.txt")
Build it:
$ jolt build hello
$ jolt build hello    # Nothing to do: the artifact is already cached
Change the message, and Jolt builds it again. Change it back, and the original artifact is used without building anything.
Examples
A C++ application built with CMake, using the fmt library from Jolt’s packages. Jolt builds fmt first, or downloads it if someone already has, and tells CMake where to find it:
from jolt.plugins import cmake
from jolt.pkgs import fmt


class App(cmake.CMake):
    """ The application, in the app directory. """

    requires = ["fmt"]
    srcdir = "app"
A web application built with a Node.js that Jolt provides, so the build doesn’t depend on what happens to be installed on the machine:
from jolt import Task
from jolt.pkgs import nodejs


class WebApp(Task):
    """ Builds the web application. """

    requires = ["nodejs"]

    def run(self, deps, tools):
        with tools.cwd("webapp"):
            tools.run("npm ci")
            tools.run("npm run build")
Parameters select variants of a task, each cached separately:
$ jolt build fmt:shared=true
$ jolt display app    # Show what app depends on
$ jolt inspect app    # Show its parameters, identity and cache status
Scaling up
Point Jolt at a cache server, and everyone shares their artifacts:
[cache]
http_uri = https://cache.example.com:8080
Add a scheduler and workers, and builds run in the cluster:
$ jolt build -n appThe build cluster guide shows how to deploy the services on Docker or Kubernetes, and how to secure them with TLS, tokens and single sign-on.
Installing
From PyPI, for Python 3.9 or later:
$ pip install joltAs a Docker image:
$ docker run robrt/joltLearn more
Documentation: the tutorial, user guides and reference
Packages: the packages that Jolt can build
Issues: bugs and ideas
Jolt is free software, licensed under the GNU General Public License v2.
1 maintainer

Metadata
1 maintainer
Release files for jolt 0.10.73
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| jolt-0.10.73.tar.gz | 17.0 MB | Without provenance | Details for jolt-0.10.73.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| jolt-0.10.73-py3-none-any.whl | Python 3 | none | any | Details for jolt-0.10.73-py3-none-any.whl |
Total release size: 34.2 MB
Release files / jolt-0.10.73.tar.gz
| Download URL | jolt-0.10.73.tar.gz |
|---|---|
| Size | 17.0 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7fe1bd3aca00396c16fa05ea0e9451f7bf0f15784f92719728b01165b464ae5a
|
|
BLAKE2b-256 checksum How to use checksums |
0037a48e3303f88a3c5bb5c36a24128ea97c397e833822a73a650652566201c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Release files / jolt-0.10.73-py3-none-any.whl
| Download URL | jolt-0.10.73-py3-none-any.whl |
|---|---|
| Size | 17.2 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c1b0a2980a4975bbcfcd088c2ca63dd389efdc16eb9a28309f2d0719da2100fa
|
|
BLAKE2b-256 checksum How to use checksums |
c2d9f63bbe279de40ae91ccd0334b4c7c20b524ba8ba988f891c9fcf5b9b628a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.12.15
|
Security for jolt 0.10.73
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














