
litsync — incremental PubMed + PMC + FDA + ClinicalTrials.gov mirror
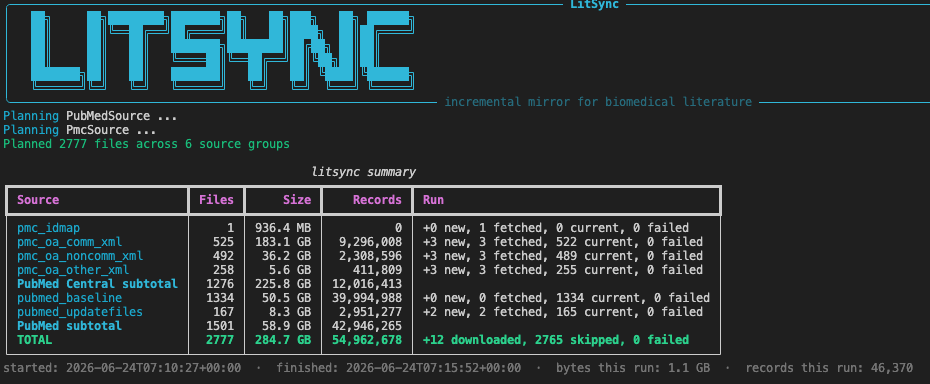
A modern, daily-runnable CLI for mirroring bulk biomedical datasets. It tracks every file in a SQLite state DB so re-runs do the minimum work: already-verified immutable files are skipped with no network request beyond the directory/manifest listing.
Documentation: https://takshan.github.io/LitSync
Install
pip install -e .
Or use the Makefile:
make install
make dev
Quick start
litsync --data-root /data/literature --email you@institute.org
Common options:
litsync --data-root /data/literature --email you@institute.org \
  --sources pubmed pmc fda clinicaltrials \
  --fda-endpoints drug/event drug/label
--sources pubmed pmc fda clinicaltrials   # which corpora (default: all four)
--fda-endpoints drug/event drug/label     # default: all openFDA endpoints
--pmc-groups oa_comm oa_noncomm oa_other
--pmc-formats xml txt                     # default: xml
--workers 4                               # concurrent downloads (keep modest; be polite)
--dry-run                                 # plan only, download nothing
--reverify                                # re-download local files (integrity audit)
--prune                                   # delete local files no longer on the server
--count-articles                          # count articles in already-downloaded files (no network)
--no-rich                                 # disable Rich progress bars / tables
On-disk layout
/data/literature/
  pubmed/baseline/                    pubmed26nXXXX.xml.gz (+ .md5 verified)
  pubmed/updatefiles/                 daily citation deltas
  pmc/oa_bulk/<group>/<fmt>/          baseline + dated incremental .tar.gz
  pmc/oa_file_list.csv                PMCID <-> PMID id map
  fda/<category>/<endpoint>/          openFDA bulk snapshot zips + extracted JSON
  clinicaltrials/ctg-public-xml.zip   ClinicalTrials.gov full XML dump
  clinicaltrials/ctg-public-xml/      extracted study XML files
  _state/state.sqlite                 file ledger (status, size, mtime, md5, etag, attempts)
  _state/logs/                        dated run logs
  _state/litsync.lock                 run lock (prevents overlapping cron runs)
Cron (daily 02:30)
30 2 * * * /path/to/venv/bin/litsync --data-root /data/literature --email you@institute.org >> /data/literature/_state/cron.log 2>&1
Extract corpus to sharded JSONL
litsync-extract --data-root /data/literature --out /data/corpus \
  --sources pubmed pmc fda clinicaltrials
Or with Make:
make extract DATA_ROOT=/data/literature CORPUS_OUT=/data/corpus
make extract-test DATA_ROOT=/data/literature
Integrity model
- PubMed: every
.xml.gzis verified against its NCBI.md5sidecar. - PMC: bulk packages have no md5 sidecar, so they are verified by
Content-Lengthand anETagis recorded for change detection. - openFDA / ClinicalTrials.gov: these sources publish full snapshots. The downloader
detects changed snapshots via
ETag/Last-Modified/Content-Lengthand only re-downloads when the snapshot changes. When a snapshot changes it is extracted again next to the zip file. - Downloads are atomic (
.part-> rename) and resumable via HTTP Range. - Exit code is non-zero if any file failed, so cron/monitoring can alert.
Notes on sources
- openFDA bulk data is zipped JSON. The manifest is fetched from
https://api.fda.gov/download.json. Each endpoint partition becomes one downloaded/extracted unit. - ClinicalTrials.gov bulk data is the full public XML dump from
https://clinicaltrials.gov/api/legacy/public-xml?format=zip. One XML file per study. - Both sources are snapshots, not daily deltas. Daily runs are still cheap because unchanged snapshots are skipped; changed snapshots are replaced in full.
1 maintainer

Metadata
1 maintainer
Release files for litsync 0.0.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| litsync-0.0.5.tar.gz | 29.1 kB | With provenance | Details for litsync-0.0.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| litsync-0.0.5-py3-none-any.whl | Python 3 | none | any | Details for litsync-0.0.5-py3-none-any.whl |
Total release size: 62.4 kB
Release files / litsync-0.0.5.tar.gz
| Download URL | litsync-0.0.5.tar.gz |
|---|---|
| Size | 29.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
994a9c98503fef8846d6a7998b8621e9a54afea844c352a9c2a1ca6f0571d38f
|
|
BLAKE2b-256 checksum How to use checksums |
4109d6fe143b6f38a07c212779e1f973de0296234c5473025be3a9cc4e255330
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 29, 2026.
Transparency logRelease files / litsync-0.0.5-py3-none-any.whl
| Download URL | litsync-0.0.5-py3-none-any.whl |
|---|---|
| Size | 33.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
22a16063621e09f2425d00957afce2bb919c84954b1d2375319060a3a47ef41d
|
|
BLAKE2b-256 checksum How to use checksums |
f81df27965cc0a6bc492148442f086c37b9ed64f320aa8ad20944e7ce7d2687c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 29, 2026.
Transparency logSecurity for litsync 0.0.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for litsync-0.0.5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 29, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














