
mcp-serverman: A MCP Server Configuration Manager




A command-line tool to manage Claude MCP servers configuration with version control and profiling. Now also has a companion mcp server to let llms config for you.
[!IMPORTANT]
I always recommend making a manual backup of the mcp configuration before making any changes. Although I tried to cover some error handling in the code, it is definitely not inclusive.
:floppy_disk:Installation
pip install mcp-serverman
or from GitHub for the latest debug version:
pip install git+https://github.com/benhaotang/mcp-serverman.git
Should be available on Windows, Linux(tested) and MacOS. If the path for a certain platform is wrong, open an issue.
:computer: Cli usage
After installation, you can use the mcp-serverman command directly in terminal:
# Display help message
mcp-serverman
# Initialize Client configuration(one time and must be done before using other commands, since 0.1.9)
mcp-serverman client init
# List servers
mcp-serverman list
mcp-serverman list --enabled
# Enable/disable/remove server/server version
mcp-serverman enable <server_name>
mcp-serverman disable <server_name>
mcp-serverman remove <server_name>
# Version control
mcp-serverman save <server_name> --comment <comment>
mcp-serverman change <server_name> --version <version>
# Preset/Profile management
mcp-serverman preset save <preset_name>
mcp-serverman preset load <preset_name>
mcp-serverman preset delete <preset_name>
# Multiple client support(since 0.1.9)
mcp-serverman client list
mcp-serverman client add <short_name> --name "Display Name" --path "/path/to/config.json" --key "mcpServers" [--default]
mcp-serverman client remove <short_name>
mcp-serverman client modify <short_name> --default
mcp-serverman client copy --from <short_name> --to <short_name> --merge
# Register companion mcp server to let Claude/LLM manage for you(since 0.2.1)
mcp-serverman companion [--client <client>]
For detailed usage instructions, see the manual.
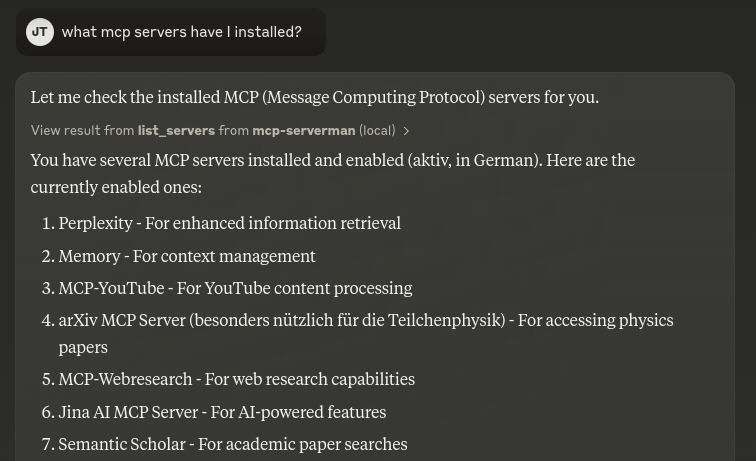
:robot: Install as a mcp server
# Install companion (since 0.2.1)
mcp-serverman companion [--client <client>]
Example:
- What mcp servers do I have?
- Disable xxx, xxx server for me.
:wrench:Development
To install the package in development mode, clone the repository and run:
pip install -e .
:checkered_flag:Roadmap
- Add support for other MCP-Clients, e.g. Cline and MCP-Bridge (since 0.1.9)
- Update the code to be more modular and easier to maintain (since v0.2.0)
- Added our own mcp-server to let Claude/LLM manage for you (since 0.2.1)
- Better error handling tests
Integration with other MCP server install tools, e.g. Smithery, or with predefined installation templates (should iron out safety issues first)We have so many mcp marketplaces now, just use mcp-installer package and instruct the model to install it for you.Maybe a Web UI via Flask?
License
MIT License (LICENSE)
1 maintainer

Metadata
1 maintainer
Release files for mcp-serverman 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| mcp_serverman-0.2.2.tar.gz | 17.5 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| mcp_serverman-0.2.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 36.0 kB
Release files / mcp_serverman-0.2.2.tar.gz
| Download URL | mcp_serverman-0.2.2.tar.gz |
|---|---|
| Size | 17.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
24965fabb4d94ec3247f1d39eefeb4f24b7ed371be6f9439670f73f4822ddd25
|
|
BLAKE2b-256 checksum How to use checksums |
ae363dfa5ef236a98386e5bcfd414be590215df5c3af26f5d69fd869542a9f28
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 24, 2025.
Transparency logRelease files / mcp_serverman-0.2.2-py3-none-any.whl
| Download URL | mcp_serverman-0.2.2-py3-none-any.whl |
|---|---|
| Size | 18.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
8ee14a1e4fb28a0abf19298d97a92c0863598a6fd4afcc3937dea4aecf6f0599
|
|
BLAKE2b-256 checksum How to use checksums |
474b0a9339846b8bca41965c65977d932f67a82cf0de33dba264ad5c3a70326e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 24, 2025.
Transparency logSecurity for mcp-serverman 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for mcp_serverman-0.2.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Feb 24, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














