
Nipoppy




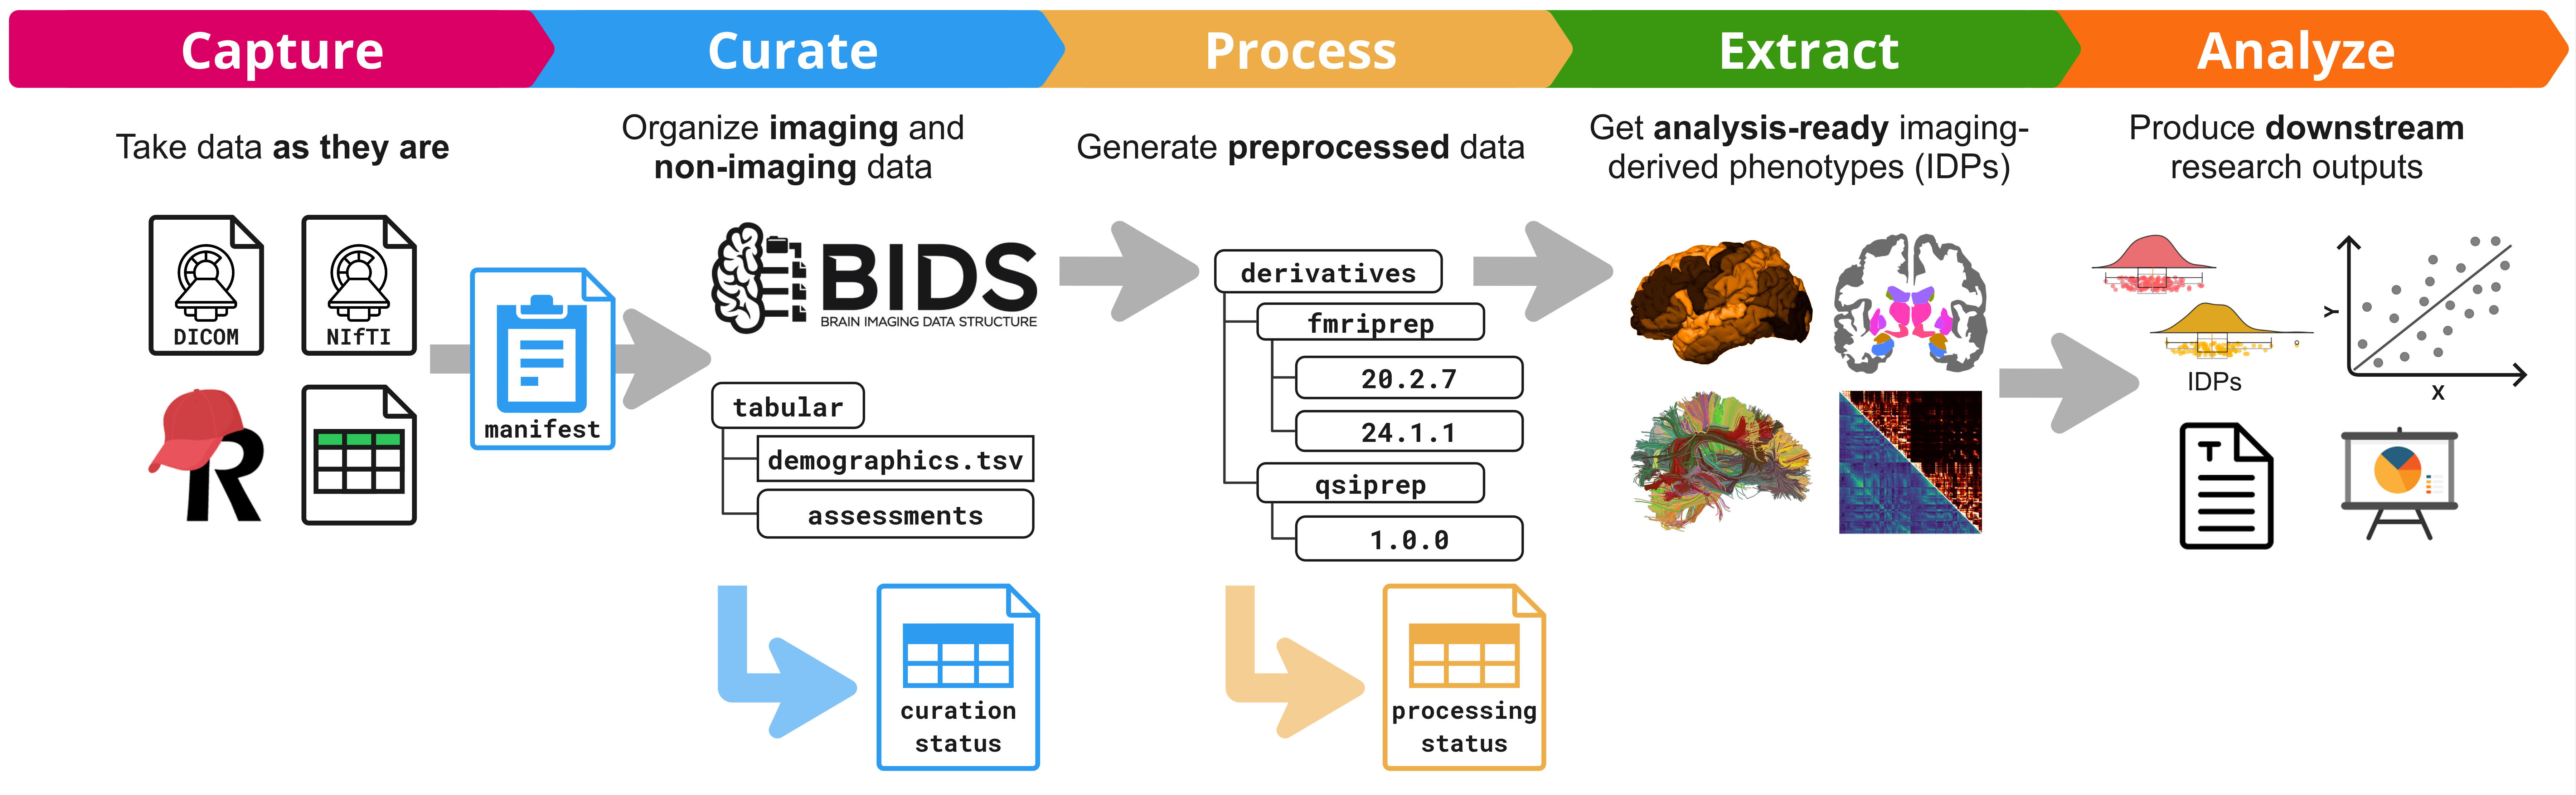
Nipoppy is a lightweight framework for standardized organization and processing of neuroimaging-clinical datasets. Its goal is to help users adopt the FAIR principles and improve the reproducibility of studies.
The framework includes three components:
-
A protocol for data organization, curation and processing, with steps that include the following:
- Organization of raw data, including conversion of raw DICOMs (or NIfTIs) to BIDS
- Processing of imaging data with existing or custom pipelines
- Tracking of data availability and processing status
- Extraction of imaging-derived phenotypes (IDPs) for downstream statistical modelling and analysis
-
A specification for dataset organization that extends the Brain Imaging Data Structure (BIDS) standard by providing additional guidelines for tabular (e.g., phenotypic) data and imaging derivatives.
-
A command-line interface and Python package that provide user-friendly tools for applying the framework. The tools build upon existing technologies such as the Apptainer container platform and the Boutiques descriptor framework. Several existing containerized pipelines are supported out-of-the-box, and new pipelines can be added easily by the user.
- We have also developed a web dashboard for interactive visualizations of imaging and phenotypic data availability.

3 maintainers


Metadata
3 maintainers
Release files for nipoppy 0.3.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| nipoppy-0.3.3.tar.gz | 1.5 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| nipoppy-0.3.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.6 MB
Release files / nipoppy-0.3.3.tar.gz
| Download URL | nipoppy-0.3.3.tar.gz |
|---|---|
| Size | 1.5 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d1b778cae1d04fa337b0b66e2156be100a5e06892c2647146e6576da480dc4f2
|
|
BLAKE2b-256 checksum How to use checksums |
e3371927985ec06ff21d55f2503e27216b6e8812a8674e37eca06259509c3def
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 31, 2025.
Transparency logRelease files / nipoppy-0.3.3-py3-none-any.whl
| Download URL | nipoppy-0.3.3-py3-none-any.whl |
|---|---|
| Size | 133.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6a48c74a457dd6ad11301fc201a5a26ea1be0e76219e8deb18a03dc215a45099
|
|
BLAKE2b-256 checksum How to use checksums |
fdf45da0c9bc9a48688c4b9229952e49b654972456caa0b1a9606c7171a71f9c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.8
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 31, 2025.
Transparency logSecurity for nipoppy 0.3.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for nipoppy-0.3.3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jan 31, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














