


开发者信息
- nikiss,个人QQ 1299577815,插件反馈QQ群 226462236,插件有问题到群里反馈响应更快哦
-
简介
我和老婆经常做菜忘记以前某个菜咋做,于是就整了这个插件记录一下我们的菜谱,顺便发到商店,嘿嘿~
安装
使用nb-cli安装
nb plugin install nonebot_plugin_nya_cook_menu
或者
直接把插件clone下来放进去plugins文件夹,但要记得装Pillow库
配置
在bot对应的.env文件修改
# 使用用户qq号,必填
nya_cook_user_list = [1234, 5678]
# 机器人的QQ号列表,选填
# 如果有多个bot连接,会按照填写的list,左边的机器人QQ优先级最高 1234 > 5678 > 6666,会自动切换
# 如果不填该配置则由第一个连上的bot响应
nya_cook_bot_qqnum_list = [1234,5678,6666]
插件命令
| 指令 | 说明 |
|---|---|
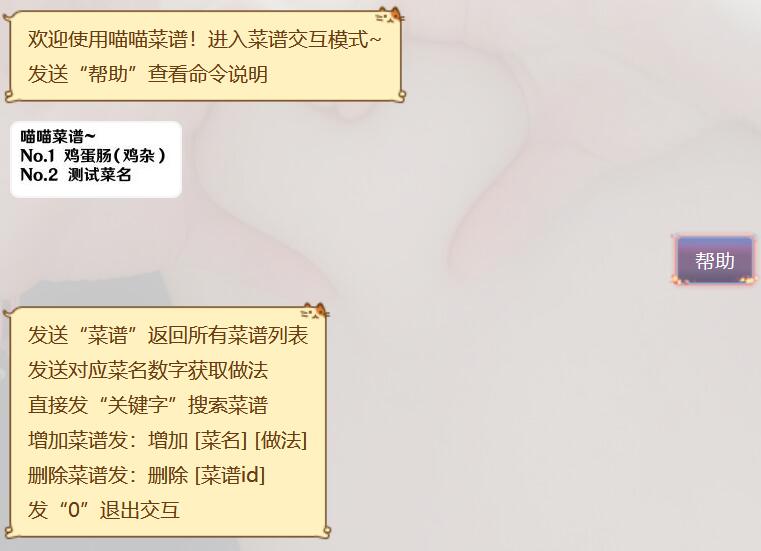
| 菜谱 | 你发一下就知道啦 |
更新日志
2024/6/25 [v0.1.8]
- 兼容新版本的nb
2024/6/25 [v0.1.7]
- 更新插件元数据
2023/1/24 [v0.1.5]
- 修复多bot处理bug
2023/1/16 [v0.1.3]
- 最低python版本兼容至3.8
- 默认字体大小从16改到18
2023/1/16 [v0.1.1]
- 发布插件
1 maintainer

Metadata
1 maintainer
Release files for nonebot_plugin_nya_cook_menu 0.1.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| nonebot_plugin_nya_cook_menu-0.1.8.tar.gz | 4.6 MB | Without provenance | Details for nonebot_plugin_nya_cook_menu-0.1.8.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| nonebot_plugin_nya_cook_menu-0.1.8-py3-none-any.whl | Python 3 | none | any | Details for nonebot_plugin_nya_cook_menu-0.1.8-py3-none-any.whl |
Total release size: 9.2 MB
Security for nonebot_plugin_nya_cook_menu 0.1.8
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














