
User roles



This module was written to extend the standard functionality regarding users and groups management. It helps creating well-defined user roles and associating them to users.
It can become very hard to maintain a large number of user profiles over time, juggling with many technical groups. For this purpose, this module will help you to:
define functional roles by aggregating low-level groups,
set user accounts with the predefined roles (roles are cumulative),
update groups of all relevant user accounts (all at once),
ensure that user accounts will have the groups defined in their roles (nothing more, nothing less). In other words, you can not set groups manually on a user as long as there is roles configured on it,
activate/deactivate roles depending on the date (useful to plan holidays, etc)
get a quick overview of roles and the related user accounts.
That way you make clear the different responsabilities within a company, and are able to add and update user accounts in a scalable and reliable way.
Table of contents
Configuration
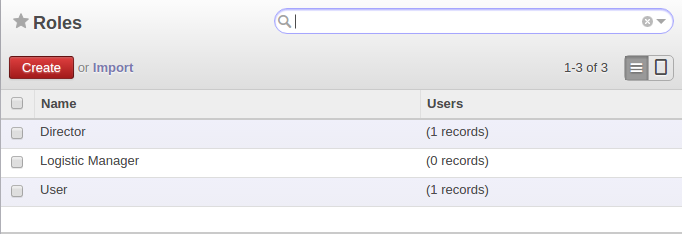
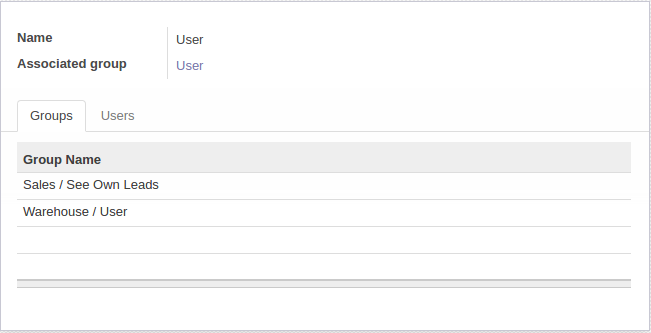
To configure this module, you need to go to Configuration / Users / Roles, and create a new role. From there, you can add groups to compose your role, and then associate users to it.
You can also define default roles for a new user by editing the user called “Default User”.
Roles:
Add groups:
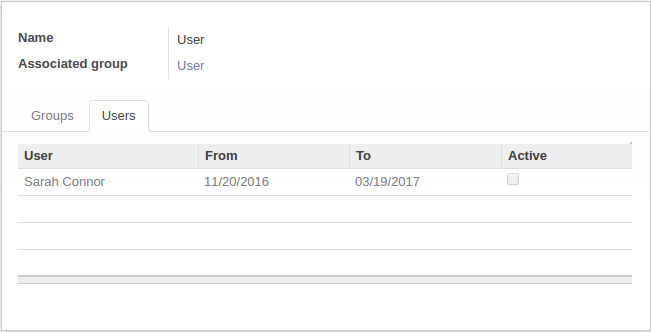
Add users (with dates or not):
Usage
- [ This file must be present and contains the usage instructions
for end-users. As all other rst files included in the README, it MUST NOT contain reStructuredText sections only body text (paragraphs, lists, tables, etc). Should you need a more elaborate structure to explain the addon, please create a Sphinx documentation (which may include this file as a “quick start” section). ]
To use this module, you need to:
Go to Configuration / Users / Users choose user and set Roles:

Bug Tracker
Bugs are tracked on GitHub Issues. In case of trouble, please check there if your issue has already been reported. If you spotted it first, help us smashing it by providing a detailed and welcomed feedback.
Do not contact contributors directly about support or help with technical issues.
Credits
Contributors
Sébastien Alix <sebastien.alix@osiell.com>
Duc, Dao Dong <duc.dd@komit-consulting.com> (https://komit-consulting.com)
Jean-Charles Drubay <jc@komit-consulting.com> (https://komit-consulting.com)
Pierrick Brun <pierrick.brun@akretion.com>
Kevin Khao <kevin.khao@akretion.com>
Andrius Laukavičius <andrius@focusate.eu> (http://focusate.eu)
Do not contact contributors directly about support or help with technical issues.
Other credits
Images
Oxygen Team: Icon (LGPL)
Maintainers
This module is maintained by the OCA.
OCA, or the Odoo Community Association, is a nonprofit organization whose mission is to support the collaborative development of Odoo features and promote its widespread use.
Current maintainers:


This module is part of the OCA/server-backend project on GitHub.
You are welcome to contribute. To learn how please visit https://odoo-community.org/page/Contribute.
1 maintainer

Metadata
1 maintainer
Release files for odoo12-addon-base-user-role 12.0.2.1.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| odoo12_addon_base_user_role-12.0.2.1.3-py3-none-any.whl | Python 3 | none | any | Details for odoo12_addon_base_user_role-12.0.2.1.3-py3-none-any.whl |
Release files / odoo12_addon_base_user_role-12.0.2.1.3-py3-none-any.whl
| Download URL | odoo12_addon_base_user_role-12.0.2.1.3-py3-none-any.whl |
|---|---|
| Size | 215.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
4000836b0e6ab67cae099a2b1f0ee78e6034e6b9cf63147d326a71c6223649f5
|
|
BLAKE2b-256 checksum How to use checksums |
b50802803d4a36aa3f6225ae6871ad31c1d185b3b6706ed8e580ff567166765f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.1 CPython/3.8.5
|
Security for odoo12-addon-base-user-role 12.0.2.1.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














