
PyOTP - The Python One-Time Password Library
PyOTP is a Python library for generating and verifying one-time passwords. It can be used to implement two-factor (2FA) or multi-factor (MFA) authentication methods in web applications and in other systems that require users to log in.
Open MFA standards are defined in RFC 4226 (HOTP: An HMAC-Based One-Time Password Algorithm) and in RFC 6238 (TOTP: Time-Based One-Time Password Algorithm). PyOTP implements server-side support for both of these standards. Client-side support can be enabled by sending authentication codes to users over SMS or email (HOTP) or, for TOTP, by instructing users to use Google Authenticator, Authy, or another compatible app. Users can set up auth tokens in their apps easily by using their phone camera to scan otpauth:// QR codes provided by PyOTP.
Implementers should read and follow the HOTP security requirements and TOTP security considerations sections of the relevant RFCs. At minimum, application implementers should follow this checklist:
Ensure transport confidentiality by using HTTPS
Ensure HOTP/TOTP secret confidentiality by storing secrets in a controlled access database
Deny replay attacks by persisting the last accepted OTP counter for each credential and rejecting reused counters. For TOTP, use verify_and_get_timecode() as described in Preventing replay attacks below.
Throttle (rate limit) brute-force attacks against your application’s login functionality (see RFC 4226, section 7.3)
When implementing a “greenfield” application, consider supporting FIDO U2F/WebAuthn in addition to or instead of HOTP/TOTP. U2F uses asymmetric cryptography to avoid using a shared secret design, which strengthens your MFA solution against server-side attacks. Hardware U2F also sequesters the client secret in a dedicated single-purpose device, which strengthens your clients against client-side attacks. And by automating scoping of credentials to relying party IDs (application origin/domain names), U2F adds protection against phishing attacks. One implementation of FIDO U2F/WebAuthn is PyOTP’s sister project, PyWARP.
We also recommend that implementers read the OWASP Authentication Cheat Sheet and NIST SP 800-63-3: Digital Authentication Guideline for a high level overview of authentication best practices.
Quick overview of using One Time Passwords on your phone
OTPs involve a shared secret, stored both on the phone and the server
OTPs can be generated on a phone without internet connectivity
OTPs should always be used as a second factor of authentication (if your phone is lost, you account is still secured with a password)
Google Authenticator and other OTP client apps allow you to store multiple OTP secrets and provision those using a QR Code
Installation
pip install pyotp
Usage
Time-based OTPs
import pyotp
import time

totp = pyotp.TOTP('base32secret3232')
totp.now() # => '492039'

# OTP verified for current time
totp.verify('492039') # => True
time.sleep(30)
totp.verify('492039') # => False
Preventing replay attacks
TOTP.verify() and TOTP.verify_and_get_timecode() are stateless: they can accept the same OTP repeatedly while it remains valid. To prevent reuse, call verify_and_get_timecode() and persist its returned timecode for each credential in a database shared by all application workers. The timecode identifies the matching TOTP interval; it is not the wall-clock timestamp when verification occurred. Reject a timecode that is less than or equal to the last accepted timecode.
verify_and_get_timecode() raises pyotp.OTPVerificationError (a subclass of pyotp.PyOTPError) if the OTP does not match within the allowed window. Successful verification always returns an integer timecode.
The check and update must be atomic, so two concurrent requests cannot both accept the same timecode. For example, the following function uses a sqlite3.Connection named db and a totp_credentials table with one existing row per credential, an id primary key, and a nullable integer last_timecode column. Initialize last_timecode to NULL for a new credential. totp and credential_id must refer to the same credential.
import pyotp

def verify_totp_once(db, credential_id, totp, otp):
    try:
        matched_timecode = totp.verify_and_get_timecode(otp)
    except pyotp.OTPVerificationError:
        return False

    with db:
        updated = db.execute(
            "UPDATE totp_credentials SET last_timecode = ? "
            "WHERE id = ? AND (last_timecode IS NULL OR last_timecode < ?)",
            (matched_timecode, credential_id, matched_timecode),
        )
    return updated.rowcount == 1
Grant authentication only when this function returns True, after the database transaction has committed. If you enable valid_window, persist the returned matching timecode, which may differ from the server’s current timecode.
Counter-based OTPs
import pyotp

hotp = pyotp.HOTP('base32secret3232')
hotp.at(0) # => '260182'
hotp.at(1) # => '055283'
hotp.at(1401) # => '316439'

# OTP verified with a counter
hotp.verify('316439', 1401) # => True
hotp.verify('316439', 1402) # => False
Generating a Secret Key
A helper function is provided to generate a 32-character base32 secret, compatible with Google Authenticator and other OTP apps:
pyotp.random_base32()Some applications want the secret key to be formatted as a hex-encoded string:
pyotp.random_hex() # returns a 40-character hex-encoded secretGoogle Authenticator Compatible
PyOTP works with the Google Authenticator iPhone and Android app, as well as other OTP apps like Authy. PyOTP includes the ability to generate provisioning URIs for use with the QR Code scanner built into these MFA client apps:
pyotp.totp.TOTP('JBSWY3DPEHPK3PXP').provisioning_uri(name='alice@google.com', issuer_name='Secure App')

>>> 'otpauth://totp/Secure%20App:alice%40google.com?secret=JBSWY3DPEHPK3PXP&issuer=Secure%20App'

pyotp.hotp.HOTP('JBSWY3DPEHPK3PXP').provisioning_uri(name="alice@google.com", issuer_name="Secure App", initial_count=0)

>>> 'otpauth://hotp/Secure%20App:alice%40google.com?secret=JBSWY3DPEHPK3PXP&issuer=Secure%20App&counter=0'
This URL can then be rendered as a QR Code (for example, using https://github.com/soldair/node-qrcode) which can then be scanned and added to the users list of OTP credentials.
Parsing these URLs is also supported:
pyotp.parse_uri('otpauth://totp/Secure%20App:alice%40google.com?secret=JBSWY3DPEHPK3PXP&issuer=Secure%20App')

>>> <pyotp.totp.TOTP object at 0xFFFFFFFF>

pyotp.parse_uri('otpauth://hotp/Secure%20App:alice%40google.com?secret=JBSWY3DPEHPK3PXP&issuer=Secure%20App&counter=0'

>>> <pyotp.totp.HOTP object at 0xFFFFFFFF>
Working example
Scan the following barcode with your phone’s OTP app (e.g. Google Authenticator):
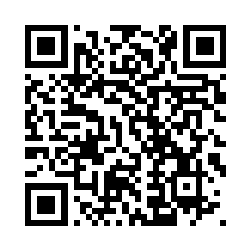
Now run the following and compare the output:
import pyotp
totp = pyotp.TOTP("JBSWY3DPEHPK3PXP")
print("Current OTP:", totp.now())
Third-party contributions
The following third-party contributions are not described by a standard, not officially supported, and provided for reference only:
pyotp.contrib.Steam(): An implementation of Steam TOTP. Uses the same API as pyotp.TOTP().
Links
ROTP - Original Ruby OTP library by Mark Percival
For new applications:
Versioning
This package follows the Semantic Versioning 2.0.0 standard. To control changes, it is recommended that application developers pin the package version and manage it using pip-tools or similar. For library developers, pinning the major version is recommended.


Release files for PyOTP 2.11.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| pyotp-2.11.2.tar.gz | 25.5 kB | With provenance | Details for pyotp-2.11.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| pyotp-2.11.2-py3-none-any.whl | Python 3 | none | any | Details for pyotp-2.11.2-py3-none-any.whl |
Total release size: 41.6 kB
Release files / pyotp-2.11.2.tar.gz
| Download URL | pyotp-2.11.2.tar.gz |
|---|---|
| Size | 25.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
651926820da4adccbe9801c77bdc14558552485b1a957d3e1e842d587597cbb0
|
|
BLAKE2b-256 checksum How to use checksums |
5d01beed98d5c77fdb2b44dfa82f8ee9dadb120ce7466c0d131ce8a3eafdf62e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logRelease files / pyotp-2.11.2-py3-none-any.whl
| Download URL | pyotp-2.11.2-py3-none-any.whl |
|---|---|
| Size | 16.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d693ddda5c2fd2c368a034ec1ad2fbbe0d3f59d9a662ab00f41ae839a0d00474
|
|
BLAKE2b-256 checksum How to use checksums |
221bec5b1ac0c4aea3702a20e9c7ee1e21926735cc87159e252616e31e0a87dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logSecurity for PyOTP 2.11.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for pyotp-2.11.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














