
ShodanX⚡ – A terminal-powered recon and OSINT tool built on top of the Shodan Services.

Features | Installation | Usage | Post Installation Setup


Features🔧:
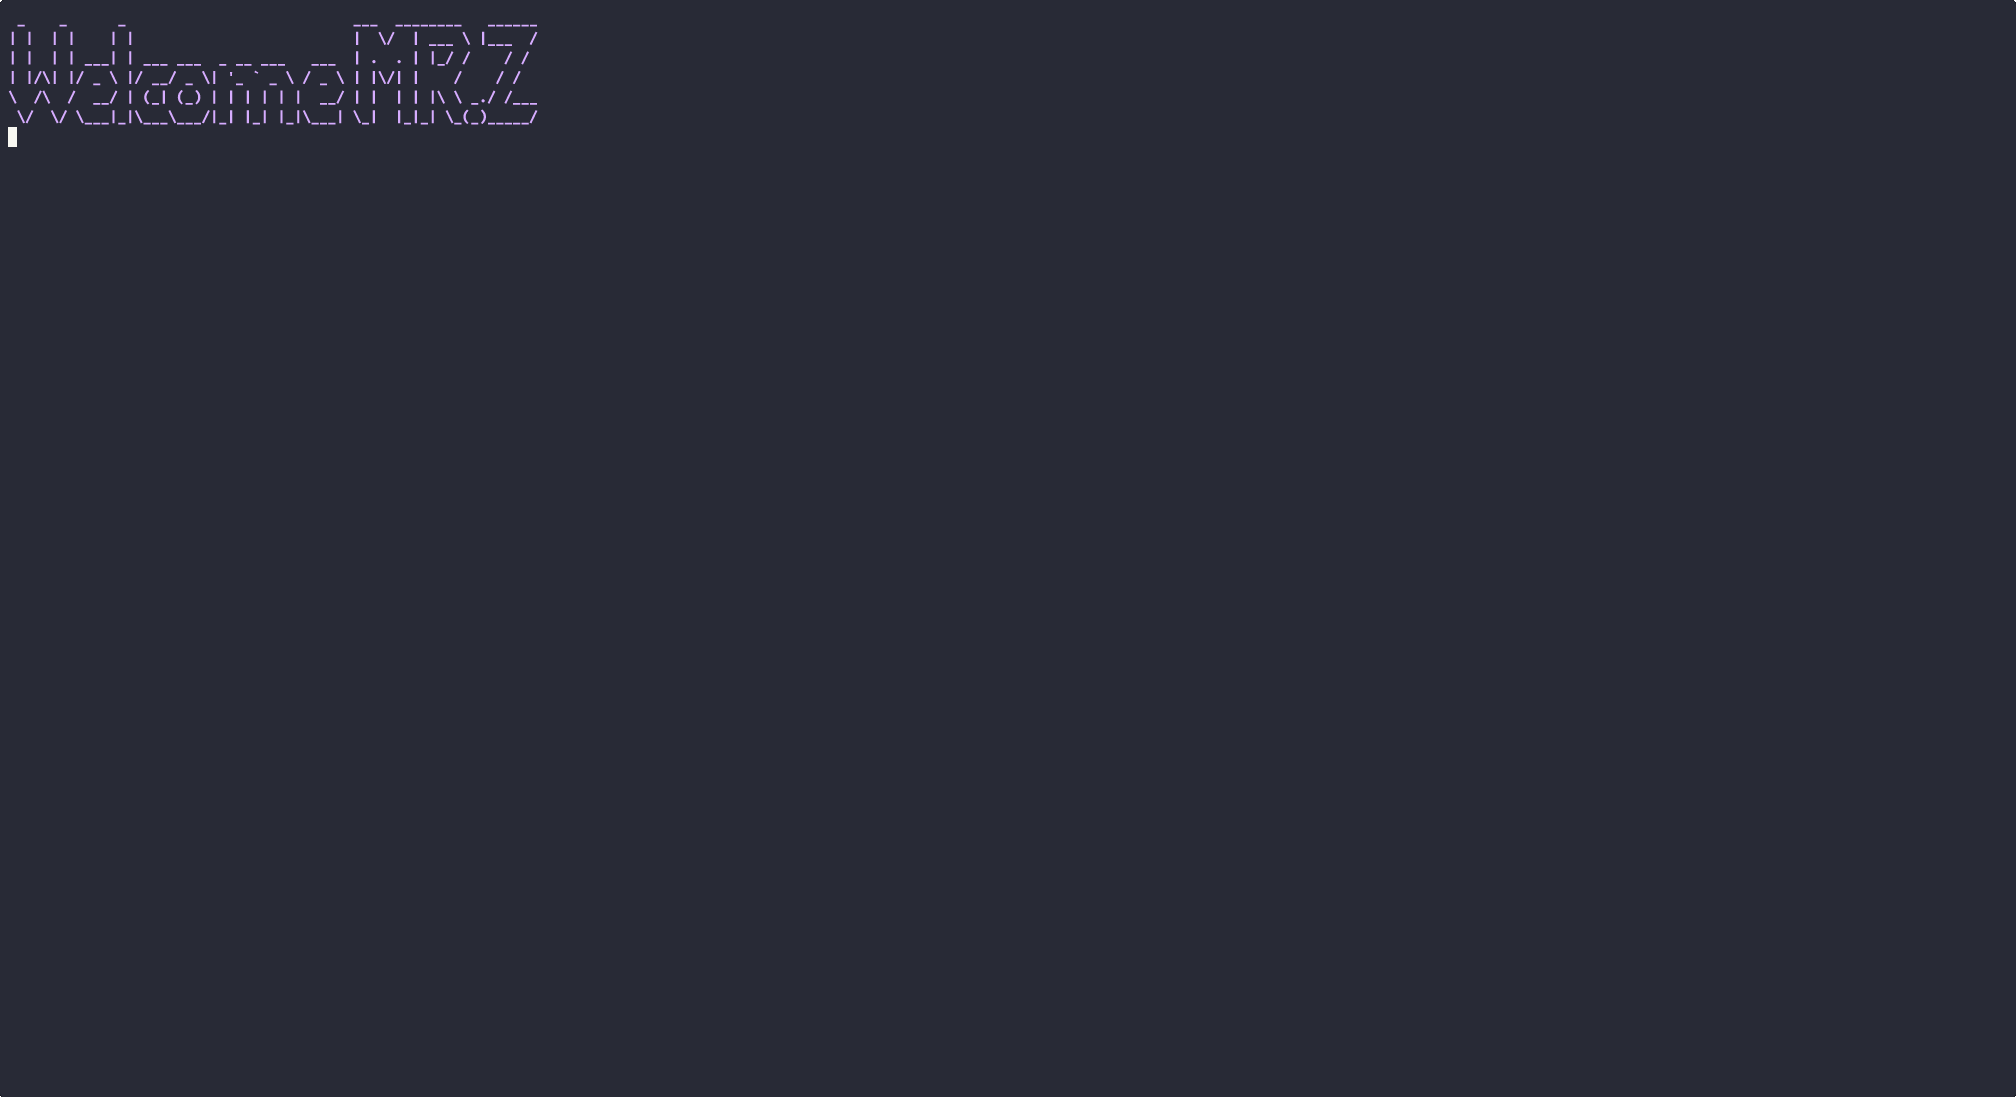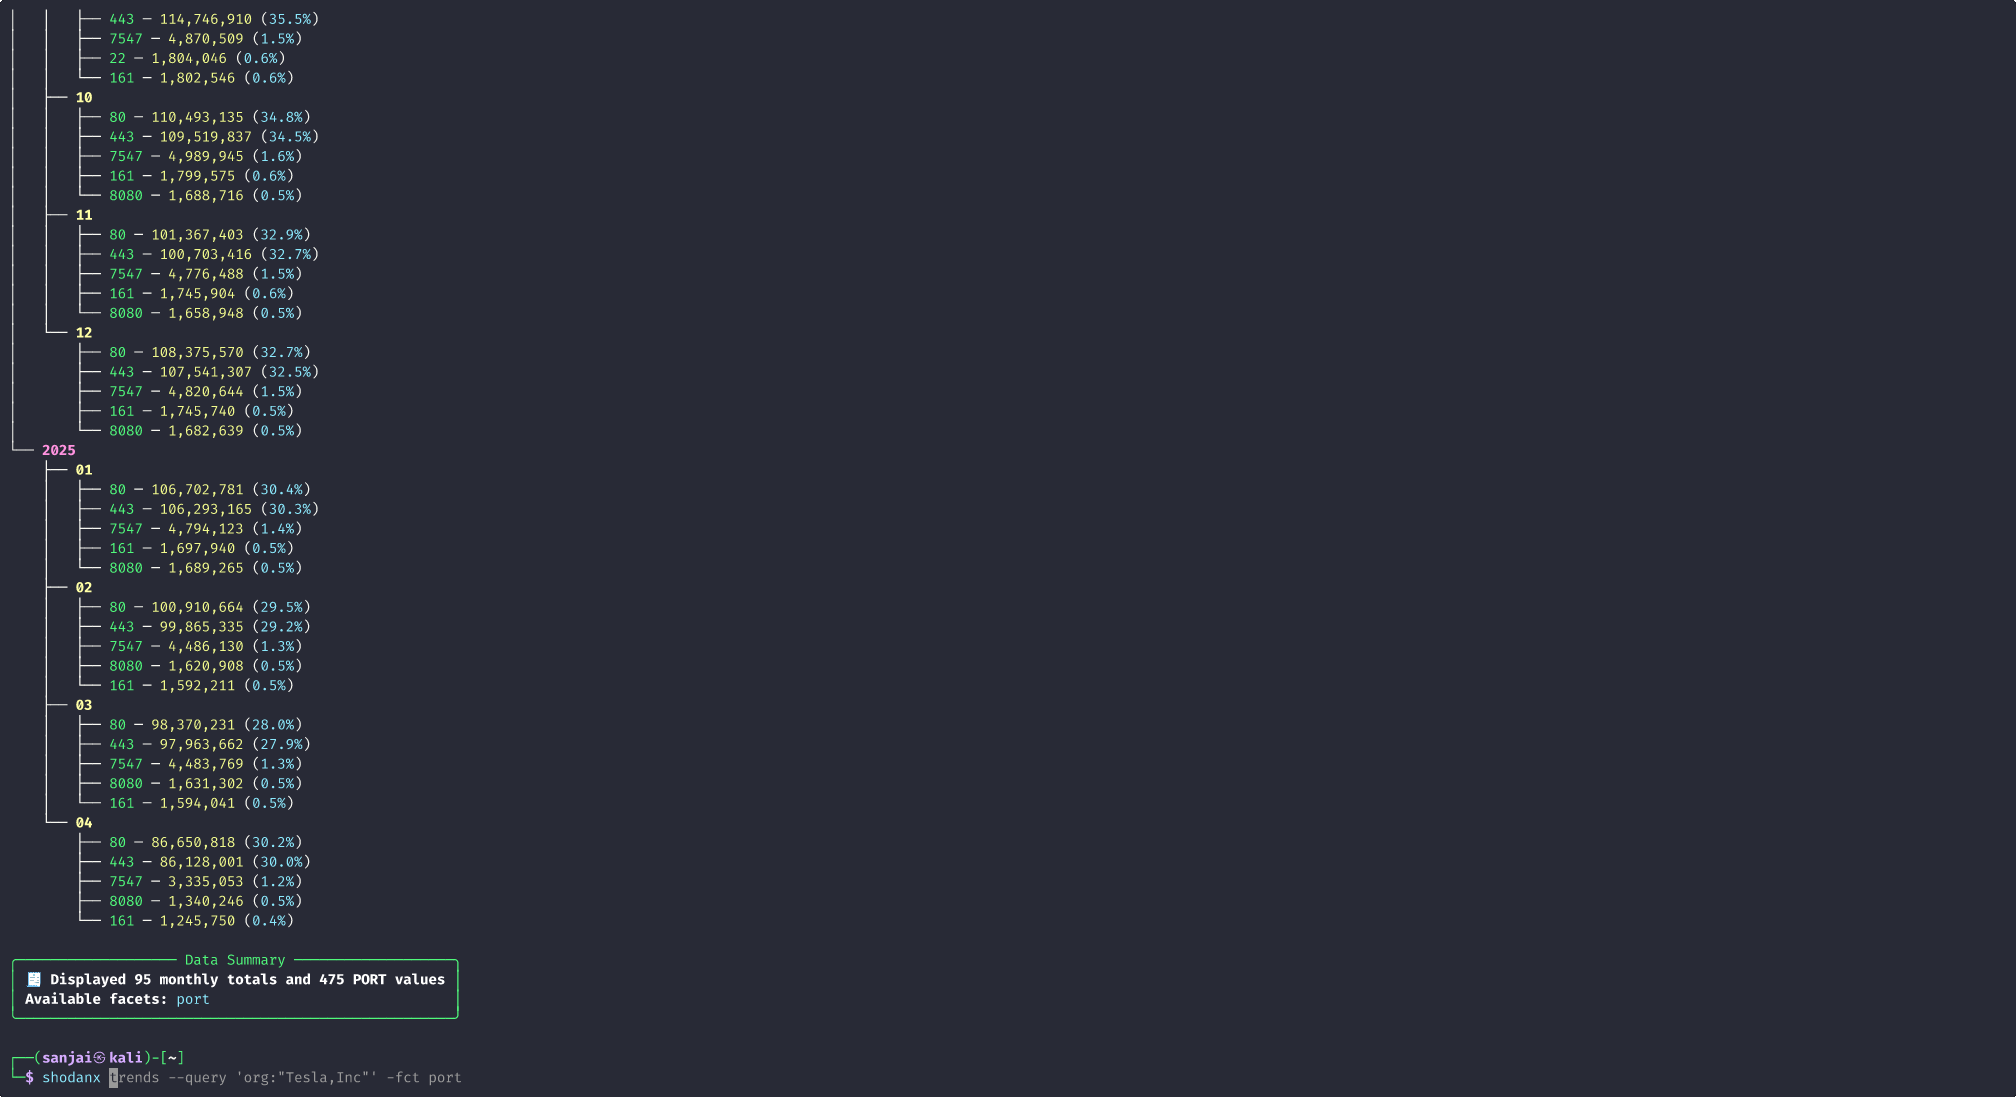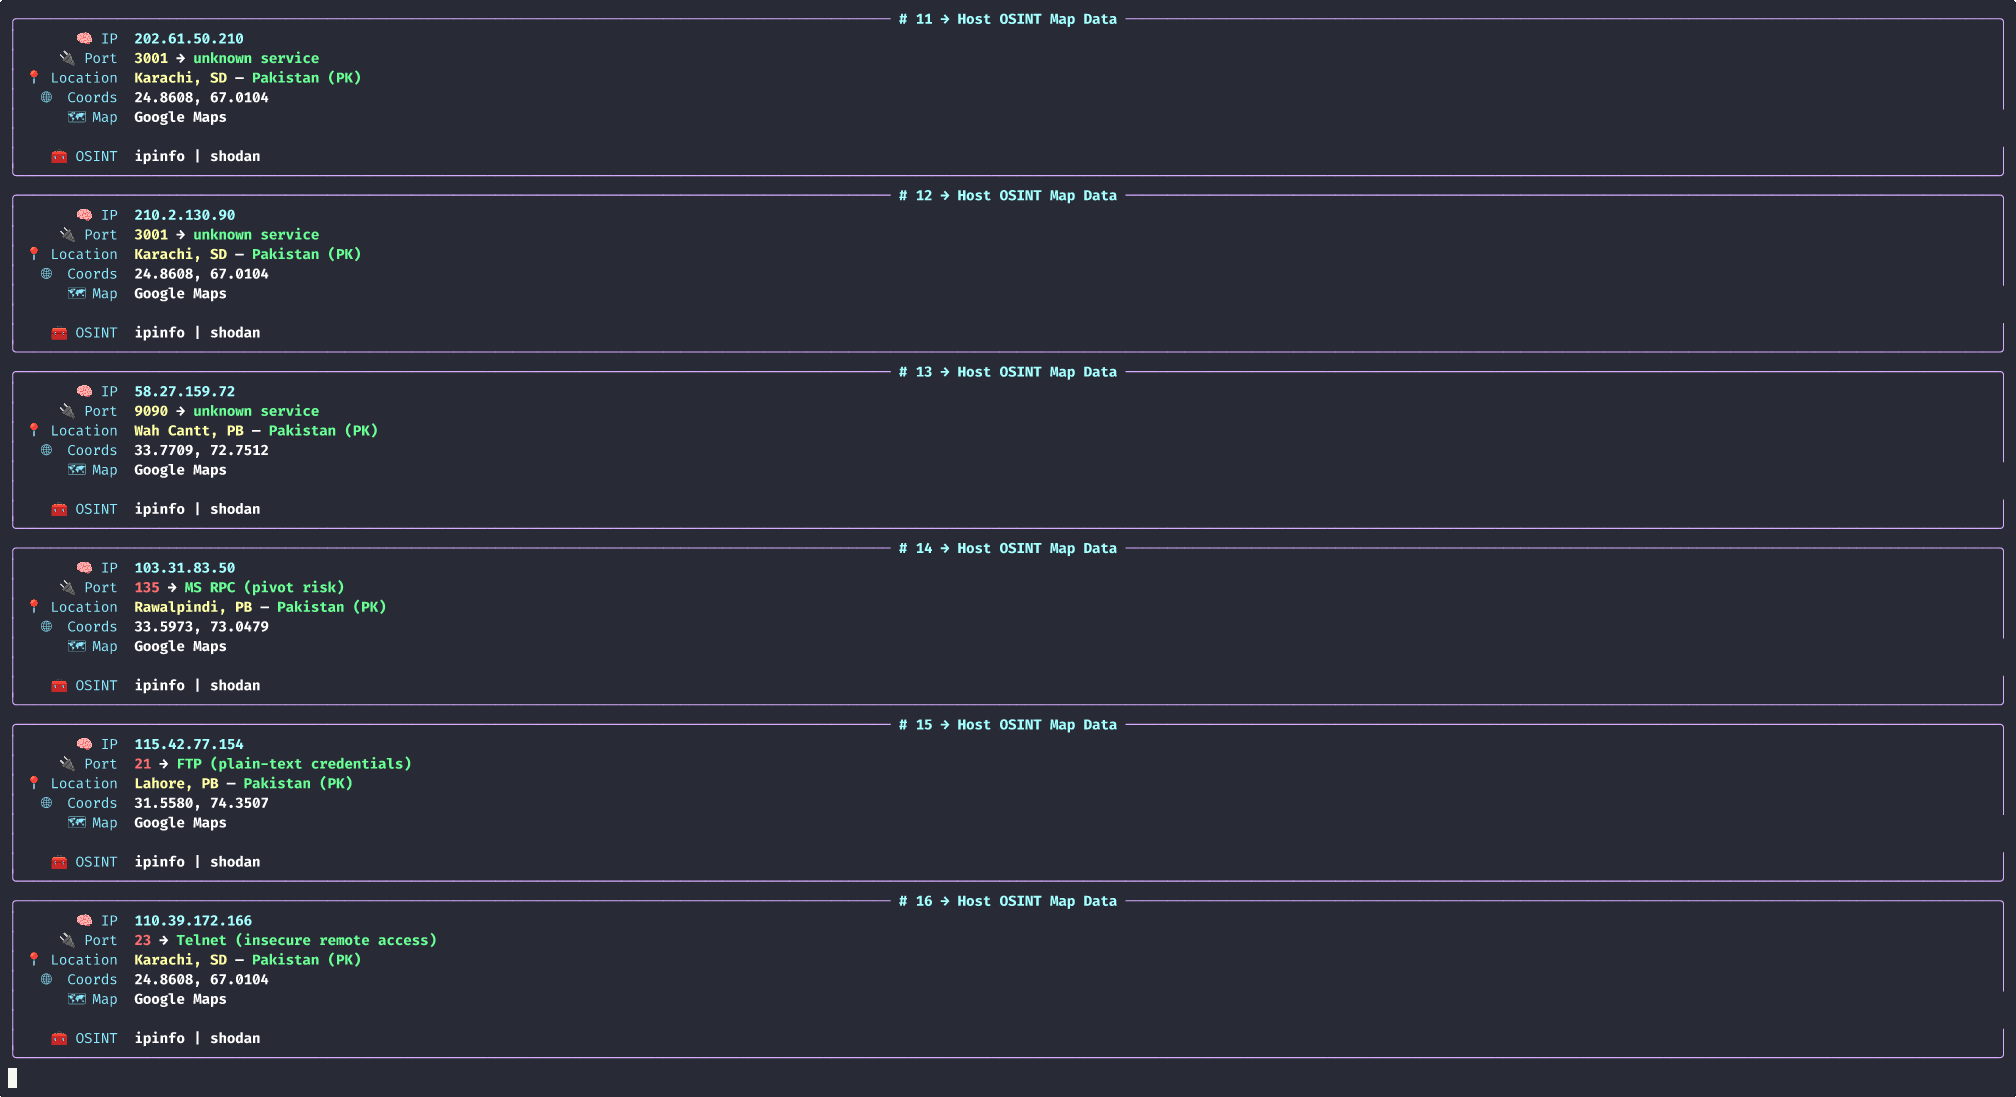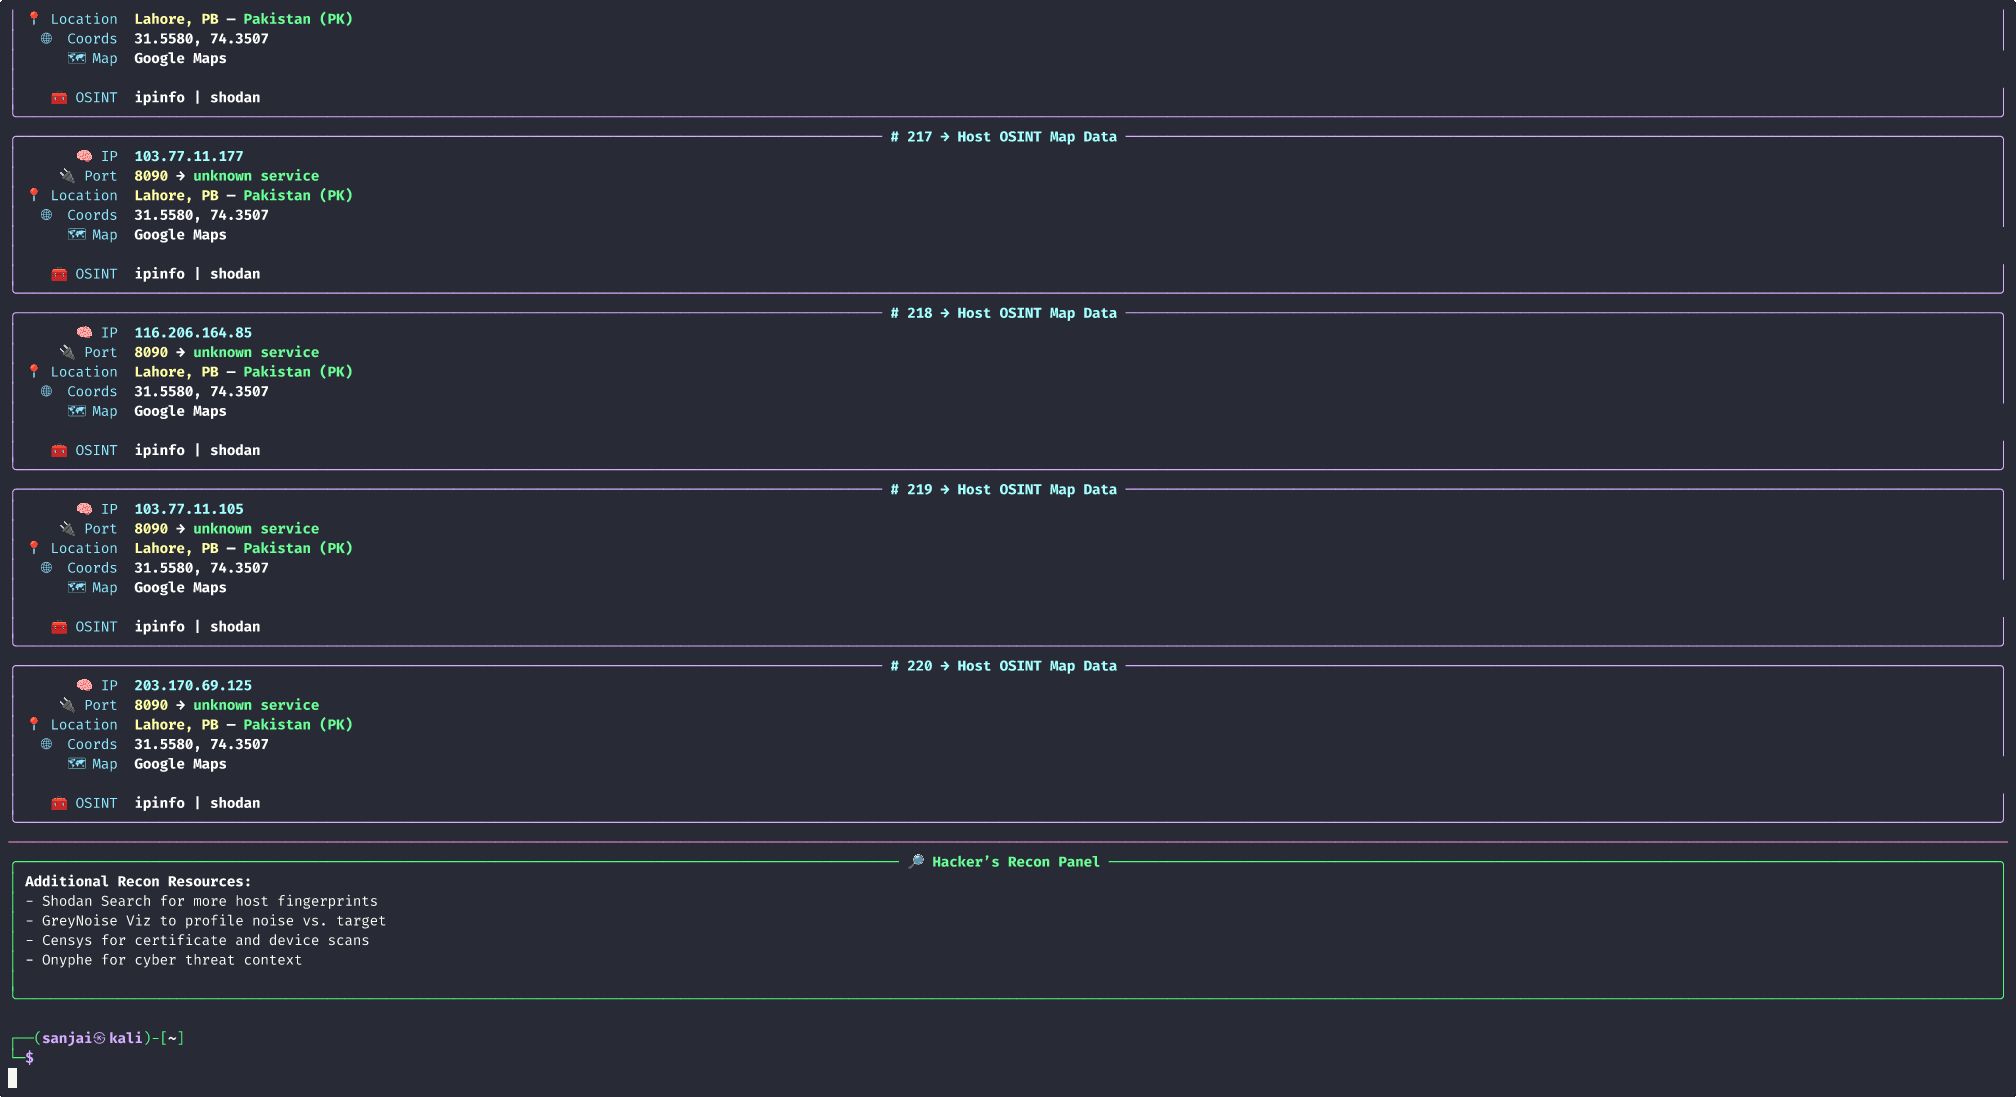
🔐 shodanx auth– Configure and store your Shodan API key securely.🔓 shodanx login– Validate your access level and API key status.🏢 shodanx org– Perform organization-wide scans using Shodan’s powerful facets.🌐 shodanx domain– Enumerate domain-related metadata, open ports, and host exposures.📡 shodanx subdomain– Discover passive subdomains via Shodan’s DNS intel.🔒 shodanx ssl– Track reused or expired SSL certificates via fingerprint searches.🎯 shodanx custom– Run advanced Shodan dorks and custom filter queries.📦 shodanx internetdb– Use Shodan’s lightweight InternetDB for quick IP/domain analysis.🗺️ shodanx map– Visualize geographic distribution of exposed services and ports.🧬 shodanx cvedb– Map hosts to known vulnerabilities using the CVE database.🏭 shodanx entitydb– Explore technologies, software, and vendors across exposed systems.🌍 shodanx exposuredb– Identify publicly exposed assets and data leaks by country.🖼️ shodanx faviconmap– Track systems by unique favicons for lateral discovery.📈 shodanx trends– Analyze exposure trends over time (Enterprise access required).
Installation🚀
shodanx can be easily installed using pip
pip install git+https://github.com/RevoltSecurities/ShodanX --break-system-packages
✅ Make sure you have Python 3.13 or newer installed.
Usage:
shodanx -h
   _____    __                __                   _  __
  / ___/   / /_   ____   ____/ /  ____ _   ____   | |/ /
  \__ \   / __ \ / __ \ / __  /  / __ `/  / __ \  |   /
 ___/ /  / / / // /_/ // /_/ /  / /_/ /  / / / / /   |
/____/  /_/ /_/ \____/ \__,_/   \__,_/  /_/ /_/ /_/|_|


                     - RevoltSecurities

╭───────────────────────╮
│                       │
│    SHODANX ⚡ HELP    │
│                       │
╰───────────────────────╯
DESCRIPTION

ShodanX is a terminal-powered recon and OSINT tool built on top of the Shodan Services.
It empowers ethical hackers and red teamers to identify exposed infrastructure,
search CVEs, map attack surfaces, and run internet-wide queries in real time.

MODES (shodanx <mode>)

┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Mode       ┃ Description                                                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ auth       │ Configure and save your Shodan API key for authenticated access. │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ login      │ Verify your ShodanX access level and API key validity.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ org        │ Perform organization-wide scans using Shodan facets.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ domain     │ Enumerate metadata, ports, and host exposure for a domain.       │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ subdomain  │ Discover passive subdomains using Shodan’s DNS data.             │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ ssl        │ Search by SSL fingerprint to track reused/expired certs.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ custom     │ Execute advanced queries using Shodan filters and dorks.         │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ internetdb │ Lightweight analysis of IPs/domains via Shodan InternetDB API.   │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ map        │ Visualize geo-distribution of exposed services and ports.        │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ cvedb      │ Identify vulnerable systems via Shodan’s CVE database.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ entitydb   │ Explore technologies/vendors via Shodan’s EntityDB.              │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ exposuredb │ Discover globally exposed assets and leaks by country.           │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ faviconmap │ Find systems using specific favicons via Shodan FaviconMap.      │
├────────────┼──────────────────────────────────────────────────────────────────┤
│ trends     │ View historical exposure trends (Shodan Enterprise required).    │
└────────────┴──────────────────────────────────────────────────────────────────┘
FLAGS
┏━━━━━━━━━━━━┳━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┓
┃ Flag       ┃ Description                      ┃
┡━━━━━━━━━━━━╇━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━━┩
│ -h, --help │ Show this help message and exit. │
└────────────┴──────────────────────────────────┘
USAGE
shodanx <mode>

DETAILS
 shodanx auth        → Configure and save your Shodan API key for authenticated access.
 shodanx login       → Verify your ShodanX access level and API key validity.
 shodanx org         → Perform organization-wide scans using Shodan facets.
 shodanx domain      → Enumerate metadata, ports, and host exposure for a domain.
 shodanx subdomain   → Discover passive subdomains using Shodan’s DNS data.
 shodanx ssl         → Search by SSL fingerprint to track reused/expired certs.
 shodanx custom      → Execute advanced queries using Shodan filters and dorks.
 shodanx internetdb  → Lightweight analysis of IPs/domains via Shodan InternetDB API.
 shodanx map         → Visualize geo-distribution of exposed services and ports.
 shodanx cvedb       → Identify vulnerable systems via Shodan’s CVE database.
 shodanx entitydb    → Explore technologies/vendors via Shodan’s EntityDB.
 shodanx exposuredb  → Discover globally exposed assets and leaks by country.
 shodanx faviconmap  → Find systems using specific favicons via Shodan FaviconMap.
 shodanx trends      → View historical exposure trends (Shodan Enterprise required).
Post Installation:
Once you've successfully installed shodanx, follow these quick steps to get fully authenticated and ready to scan:
1. 🔑 Authenticate Your Shodan API Key
Start by running the auth command to securely store your credentials:
shodanx auth
You'll be prompted to enter:
- Username – for local session identification
- Password – used for encrypting your local credentials
- Shodan API Key – required for authenticated access to most Shodan services
✅ Security Note: All your sensitive inputs (username, password, API key) are securely stored in your local user shodanx configuration file. No external calls or storage are involved during this setup.
2. 🧠 Session Login via Shodan Web Cookie
Next, run the login command to authenticate against Shodan’s session-protected endpoints:
shodanx login
You'll be asked to paste your active Shodan session cookie (copied as a single string) from:
- Browser Dev Tools → Application → Cookies →
.shodan.io - OR intercept it via Burp Suite / Proxy tools
Paste the session string when prompted. This is used for advanced session-based features.
3. 🚀 You're Ready!
You now have access to the full shodanx suite of modules.
💡 Note: Certain modules like
trendsrequire a Shodan Enterprise API key for access to premium data visualizations and trend insights andmaprequire a Shodan's high level subscription account cookie
Acknowledgements
ShodanX is built with ❤️ by RevoltSecurities — for hackers, by hackers.
We deeply appreciate all the users who trust ShodanX for automating and enhancing their cybersecurity workflows. Your usage, feedback, and support drive the continued evolution of this powerful tool. Thank you for choosing ShodanX to power your recon, enumeration, and exploitation efforts.
Stay ethical. Stay sharp. Stay ahead. — With respect, the RevoltSecurities
1 maintainer

Metadata
1 maintainer
Release files for shodanx 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| shodanx-1.1.1.tar.gz | 35.3 kB | Without provenance | Details for shodanx-1.1.1.tar.gz |
Release files / shodanx-1.1.1.tar.gz
| Download URL | shodanx-1.1.1.tar.gz |
|---|---|
| Size | 35.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
23e1970db64ded6946ee6bb2a2897d30e650b4ff5a96f205be93c2d30df575a8
|
|
BLAKE2b-256 checksum How to use checksums |
8b9a34bd2af8a8b400cdabe39a66065e978f26ee6535430810bfd826638d3f7f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.1.0 CPython/3.12.10
|
Security for shodanx 1.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














