
tagged-users
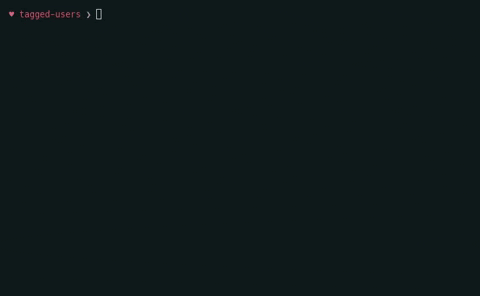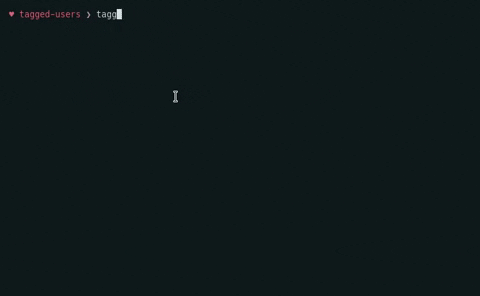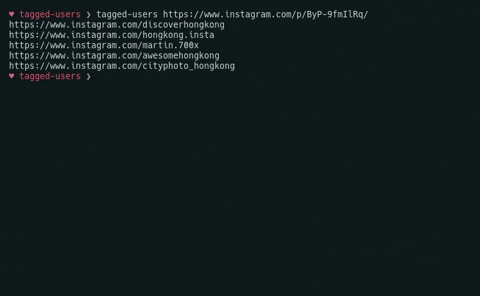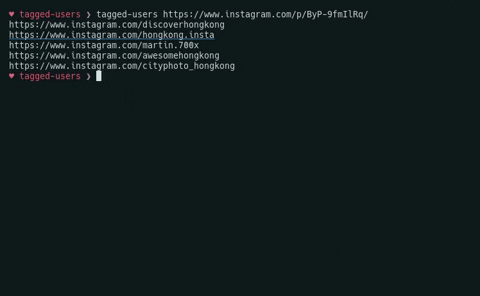
- Exactly 64 lines of code (including comments)
- Works on Linux and MacOS
- Only 4KB
- Able to be piped out to other programs
Why?
Many times, the person who posted the photo, puts all the tags very close to each other, which makes is very difficult click on the username.
Here is an example of what I mean:
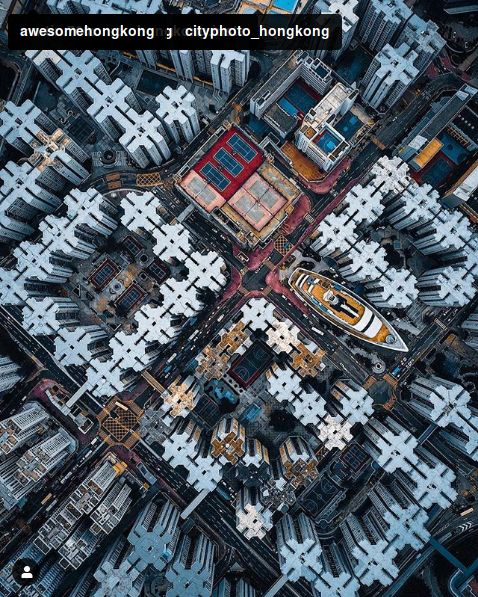
Honestly, it is almost impossible to click on some of the tags.
Installation
pip3 install tagged-users
Usage
usage: tagged-users [-h] url

Get all the usernames of the people who got tagged in an Instagram post

positional arguments:
  url         URL to Instagram post

optional arguments:
  -h, --help  show this help message and exit
License
MIT License
Copyright (c) 2019 Siddharth Dushantha
1 maintainer

Metadata
1 maintainer
Release files for tagged-users 1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| tagged-users-1.1.tar.gz | 2.5 kB | Without provenance | Details |
Release files / tagged-users-1.1.tar.gz
| Download URL | tagged-users-1.1.tar.gz |
|---|---|
| Size | 2.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5471f05084bbcf533068a97b583848830c2c5f6c01786d1c87e2b885ef87ed9e
|
|
BLAKE2b-256 checksum How to use checksums |
db27d429adc16e89d87d2a7898355c93d8030ab23a168ef3c754f0cc2f595ce5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.13.0 pkginfo/1.5.0.1 requests/2.22.0 setuptools/41.0.1 requests-toolbelt/0.9.1 tqdm/4.32.1 CPython/3.7.3
|
Security for tagged-users 1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














