
wxc


wxc (pronounced "which") allows you to inspect source code in your Python
environment from the command line. It is based on the inspect module from the
standard library.
Installation
$ python -m pip install wxc
Usage
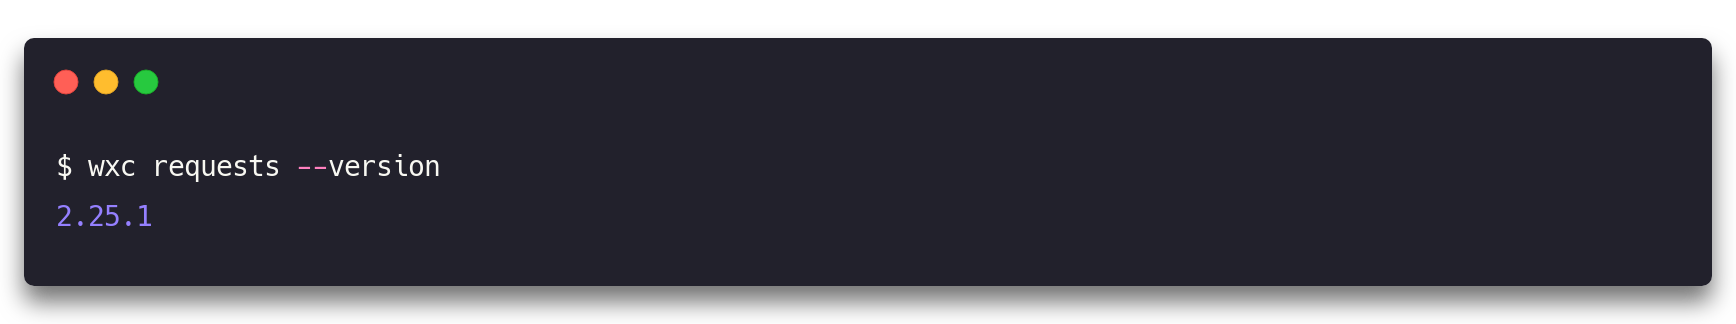
Get the version number of a package in your current environment
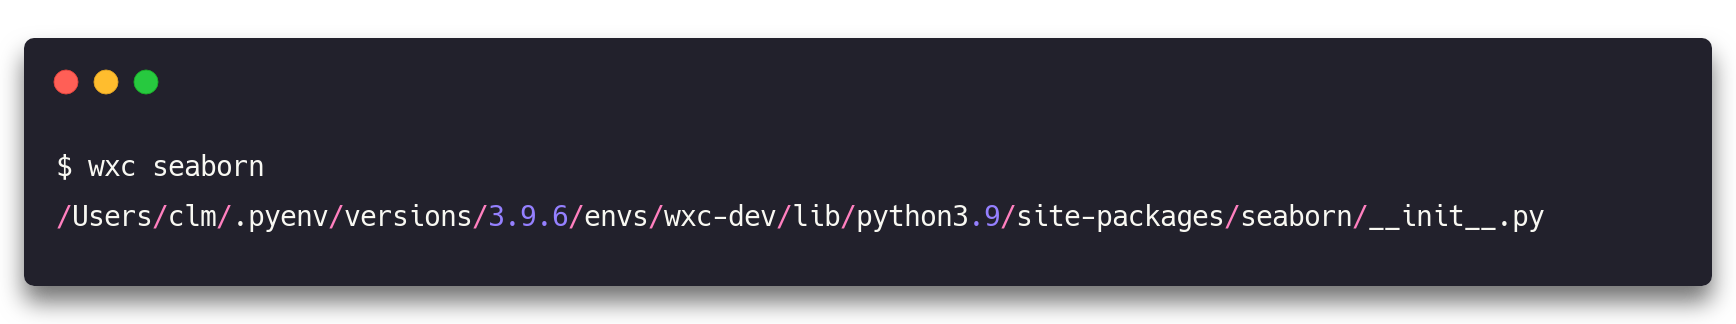
Locate the file from which a Python package is imported
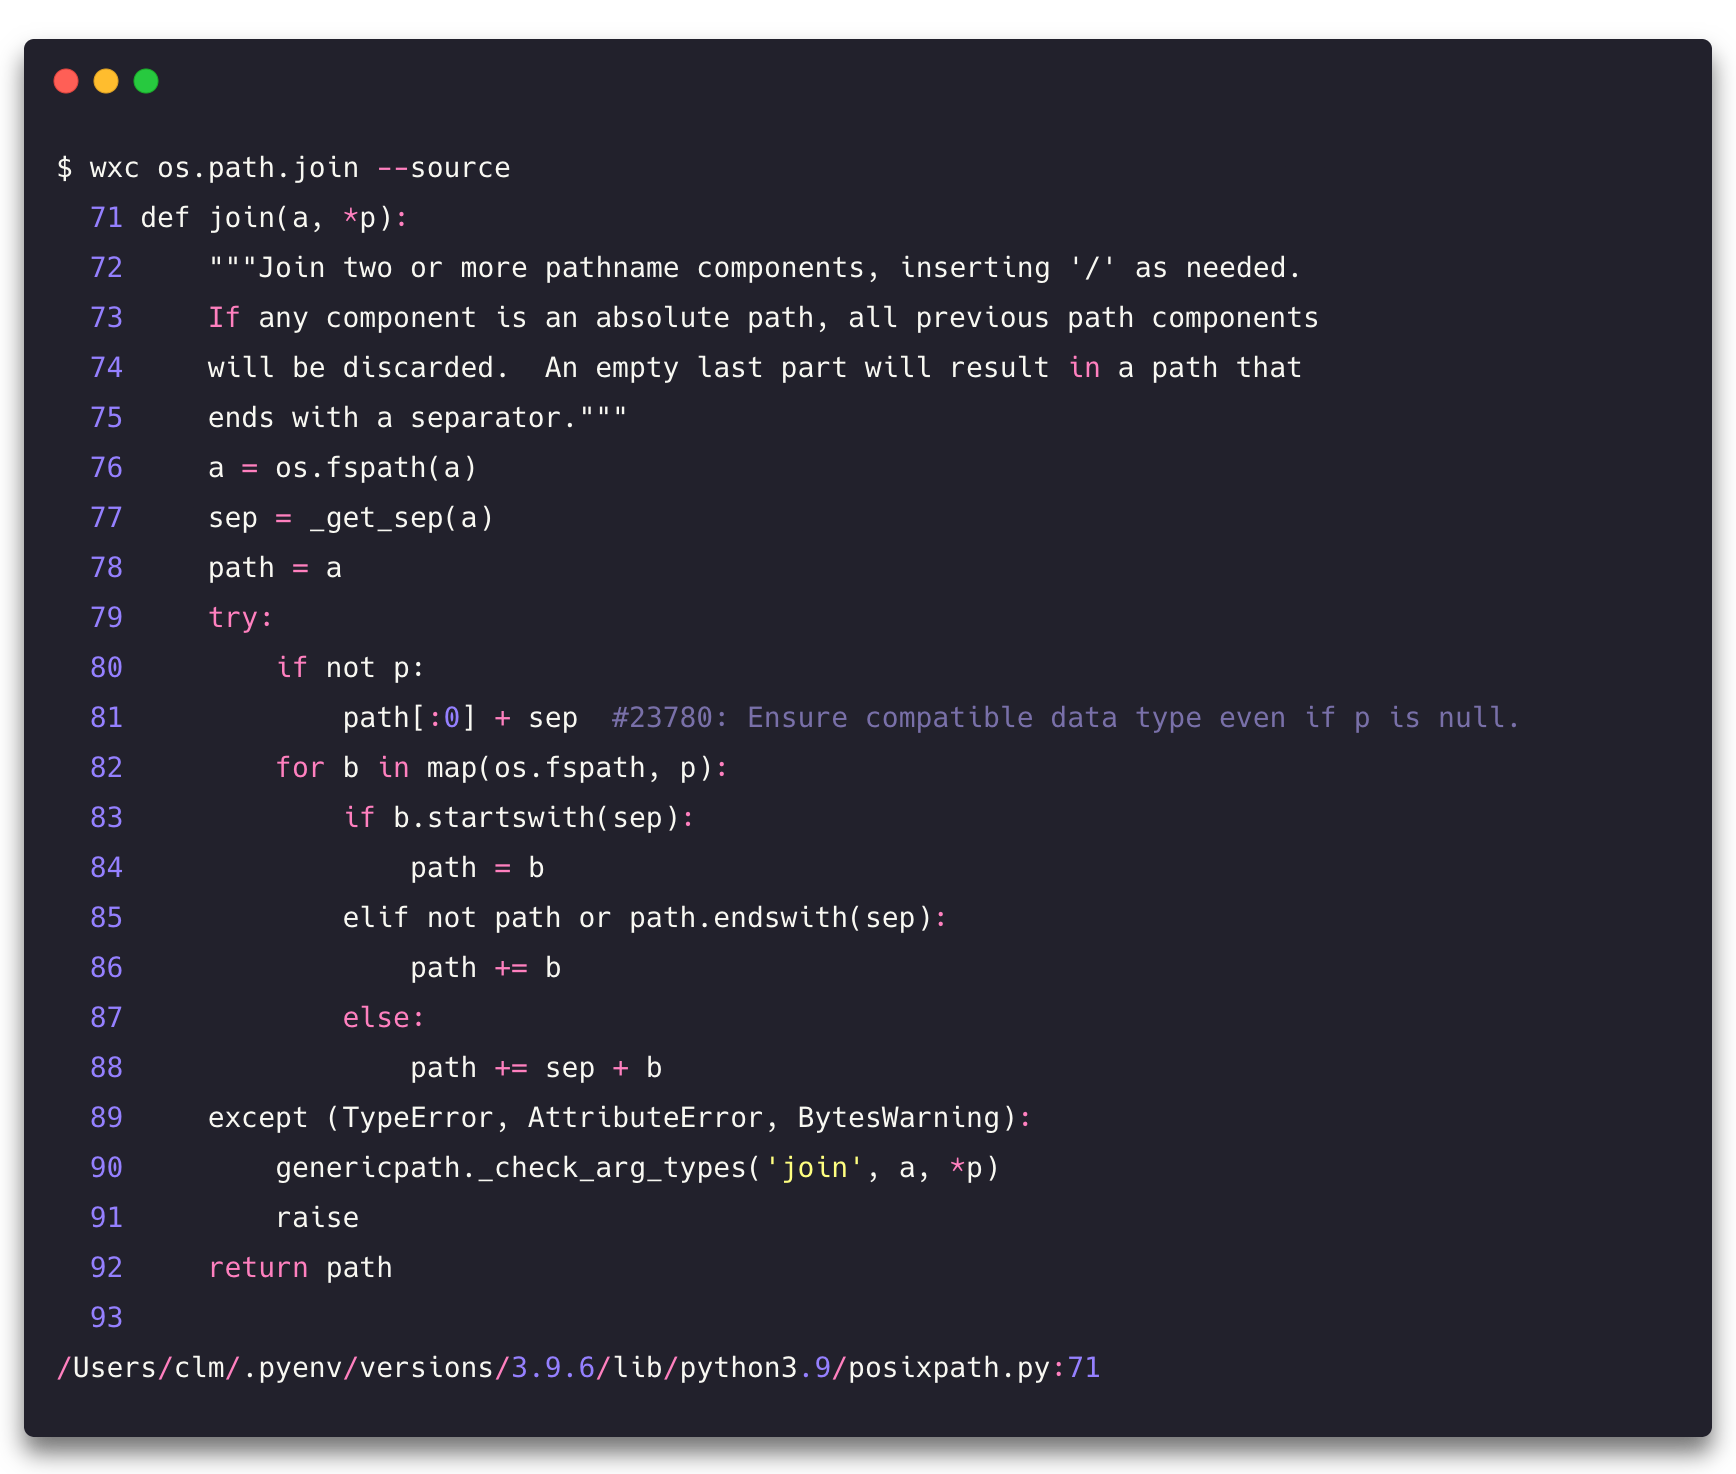
Locate a specific method's source code

View the source code of function directly from the terminal stdout
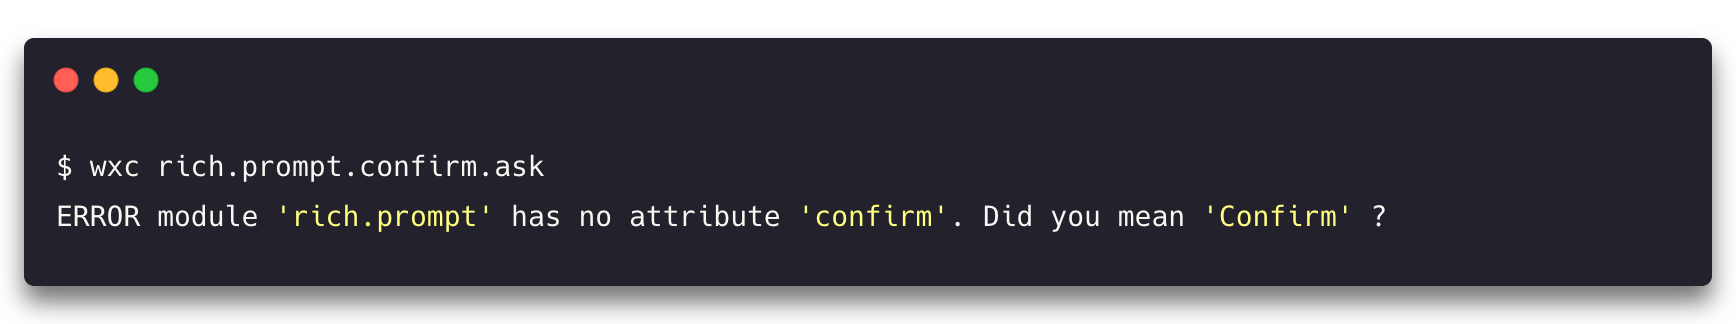
wxc tries to be helpful when you mistype
For more, run
$ wxc --help
Known limitations
wxc is not currently able to retrieve the source of compiled code binded into
Python. It should however correctly point to the compiled file that an object is
imported from.
wxc should never be installed in isolation (for instance via
pipx) since it would completely defeat
its purpose.
Notes
wxcis fully tested on macOS, Linux, and partially on Windows- this project was formerly named "whych" and renamed to avoid confusion with the pypi-available package of the same name.
1 maintainer

Metadata
1 maintainer
Release files for wxc 7.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| wxc-7.2.0.tar.gz | 18.0 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| wxc-7.2.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 36.9 kB
Release files / wxc-7.2.0.tar.gz
| Download URL | wxc-7.2.0.tar.gz |
|---|---|
| Size | 18.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7a5089f6d67afe3cefe794890c4e99d56039adfd35ef969f50e8643d722608b1
|
|
BLAKE2b-256 checksum How to use checksums |
3ac561400f0caa4e16a19abe9101a52fe3ffa14995303f485ad85130c8e531e5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jun 29, 2025.
Transparency logRelease files / wxc-7.2.0-py3-none-any.whl
| Download URL | wxc-7.2.0-py3-none-any.whl |
|---|---|
| Size | 18.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
9ab70f52c5610af4ceb0d197efdb74c63195a2e8ec8df544a233fd8befefc7c2
|
|
BLAKE2b-256 checksum How to use checksums |
625426830ddb83b0f6906c511b24786406e7dd7af1e733241454b563211c0d87
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jun 29, 2025.
Transparency logSecurity for wxc 7.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for wxc-7.2.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jun 29, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














