
🧠🤖 Deep Agents Code


Quick Install
curl -LsSf https://langch.in/dcode | bash
# With model provider extras
# OpenAI, Anthropic, and Gemini are included by default
DEEPAGENTS_CODE_EXTRAS="nvidia,ollama" curl -LsSf https://langch.in/dcode | bash
Run:
dcode
🤔 What is this?
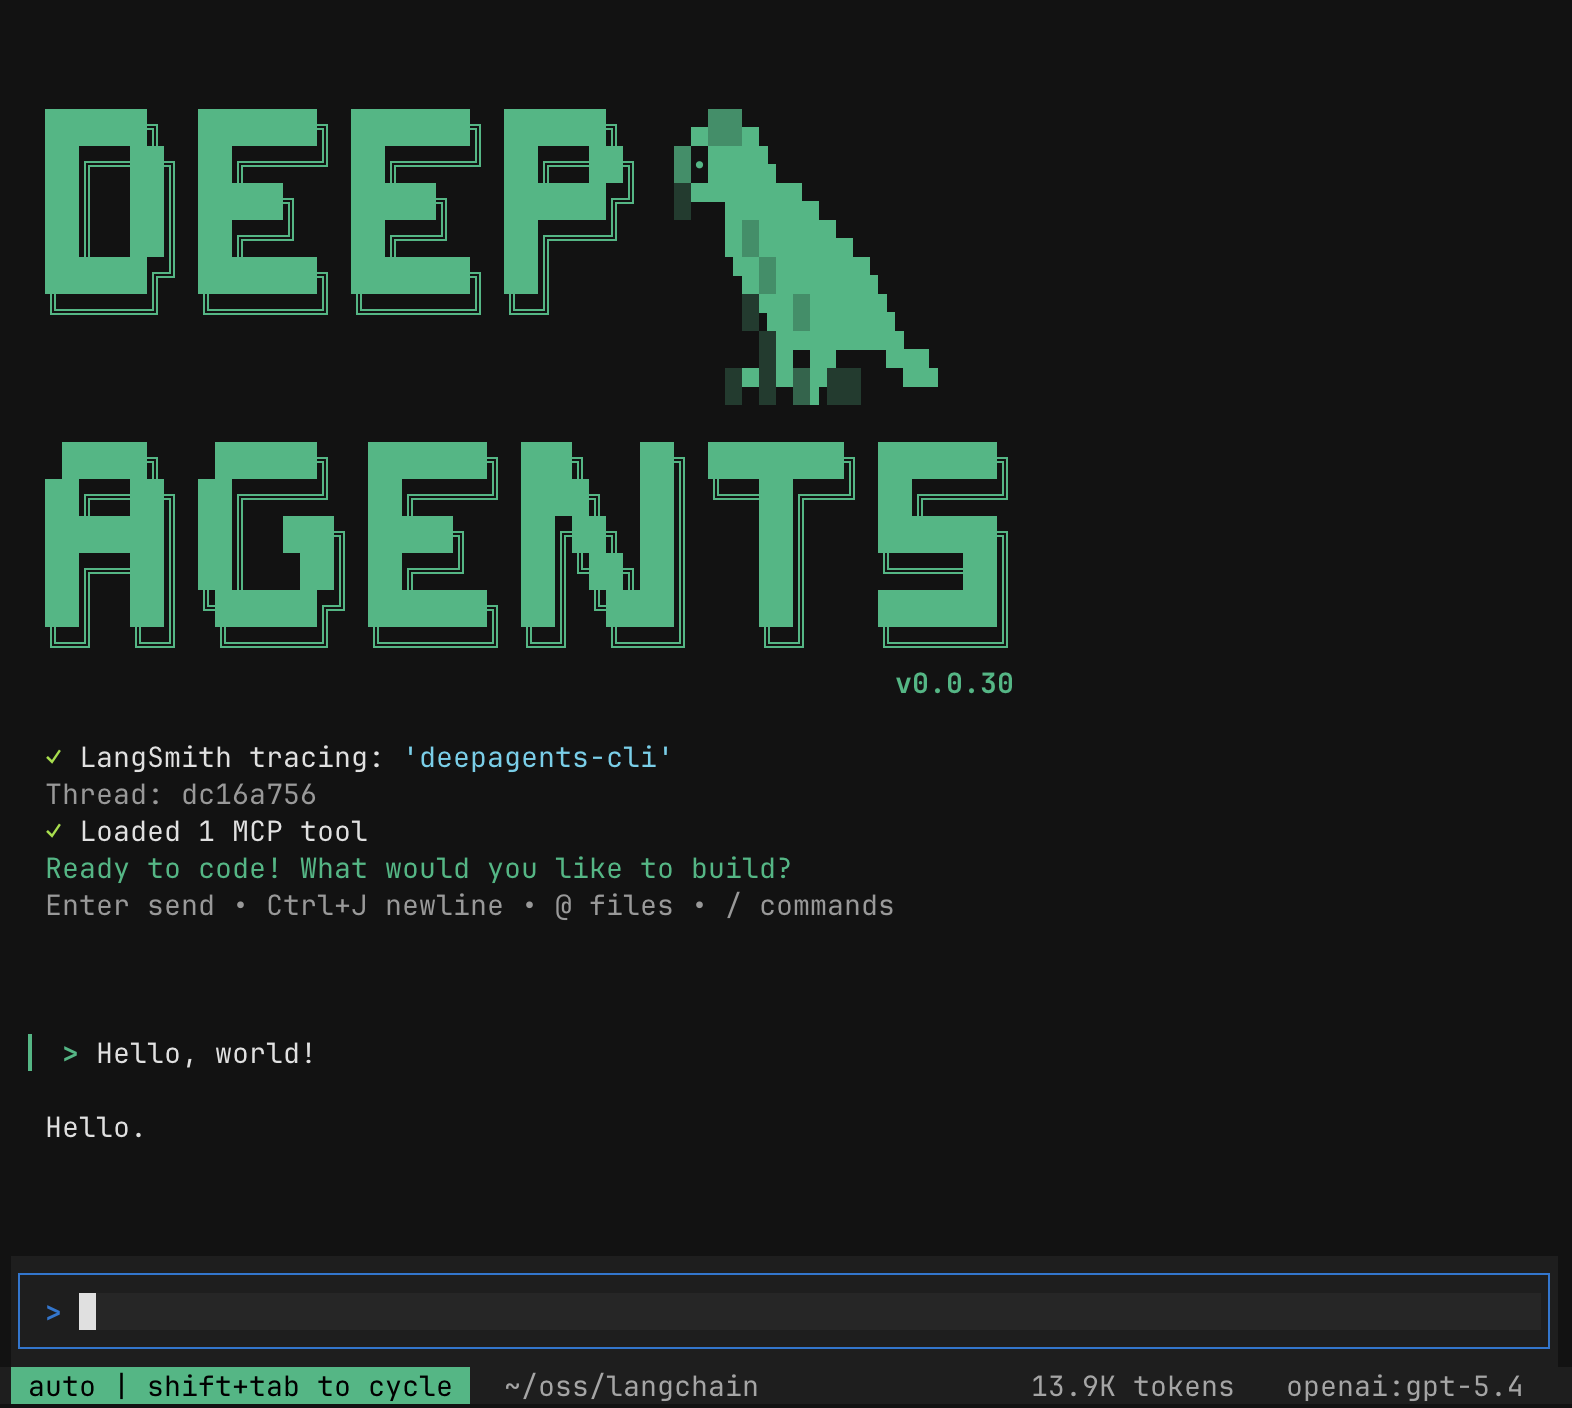
The fastest way to start using Deep Agents. deepagents-code is a pre-built coding agent in your terminal — similar to Claude Code or Cursor — powered by any LLM that supports tool calling. One install command and you're up and running, no code required.
What deepagents-code adds on top of the SDK:
- Interactive TUI — rich terminal interface with streaming responses
- Conversation resume — pick up where you left off across sessions
- Web search — ground responses in live information
- Remote sandboxes — run code in isolated environments (LangSmith, AgentCore, Daytona, Modal, Runloop, & more)
- Persistent memory — agent remembers context across conversations
- Custom skills — extend the agent with your own slash commands
- Headless mode — run non-interactively for scripting and CI
- Human-in-the-loop — approve or reject tool calls before execution
🔒 Security model
By default, dcode trusts the directory you run it in. Human-in-the-loop approval gates model-requested tool calls, but project artifacts are read before any approval prompt.
Do not run dcode in a directory you do not trust without a sandbox backend. For untrusted repositories, use a remote sandbox so execution is isolated from your machine. Running dcode in a directory lets that directory's files shape execution. See THREAT_MODEL.md for details.
📖 Resources
- Documentation
- Changelog
- Source code
- Deep Agents SDK — underlying agent harness
- LangChain Academy — Comprehensive, free courses on LangChain libraries and products, made by the LangChain team.
- Code of Conduct — community guidelines and standards
📕 Releases & Versioning
See our Releases and Versioning policies.
💁 Contributing
As an open-source project in a rapidly developing field, we are extremely open to contributions, whether it be in the form of a new feature, improved infrastructure, or better documentation.
For detailed information on how to contribute, see the Contributing Guide.
🤝 Acknowledgements
This project was primarily inspired by Claude Code, and initially was largely an attempt to see what made Claude Code general purpose, and make it even more so.
1 maintainer

Metadata
1 maintainer
Release files for zjcode 0.0.16
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| zjcode-0.0.16.tar.gz | 3.2 MB | With provenance | Details for zjcode-0.0.16.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| zjcode-0.0.16-py3-none-any.whl | Python 3 | none | any | Details for zjcode-0.0.16-py3-none-any.whl |
Total release size: 4.4 MB
Release files / zjcode-0.0.16.tar.gz
| Download URL | zjcode-0.0.16.tar.gz |
|---|---|
| Size | 3.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b3f035657406bcbb72d110490ce55700fb98ec3833b90139bd2e46b65aa90e3a
|
|
BLAKE2b-256 checksum How to use checksums |
f4a2b9ccaf694a36a51a1c071dcc342365007bfe86f59a7dd3649f52754bc0fb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 2, 2026.
Transparency logRelease files / zjcode-0.0.16-py3-none-any.whl
| Download URL | zjcode-0.0.16-py3-none-any.whl |
|---|---|
| Size | 1.2 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
95322f31e6fffe07836a4cbfbd01005c9e1ed43594bfe725225b285a39b946a2
|
|
BLAKE2b-256 checksum How to use checksums |
7670a36932cb74c2529bea0ff8ecc90991b1fd337651474fa19f9cfb61c659db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 2, 2026.
Transparency logSecurity for zjcode 0.0.16
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for zjcode-0.0.16.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 2, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














