
Overview
Gitman is a language-agnostic dependency manager using Git. It aims to serve as a submodules replacement and provides advanced options for managing versions of nested Git repositories.


Setup
Requirements
- Python 3.10+
- Git 2.8+ (with stored credentials)
Installation
Install this tool globally with pipx (or pip):
$ pipx install gitman
or add it to your Poetry project:
$ poetry add gitman
Configuration
Generate a sample config file:
$ gitman init
or manually create one (gitman.yml or .gitman.yml) in the root of your working tree:
location: vendor/gitman

sources:
  - repo: "https://github.com/kstenerud/iOS-Universal-Framework"
    name: framework
    rev: Mk5-end-of-life
  - repo: "https://github.com/jonreid/XcodeCoverage"
    name: coverage
    links:
      - target: Tools/XcodeCoverage
  - repo: "https://github.com/dxa4481/truffleHog"
    name: trufflehog
    rev: master
    scripts:
      - chmod a+x truffleHog/truffleHog.py
  - repo: "https://github.com/FortAwesome/Font-Awesome"
    name: fontawesome
    rev: master
    sparse_paths:
      - "webfonts/*"
  - repo: "https://github.com/google/material-design-icons"
    name: material-design-icons
    rev: master

groups:
  - name: code
    members:
      - framework
      - trufflehog
  - name: resources
    members:
      - fontawesome
      - material-design-icons

default_group: code
Ignore the dependency storage location:
$ echo vendor/gitman >> .gitignore
Usage
See the available commands:
$ gitman --help
Updating Dependencies
Get the latest versions of all dependencies:
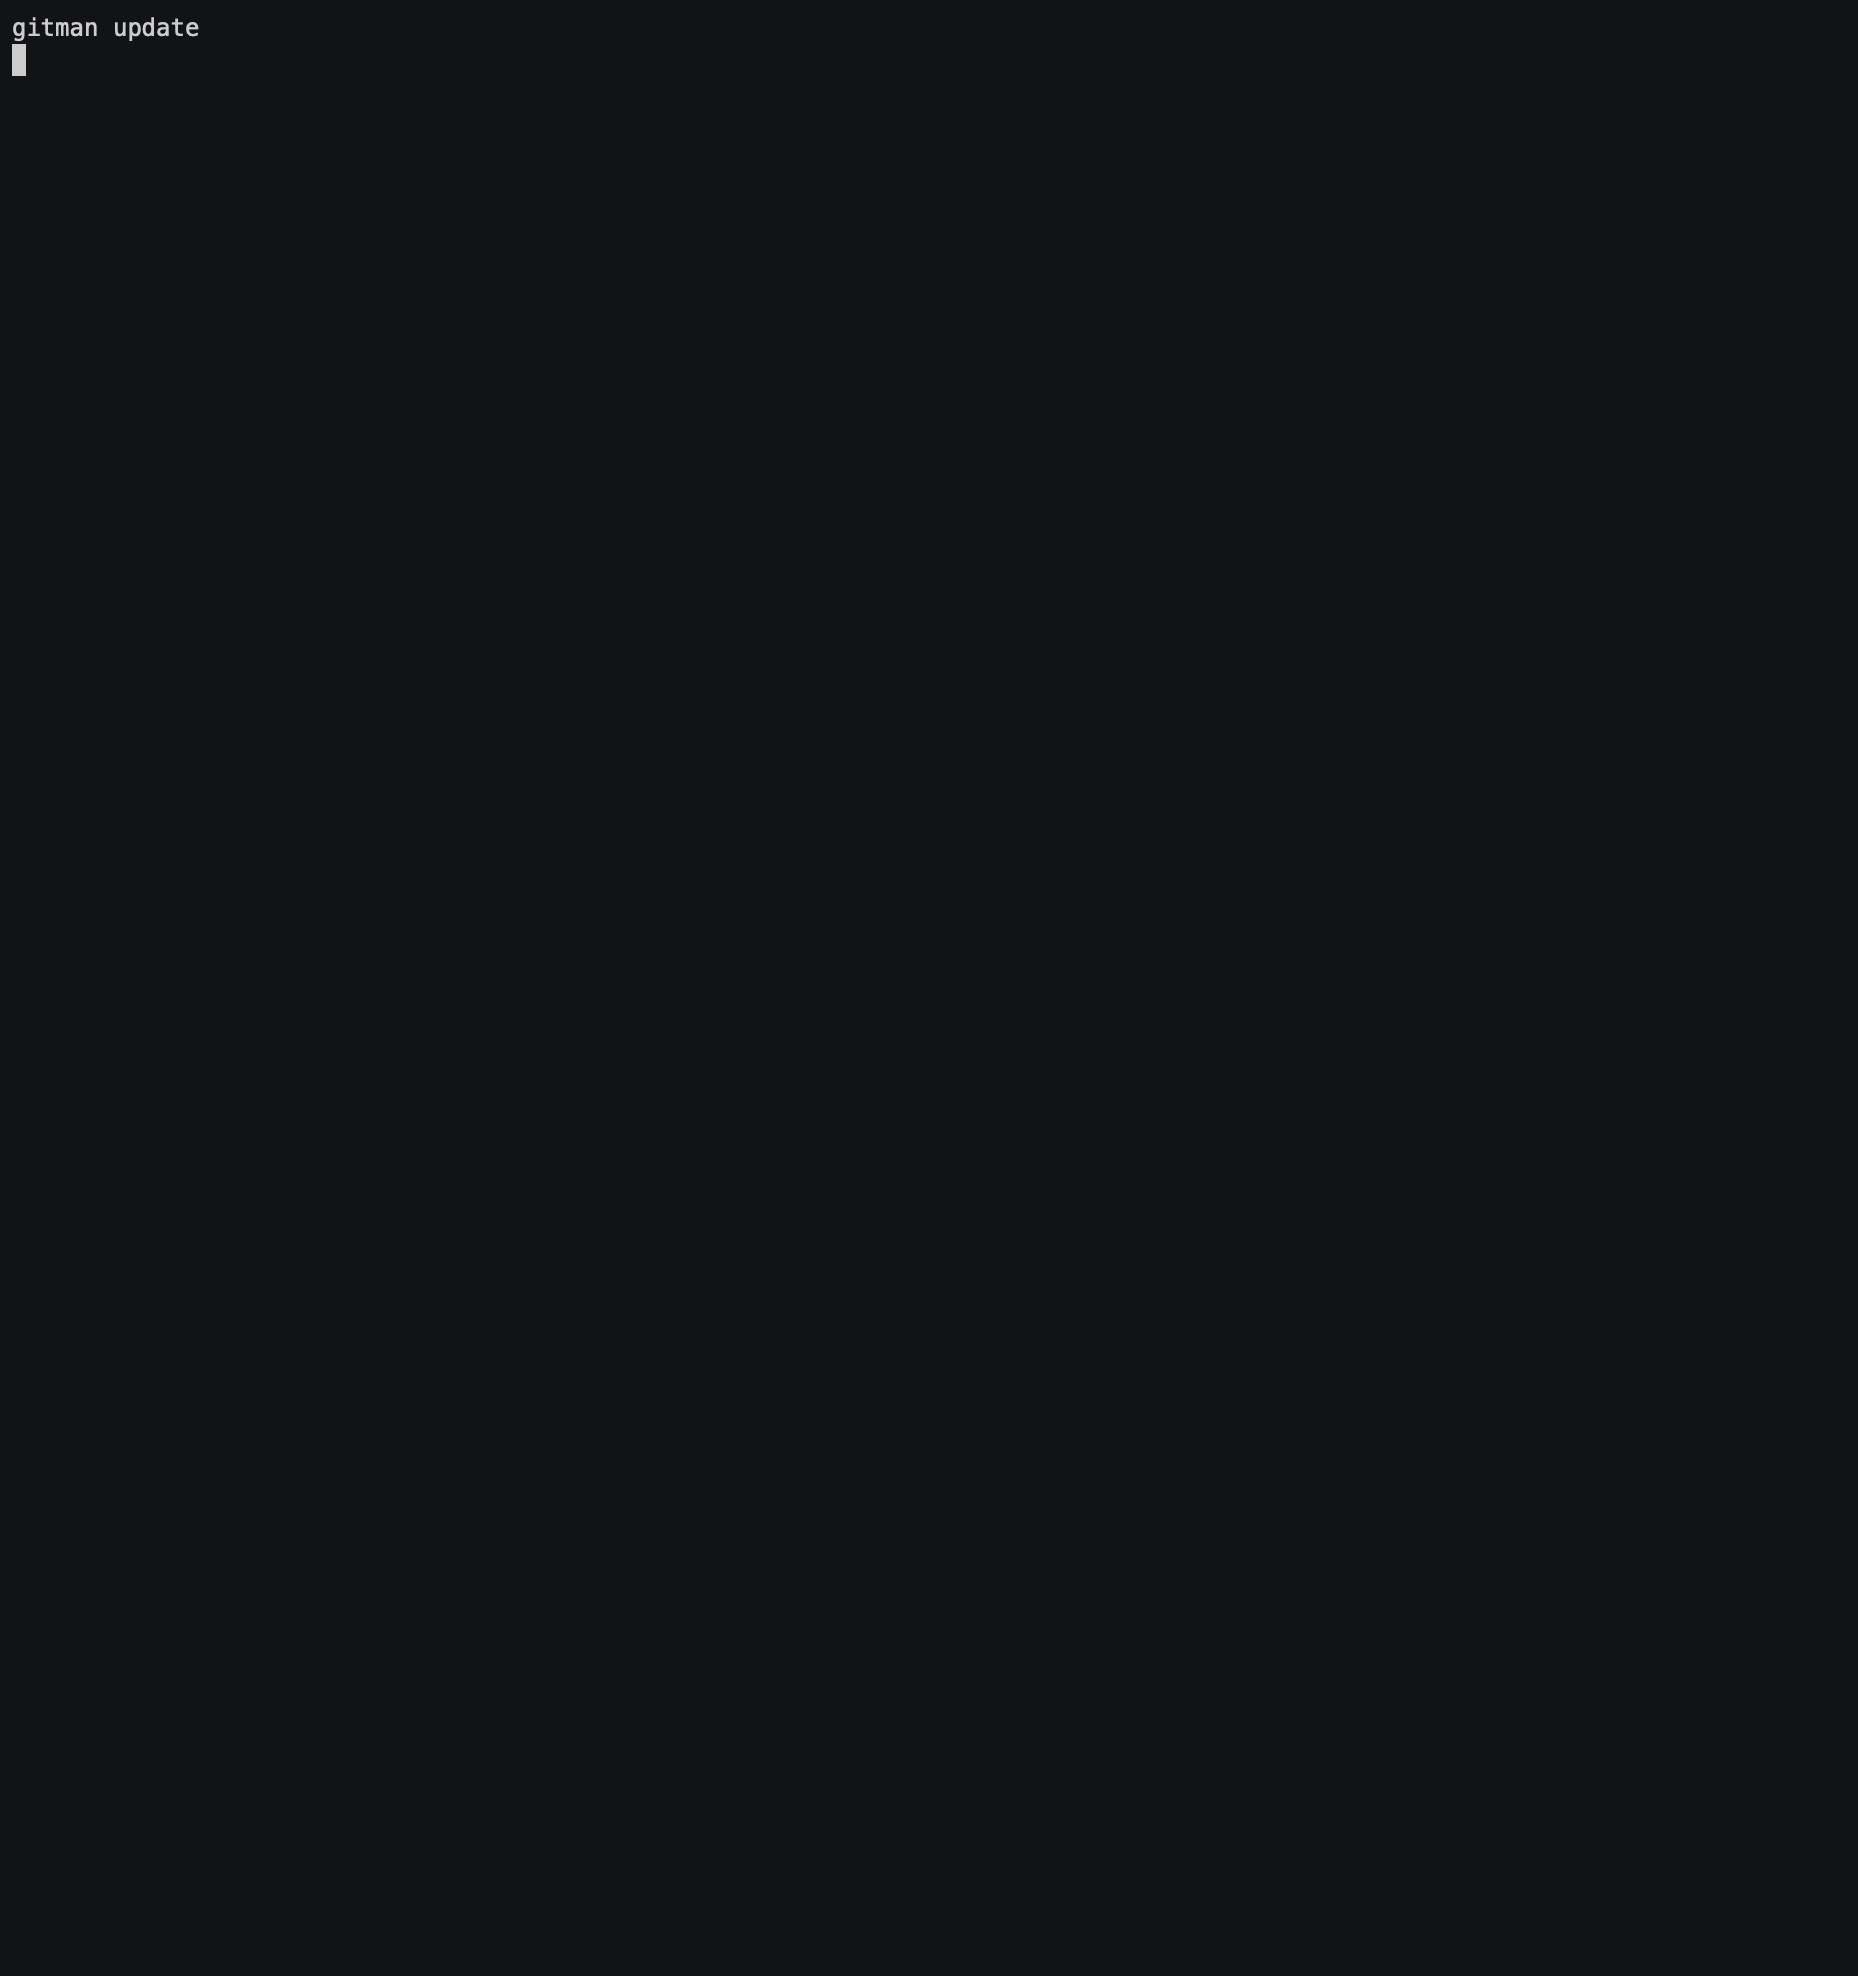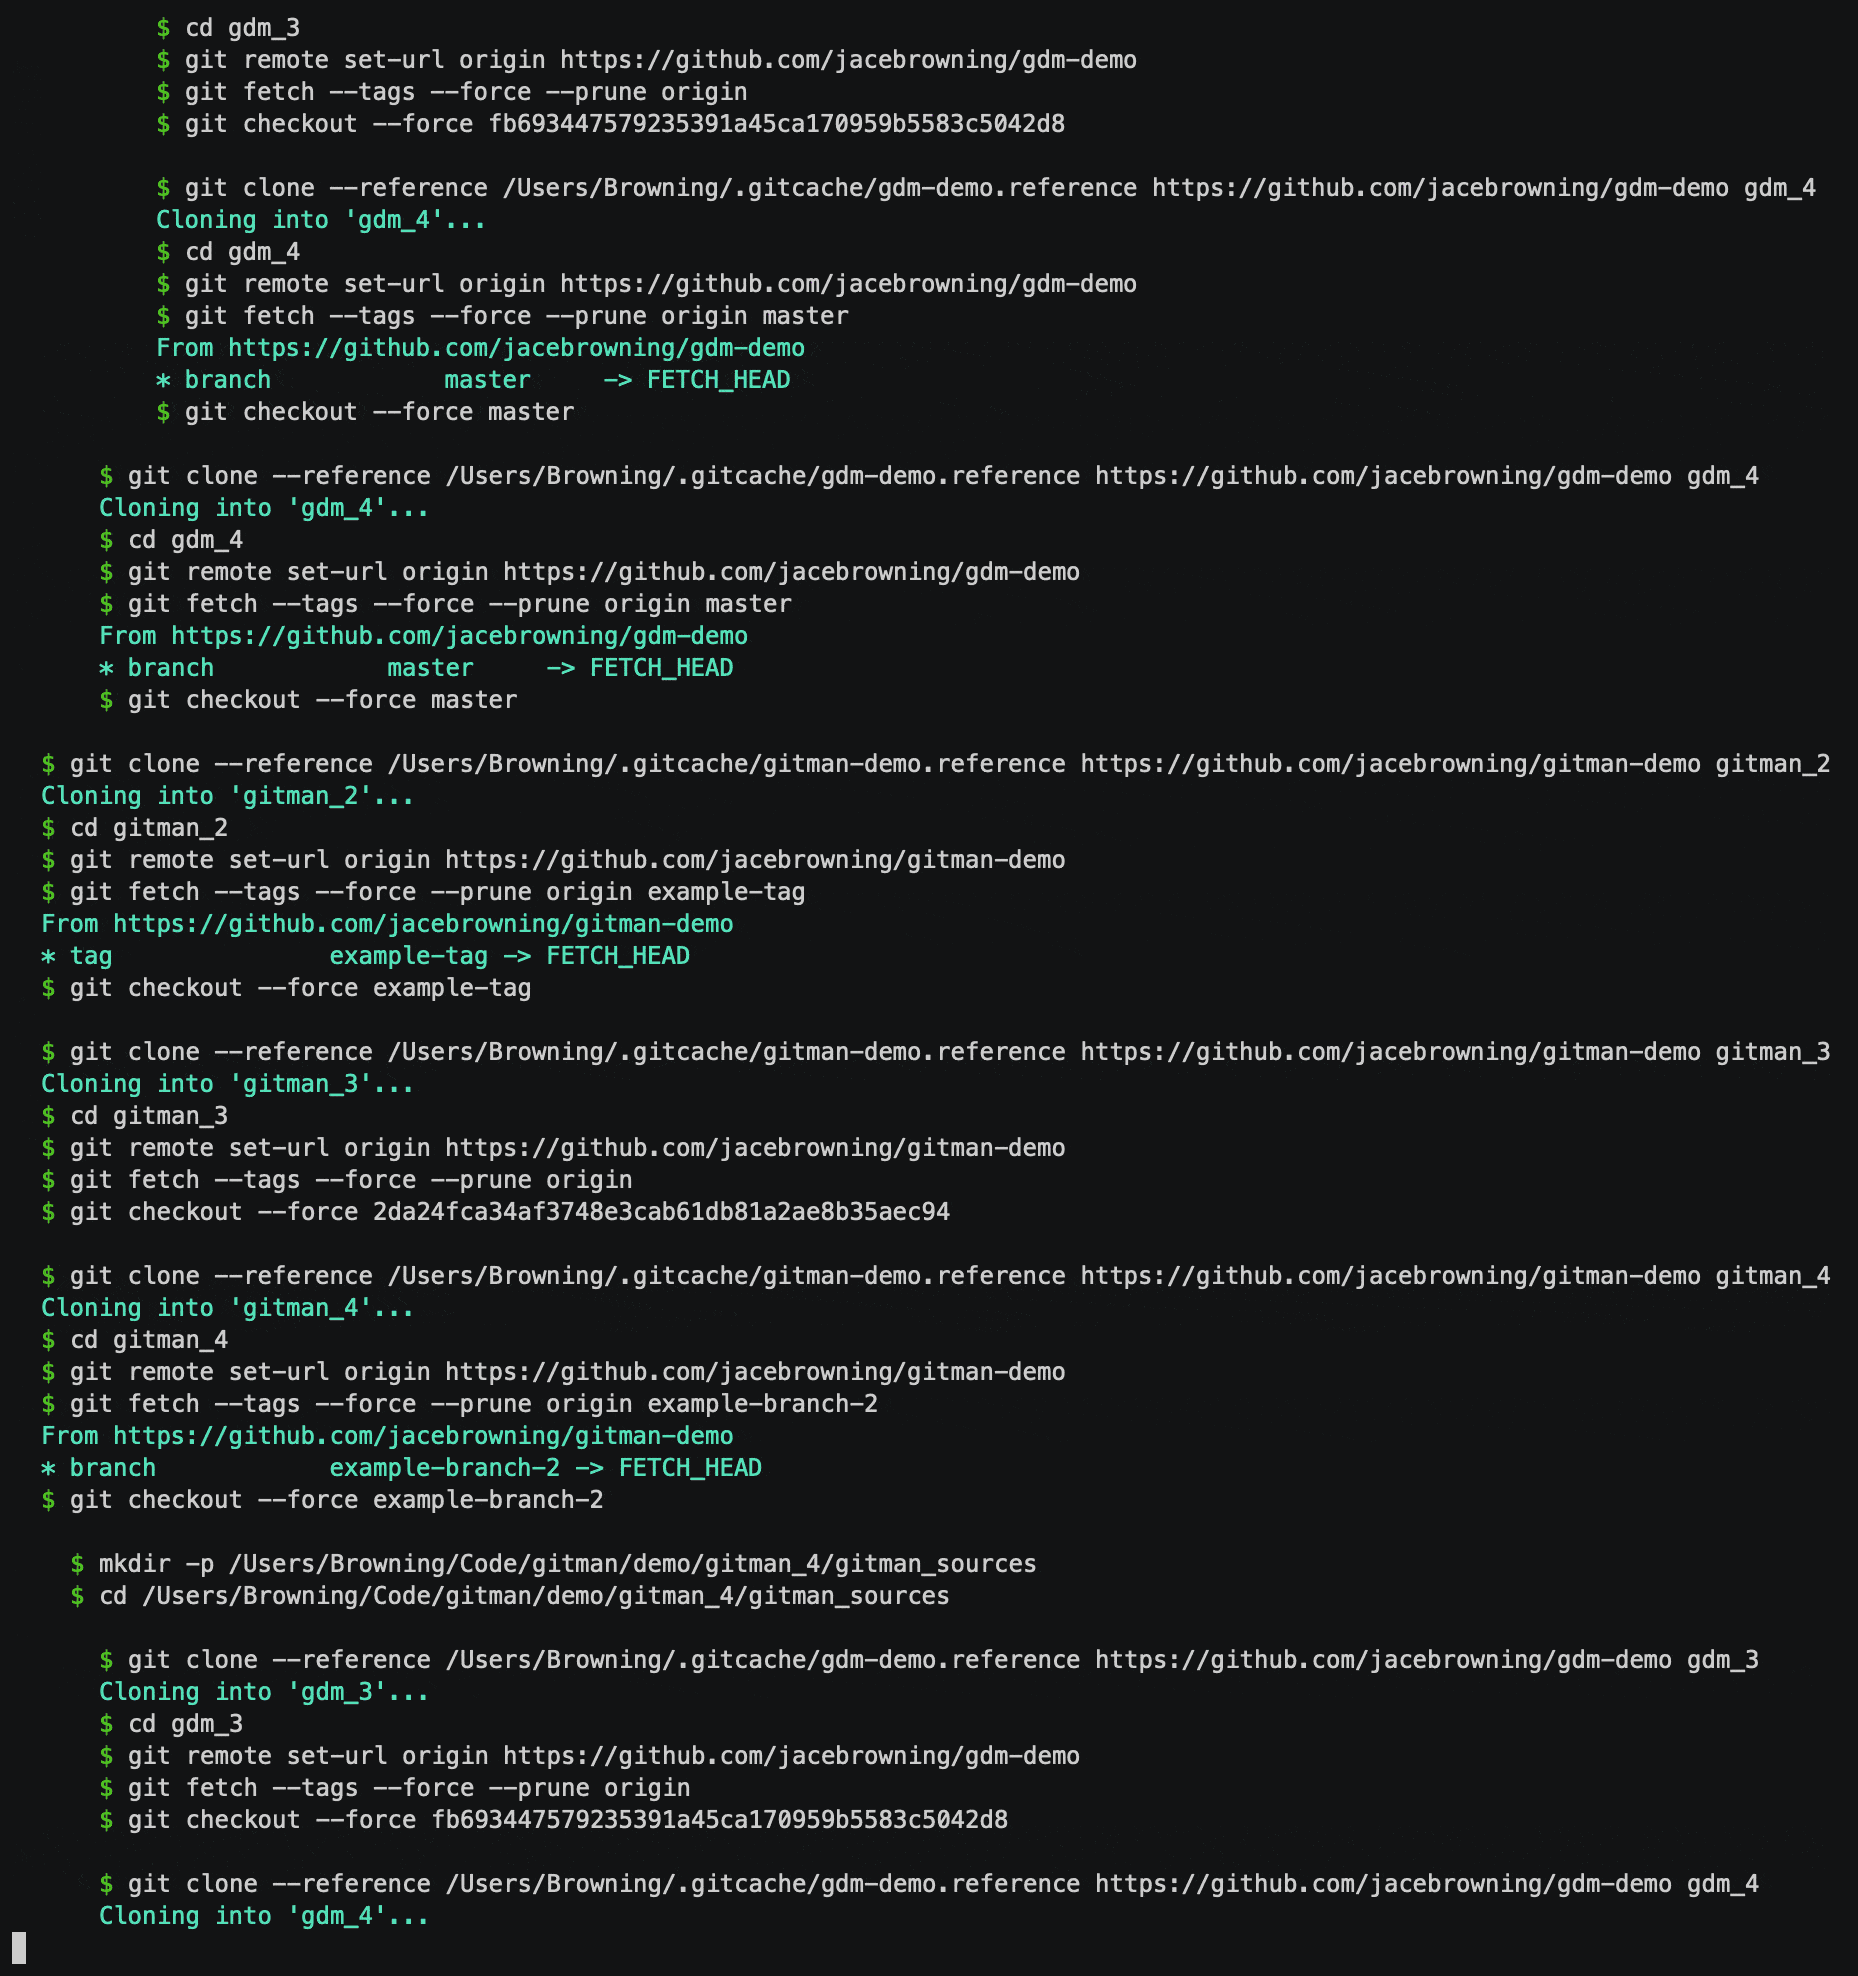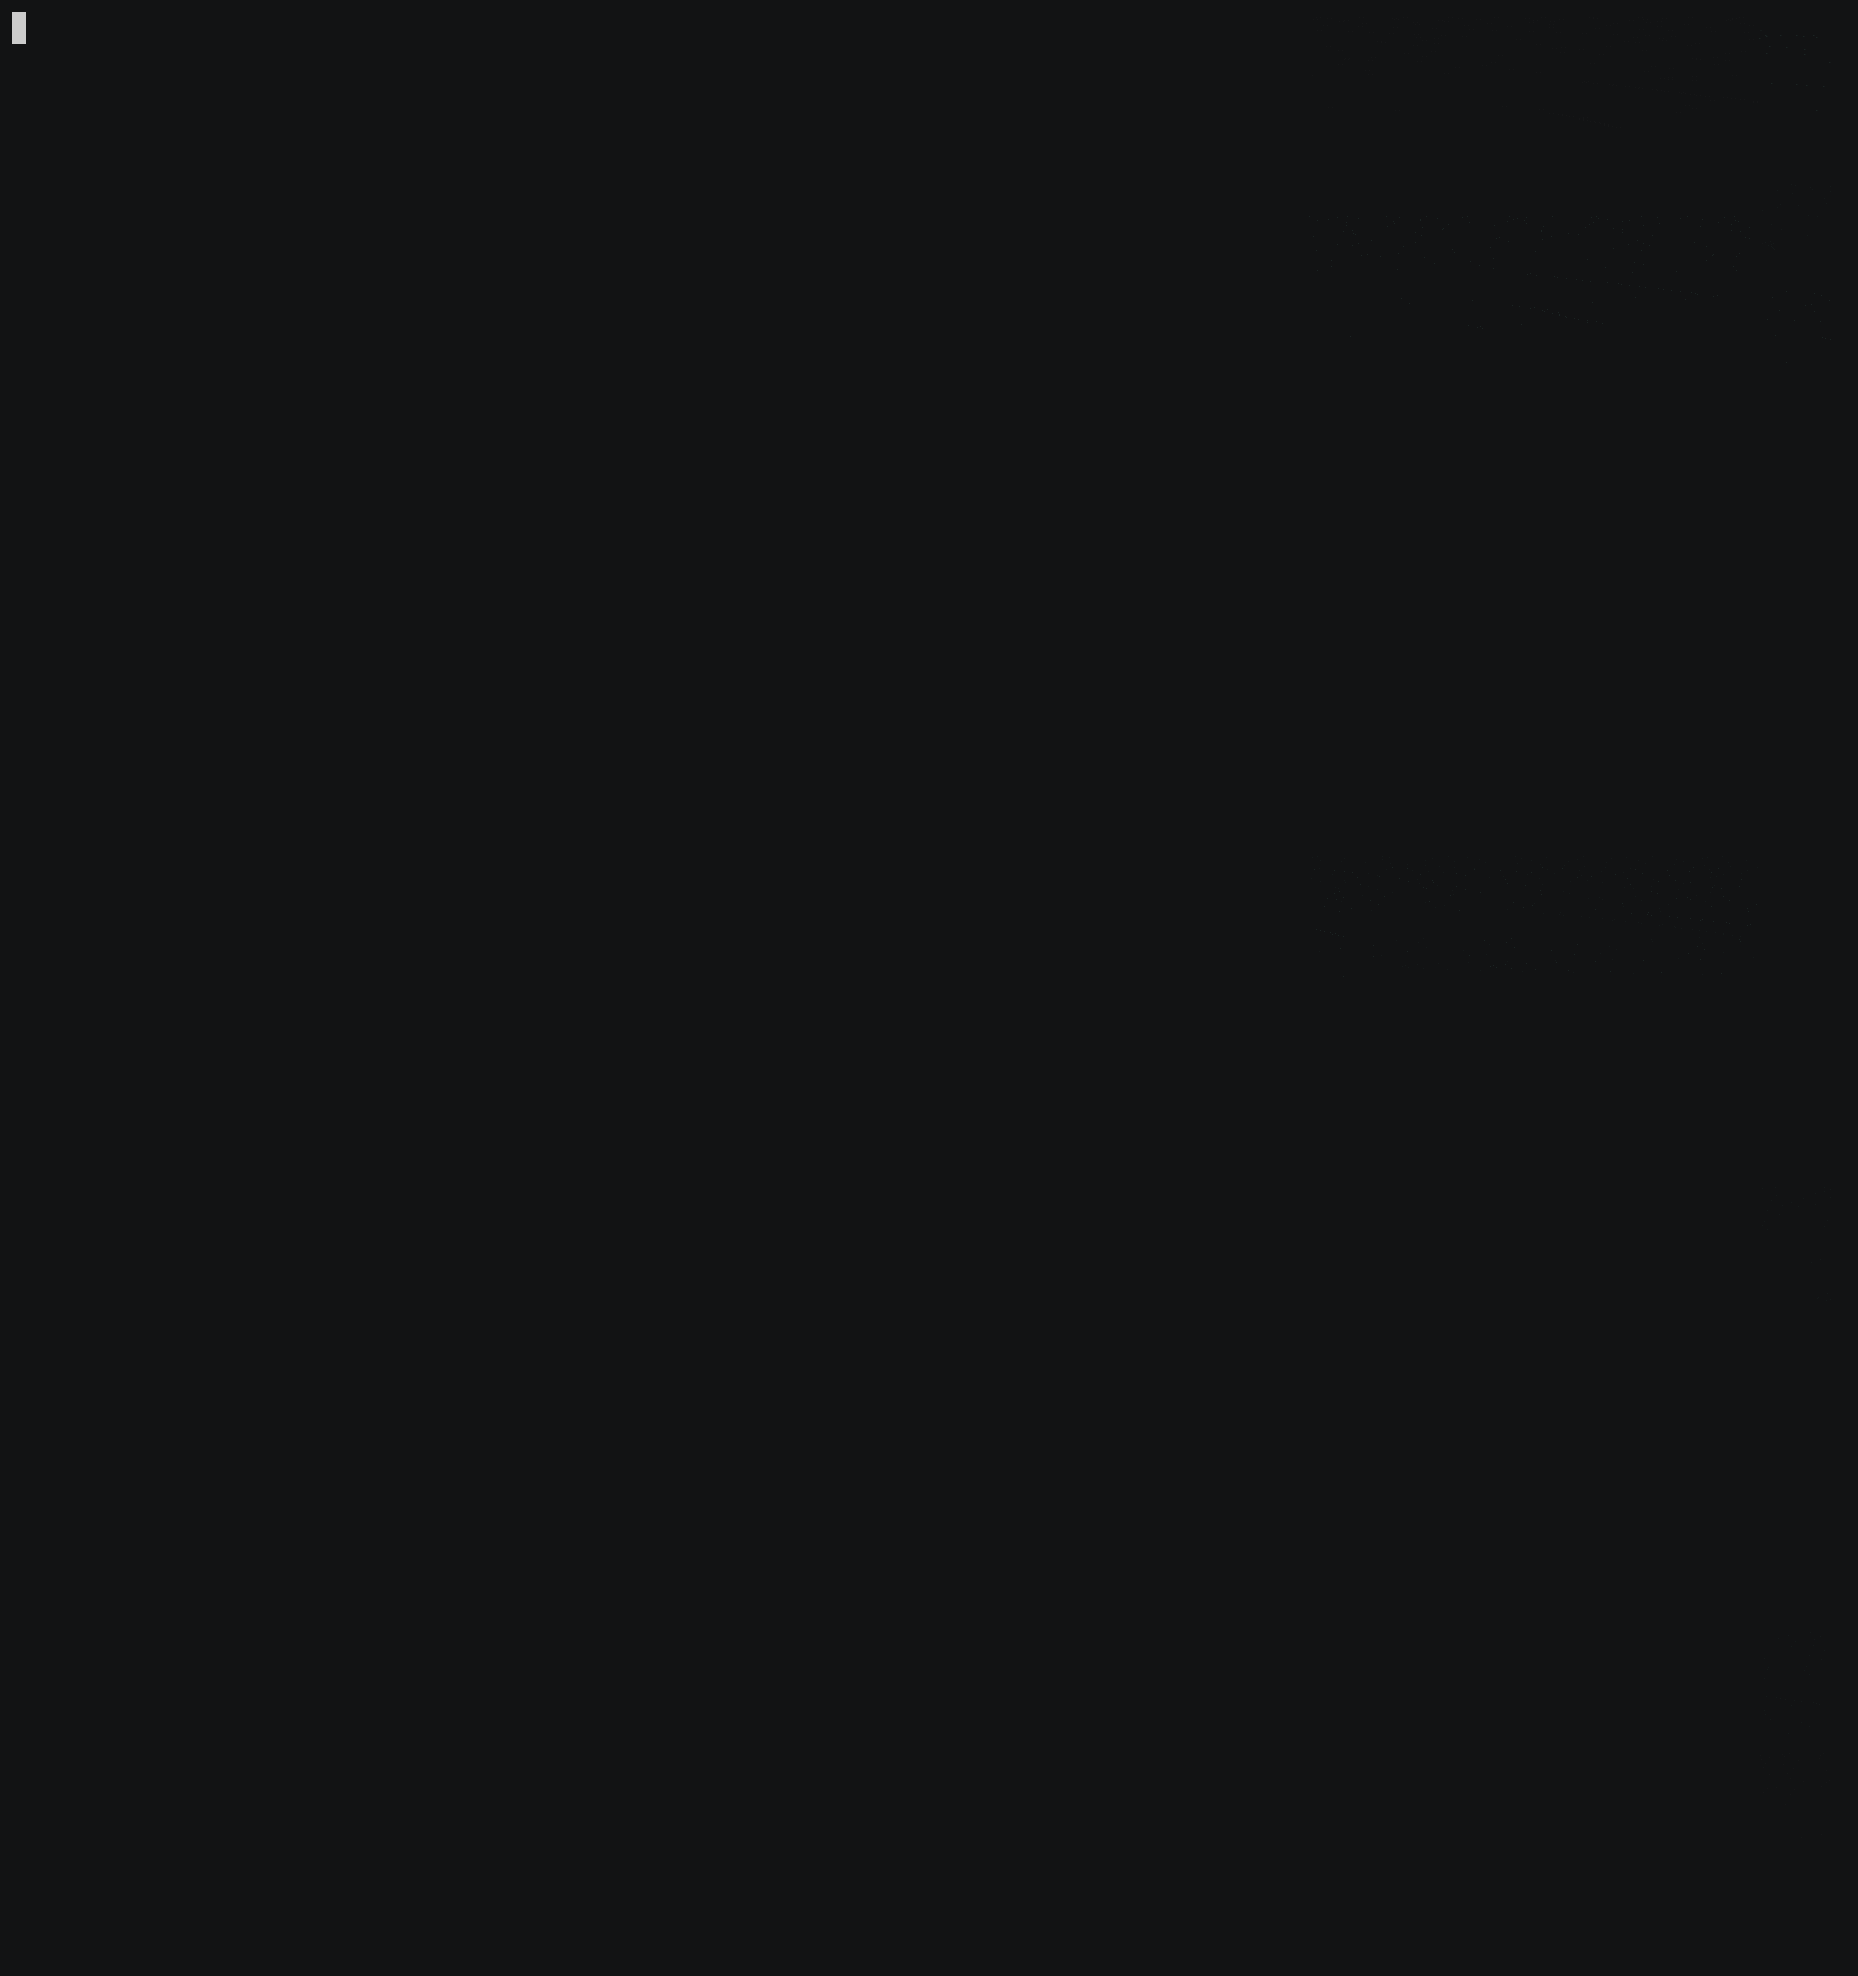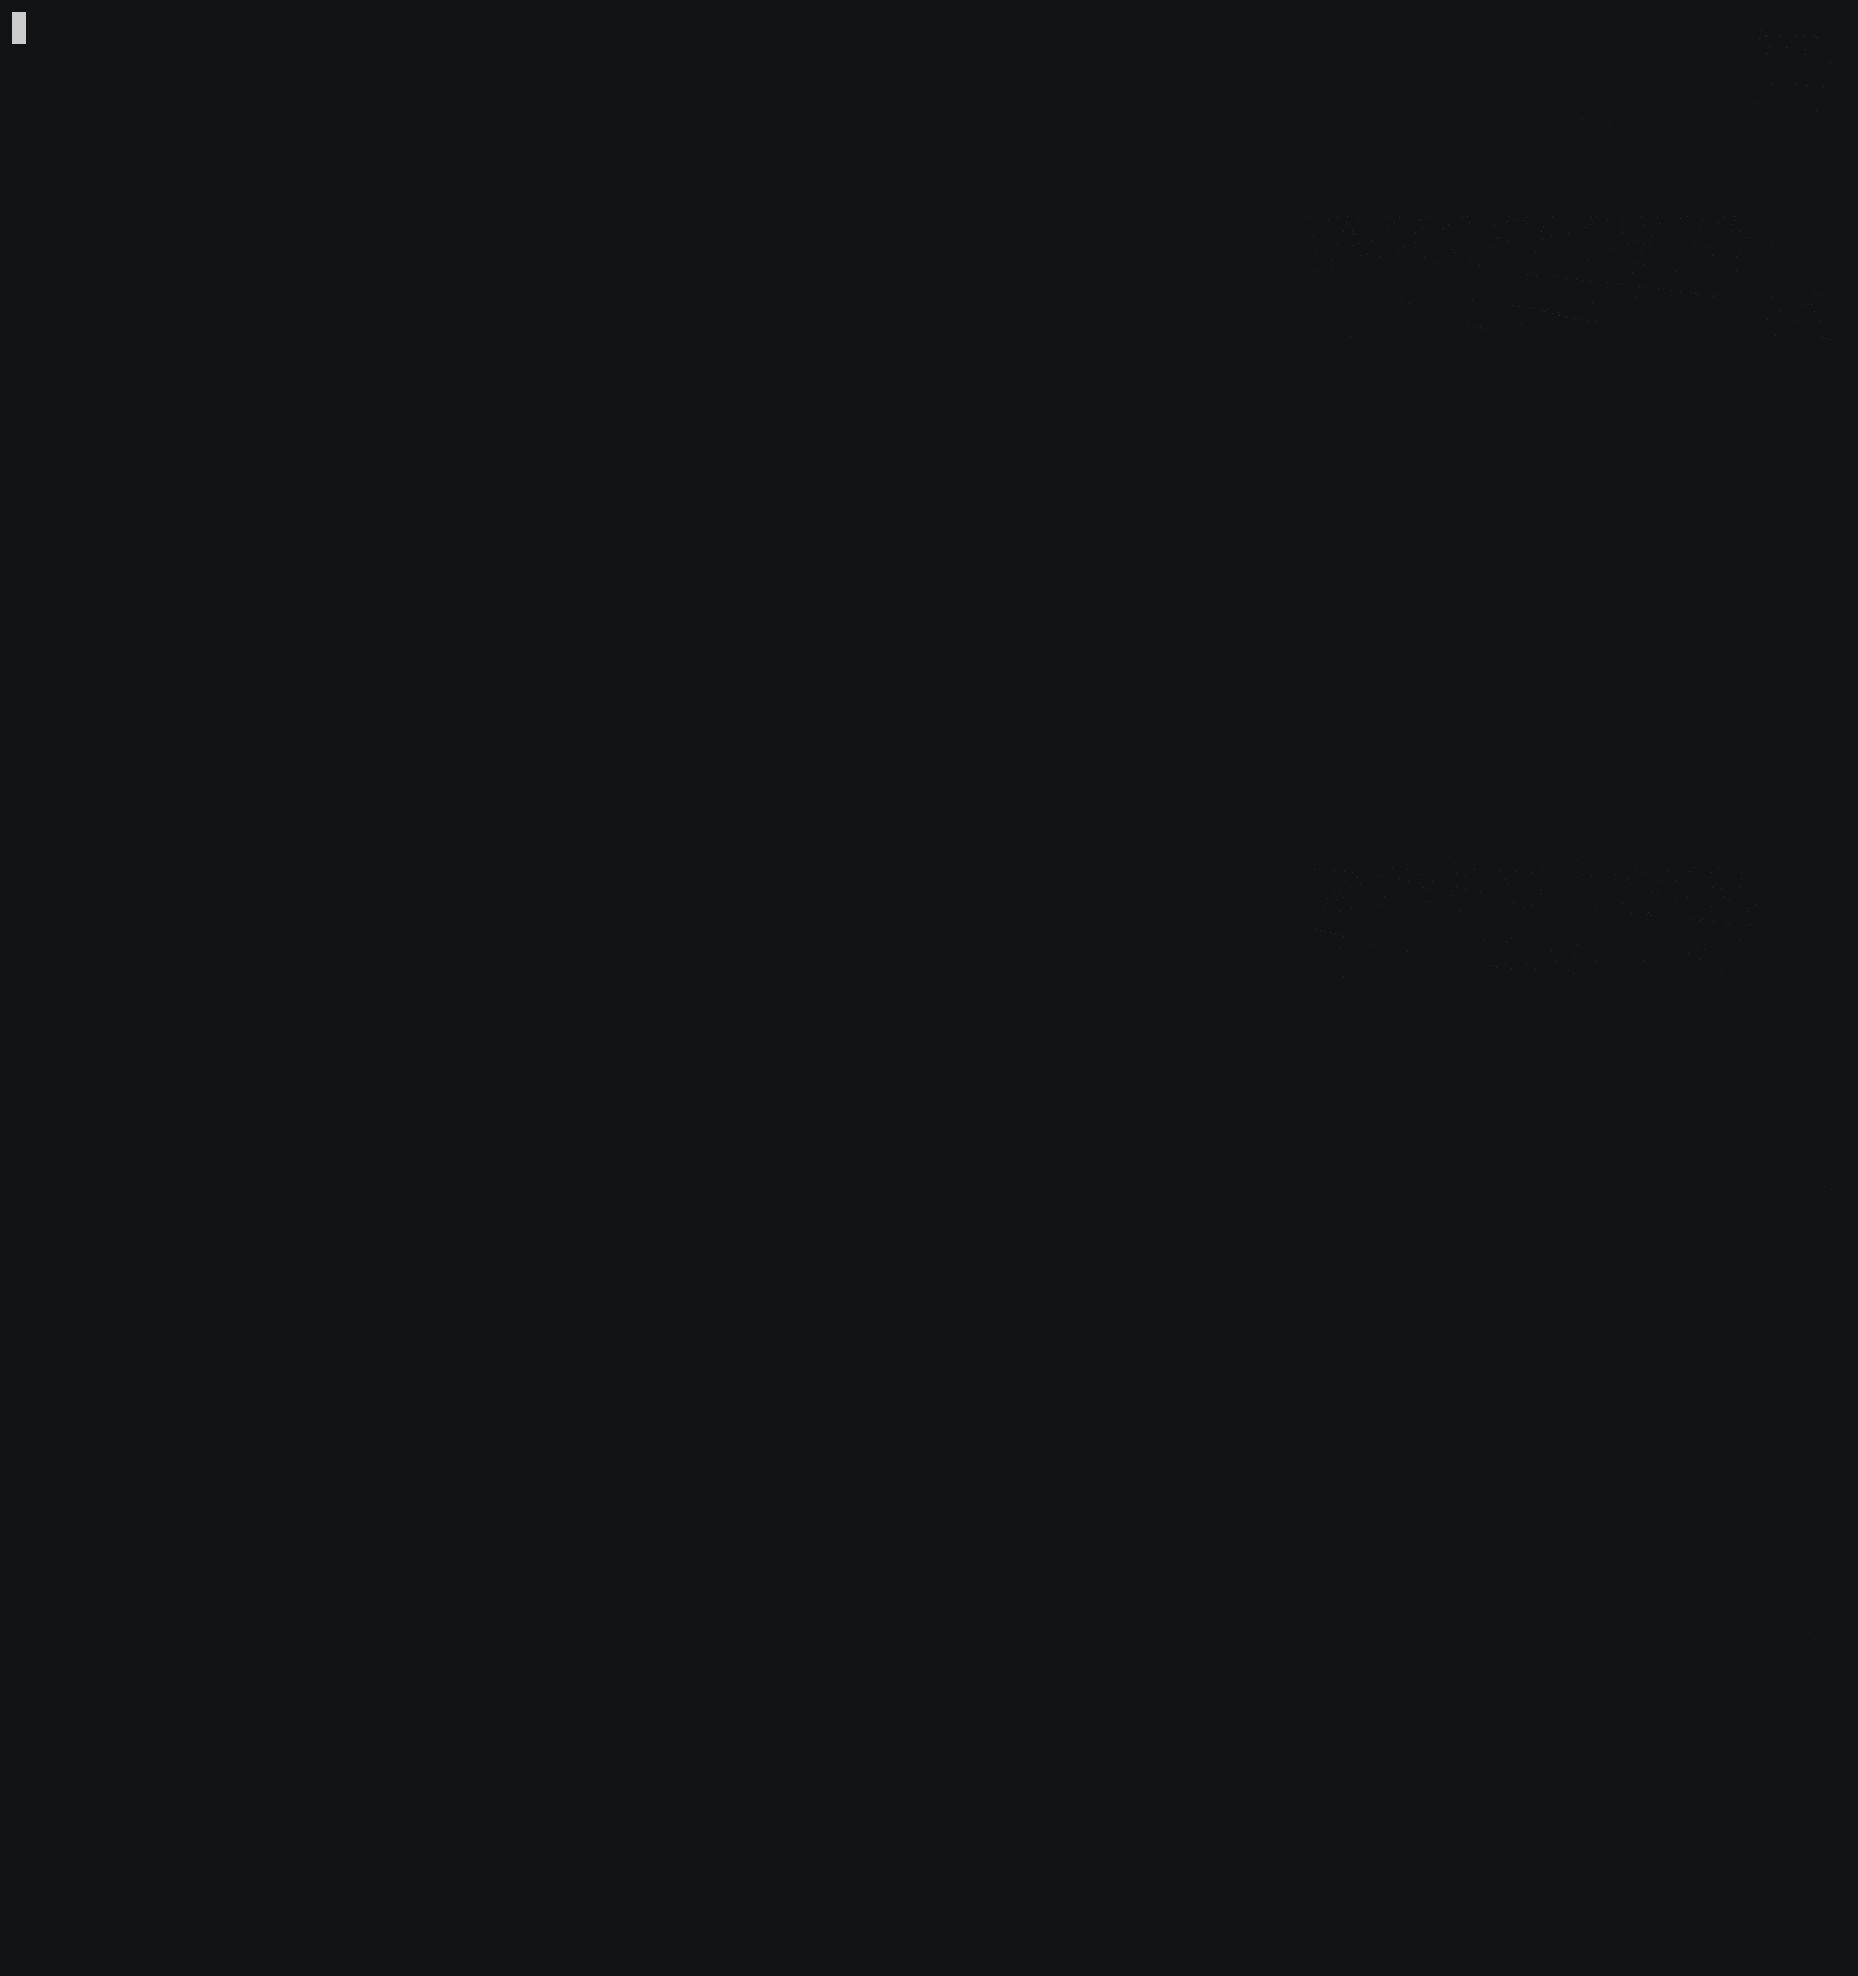
$ gitman update
which will essentially:
- Create a working tree at
<root>/<location>/<name> - Fetch from
repoand checkout the specifiedrev - Symbolically link each
<location>/<name>from<root>/<link>(if specified) - Repeat for all nested working trees containing a config file
- Record the actual commit SHAs that were checked out (with
--lockoption) - Run optional post-install scripts for each dependency
where rev can be:
- all or part of a commit SHA:
123def - a tag:
v1.0 - a branch:
main - a
rev-parsedate:'main@{2015-06-18 10:30:59}'
Alternatively, get the latest versions of specific dependencies:
$ gitman update framework
or named groups:
$ gitman update resources
Restoring Previous Versions
Display the versions that are currently installed:
$ gitman list
Reinstall these specific versions at a later time:
$ gitman install
Deleting Dependencies
Remove all installed dependencies:
$ gitman uninstall
Resources
1 maintainer

Metadata
1 maintainer
Release files for gitman 3.9
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| gitman-3.9.tar.gz | 32.5 kB | Without provenance | Details for gitman-3.9.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| gitman-3.9-py3-none-any.whl | Python 3 | none | any | Details for gitman-3.9-py3-none-any.whl |
Total release size: 74.3 kB
Release files / gitman-3.9.tar.gz
| Download URL | gitman-3.9.tar.gz |
|---|---|
| Size | 32.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
454771624ecaa2d372d093926ea78e0f514d653a5959c3d41730f8a925fd1ee3
|
|
BLAKE2b-256 checksum How to use checksums |
36c230def0e25ee6fcfa38a40bedd8642ad16a81e48bb1ee4c26526d2fa37393
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.5.1 CPython/3.11.17 Darwin/24.6.0
|
Release files / gitman-3.9-py3-none-any.whl
| Download URL | gitman-3.9-py3-none-any.whl |
|---|---|
| Size | 41.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
230bff931da0df5e21bb94c9156523e97e2939a34530ee27f5ebb1cc7e822c34
|
|
BLAKE2b-256 checksum How to use checksums |
7194f32a9f331f79abbd6bd62196ca2c6d504f92418be56db86aeceb460e0275
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
poetry/2.5.1 CPython/3.11.17 Darwin/24.6.0
|
Security for gitman 3.9
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














