
nonebot_plugin_bind

适配支持
- onebotv11
- telegram
- discord
- kook(开黑啦)
- villa(大别野)
- 飞书
使用说明
用户使用说明
| 命令 | 限制 | 含义 |
|---|---|---|
| 'bind' | 群聊或私聊 | 将其他通用账户绑定至当前通用账户 |
| 'bindinfo' | 仅私聊 | 查看当前通用账户的平台账户绑定信息 |
| 'rebind' | 仅私聊 | 取消本平台账户和通用账户的绑定,并形成一个新的通用账户 |
| 'bind -group' | 群聊或私聊 | 将其他通用群组绑定至当前通用群组 |
| 'bindinfo -group' | 仅私聊 | 查看当前通用群组的平台群组绑定信息 |
| 'rebind -group' | 仅私聊 | 取消本平台群组和通用尊祖的绑定,并形成一个新的通用群组 |
配置项
请使用Webui 进行配置,默认端口为8666,ip为主机对应ip,默认本地地址为http: //127.0.0.1:8666
| 配置名 | 默认 | 含义 |
|---|---|---|
| bind_superuser | [] | bind的superuser,用以管理群组绑定,注意填写的值应该是通过bindinfo查询出的id,而不是你的某个社交平台的账户 |
| bind_group_admin | False | 是否允许某社交平台的群组的管理员直接管理其群组绑定,不管他是否是bind_superuser |
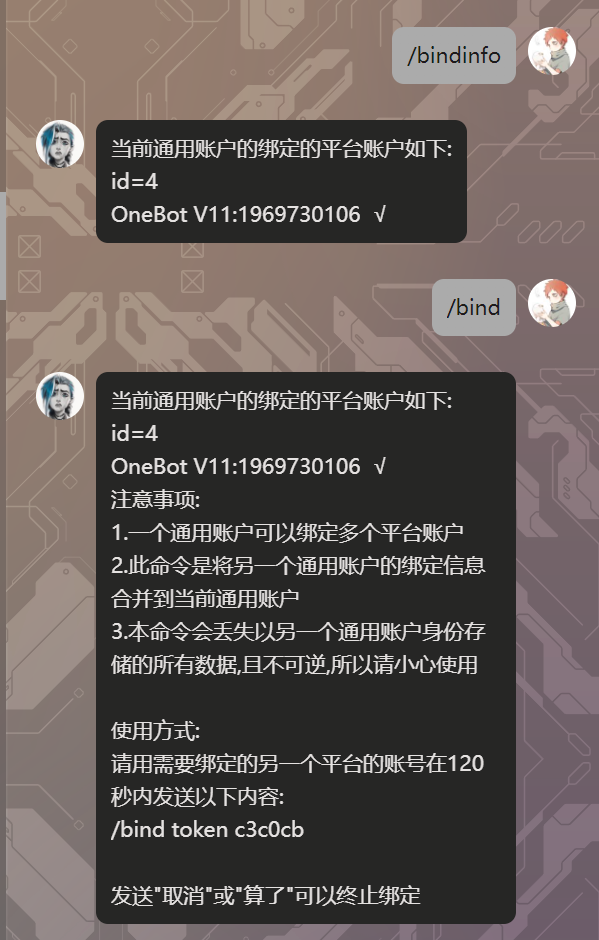
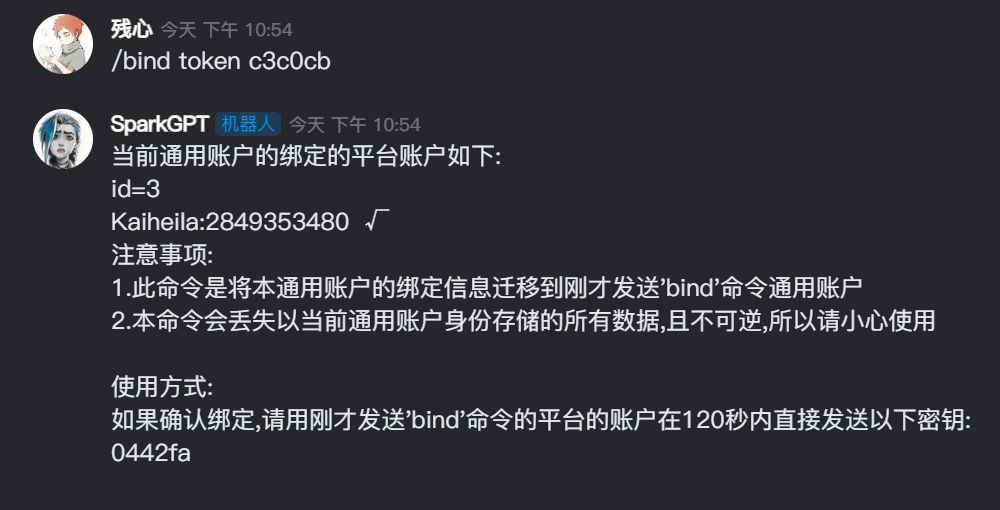
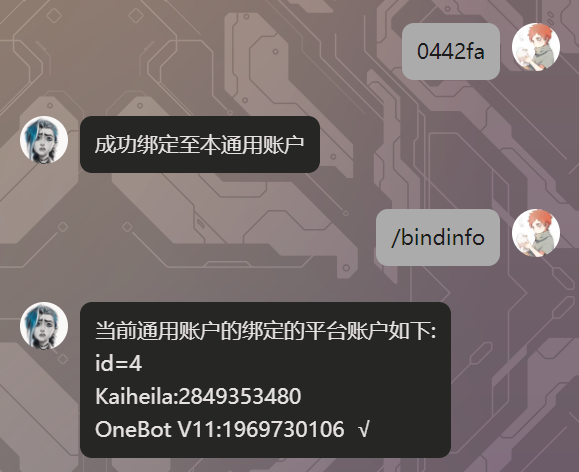
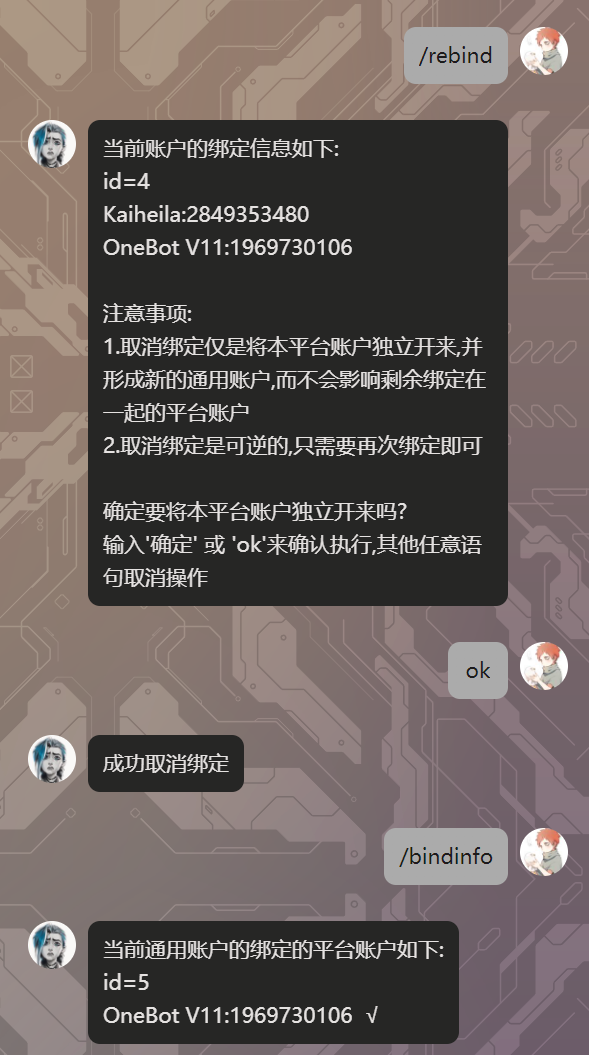
具体使用请看下图流程示例(群聊绑定同理)
(如果是在群聊中发起的绑定,不会显示下面的绑定信息,只会显示其他内容)
开发者说明
主要提供两个依赖注入
- GetUser:返回一个User实例,其属性id为一个通用账户的唯一标识,其属性platform_users中包含绑定的所有平台账户的信息
- GetGroup:返回一个Group实例,其属性id为一个通用群组的唯一标识,其属性platform_groups中包含所有绑定的平台群组的信息( 其中groupid是对应平台群组的id)(如果不想在匹配非群组消息时跳过matcher,请使用Optional类型注释)
示例代码如下
from typing import Annotated

from nonebot import require

require('nonebot_plugin_bind')

from nonebot_plugin_bind import GetUser, GetGroup, GetGroupId, User, Group

# 此处省略了部分import

bind_info = on_alconna(Alconna(Command_Start, "bindinfo", Option("-group")))


@bind_info.assign("$main")
async def bind_info_(
        event: Event, bot: Bot, matcher: Matcher, user: Annotated[User, GetUser()]
):
    user_str = "\n".join(
        pg + "  √" if event.get_user_id() in pg else pg for pg in str(user).split("\n")
    )
    if _is_private_(event, bot):
        await matcher.finish(f"当前通用账户的绑定的平台账户如下:\n{str(user_str)}")
    else:
        await matcher.finish("账户绑定信息只能在私聊中查看")


@bind_info.assign("group")
async def bind_info_group(
        matcher: Matcher,
        group: Optional[Group] = GetGroup(),
        groupid: Optional[str] = GetGroupId(),
):
    # 如果在私聊中发送此命令,得到的group会是None,groupid也是如此
    if group is None:
        await matcher.finish("本命令只能在各平台的群聊中使用,私聊中无法使用")
    group_str = "\n".join(
        pg + "  √" if groupid in pg else pg for pg in str(group).split("\n")
    )
    await matcher.send(f"当前通用群组的绑定的平台群组如下:\n{group_str}")


_bind_ = on_alconna(
    Alconna(Command_Start, "bind", Option("token", Args["token_value", str]))
)
1 maintainer

Metadata
1 maintainer
Release files for nonebot-plugin-bind 0.2.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| nonebot_plugin_bind-0.2.2.tar.gz | 10.0 kB | Without provenance | Details for nonebot_plugin_bind-0.2.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| nonebot_plugin_bind-0.2.2-py3-none-any.whl | Python 3 | none | any | Details for nonebot_plugin_bind-0.2.2-py3-none-any.whl |
Total release size: 22.9 kB
Release files / nonebot_plugin_bind-0.2.2.tar.gz
| Download URL | nonebot_plugin_bind-0.2.2.tar.gz |
|---|---|
| Size | 10.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1ae669e0814041d9955eb754a941b998e4b2cbd63d61b00fa2cfb76d321049ca
|
|
BLAKE2b-256 checksum How to use checksums |
6dc9b94d0fde50e3fc8c5e7ee24f85b3ff0942a41fcc7c46f72d2e24540c10f9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.5
|
Release files / nonebot_plugin_bind-0.2.2-py3-none-any.whl
| Download URL | nonebot_plugin_bind-0.2.2-py3-none-any.whl |
|---|---|
| Size | 12.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
56013e280a5441a82ac850998cb25b8c2a604d0829e29363a0df54e5b6367bee
|
|
BLAKE2b-256 checksum How to use checksums |
b954049f3c9cdab2814ad2f6a70b312e81bf92a4fcd2ef5734d7cfb324b78bbe
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.5
|
Security for nonebot-plugin-bind 0.2.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














