
Pycycle: Find and fix circular imports in python projects




Pycycle is an experimental project that aims to help python developers fix their circular dependencies problems.
ImportError: Cannot import name X is a python exception that is related to the circular imports, but the exception tells nothing about where or what.
This tool automatically analyzes the imports of your projects, and looks for imports that may cause a circular dependency problem.
Features
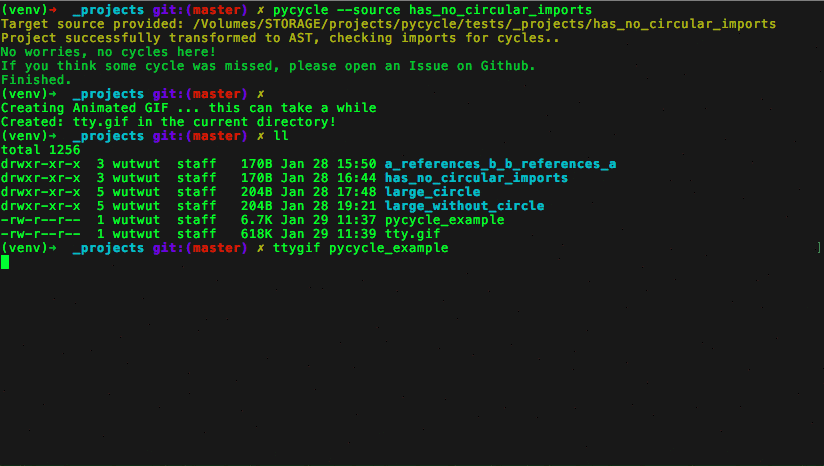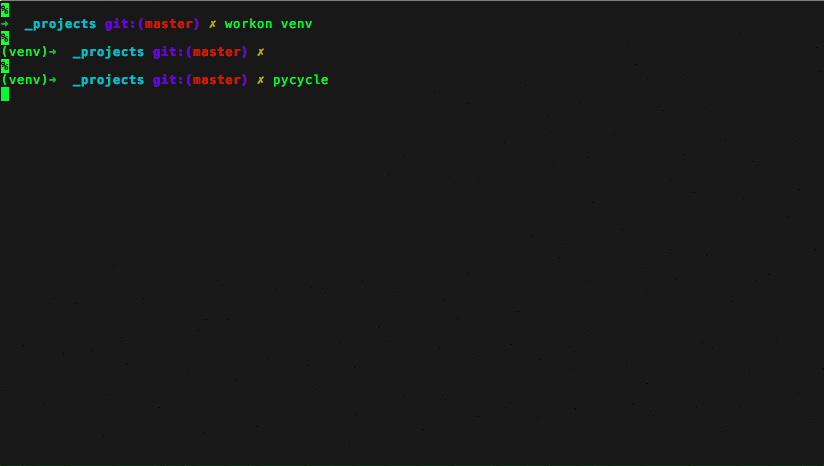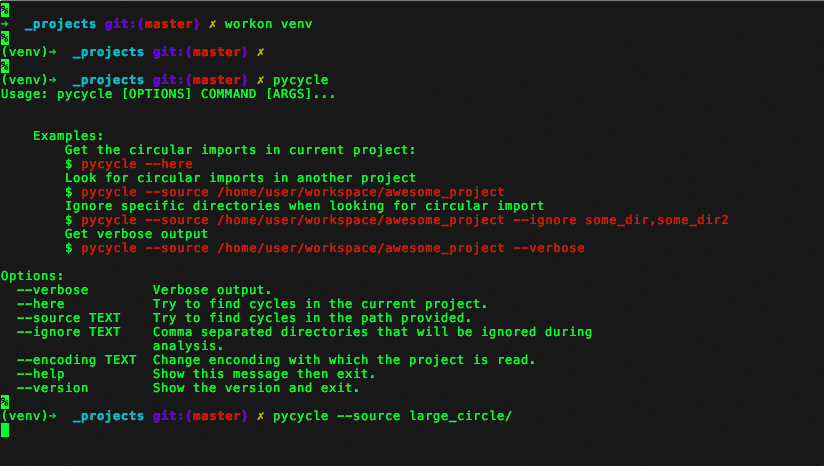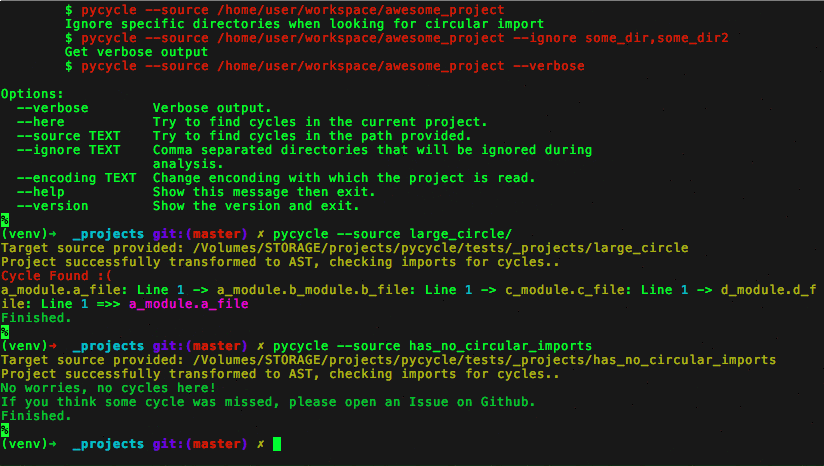
Shows you the whole chain of the circular imports.
Gives you lines of code where each import is, for you to easily find and fix the problem.
Visualizes your imports in a graph (Not Yet Implemented)
Usage
$ pycycle
Usage: pycycle [OPTIONS] COMMAND [ARGS]...


Examples:
    Get the circular imports in current project:
    $ pycycle --here
    Look for circular imports in another project
    $ pycycle --source /home/user/workspace/awesome_project
    Ignore specific directories when looking for circular import
    $ pycycle --source /home/user/workspace/awesome_project --ignore some_dir,some_dir2
    Get verbose output
    $ pycycle --source /home/user/workspace/awesome_project --verbose

Options:
  --verbose        Verbose output.
  --here           Try to find cycles in the current project.
  --source TEXT    Try to find cycles in the path provided.
  --ignore TEXT    Comma separated directories that will be ignored during
                   analysis.
  --encoding TEXT  Change enconding with which the project is read.
  --help           Show this message then exit.
  --version        Show the version and exit.
$ pycycle --here
Project successfully transformed to AST, checking imports for cycles..
Cycle Found :(
a_module.a_file: Line 1 -> a_module.b_module.b_file: Line 1 -> c_module.c_file: Line 1 -> d_module.d_file: Line 1 =>> a_module.a_file
Finished.
$ pycycle --source /Users/vkravcenko/workspace/awesome_project
Target source provided:/Users/vkravcenko/workspace/awesome_project
Project successfully transformed to AST, checking imports for cycles..
No worries, no cycles here!
If you think some cycle was missed, please open an Issue on Github.
Finished.
Installation
$ pip install pycycle
1 maintainer

Metadata
1 maintainer
Release files for pycycle 0.0.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| pycycle-0.0.8.tar.gz | 5.8 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| pycycle-0.0.8-py2-none-any.whl | Python 2 | none | any | Details |
Total release size: 14.5 kB
Release files / pycycle-0.0.8.tar.gz
| Download URL | pycycle-0.0.8.tar.gz |
|---|---|
| Size | 5.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fdcde6eef1fded7113f211255971dcc93a740cc6fa57a24ab7c9c3c681bf4351
|
|
BLAKE2b-256 checksum How to use checksums |
99c90a6e09b0d7d0fbc339191b3b37bfab92be84513700418c61a2adbfd3ae2d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
Release files / pycycle-0.0.8-py2-none-any.whl
| Download URL | pycycle-0.0.8-py2-none-any.whl |
|---|---|
| Size | 8.7 kB |
| Tags | Python 2 |
|
SHA-256 checksum How to use checksums |
37af51d31861449ad05db4d0f79de26e9fdf2519aca8866b57d03af3a8fccf36
|
|
BLAKE2b-256 checksum How to use checksums |
27f92dbaf7797277db3901086babde14d7a9673ed6b1925193ce4d2a15699ff8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
Security for pycycle 0.0.8
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














