
pytest-ipynb
Plugin for pytest to run IPython notebooks as unit tests, relies on runipy to interface with the Notebook.
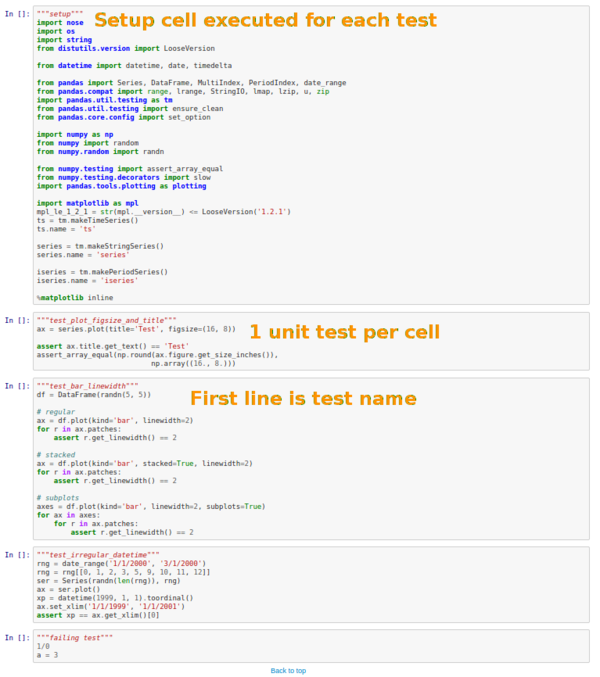
Define unit tests in IPython notebook cells (see example on nbviewer):
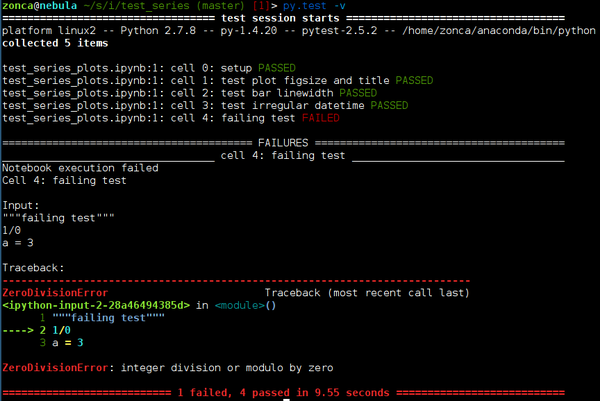
Run py.test to execute them:
Example
See the examples/ folder or a preview on nbviewer.
Features
Discover files named test*.ipynb
Run each cell of the notebook as a unit test (just use assert)
First line of each cell is the test name, either as docstring, comment or function name
A cell named fixture* or setup* is run before each of the following unit tests as a fixture
Add SKIPCI to a cell description to skip the test on Travis-CI (checks if the CI environment variable is defined)
IPython notebook kernel is restarted after each test
Each notebook is executed in the folder where the .ipynb file is located
Requirements
Python 2.7+, Python 3.2+
pytest
IPython Notebook 2.0+
Install
$ pip install pytest-ipynb
Credits
Thomas Kluyver for help on the IPython mailing list
1 maintainer

Metadata
1 maintainer
Release files for pytest-ipynb 1.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| pytest-ipynb-1.1.1.tar.gz | 3.7 kB | Without provenance | Details for pytest-ipynb-1.1.1.tar.gz |
Release files / pytest-ipynb-1.1.1.tar.gz
| Download URL | pytest-ipynb-1.1.1.tar.gz |
|---|---|
| Size | 3.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
fca7ab0f75475cadcf0f6c0340b60be14b0174fd79a779b9c3865440ecc32183
|
|
BLAKE2b-256 checksum How to use checksums |
3659c37eb45b309a3bd7ce63871e03a291197a1dde53c4acfc413fb2b04c7a82
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.11.0 pkginfo/1.4.2 requests/2.18.4 setuptools/38.5.1 requests-toolbelt/0.8.0 tqdm/4.25.0 CPython/3.6.0
|
Security for pytest-ipynb 1.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














