
sshmenu
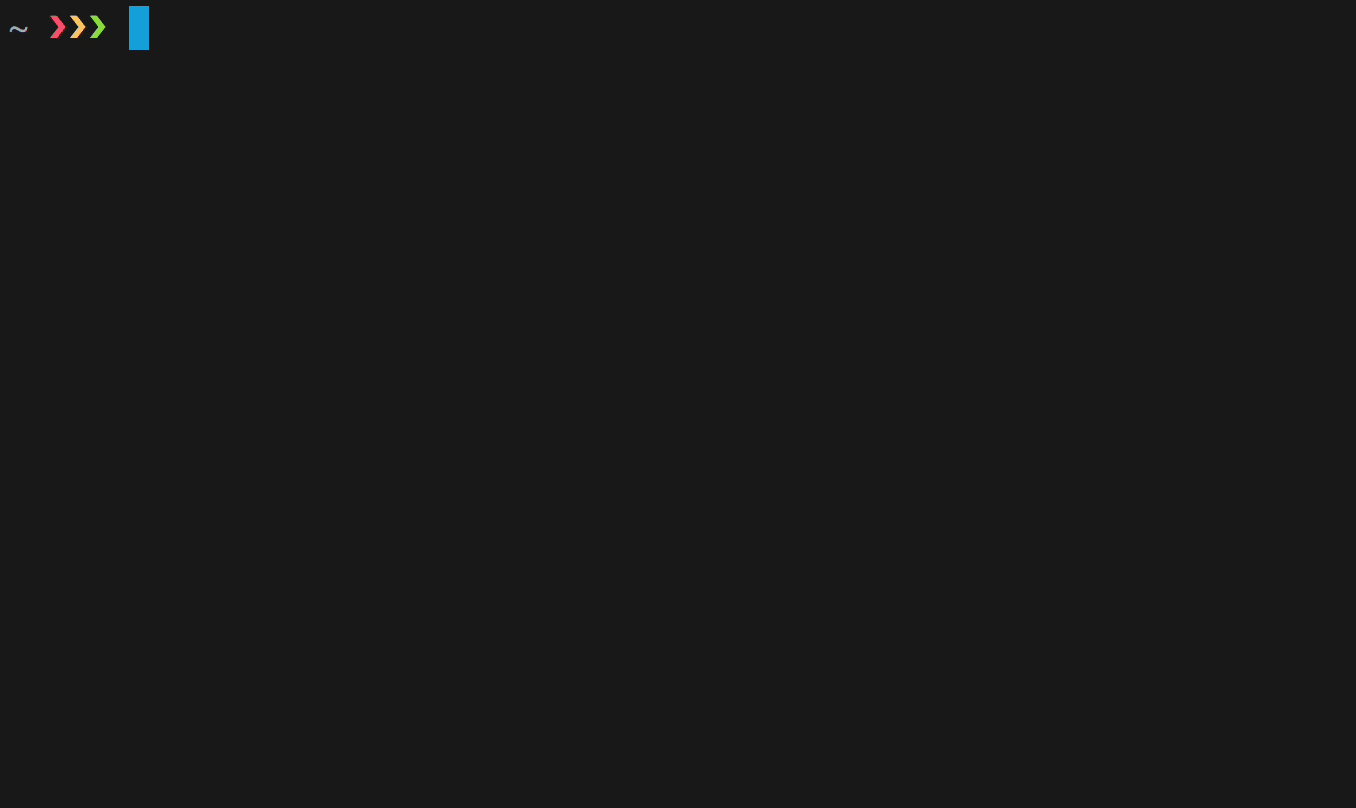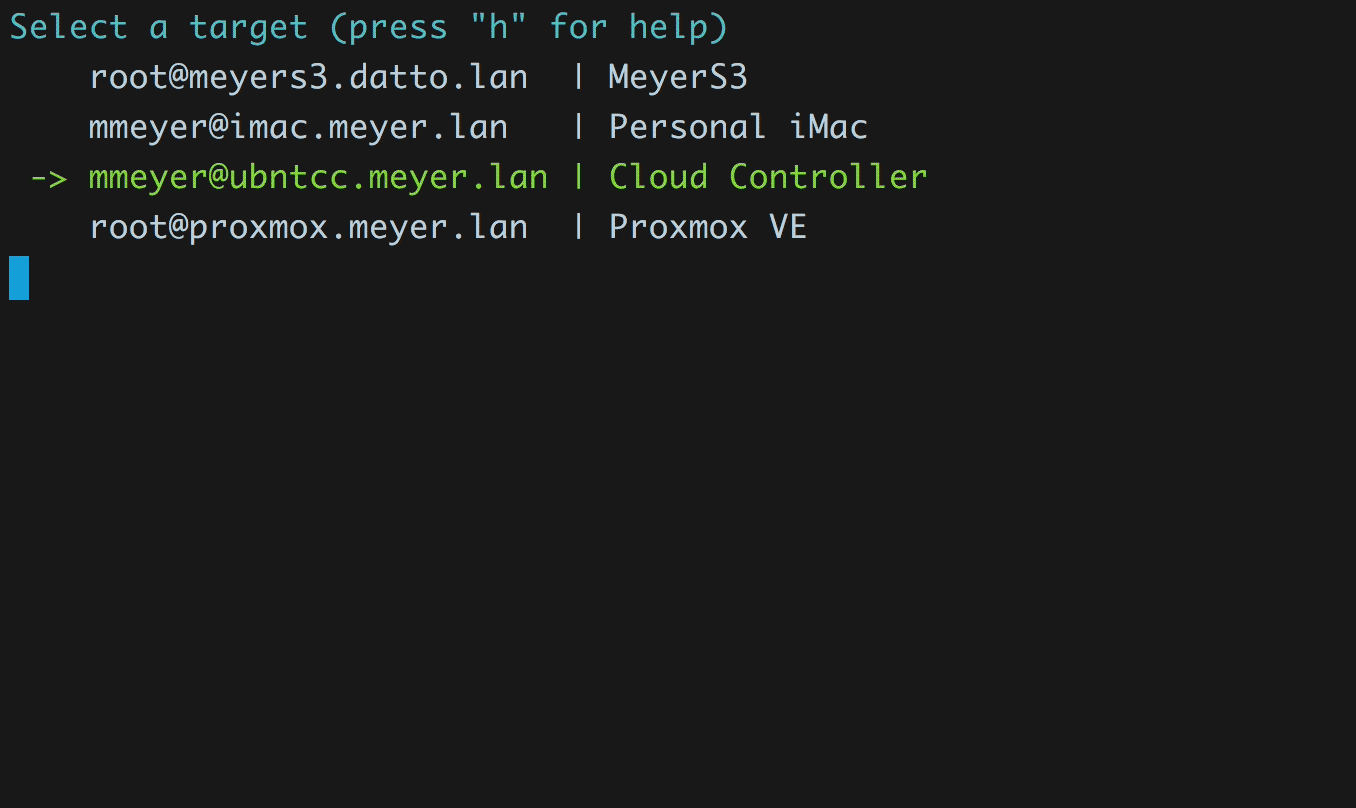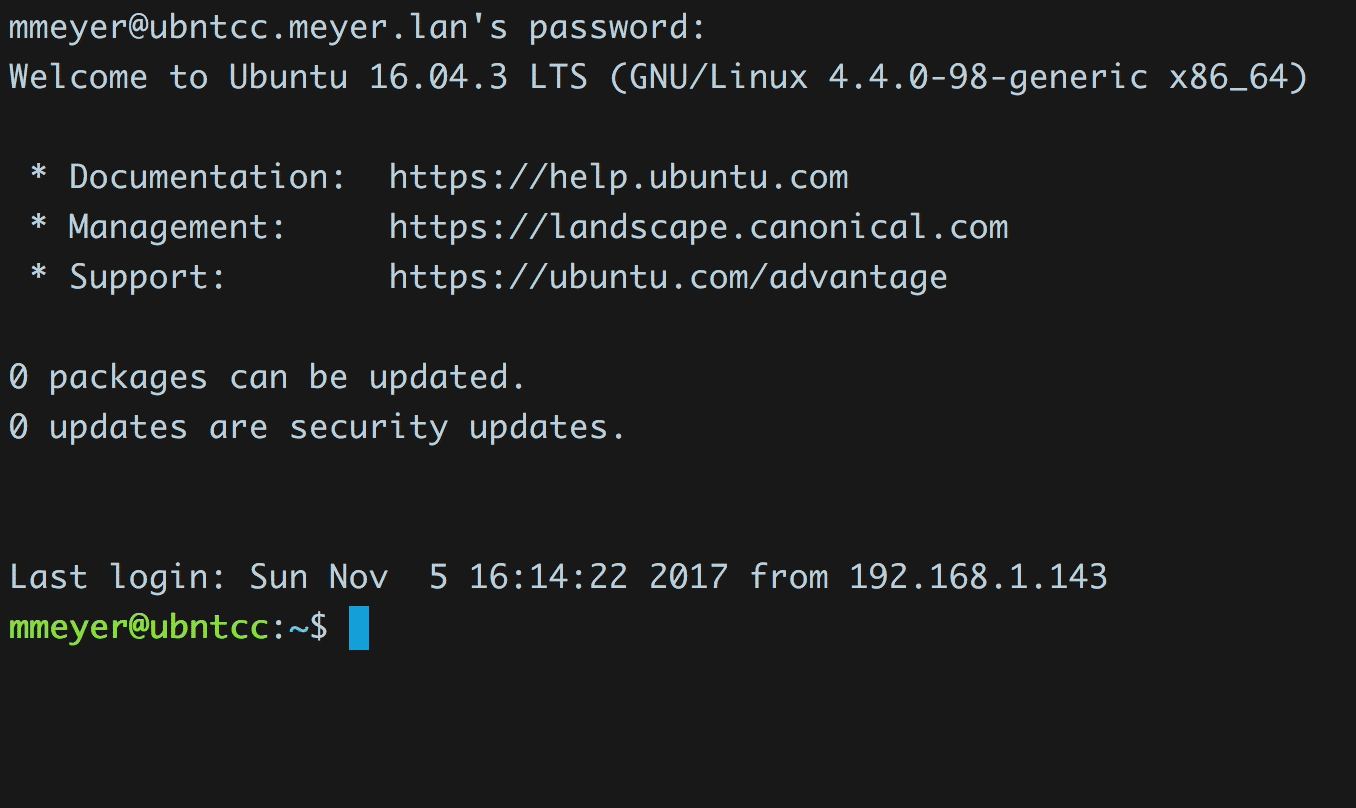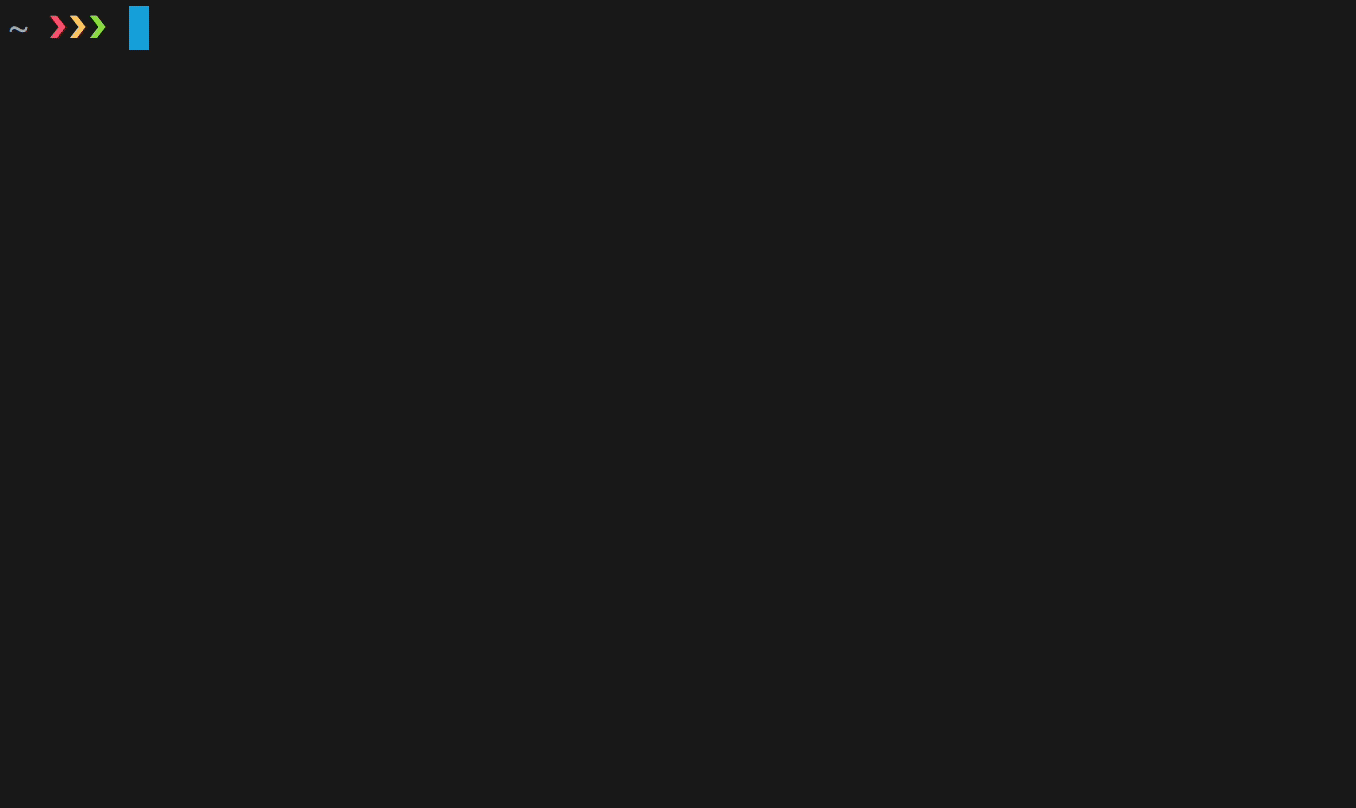
sshmenu is a simple tool for connecting to remote hosts via ssh. Great if you have trouble remembering ip addresses, hostnames, or usernames.
This tool works by using Python’s os.execvp(...), which will replace the current process (python) with ssh to create a seamless transition.
Quick Setup
Tested working on macOS High Sierra (10.13.1) and Ubuntu Trusty Tahr (14.04), Xenial Xerus (16.04)
macOS
brew install https://raw.githubusercontent.com/mmeyer724/sshmenu/master/sshmenu.rb
sshmenu
Linux
pip3 install sshmenu
sshmenu
Development
git clone https://github.com/mmeyer724/sshmenu.git
cd sshmenu
pip3 install -r requirements.txt
python3 -m sshmenu
Configuration
On first run an example configuration file will be created for you, along with the path. For reference, I’ve added this information here as well.
OS X
nano ~/Library/Application\ Support/sshmenu/config.jsonLinux
nano ~/.config/sshmenu/config.jsonDefault contents
{
    "targets": [
        {
            "host": "user@example-machine.local",
            "friendly": "This is an example target",
            "options": []
        },
        {
            "command": "mosh",
            "host": "user@example-machine.local",
            "friendly": "This is an example target using mosh",
            "options": []
        }
    ]
}
You can specify additional command line options (see man ssh) as follows:
{
    "targets": [
        {
            "host": "user@example-machine.local",
            "friendly": "An example target listening non-standard port and verbose flag",
            "options" : [
                "-p443",
                "-v"
            ]
        }
    ]
}
Todo
Automatically ask to place your ~/.ssh/id_rsa.pub into the remote host’s ~/.ssh/authorized_keys
1 maintainer

Metadata
1 maintainer
Release files for sshmenu 0.0.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| sshmenu-0.0.4-py2.py3-none-any.whl | Python 3, Python 2 | none | any | Details |
Security for sshmenu 0.0.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














