
0xarchive-backtest
A deterministic backtester for Hyperliquid perps, on 0xArchive data. The engine is Rust; strategies are Python. The same strategy, data and parameters give the same result hash on every machine, so a result is a claim anyone can check.
It is the engine behind 0xarchive-quant, a quant research skill for coding agents: hand Claude Code or Codex a wallet, an idea or a script, and it comes back with a verdict you can rerun.
Install
pip install "0xarchive-backtest[curated]"
Prebuilt for macOS, Linux and Windows; Python 3.12 or later (3.11 without [curated], the pinned
numpy, pandas and scipy that strategies may import).
Quickstart
Pull a minute dataset with your 0xArchive API key. Months are inclusive. Free keys read only the last 30 days, so this September window needs a paid plan:
export OXARCHIVE_API_KEY="0xa_your_api_key"
0xbt data pull --markets BTC,ETH,SOL,HYPE --from 2026-09 --to 2026-09
Write a strategy:
# momentum.py: each day, long the strongest of four perps over 3 days and short the weakest
import oxarchive_backtest as oxb
from oxarchive_backtest import x


def strategy(lookback="3d"):
    return oxb.Strategy(
        universe=["BTC", "ETH", "SOL", "HYPE"],
        clock=x.daily(),
        signal=lambda h: h.close.ret(lookback),
        weights=x.long_short(0.25),
    )
Backtest it, then put it through the gauntlet:
0xbt backtest momentum.py --start 2026-09-01 --end 2026-10-01
0xbt gauntlet momentum.py --start 2026-09-01 --end 2026-10-01 \
  -g lookback=1d,3d --card card.md
The backtest prints the return, Sharpe, drawdown, fees and funding, and a result hash. The gauntlet
runs every check on the best setting and reads the verdict off a fixed ladder. This one stops at
fails nulls: one in ten random books did as well, over the 5% bar, so a month of momentum on four
markets is not an edge.
The gauntlet
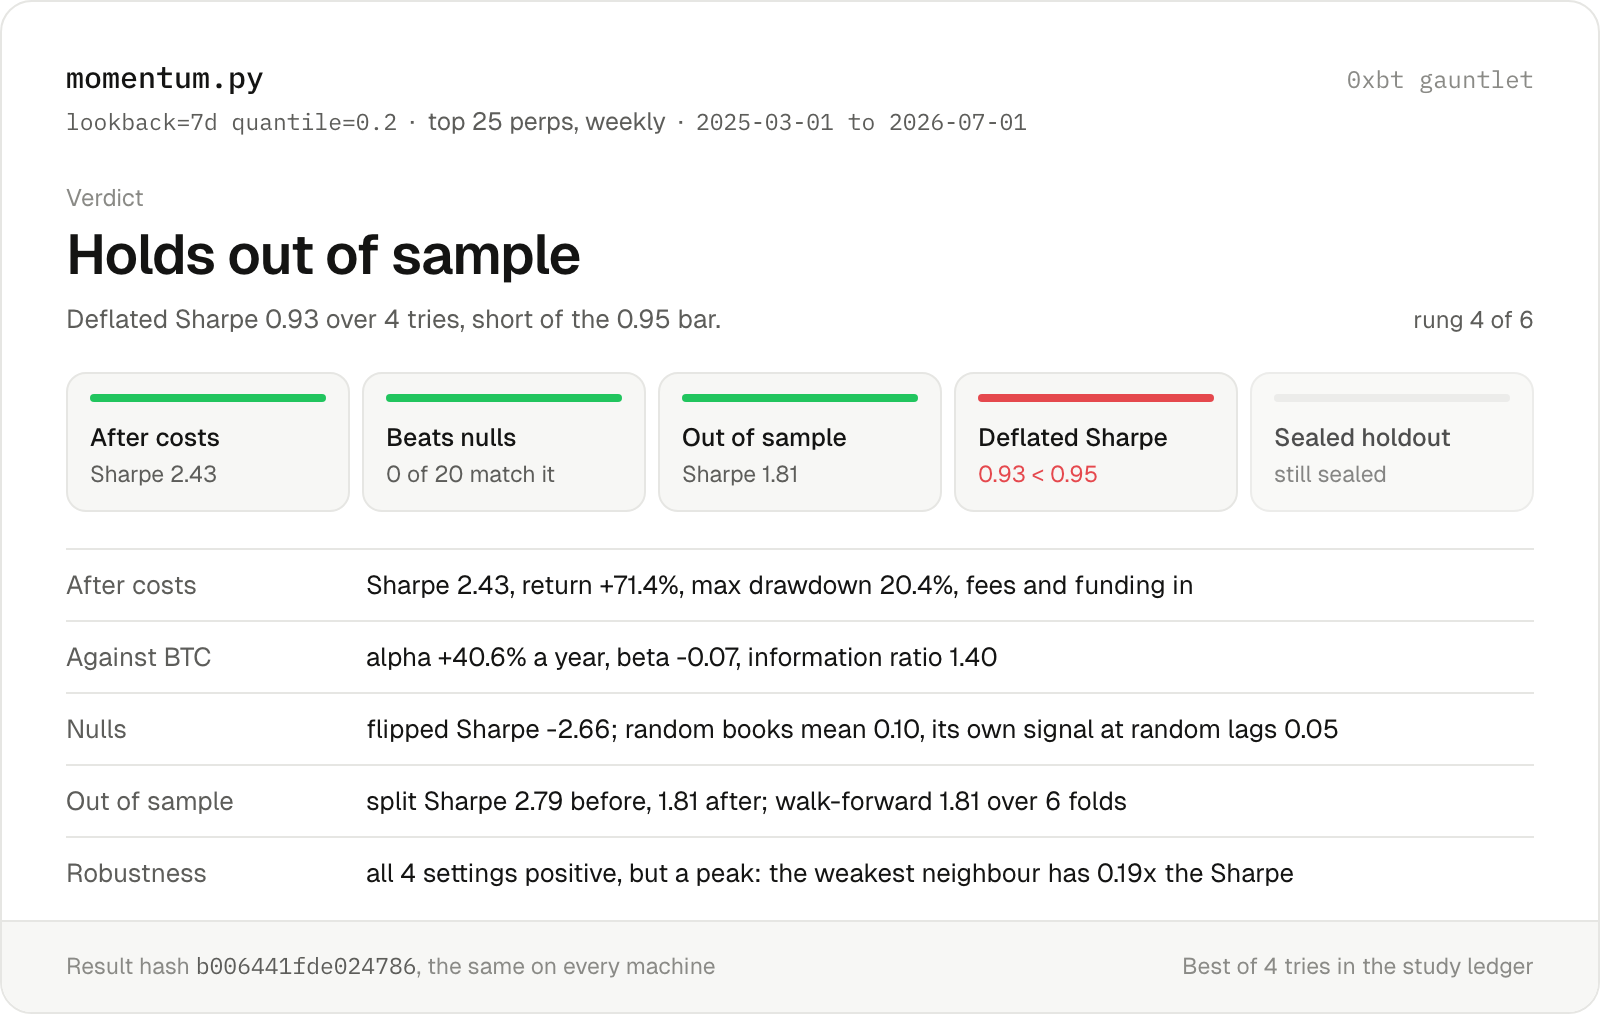
0xbt gauntlet runs, in order: the grid as trials; costs and a benchmark; nulls (the flipped signal,
random books and the strategy's own signal at random lags, redrawn at its holding period); a split and
walk-forward; the deflated Sharpe over every try; and robustness. The verdict is the first rung whose
rule fails:
| Rung | Verdict |
|---|---|
| 1 | loses after costs |
| 2 | fails nulls |
| 3 | in-sample only |
| 4 | holds out of sample |
| 5 | passes deflated Sharpe |
| 6 | passes sealed holdout |
0xbt study init starts a trial ledger: every backtest below it is recorded, the deflated Sharpe counts
all of them, and the last months of data stay sealed until one candidate is committed, once.
What the engine models
Minute bars with taker flow, funding, open interest and liquidations; taker and maker fees; funding
payments; leverage limits and liquidation; point-in-time universes (x.top_n, x.rule) so delisted
markets are included; stops, take-profits, trailing and time exits checked every minute; and
deterministic math, so results don't depend on the platform.
Links
MIT licensed.
1 maintainer

Metadata
1 maintainer
Release files for 0xarchive-backtest 0.3.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| 0xarchive_backtest-0.3.1.tar.gz | 198.2 kB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| 0xarchive_backtest-0.3.1-cp311-abi3-win_amd64.whl | CPython 3.11 | abi3 | Windows x86-64 | Details |
| 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.11 | abi3 | Linux glibc 2.17+ x86-64 | Details |
| 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.11 | abi3 | Linux glibc 2.17+ ARM64 | Details |
| 0xarchive_backtest-0.3.1-cp311-abi3-macosx_11_0_arm64.whl | CPython 3.11 | abi3 | macOS 11.0+ ARM64 | Details |
| 0xarchive_backtest-0.3.1-cp311-abi3-macosx_10_12_x86_64.whl | CPython 3.11 | abi3 | macOS 10.12+ x86-64 | Details |
Total release size: 20.6 MB
Release files / 0xarchive_backtest-0.3.1.tar.gz
| Download URL | 0xarchive_backtest-0.3.1.tar.gz |
|---|---|
| Size | 198.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
586321d963ec2639beb6837c85f231ffcaa72c4fbfbb7a910e3acbb279a560ef
|
|
BLAKE2b-256 checksum How to use checksums |
7e12e9e0123a2abe9378e381bda044ab8a298c72e6248f98d029cdfed8411c53
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logRelease files / 0xarchive_backtest-0.3.1-cp311-abi3-win_amd64.whl
| Download URL | 0xarchive_backtest-0.3.1-cp311-abi3-win_amd64.whl |
|---|---|
| Size | 4.1 MB |
| Tags | CPython 3.11 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
7d9cc76446794bc33ad6cfee9dbc29bb5b39440e6414a0bd67a3fa43e985f858
|
|
BLAKE2b-256 checksum How to use checksums |
90fc27f20560604bc25161db2283f0afd3cbb3b587a3cd74353ad2aa61b719ce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logRelease files / 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 4.3 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
cada95eac02b302eea8bb644118ef904abfa4d7b74b6541573b1d7b59b0af61b
|
|
BLAKE2b-256 checksum How to use checksums |
f7ce2caf8243b7cbe43d9f480d1cf1fff0c593cfa7919461fecdc8b2e2dad20b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logRelease files / 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | 0xarchive_backtest-0.3.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 4.1 MB |
| Tags | CPython 3.11 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
6062f75f5c1f0dd8e0295d009e505c75ddd75b7d59125b73bf7f549ce23b352b
|
|
BLAKE2b-256 checksum How to use checksums |
e718190a78bbb21b0629fae67fc4f7a82263b68df8ae4afd01388389bafdc52c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logRelease files / 0xarchive_backtest-0.3.1-cp311-abi3-macosx_11_0_arm64.whl
| Download URL | 0xarchive_backtest-0.3.1-cp311-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 3.8 MB |
| Tags | CPython 3.11 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
dd583c9cf28e9961310bf555ec691ed1e3538ce6157684f2b3462bc5e72c6fc8
|
|
BLAKE2b-256 checksum How to use checksums |
7925a52402aea1b783b2771db70744d8ee2ea04bbc1a0db194956d102a5ea97d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logRelease files / 0xarchive_backtest-0.3.1-cp311-abi3-macosx_10_12_x86_64.whl
| Download URL | 0xarchive_backtest-0.3.1-cp311-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 4.1 MB |
| Tags | CPython 3.11 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
454214725f84c25b4baab74ba96dc83340fa22706219a27bd9eabd6a3c58b3f7
|
|
BLAKE2b-256 checksum How to use checksums |
75b9614e74cdd2a4ec89dc2b0d0a3ecb7a7fc2160cd18150b480bbdc50082db6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logSecurity for 0xarchive-backtest 0.3.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for 0xarchive_backtest-0.3.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 25, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














