
A11
Build AI applications like normal software.
A11 is the open-source runtime for connecting models, tools and interfaces while keeping your architecture. It gives ordinary asynchronous code named streams, concurrency, tools and local-to-remote execution, and exposes the running application to Studio.
The Python API runs on a native C++20 runtime. TypeScript, Kotlin, C++ and Flow use the same action boundary where an application needs another language or process.
- Named streams instead of mixed provider events. Read model text, reasoning, tool activity, progress, and durable interaction state from separate ports.
- The same action contract locally and remotely. Move a handler to a GPU host, browser, or service without changing its inputs and outputs.
- Deterministic runtime composition with Flow. Check and load compositions at runtime with defined concurrency, draining, deadlines, cancellation, and error propagation.
Run the first action · Try the live research agent · Read the documentation · Star A11
Try A11 live
The hosted parallel research agent plans a topic, searches the web for each brief, reviews the returned evidence concurrently, and streams a cited report to the browser. Its default model and search backends need no visitor account or API key.
Run your first streaming action
Install the core runtime on Python 3.11 or later:
python -m venv .venv
source .venv/bin/activate
pip install a11-kit
Save this as quickstart.py. The function signature becomes an action schema,
and its asynchronous iterator becomes a named streaming output:
import asyncio
from collections.abc import AsyncIterator

import a11


REGISTRY = a11.ActionRegistry()


@REGISTRY.action(name="split-words", output="words")
async def split_words(text: str) -> AsyncIterator[str]:
    """Emit the words in a line as they become available."""
    for word in text.split():
        yield word


async def main() -> None:
    action = REGISTRY.make_action("split-words")
    await action["text"].finalize("named streams arrive early")
    action.run()

    async for word in action["words"]:
        print(word)
    await action.wait()


asyncio.run(main())
Run it:
python quickstart.py
The output port streams four values and then closes successfully. The same
REGISTRY can be served over WebSocket, HTTP SSE, or WebRTC; callers still use
the text and words ports.
Add model providers when the application needs them. With Ollama already running locally:
pip install "a11-kit[llm]"
a11 chat --provider ollama --no-voice --no-shell-tools
a11 chat reuses a gateway at the default endpoint, or starts one for the
duration of the chat with the current directory as its coding workspace.
--cwd PATH selects another workspace for a new gateway. An explicit
--gateway URL must be reachable.
In a coding chat, /sandbox unrestricted grants host filesystem access and
disables kernel process confinement. /sandbox workspace-write or
/sandbox read-only restores confinement. Approval remains a separate setting
(/approval suggest|auto). Sandbox changes affect subsequent tool calls for
all clients of that gateway, not already-running processes.
Studio and IDE clients can call the UI-only configure_coding_agent action
with sandbox_mode (read-only, workspace-write, or unrestricted) and/or
approval_mode (suggest or auto). Omitted fields keep their current values;
the result contains approval_mode, sandbox_ceiling, and network. This
control is excluded from the coding agent's model-facing action list.
Input questions appear above the TUI composer. Use Up/Down to select and Enter
to answer, or type a response when free text is allowed. An output-area status
line shows Working during model calls and Waiting for input while a
question is pending.
Add capabilities incrementally
Streaming. An asynchronous iterator yields values before it finishes. Named outputs give model text, reasoning, progress and structured values their own interfaces. The caller reads those streams and checks the action's final status separately.
Concurrency. Use ordinary Python tasks or C++ runtime primitives for independent work. Use nested A11 actions when the runtime should understand a parent/child relationship and propagate cancellation.
Tools. Expose registered actions to model calls through the SDK, or serve the same registry through MCP. The application still owns validation, authorization and policy.
Remote execution. Serve a registry from another process or machine. The caller configures a connection and calls the action; the handler's input and output contract stays stable.
Flow is available when an application needs a composition expressed as data. It is optional: model APIs, MCP, LangGraph and existing application code can remain part of the stack.
Inspect the work with Studio
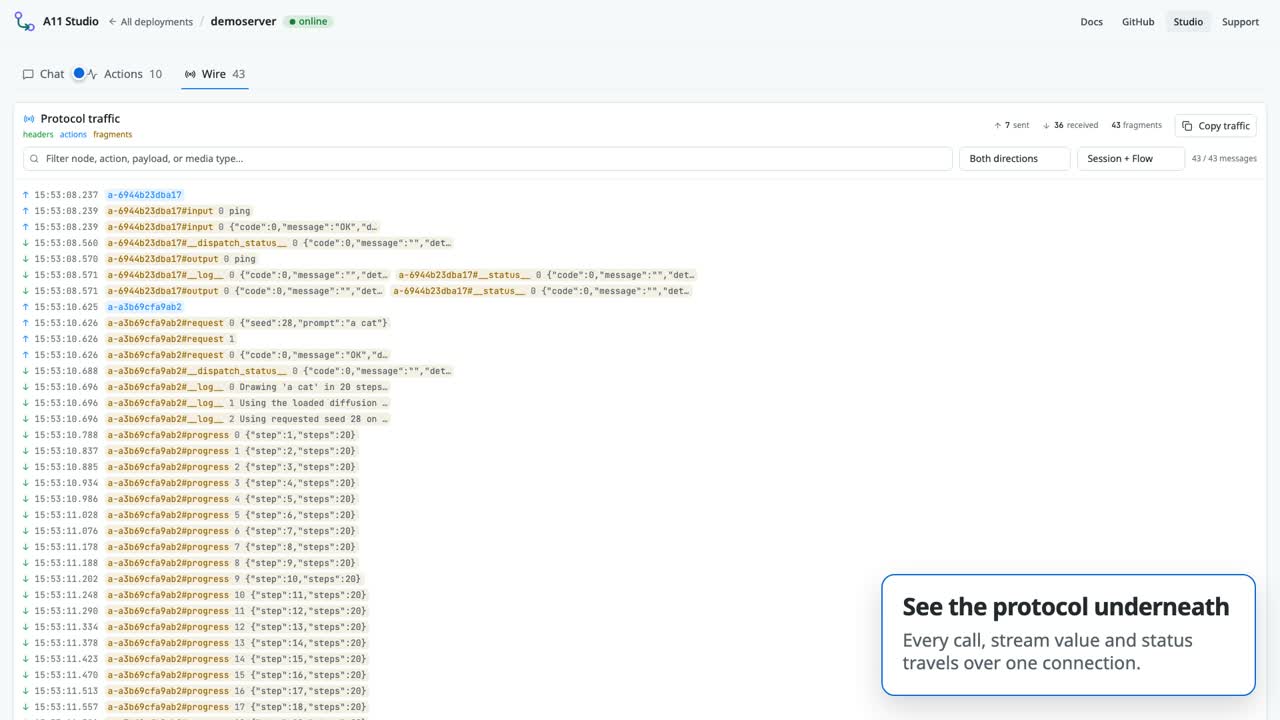
Open Studio to explore an endpoint's action schemas, run calls and inspect streamed outputs, logs, timings, failures and cancellation.
Explore complete applications
- Deep research plans a topic, searches the web in parallel and streams a cited synthesis.
- Model interactions present one streaming interface across Claude, Gemini, Ollama and OpenAI-compatible providers.
- The
a11 chat --voice-model ...path keeps audio capture, transcription and model interaction on separate streams. - Generative media streams progress independently from generated image bytes.
- Browser tools let a model call typed actions implemented inside an existing page.
Each guide names its provider, model and hardware prerequisites. Local actions and remote transports do not require a model.
Install only what the application needs
The Python distribution is a11-kit, imported as a11. Provider integrations
are optional extras such as a11-kit[ollama], a11-kit[claude] and
a11-kit[openai]. Browser and TypeScript applications use:
npm install @curiositystack/a11
The standalone C++20 runtime needs no Python installation. Build and link it through its exported CMake targets using the instructions below.
Go deeper
- Build a parallel research agent in Python.
- Stream one model interface across Claude, Gemini, and Ollama.
- Turn an application action into an LLM tool.
- Move a local action behind a remote service.
- Compose allowed actions safely at runtime.
Questions and rough edges are useful project signals: start a discussion, report friction, or tell us about an integration.
Building the C++ runtime
A11's runtime is a standalone C++20 library you can build and link without Python. The steps below are self-contained; for the editable Python build, wheel matrix, testing workflow, and architecture, see BUILDING.md.
1. Install the tools, then build the C++ libraries. A11 links a pinned set
of statically-built libraries (Boost, OpenSSL, libcurl, nghttp2, hiredis,
nlohmann-json, uvw) rather than system copies; scripts/bootstrap_wheel_deps.sh builds them
into a per-architecture prefix. From Homebrew you install only the tools (a C++20
compiler, CMake ≥ 3.28, Ninja; Linux tool package names vary):
brew install cmake googletest ninja pkg-config

export A11_DEPS_PREFIX="$HOME/.cache/a11-deps/$(uname -m)"
export CMAKE_PREFIX_PATH="$A11_DEPS_PREFIX"
export OPENSSL_ROOT_DIR="$A11_DEPS_PREFIX"
export PKG_CONFIG_PATH="$A11_DEPS_PREFIX/lib/pkgconfig"
export MACOSX_DEPLOYMENT_TARGET=14.4   # macOS only
scripts/bootstrap_wheel_deps.sh
CMake still fetches the pinned Abseil (and libdatachannel, for WebRTC) automatically. See BUILDING.md for the full rundown.
2. Configure, build, and install to a prefix (the exports above point CMake at the dependency prefix):
cmake -S . -B build -G Ninja \
  -DCMAKE_BUILD_TYPE=Release \
  -DA11_BUILD_PYTHON=OFF \
  -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 \
  -DCMAKE_INSTALL_PREFIX="$PWD/install"

cmake --build build -j
cmake --install build
On macOS, pass -DCMAKE_OSX_DEPLOYMENT_TARGET=14.4 as shown — it must match the
value the prefix was bootstrapped with. Setting it as a cache variable here (not
only via the MACOSX_DEPLOYMENT_TARGET environment export, which CMake may not
pick up) is what enables the Boost.Fiber futex spinlock; a lower target compiles
Boost.Fiber without futex support and fails with
"futex not supported on this platform". The flag is ignored on Linux.
3. Use it from your own CMake project. The install exports a CMake package
named a11 with per-component targets (a11::service links the whole runtime).
Point your consumer's CMAKE_PREFIX_PATH at both the install prefix and the
dependency prefix from step 1, so the transitive static Boost/OpenSSL/... resolve:
find_package(a11 CONFIG REQUIRED)

add_executable(my_agent main.cc)
target_link_libraries(my_agent PRIVATE a11::service)
target_compile_features(my_agent PRIVATE cxx_std_20)
#include <cstddef>
#include <iostream>
#include <memory>
#include <optional>
#include <string>
#include <vector>

#include <absl/log/log.h>
#include <absl/status/status.h>
#include <absl/status/status_macros.h>
#include <absl/strings/str_split.h>

#include "a11/actions/registry.h"
#include "a11/nodes/async_node.h"

namespace {

using a11::actions::Action;
using a11::actions::ActionPortSchema;
using a11::actions::ActionRegistry;
using a11::actions::ActionSchema;
using a11::nodes::AsyncNode;

ActionSchema SplitWordsSchema() {
  return ActionSchema{
      .name = "split-words",
      .inputs = {{"text", ActionPortSchema{
                             .name = "text", .type = "text/plain"}}},
      .outputs = {{"words", ActionPortSchema{
                               .name = "words", .type = "text/plain"}}},
  };
}

absl::Status SplitWords(std::shared_ptr<Action> action) {
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_ASSIGN_OR_RETURN(
      std::optional<std::string> text,
      input->NextObject<std::string>().Await());
  if (!text.has_value()) {
    return absl::FailedPreconditionError("text input ended before a value");
  }

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  std::vector<std::string> words =
      absl::StrSplit(*text, absl::ByAnyChar(" \t\n"), absl::SkipWhitespace());
  if (words.empty()) {
    return output->Finalize({.wait = true}).Await().status();
  }
  for (size_t index = 0; index + 1 < words.size(); ++index) {
    ABSL_RETURN_IF_ERROR(output->Put(words[index]).Await().status());
  }
  return output->Finalize(words.back(), {.wait = true}).Await().status();
}

absl::Status RunExample() {
  auto registry = std::make_shared<ActionRegistry>();
  ABSL_RETURN_IF_ERROR(registry->RegisterSync(
      "split-words", SplitWordsSchema(), SplitWords));
  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<Action> action,
                        registry->MakeAction("split-words"));

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> input,
                        action->GetInput("text"));
  ABSL_RETURN_IF_ERROR(
      input->Finalize(std::string("named streams arrive early"),
                      {.wait = true})
          .Await()
          .status());
  ABSL_RETURN_IF_ERROR(action->Run().status());

  ABSL_ASSIGN_OR_RETURN(std::shared_ptr<AsyncNode> output,
                        action->GetOutput("words"));
  while (true) {
    ABSL_ASSIGN_OR_RETURN(std::optional<std::string> word,
                          output->NextObject<std::string>().Await());
    if (!word.has_value()) break;
    std::cout << *word << '\n';
  }
  return action->Wait().Await().status();
}

}  // namespace

int main() {
  const absl::Status status = RunExample();
  if (!status.ok()) {
    LOG(ERROR) << status;
    return 1;
  }
  return 0;
}
This is the same split-words action as the Python quickstart: the registry
owns its schema and handler, the input carries one complete value, and the
output emits words as a stream. Reading the output before Wait() drains it
while the handler is running and preserves backpressure.
Configure your project with -DCMAKE_PREFIX_PATH=/path/to/install so
find_package locates it. The generated C++ API reference is published
alongside the docs.
1 maintainer

Metadata
1 maintainer
Release files for a11-kit 0.7.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| a11_kit-0.7.5.tar.gz | 2.4 MB | Details |
Built distributions (wheels)
Total release size: 140.6 MB
Release files / a11_kit-0.7.5.tar.gz
| Download URL | a11_kit-0.7.5.tar.gz |
|---|---|
| Size | 2.4 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
e34193106cce9a056e1f331e8fb29717c09c5df46c2fed88014d28a74b6a2435
|
|
BLAKE2b-256 checksum How to use checksums |
8abc3b662f32d7e94cc144eafe8a92f95c69574b49a2785571e068442d4e4baf
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp314-cp314-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.5-cp314-cp314-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.6 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
35b8fc4304d35da701b98d074b33b57236744529897bb4f1eb2c2ea86d84e9fb
|
|
BLAKE2b-256 checksum How to use checksums |
6769aee1de1daf5477c09767b256e9c4bfe32790c67406b385ccf69ad6363c9e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp314-cp314-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.5-cp314-cp314-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.0 MB |
| Tags | CPython 3.14 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
9c773c51f081d3950359c0917be76af0aa054144e79e6adaba3e7a68d39b1b1c
|
|
BLAKE2b-256 checksum How to use checksums |
67615ad2bcad9760128962c8f466db75ea066a5a8fb8389ae91548963d953ffa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp314-cp314-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.5-cp314-cp314-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.0 MB |
| Tags | CPython 3.14 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
b6111d06e99c2b65e796fd9d596e4e2cb040b9f1a2aaa6d866c6845752351bd9
|
|
BLAKE2b-256 checksum How to use checksums |
45a35b403e864adfd621285d87d8cdbccf1d9f63706afe7dcede5f489ff6ce05
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp313-cp313-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.5-cp313-cp313-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.6 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
f341431dc7facbf920b17575d5cb6cddaa7d5eb954525610cdb404930bd13e5c
|
|
BLAKE2b-256 checksum How to use checksums |
ec7200c1ca271cd0f24742fa5accefee6feab15943921a8fe0d0b2f289907a17
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp313-cp313-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.5-cp313-cp313-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 11.9 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
4b300f0da5d0265a5858752c513c707065292af4774b08cfef356f498a905c1c
|
|
BLAKE2b-256 checksum How to use checksums |
3d13ce8ae61c601b817c11579bc7fd429b9c957f5a5d3584b8106ad9a84cae83
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp313-cp313-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.5-cp313-cp313-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.0 MB |
| Tags | CPython 3.13 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
2271c2557df78327a4ba74fcbfb8b9f9ab94c2a1784106ab50fe83d2ccdc79be
|
|
BLAKE2b-256 checksum How to use checksums |
34dc3ca4cc2bfd7a61f9ba365fe72a76fe02593ba23df706c0bd59456f69caab
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp312-cp312-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.5-cp312-cp312-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.6 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
12158d4ae2e8c9f9fb98ac3c69710fedb0265bcc3d4afb1fda1edd519e2719b4
|
|
BLAKE2b-256 checksum How to use checksums |
9549c11e4d2b8c53a9f4d34be2a98c478d1b89b8716896d9c572972d29926e3e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp312-cp312-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.5-cp312-cp312-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.0 MB |
| Tags | CPython 3.12 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
d8e486af431c760511ec3594cabdfe4fbe80957ef6979256e11a2cb5f2615655
|
|
BLAKE2b-256 checksum How to use checksums |
672a869ded8fab3cd6383e28d4ffd46c3675cdebb8ea5a99dcb96900745563ec
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp312-cp312-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.5-cp312-cp312-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.0 MB |
| Tags | CPython 3.12 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
86bf705e22215abe15217e636a0200a45b481b42a1c09e6bd3426c33e674b625
|
|
BLAKE2b-256 checksum How to use checksums |
94ddd733177e086e2b34f7560f3f867d5566f98cc3fb446a2ee126223a49c5a1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp311-cp311-manylinux_2_28_x86_64.whl
| Download URL | a11_kit-0.7.5-cp311-cp311-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 12.5 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
df7a122961d30a832c5b01447a1d81f862ece96b243b5ea048e11e43112a987a
|
|
BLAKE2b-256 checksum How to use checksums |
b79d8ea755e3f2192697f1356631fa55d0636e5aed9dea1e6a7b83e81ee07782
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp311-cp311-manylinux_2_28_aarch64.whl
| Download URL | a11_kit-0.7.5-cp311-cp311-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 12.0 MB |
| Tags | CPython 3.11 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
cfeea3d73423b44da59cdc37740f09942c12f6ed18cbd1319d85c8f57567533e
|
|
BLAKE2b-256 checksum How to use checksums |
4c7b24868894f6629a436515ddf0a14ade7e2722c7fb4df36b67fd573226eecd
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency logRelease files / a11_kit-0.7.5-cp311-cp311-macosx_14_0_arm64.whl
| Download URL | a11_kit-0.7.5-cp311-cp311-macosx_14_0_arm64.whl |
|---|---|
| Size | 10.0 MB |
| Tags | CPython 3.11 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
1f2f7a68bbfa21a04c7fa1c8b15016748e031a5476ea93b2c21706019d5da242
|
|
BLAKE2b-256 checksum How to use checksums |
55a992aa87bedd3df6d81c3d4fee99ccfb2c4ca5fbe5c0cc1f9040dd22f378ce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 16, 2026.
Transparency log













