
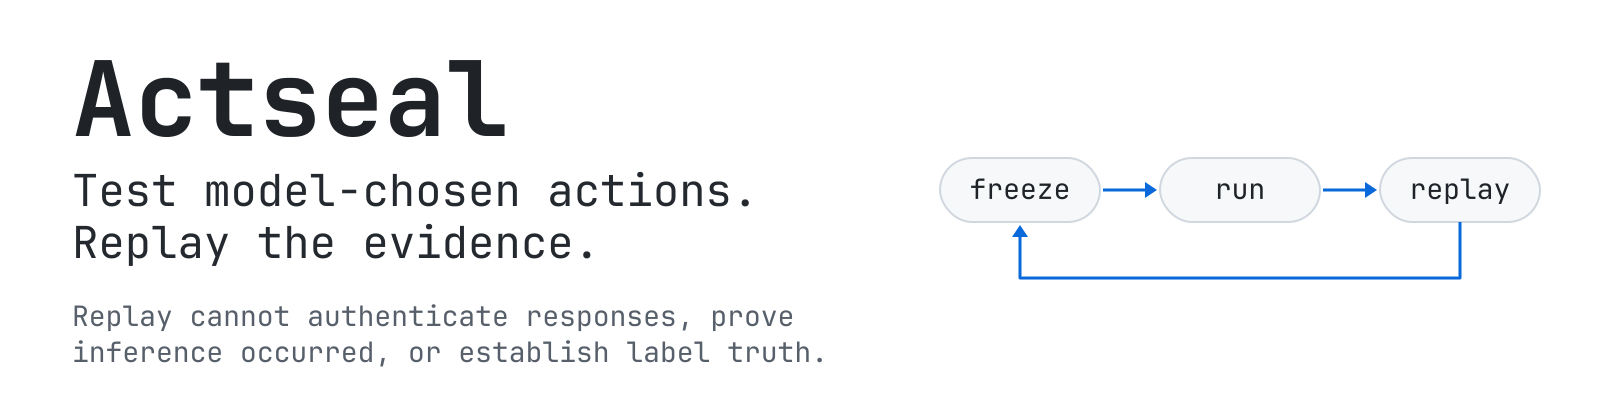
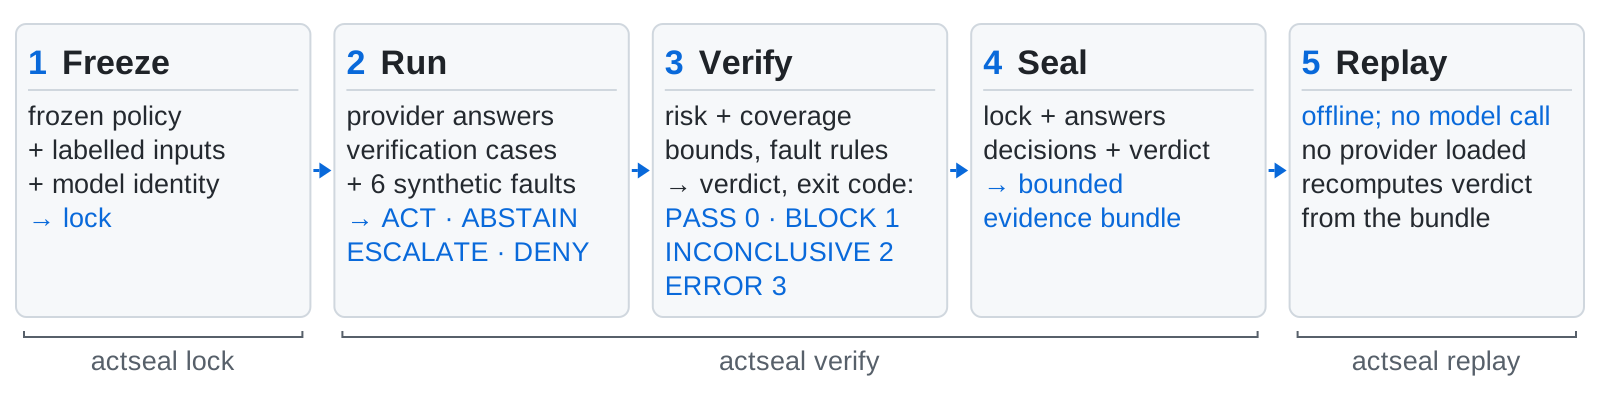
Actseal verifies model-chosen application actions for developers: freeze a policy, check its recorded decisions, and replay the evidence offline.



Run the packaged demonstration on macOS or Linux with
uv installed. The
first command resolves the latest Actseal release on PyPI
for Python 3.12; no source checkout, model or API key is needed, and
./actseal-demo must not already exist.
uvx --python 3.12 actseal demo --out ./actseal-demo
uvx --offline --python 3.12 actseal replay ./actseal-demo/fixed/evidence
uvx --offline --python 3.12 actseal replay ./actseal-demo/bad/evidence
The third command intentionally exits 1: replay faithfully reproduces the deliberately bad run's BLOCK. Python and package installation time is separate from the demo's own execution. The quickstart explains each output, the exit codes and how to pin one exact release.
Guarantees
- Complete scheduled-case and required fault evidence is checked.
- PASS requires the frozen risk/coverage bounds and fault rules to pass.
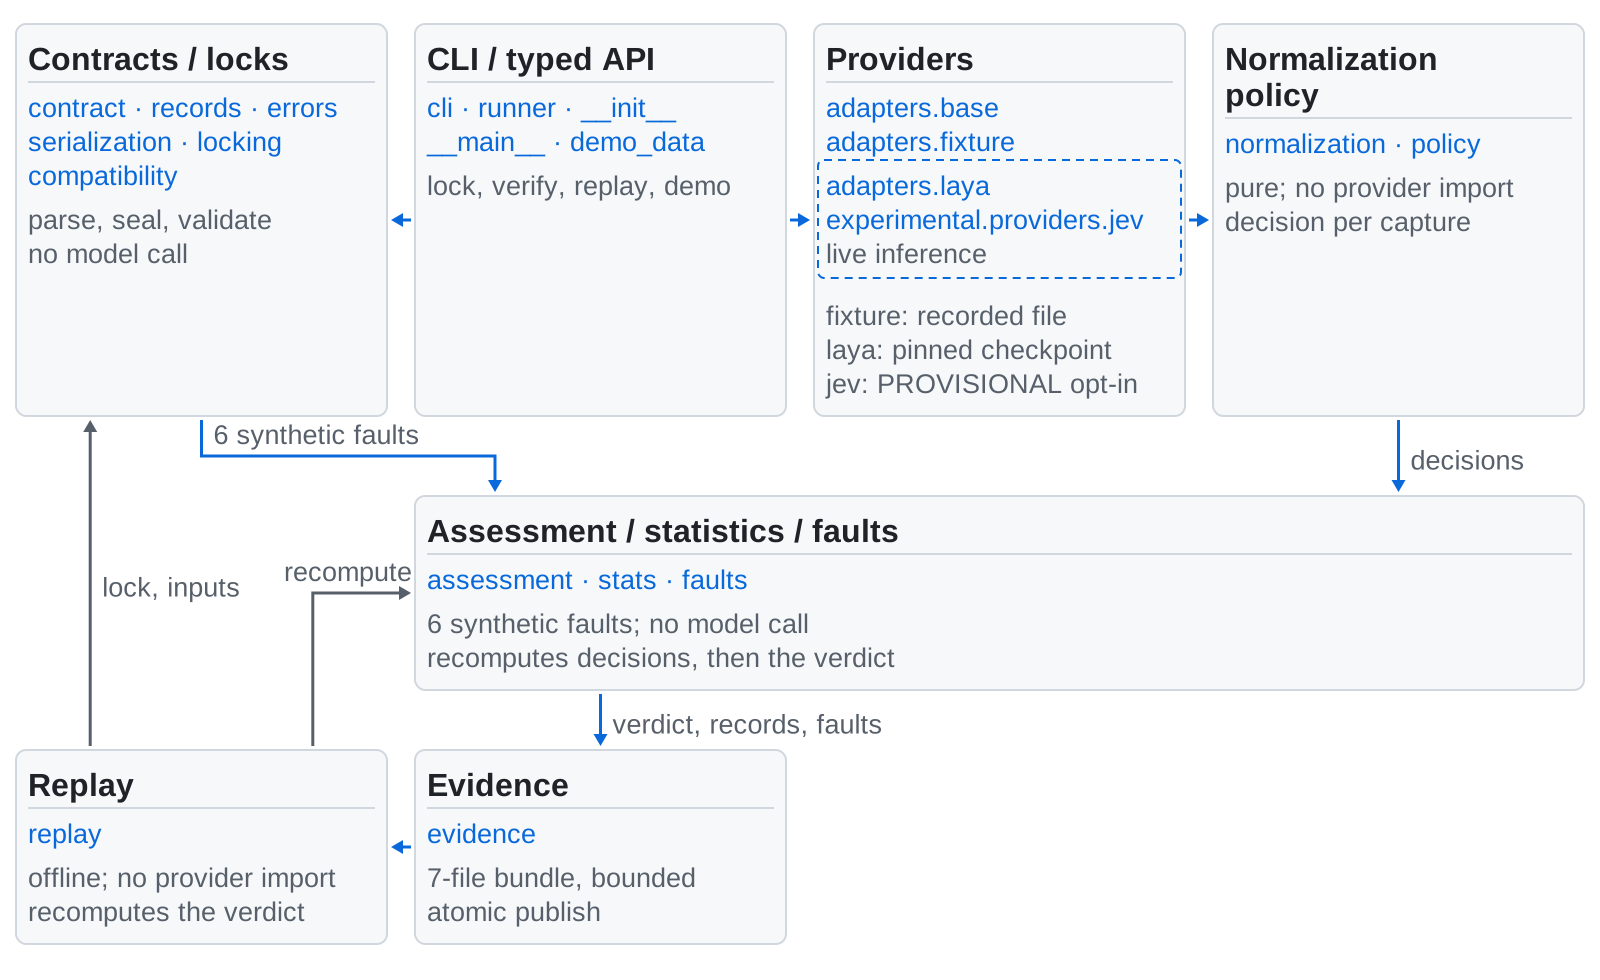
- Supported evidence is recomputed offline without calling a model.
Limits
- Hashes and replay cannot authenticate coherently rewritten responses.
- They cannot prove inference occurred or that labels are true.
- Population claims require the stated sampling assumptions; Actseal does not enforce application execution.
| Read | What it covers |
|---|---|
| Concepts | Frozen policy, selected-option probability, per-case decisions versus whole-run verdicts, evidence scope, one attempt |
| CLI reference and Python guide | Exact commands, exit codes, JSON receipts, public functions and runnable examples |
| Stability manifest, versioning and migration | The 1.x compatibility promise, what may change when, and the 0.1.0 evidence path |
| Statistical contract and threat model | Bounds, verdict rules, sampling assumptions and the authenticity boundary |
| Providers and FAQ | Fixture and optional native Laya setup; the PROVISIONAL experimental Jev cloud adapter behind --provider jev --experimental-provider (bring your own key, mocked-transport tests only, no accepted live receipt); answers to "why not PASS" |
| Publishing, CHANGELOG, release notes and SECURITY | Release pipeline and receipts, changes per version, the receipt-backed release notes, private vulnerability reporting and support |
Read a result
An ACT is a per-case decision permitted by the frozen allowlist and the selected-label probability threshold; it is not a statement that the answer is correct. Coverage is ACT decisions over all scheduled cases and risk is wrong ACT decisions over ACT decisions. A whole-run verdict bounds those rates:
| Exit | Verdict | Meaning |
|---|---|---|
| 0 | PASS | Valid evidence satisfies the frozen risk and coverage limits and the fault checks. |
| 1 | BLOCK | Valid evidence establishes a limit violation or a fault-check failure. |
| 2 | INCONCLUSIVE | Valid evidence proves neither PASS nor BLOCK. |
| 3 | ERROR | Invalid or incomplete evidence, a usage or setup failure, or an invalidated native-worker experiment. |
lock exits 0 on success. demo exits 0 only for its expected BLOCK/PASS
pair with matching replays; it never relabels the bad run. Every command
accepts --json for one versioned receipt.
Scope
Actseal 1.x supports one categorical question with 2 to 16 labels, a frozen
action allowlist and threshold, recorded fixture responses and an optional
pinned native Laya CPU adapter. An experimental Jev cloud adapter ships as a
PROVISIONAL, explicit opt-in (--provider jev --experimental-provider) with
no 1.x compatibility promise and no accepted live evidence. The runtime core
depends only on the Python standard library (3.12 or 3.13) on Linux and
macOS; Windows is unsupported. Replay never imports a provider. The packaged demonstration is synthetic
(evidence_scope=demo) and establishes no population or model-quality
result. Real interpretation requires independent cases and one prespecified
attempt under a fixed policy; do not retry until PASS.
Apache-2.0; see LICENSE, NOTICE and dependency notices. Contributions: CONTRIBUTING.
1 maintainer

Metadata
1 maintainer
Release files for actseal 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| actseal-1.0.0.tar.gz | 2.1 MB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| actseal-1.0.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.2 MB
Release files / actseal-1.0.0.tar.gz
| Download URL | actseal-1.0.0.tar.gz |
|---|---|
| Size | 2.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
aa31ccf9f5cce30c40269dd5d9904ef61f147f9c4aaf21e3db288981b3278da6
|
|
BLAKE2b-256 checksum How to use checksums |
42afa6bc4bbc02ce7d20eecd4139c3d17040beeeb32bb9ad18a6c5536a4b5274
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency logRelease files / actseal-1.0.0-py3-none-any.whl
| Download URL | actseal-1.0.0-py3-none-any.whl |
|---|---|
| Size | 101.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
4497fef4878cb67f03845e13f91c8b8c4e7686361198d0ebc52a1764157ae3bf
|
|
BLAKE2b-256 checksum How to use checksums |
f7e4602fe2c84324dcbd4a55dc4a451e319ba8833d59ebaa7128eccf68e22e96
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 7, 2026.
Transparency log













