
Agent Atlas
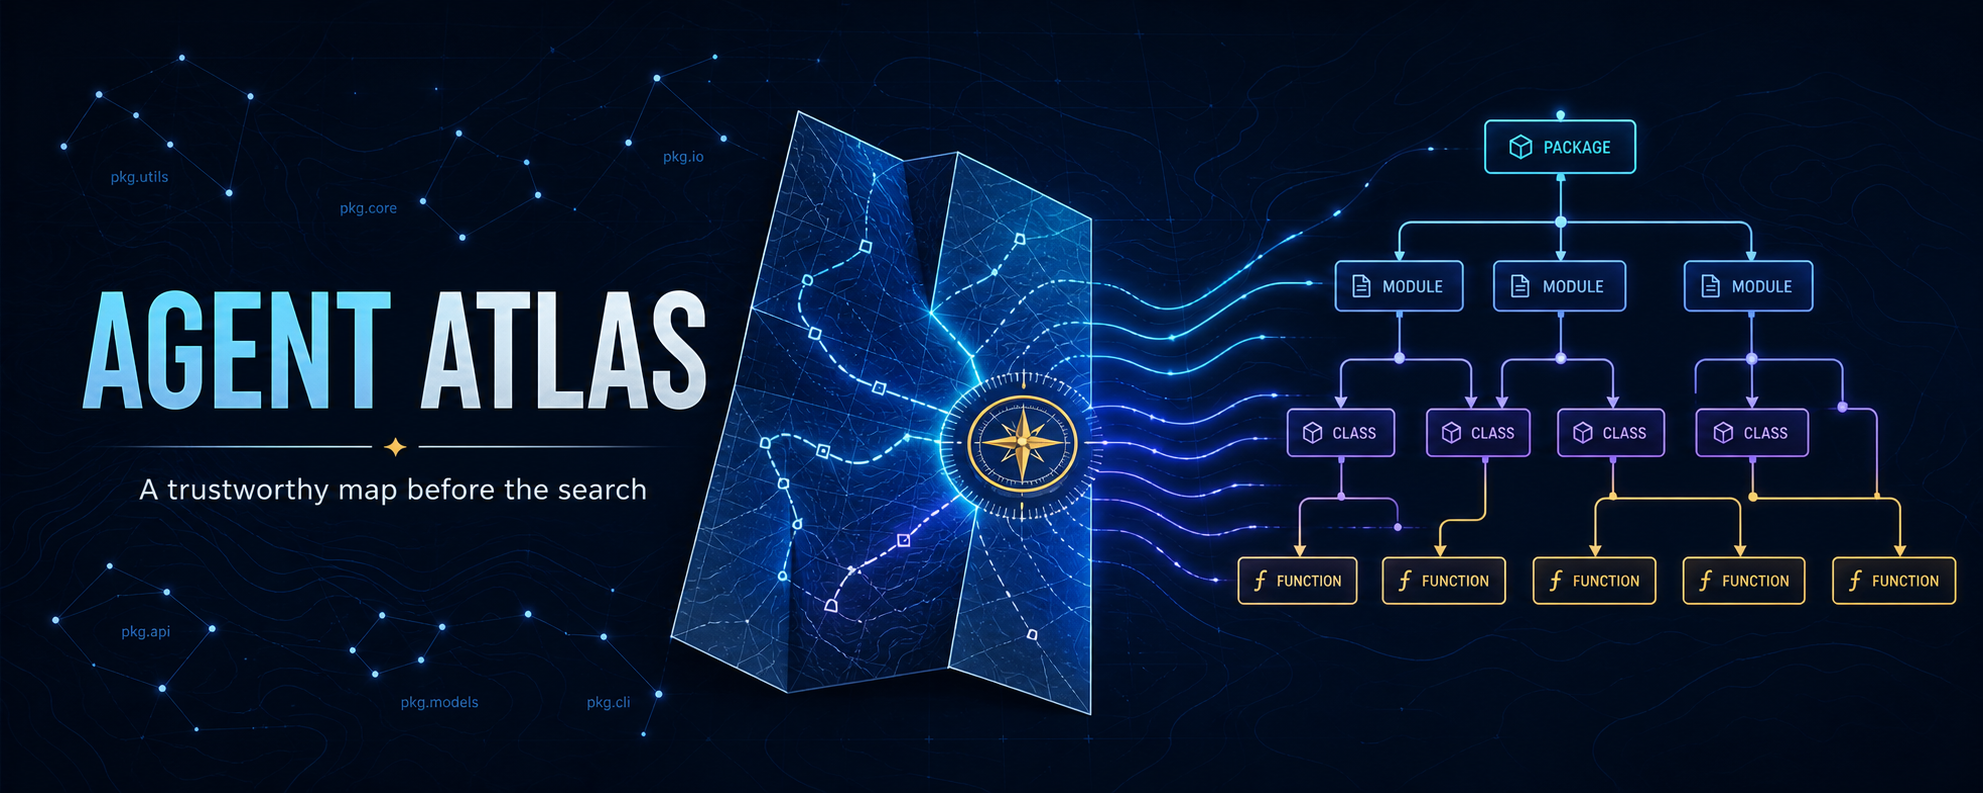


Agent Atlas generates a deterministic, static repository map for coding agents. It uses Griffe to extract Python packages, public symbols, signatures, annotations, docstrings, source locations, and local type references without importing the project being mapped.
No LLM calls. No target-code execution. No invented explanations.
Start with MAP.md, follow the package and module pages to the exact symbol,
then open the source. Use deeper graph tools only when relationships or impact
analysis actually matter.
Install
pip install agent-atlas-map
Python 3.11 or later is required. The agent-atlas and repo-map commands are
equivalent; repo-map is retained as a compatibility alias.
Configure and run
Add a minimal configuration to the target repository's pyproject.toml:
[tool.repo-map]
source_roots = ["src"]
root_packages = ["my_package"]
source_roots defaults to ["src"]. When root_packages is omitted, Agent
Atlas discovers importable packages and modules directly below each source
root. Output defaults to .repo-map and MAP.md; the paths and additional
filtering, policy, summary, and watch settings can be configured in the same
table.
# Generate or update the map in the current repository.
agent-atlas build

# Fail when generated files are missing or differ from a fresh render.
agent-atlas check

# Generate once, then rebuild after debounced .py or .pyi source changes.
agent-atlas watch

# Run against another repository.
agent-atlas build --project-root /path/to/project
Output and exit codes
build writes a generated MAP.md at the project root and a .repo-map/
directory containing index.json, package maps, and module maps. check does
not write files.
| Code | Meaning |
|---|---|
| 0 | Build succeeded, or check found current, policy-compliant output. |
| 1 | check found stale, missing, or unexpected generated output. |
| 2 | A configured public-API policy requirement was violated. |
| 3 | Generation, publication, or watch failed. |
| 4 | Command usage or repository-map configuration was invalid. |
| 130 | The process was interrupted. |
Limits and safety
Agent Atlas is static analysis, not runtime introspection. Dynamically created symbols, imports resolved only at runtime, generated source, and information available only through execution may be absent or unresolved in the map.
Builds stage and validate output before publishing. Agent Atlas refuses to
replace output it cannot identify as its own and attempts rollback when a
publication step fails. Each target replacement is atomic on the local
filesystem, but .repo-map/ and MAP.md are separate targets: a process or
filesystem failure between replacements cannot be made globally atomic. Keep
the generated files under version control or regenerate after an interrupted
build. Publication assumes a locally controlled checkout; it does not defend
against another process maliciously replacing target directories during the
publication window.
Development
uv sync --group dev
uv run pytest
uv run ruff check .
uv run mypy
uv build
License
MIT. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for agent-atlas-map 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| agent_atlas_map-0.1.0.tar.gz | 58.2 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| agent_atlas_map-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 84.6 kB
Release files / agent_atlas_map-0.1.0.tar.gz
| Download URL | agent_atlas_map-0.1.0.tar.gz |
|---|---|
| Size | 58.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b916953fb933d18dd81b571ca01e66e02c7efdffc544eaf6ad1677941e97d767
|
|
BLAKE2b-256 checksum How to use checksums |
70717b1940156f49b99cb2d7d54fc3c5e9ef7fe2663d44354c42c090db64622c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.0 {"installer":{"name":"uv","version":"0.12.0","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Release files / agent_atlas_map-0.1.0-py3-none-any.whl
| Download URL | agent_atlas_map-0.1.0-py3-none-any.whl |
|---|---|
| Size | 26.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7c4a87705926bdcdb400bcfd014a0002e1db495dc8001e234d2ff3f4e73de1cc
|
|
BLAKE2b-256 checksum How to use checksums |
6d7f3bc717caadc16cdff180f6b521369c447a921352bb135b5c08406d029138
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.0 {"installer":{"name":"uv","version":"0.12.0","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Security for agent-atlas-map 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













