
Dreamer


Stop repeating the same coding-agent corrections.
Most teams give their coding agent the same feedback over and over: verify
builds and tests before declaring done, don't weaken tests to make them pass,
don't add comments nobody asked for, follow the project's naming conventions.
That feedback rarely makes it into AGENTS.md or CLAUDE.md, so the agent
keeps making the same mistakes.
Dreamer mines your recent coding-agent session history for the corrections that keep recurring, and turns them into concrete additions to your context files, with the original conversation as evidence and your approval required before anything is written.
Dreamer works with 20 coding harnesses including Claude Code, Codex, Cursor, OpenCode, Gemini CLI and more.
session history -> recurring corrections -> context file updates -> fewer repeated corrections
Get started
Requires Python 3.11-3.13.
npx skills add whistler/dreamer --skill dream -g -y
Then, in your agent:
/dream
/dream --days 14
Dreamer proposes context-file updates as a reviewable in-chat plan (instructions, supporting evidence, and destination files) and applies only what you approve.
No provider keys needed; Dreamer uses your existing subscription. Everything
runs locally: session history is read on your machine, context files are
edited on your machine, and nothing is uploaded. Session history comes from
cass,
which Dreamer installs automatically on first run.
The dashboard
For reviewing patterns, evidence, and trends across many sessions at once, use the dashboard:
pipx install agent-dreamer
dreamer serve
If you want the CLI to mine sessions without the /dream skill, run
dreamer run --yes after configuring a provider key.
See it in action
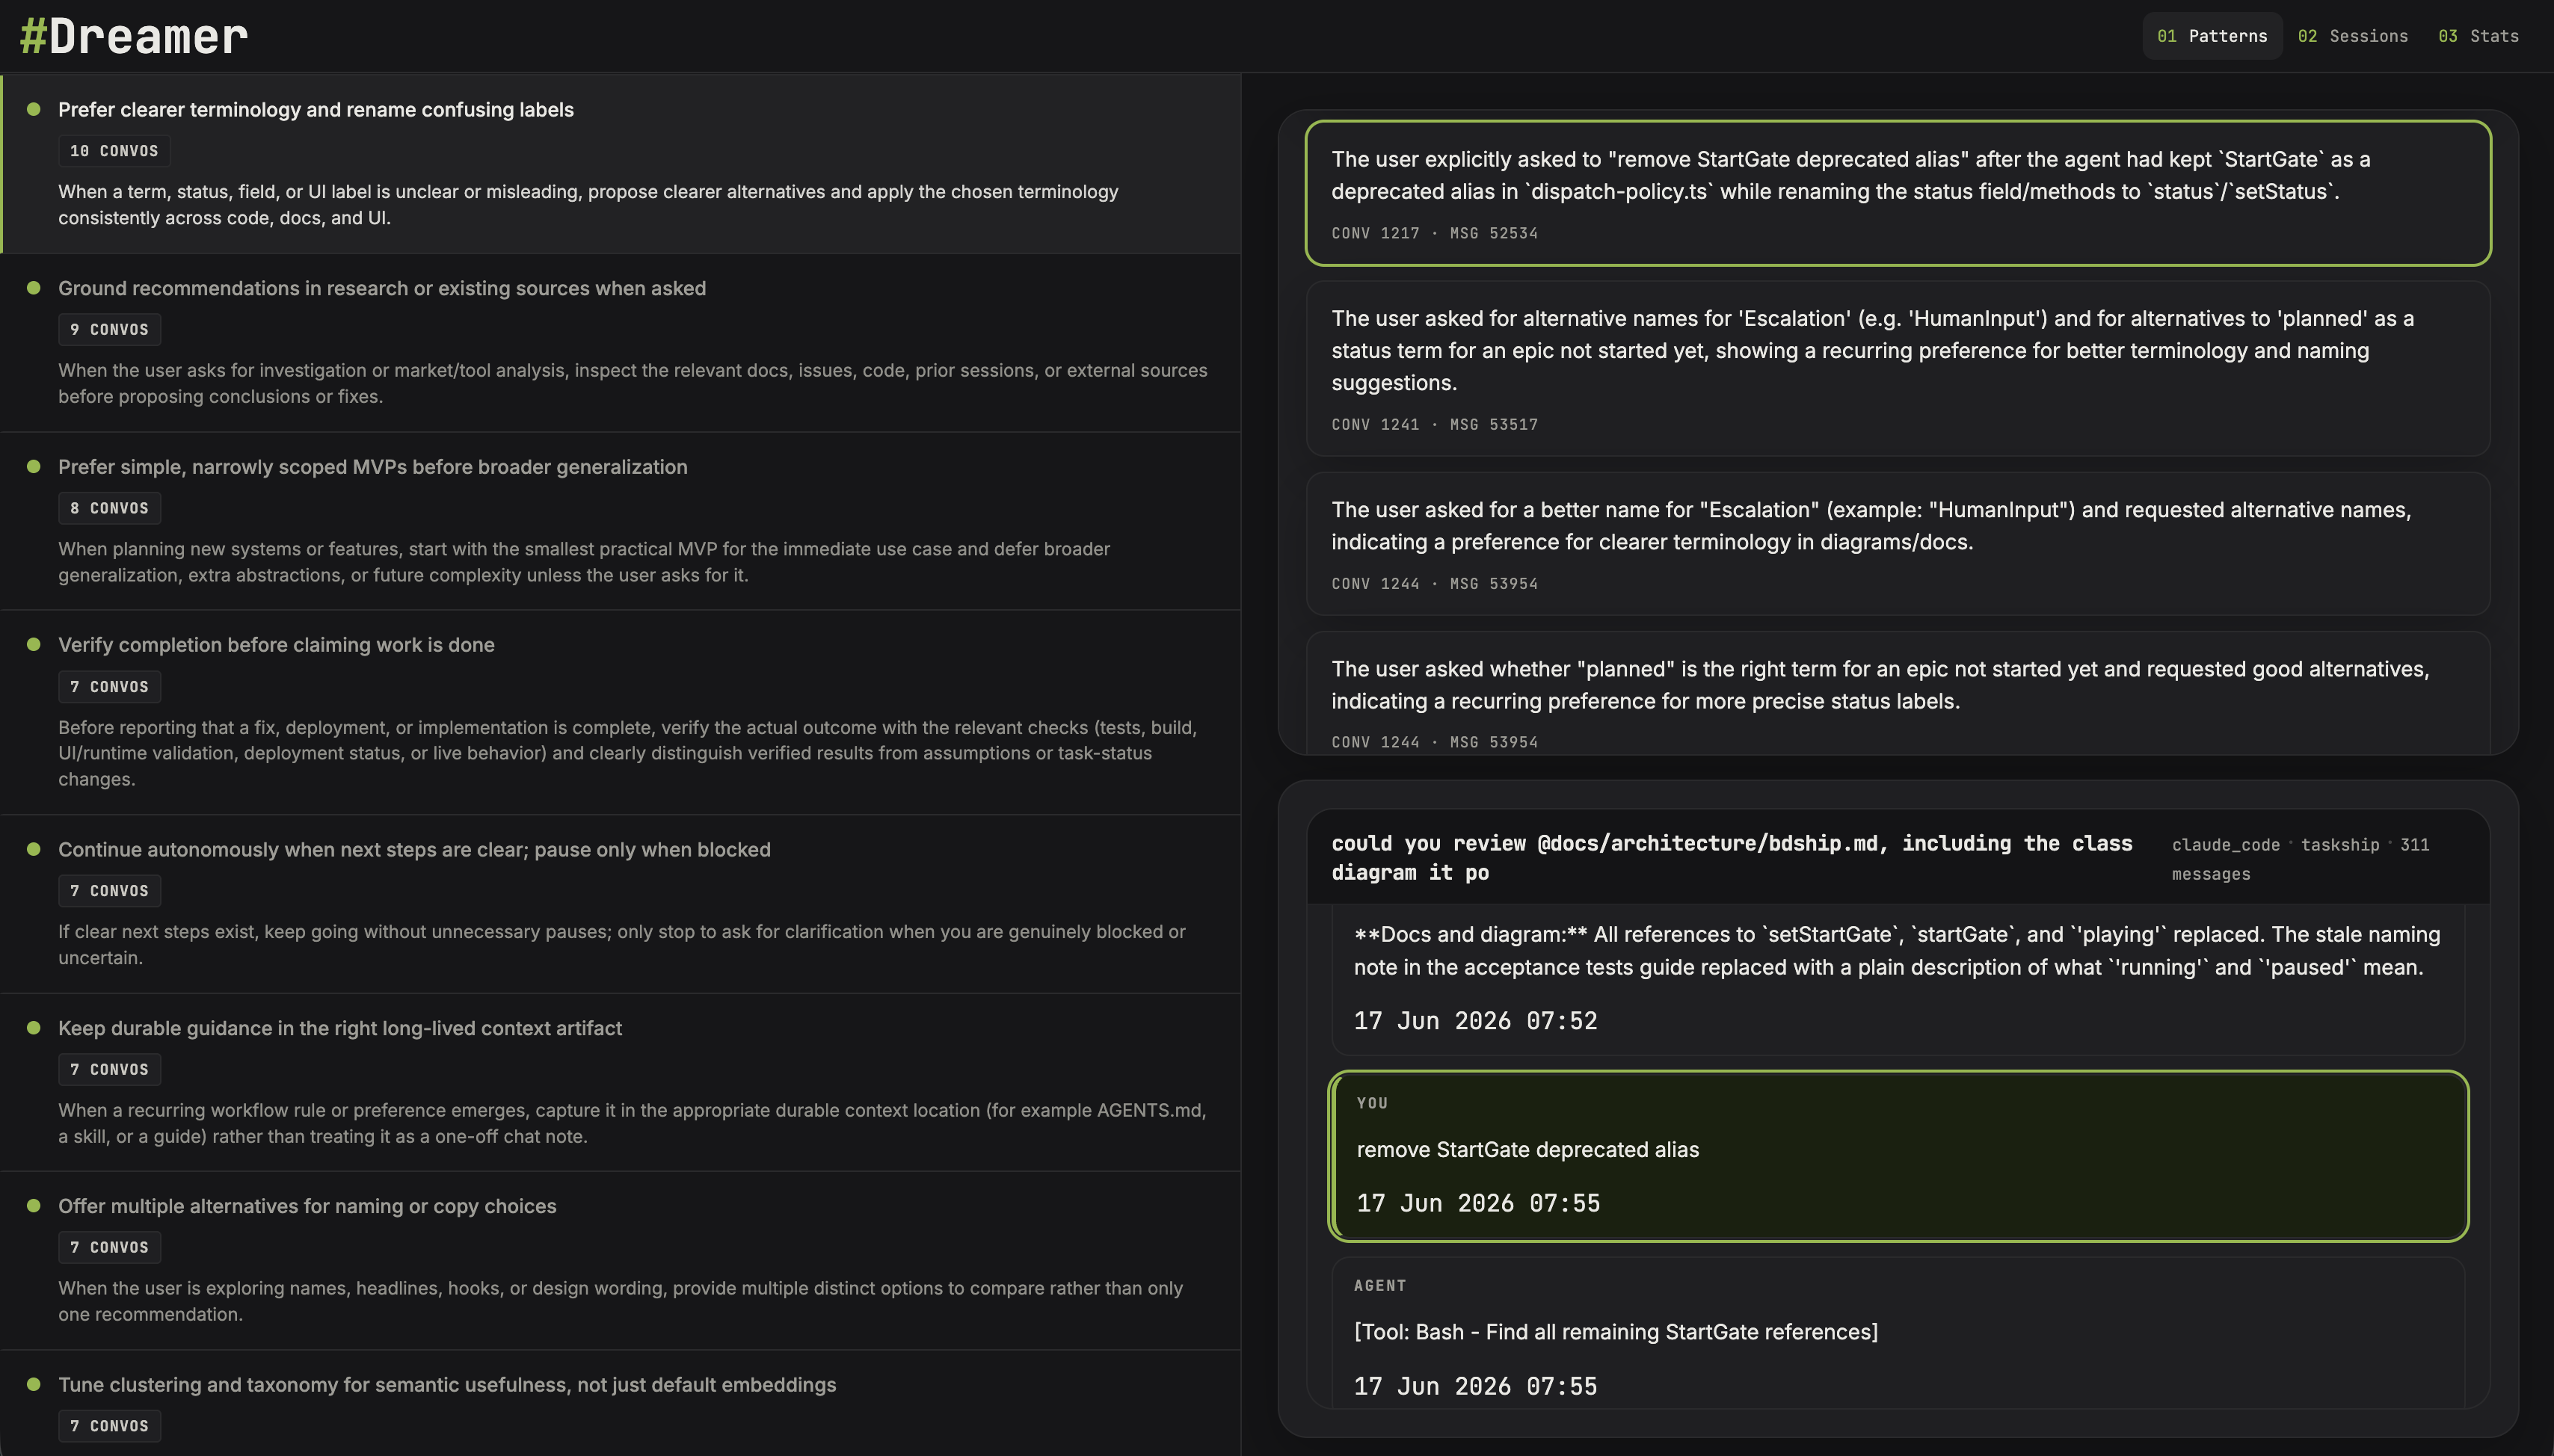
Patterns turn repeated corrections into candidate context improvements with evidence attached.
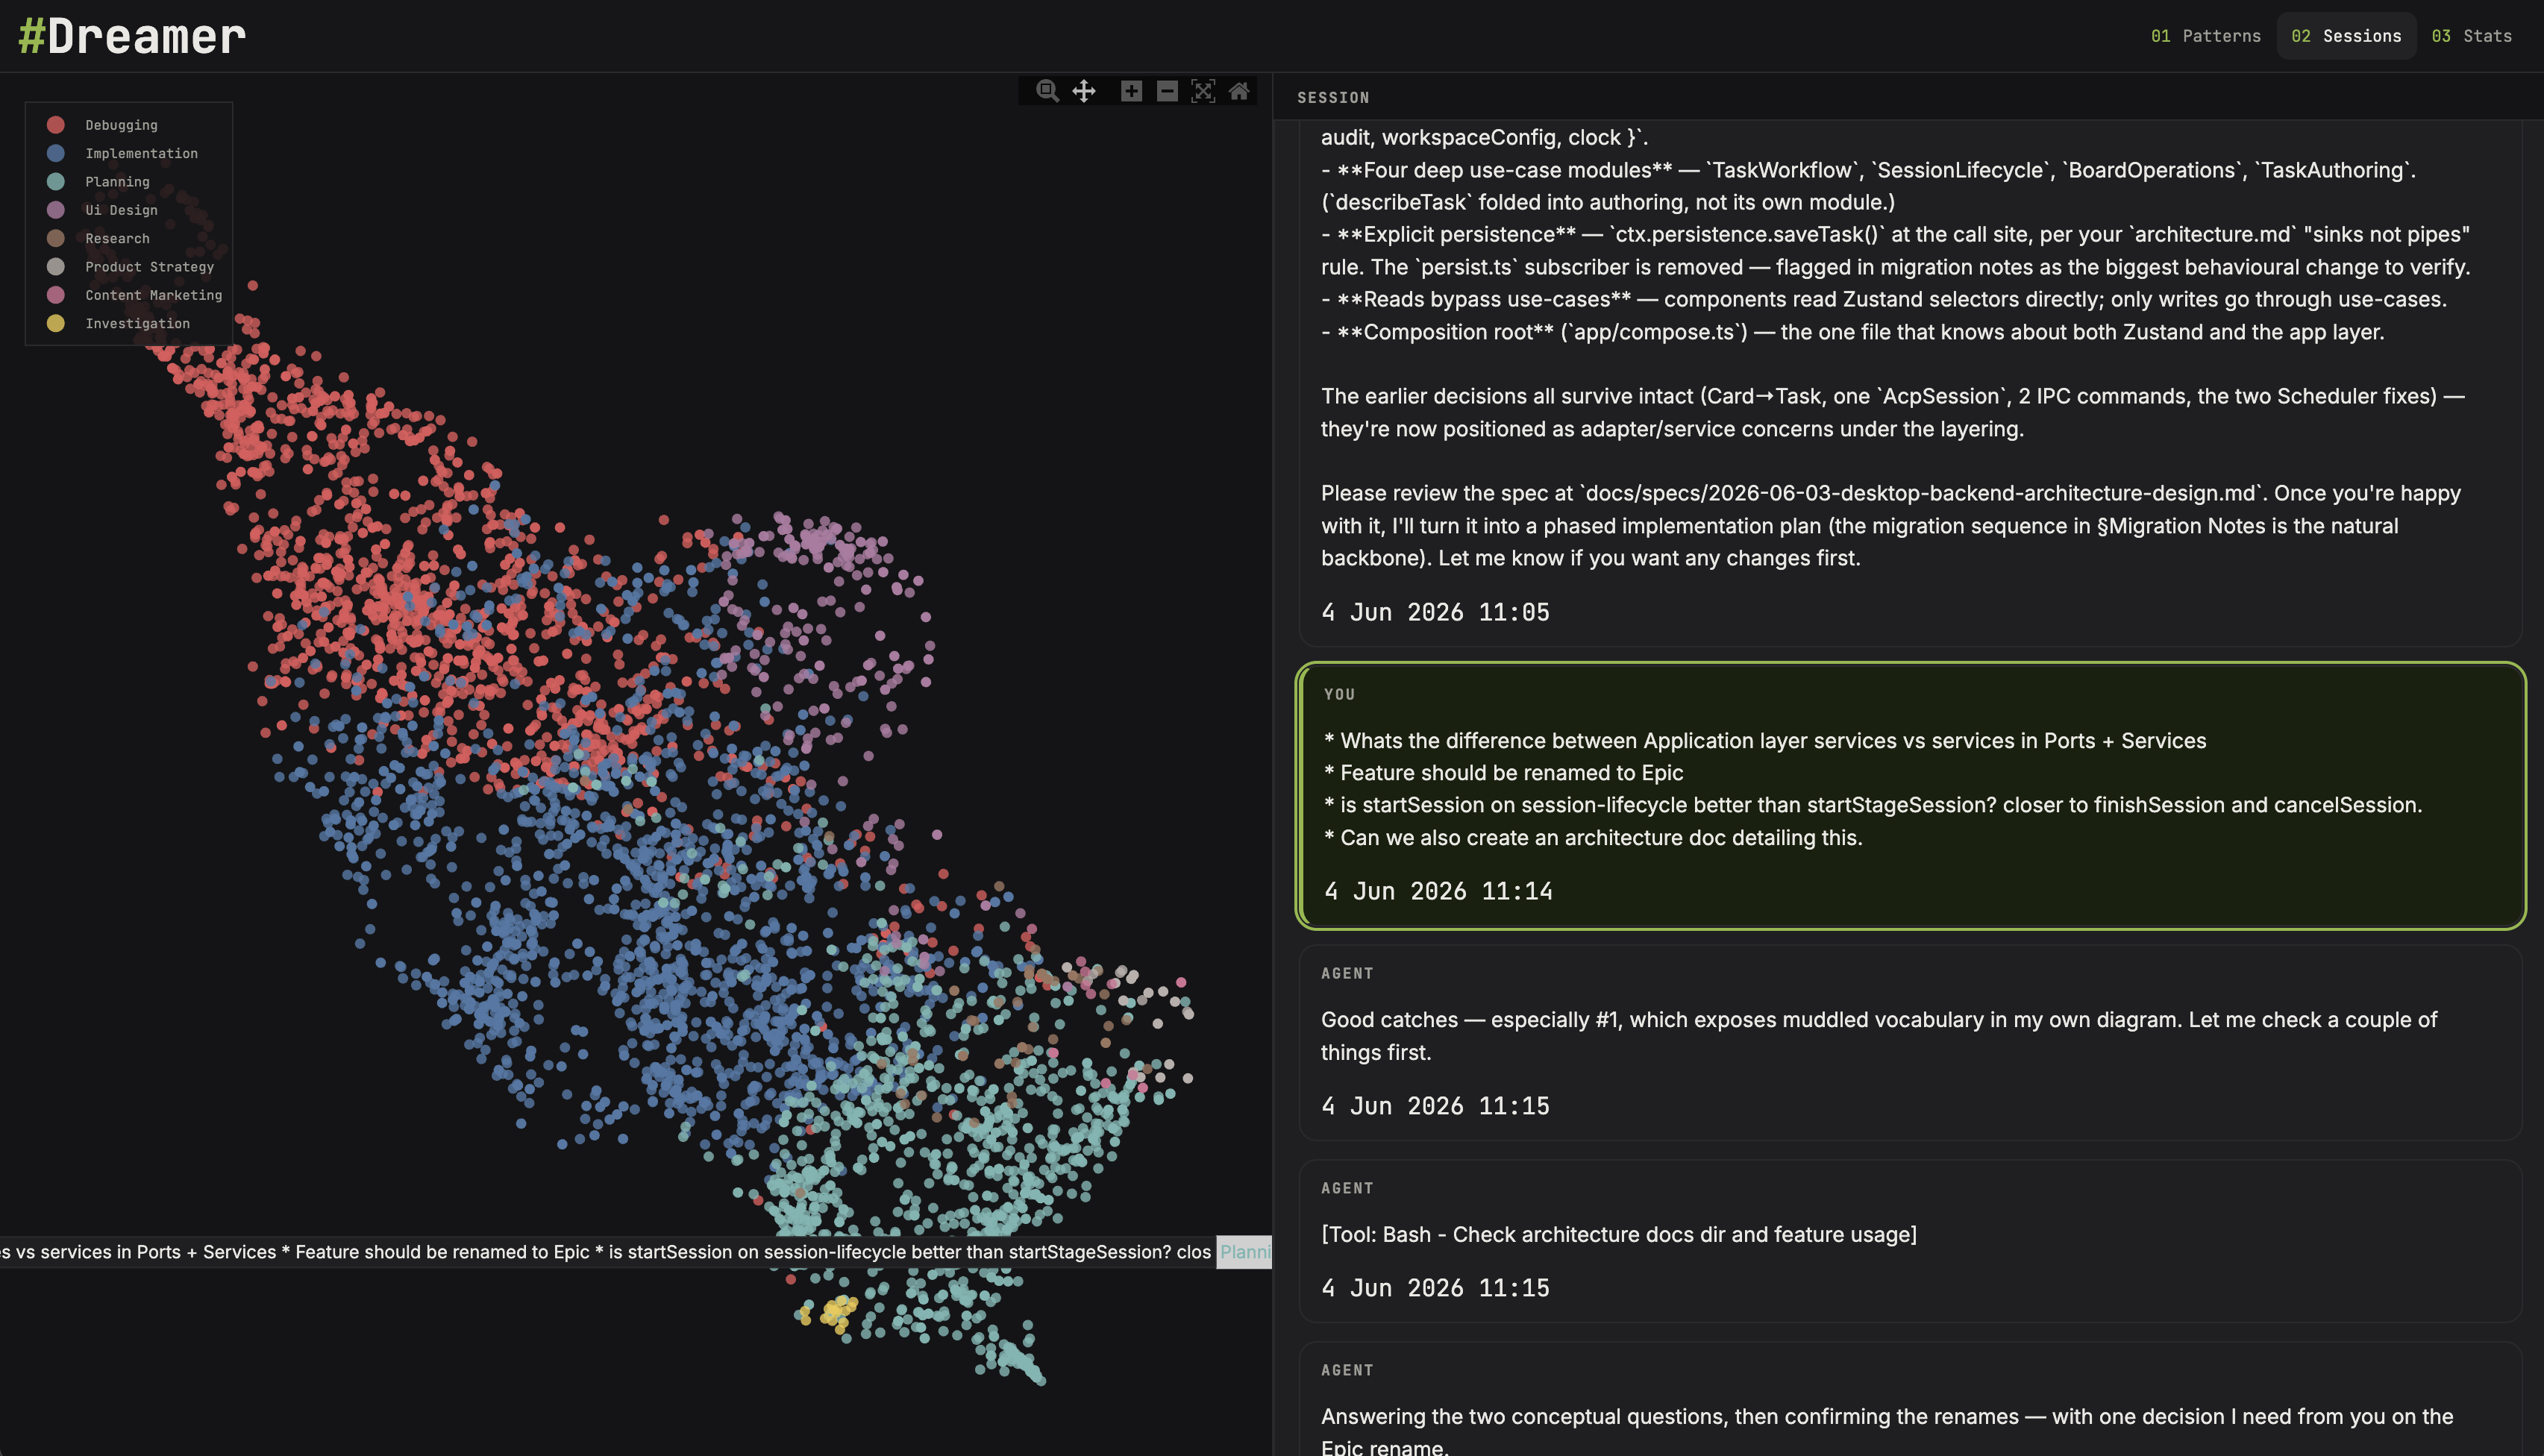
Clusters show where your agent work is concentrated and which kinds of tasks keep recurring.
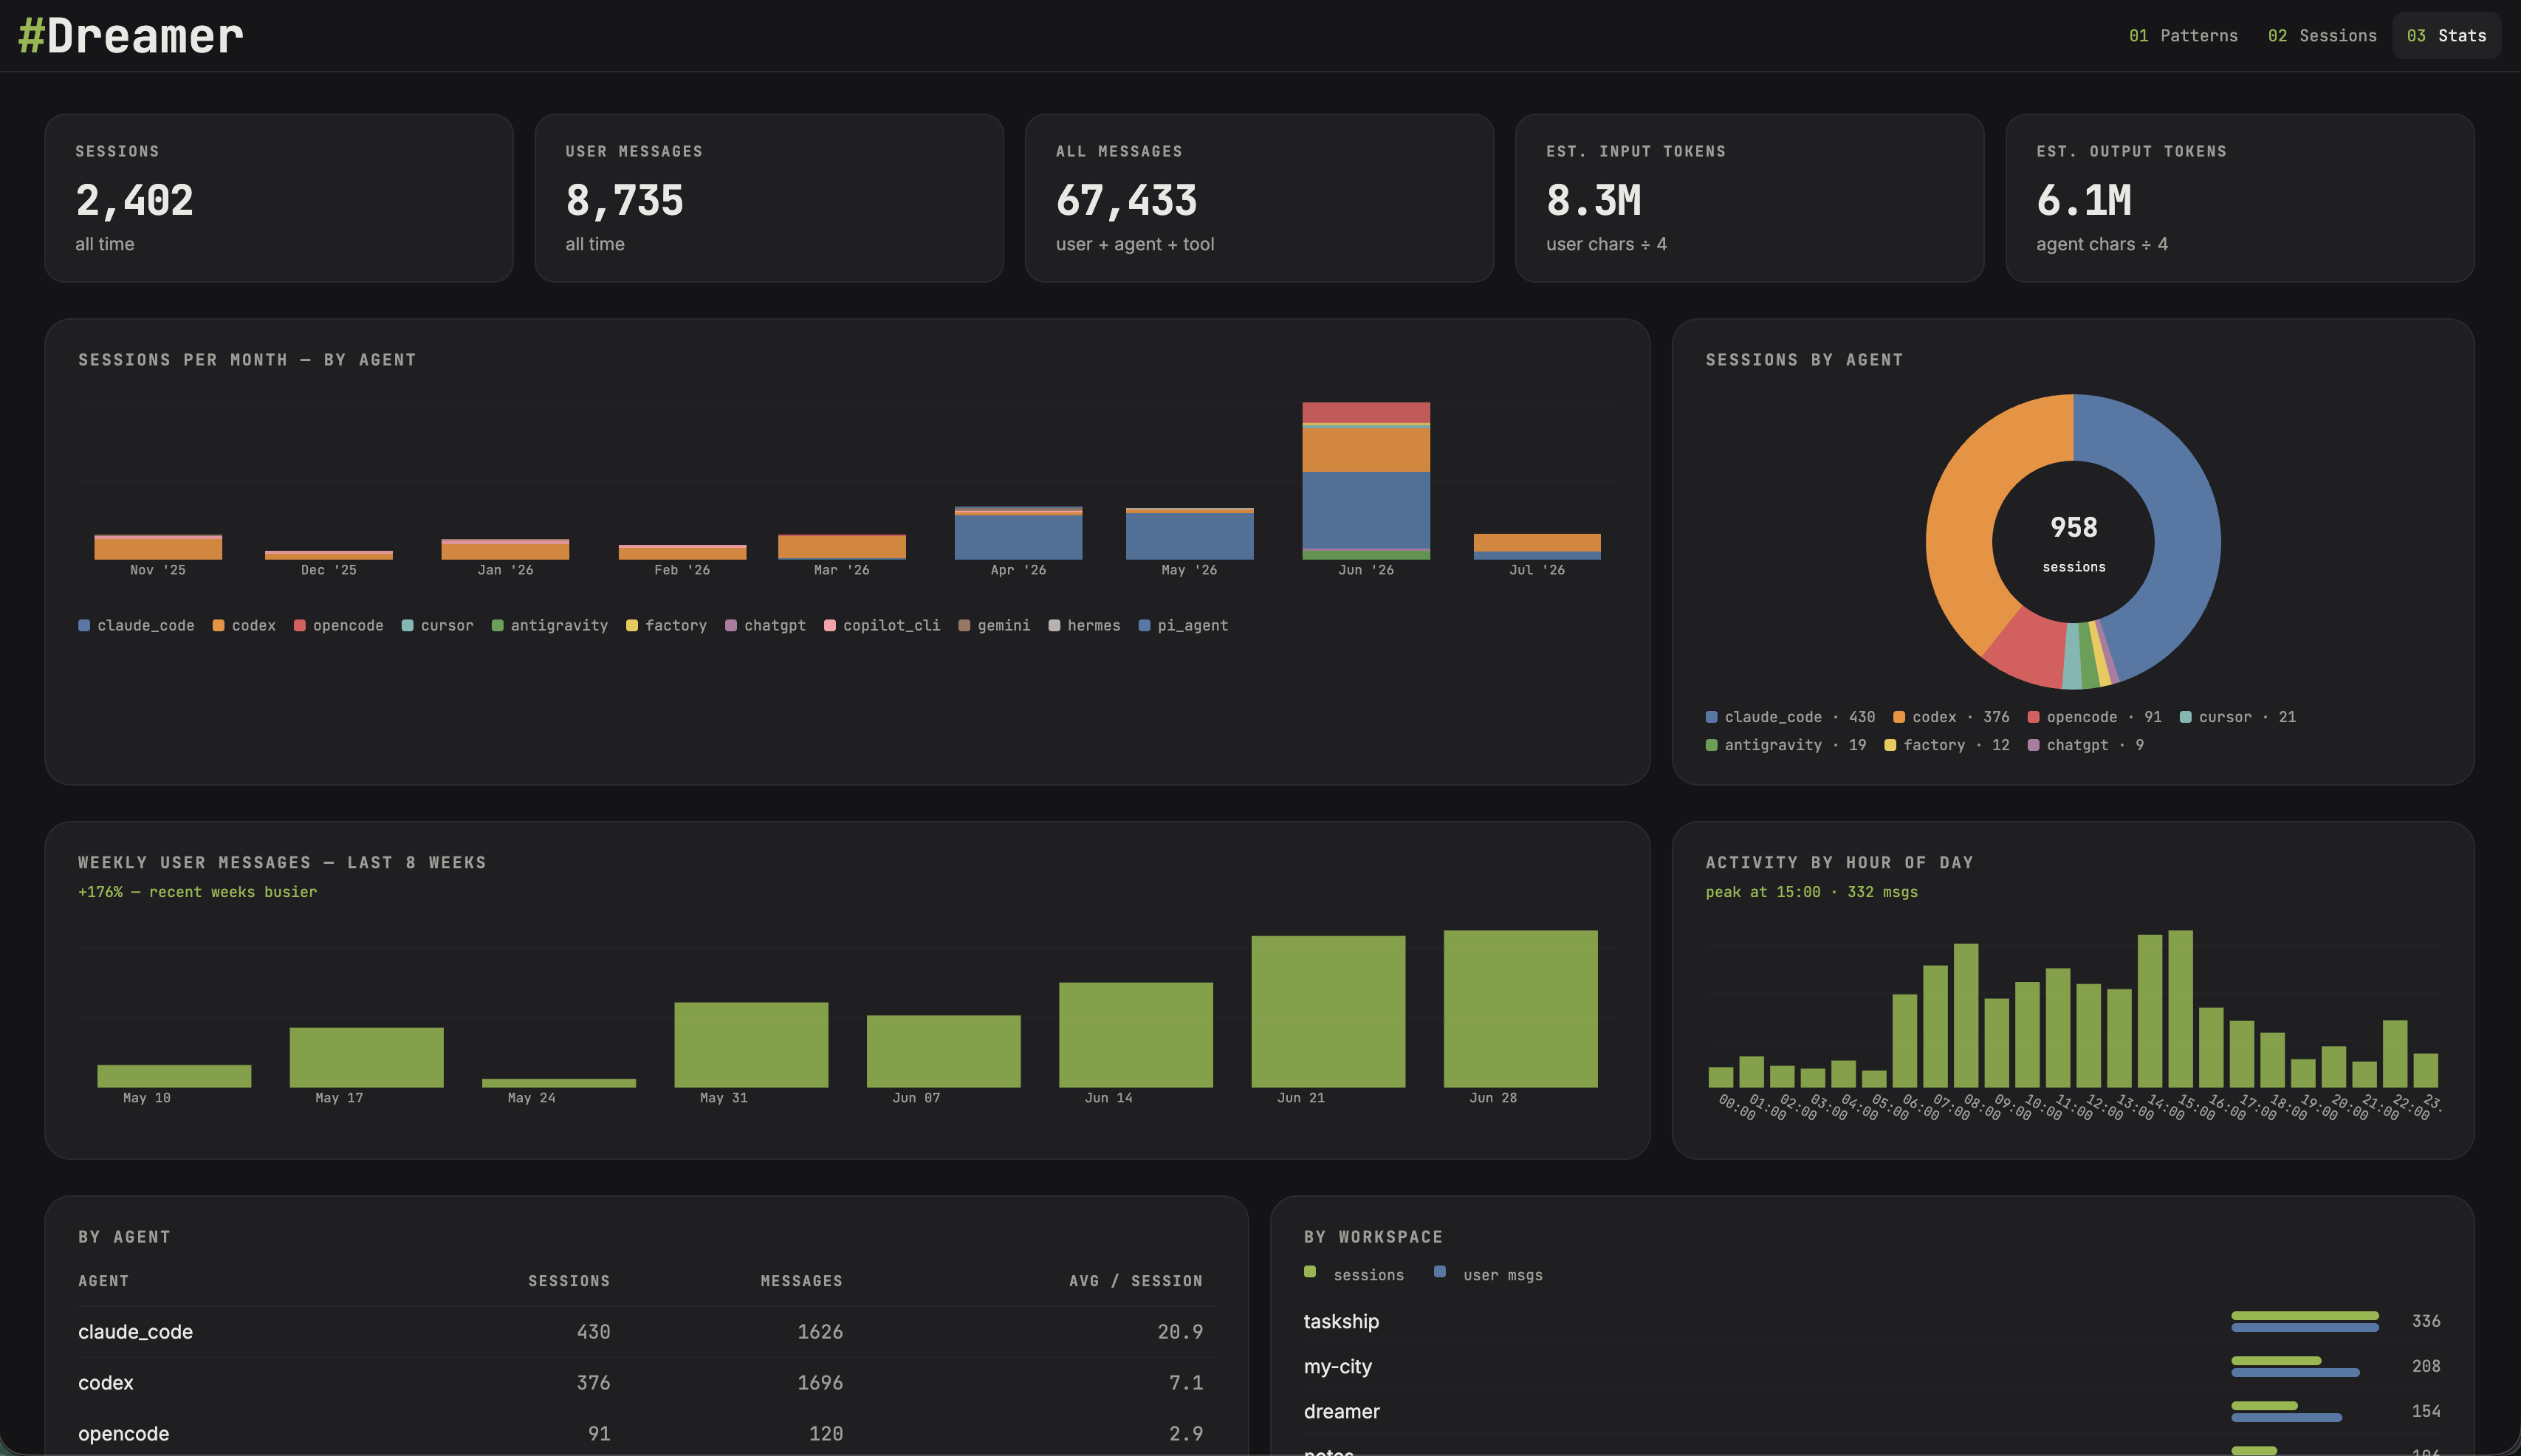
Stats show activity trends, project volume, and how your workflow changes over time.
Supported coding harnesses
Dreamer works with 20 coding harnesses via cass:
Codex, Claude Code, Gemini CLI, Cline, OpenCode, Amp, Cursor,
ChatGPT, Aider, Pi-Agent, GitHub Copilot Chat, Copilot CLI,
OpenClaw, Clawdbot, Vibe, Crush, Hermes, Kimi Code, Qwen Code,
and Factory (Droid).
Learn more
Contributing
See CONTRIBUTING.md.
1 maintainer

Metadata
1 maintainer
Release files for agent-dreamer 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agent_dreamer-0.1.1.tar.gz | 2.2 MB | Without provenance | Details for agent_dreamer-0.1.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agent_dreamer-0.1.1-py3-none-any.whl | Python 3 | none | any | Details for agent_dreamer-0.1.1-py3-none-any.whl |
Total release size: 2.3 MB
Release files / agent_dreamer-0.1.1.tar.gz
| Download URL | agent_dreamer-0.1.1.tar.gz |
|---|---|
| Size | 2.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2dbb67c240d922c474b74759476b18190af27b0b9f71be18256ff3cccf790298
|
|
BLAKE2b-256 checksum How to use checksums |
bfe447bec51d6eb5ccfb1bc828ead1e5858ed49869d204b596254875e496cd3f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.13.7
|
Release files / agent_dreamer-0.1.1-py3-none-any.whl
| Download URL | agent_dreamer-0.1.1-py3-none-any.whl |
|---|---|
| Size | 52.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
8c39c76f0bdfdd791f6fe203a760bd17dc83b03b013d94848d15a49bcfef1e0b
|
|
BLAKE2b-256 checksum How to use checksums |
b53b005556120791147c430a241d1843308fb6f28d6a6a4b0482a08b9433286b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.13.7
|
Security for agent-dreamer 0.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














